VLANS are extremely useful in preventing groups of users from accessing each other and are recommended.
For users within a VLAN, then firewall rules are useless.
In the old way of WIFI one could use access lists … however all i can find on my hapax3 is clien-isolation.
Here is a quote for Datapath Function TAB in Wifi… client-isolation (no | yes) Determines whether client devices connecting to this interface are (by default) isolated from others or not.
This policy can be overridden on a per-client basis using access list rules, so a an AP can have a mixture of isolated and non-isolated clients.
Traffic from an isolated client will not be forwarded to other clients and unicast traffic from a non-isolated client will not be forwarded to an isolated one.
Default: no
I just read that I can’t have more than 1 VLAN per virtual/SSID. If that is the case, I guess that client-isolation is the way to go.
Is there some way to have firewall rules between WIFI devices? So for example to allow one specific IP to connect to another IP over port 80 and nothing else?
On wireless chip, enable client isolation, then VLANs (Main VLAN, Guest VLAN etc), and finally on the layer 3-sub interface VLAN, you enable local-proxy-arp.
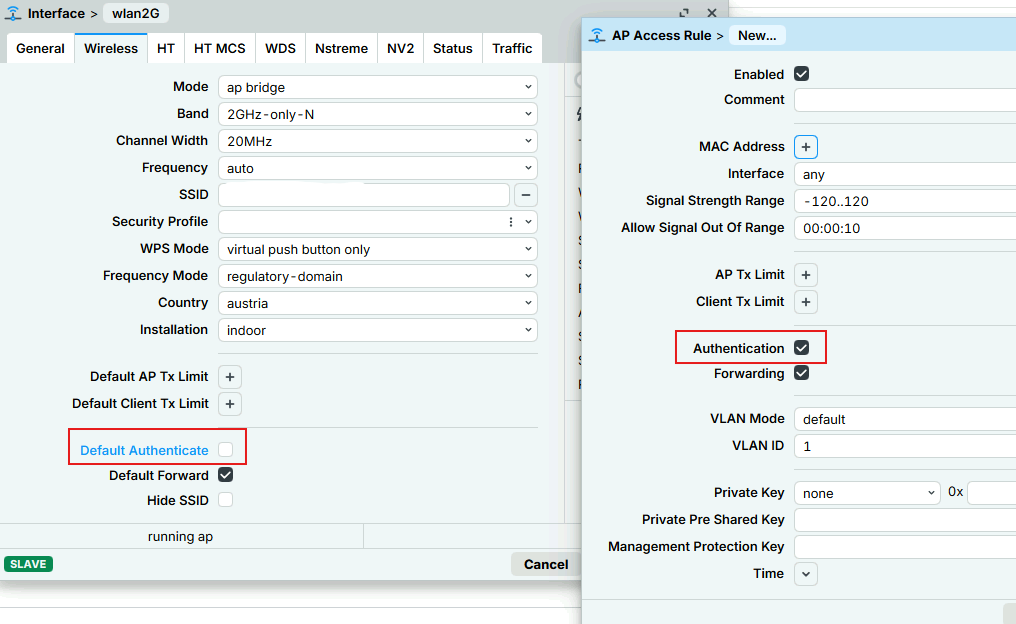
thanks ... applied that on a hAPacLite (no wave2 - only "legacy wireless"), because i ffs did not find any "client isolation" related stuff - and now that i think about that filter rules .... yes, makes absolute SENSE!
how does this isolate wifi clients? this only states that clients which are authenticated and thus connected do not get their traffic forwarded unless it is stated in an AP Access Rule
??? I don't understand the question, if one...
the screenshot shows forwarding, not authentication, and it's on the standard wireless connection, not Wave2/WiFi.