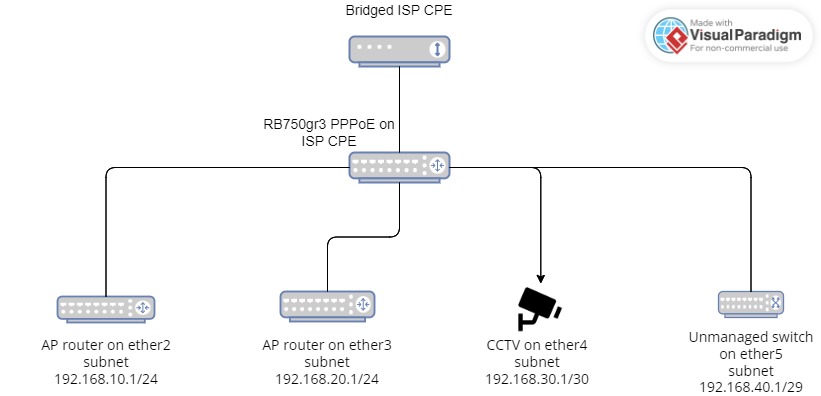
Thanks for your time. Please check below the conf and diagram (hope the diagram is clear).
# mar/30/2023 15:05:05 by RouterOS 6.49.7
# software id = QXU3-9BSF
#
# model = RB750Gr3
# serial number = CC210FFC6E46
/interface ethernet
set [ find default-name=ether1 ] comment="Uplink from CTCPE" loop-protect=on \
    mtu=1596
set [ find default-name=ether2 ] comment="DCOS / R2 / sw-8P" loop-protect=on \
    loop-protect-disable-time=10m mtu=1596
set [ find default-name=ether3 ] comment=R3 loop-protect=on \
    loop-protect-disable-time=10m mtu=1596
set [ find default-name=ether4 ] comment=CCTV loop-protect=on \
    loop-protect-disable-time=10m mtu=1596
set [ find default-name=ether5 ] comment=sw-8p l2mtu=1598 loop-protect=on \
    loop-protect-disable-time=10m
/interface pppoe-client
add disabled=no interface=ether1 name=pppoe-ctfiber user=user
/interface l2tp-server
add name=adu-1.PA-8010ANDGER7.ck******.com user=ad*****
add name=adu-1.PA-8820POLIS.ck******.com user=ad*****
add disabled=yes name=l2tp-ck**** user=ck****
add name=l2tp-hb535 user=hb*****
/interface ovpn-server
add name=ovpn-ck user=ch*****
/interface wireless security-profiles
set [ find default=yes ] supplicant-identity=MikroTik
/ip ipsec policy group
set [ find default=yes ] name=L2TP
/ip ipsec profile
set [ find default=yes ] dh-group=modp2048 dpd-interval=disable-dpd \
    enc-algorithm=aes-256 hash-algorithm=sha256
/ip ipsec proposal
set [ find default=yes ] auth-algorithms=sha256 enc-algorithms=aes-256-cbc \
    pfs-group=modp2048
/ip pool
add name=OVPN-Pool ranges=10.1.1.2-10.1.1.254
add name=L2TP-Pool ranges=10.2.1.2-10.2.1.100
add name=ether3_pool ranges=192.168.20.2-192.168.20.254
add name=ether2_pool ranges=192.168.10.2-192.168.10.254
add name=dhcp_pool20 ranges=192.168.40.2-192.168.40.6
/ip dhcp-server
add address-pool=ether3_pool disabled=no interface=ether3 lease-time=2h name=\
    ether3_dhcp
add address-pool=ether2_pool disabled=no interface=ether2 lease-time=2h name=\
    ether2_dhcp
add address-pool=dhcp_pool20 disabled=no interface=ether5 lease-time=2h name=\
    dhcp1
/ppp profile
set *0 change-tcp-mss=default
add local-address=10.1.1.1 name=OVPN remote-address=OVPN-Pool
add local-address=10.2.1.1 name=L2TP remote-address=L2TP-Pool
set *FFFFFFFE change-tcp-mss=default use-encryption=default
/queue simple
add burst-time=2s/2s max-limit=52M/205M name=192.168.10.0/24_200/50 target=\
    192.168.10.0/24
add burst-time=2s/2s max-limit=52M/205M name=ether3_200/50 target=ether3
/snmp community
set [ find default=yes ] disabled=yes
add addresses=172.168.188.2/32 name=d*****
/system logging action
add email-start-tls=yes email-to=ch****@hotmail.com name=email \
    target=email
/interface l2tp-server server
set default-profile=L2TP enabled=yes max-mru=1700 max-mtu=1700 \
    one-session-per-host=yes use-ipsec=required
/interface ovpn-server server
set auth=sha1 certificate=server cipher=aes256 default-profile=OVPN enabled=\
    yes port=61194 require-client-certificate=yes
/ip address
add address=192.168.10.1/24 comment=DHCP interface=ether2 network=\
    192.168.10.0
add address=192.168.20.1/24 comment=DHCP interface=ether3 network=\
    192.168.20.0
add address=172.168.188.1/24 comment=Fasttrack interface=ether2 network=\
    172.168.188.0
add address=192.168.8.250/24 comment=Failover interface=ether2 network=\
    192.168.8.0
add address=192.100.30.1/29 comment=CCTV interface=ether4 network=\
    192.100.30.0
add address=192.168.40.1/29 comment=DHCP interface=ether5 network=\
    192.168.40.0
/ip dhcp-server network
add address=192.168.10.0/24 dns-server=1.1.1.1,8.8.8.8 gateway=192.168.10.1
add address=192.168.20.0/24 dns-server=1.1.1.1,8.8.8.8 gateway=192.168.20.1
add address=192.168.40.0/29 dns-server=1.1.1.1,8.8.8.8 gateway=192.168.40.1
/ip dns
set allow-remote-requests=yes servers=10.0.0.1,1.1.1.1,8.8.8.8
/ip dns static
add address=172.168.188.2 name=dcos.ck******.com
add address=213.7.231.xx name=ns1monitoring.ck******.com
add address=38.242.199.97 name=ns2monitoring.ck******.com
add address=38.242.199.97 name=mail.ck******.com
add address=172.168.188.1 name=bbhq.ck******.com
add address=10.2.1.150 name=adu-1.PA-8010ANDGER7.ck******.com
add address=10.2.1.151 name=adu-1.PA-8820POLIS.ck******.com
add address=192.100.30.2 name=cctv.ck******.com
/ip firewall filter
add action=fasttrack-connection chain=forward comment=\
    "Allow fasttrack on 172.168.188.0/24" src-address=172.168.188.0/24
add action=accept chain=input comment="Allow incoming good connection states" \
    connection-state=established,related,new
add action=accept chain=forward comment=\
    "Allow forward good connection states" connection-state=\
    established,related,new
add action=drop chain=input comment="Drop input invalid connection state" \
    connection-state=invalid
add action=accept chain=input comment="Accept L2TP ipsec encapsulated" \
    dst-port=1701 ipsec-policy=in,ipsec protocol=udp
add action=accept chain=input comment="Accept IKE" dst-port=500 protocol=udp
add action=accept chain=input comment="Accept IPsec NAT" dst-port=4500 \
    protocol=udp
add action=accept chain=input protocol=ipsec-esp
add action=drop chain=forward comment="Drop forward invalid connection state" \
    connection-state=invalid
add action=accept chain=input comment="Port Scanner Block" disabled=yes \
    protocol=tcp src-address=172.168.188.0/24
add action=accept chain=input disabled=yes protocol=tcp src-address=\
    10.100.1.0/24
add action=add-src-to-address-list address-list="Ports Scanner Attacks" \
    address-list-timeout=1d chain=input disabled=yes dst-port=\
    62222,60080,60090 protocol=tcp
add action=drop chain=input disabled=yes dst-port=62222,60080,60090 protocol=\
    tcp src-address-list="Ports Scanner Attacks"
/ip firewall mangle
add action=change-mss chain=forward disabled=yes new-mss=1700 passthrough=yes \
    protocol=tcp tcp-flags=syn tcp-mss=!0-1700
/ip firewall nat
add action=masquerade chain=srcnat src-address=172.168.188.0/24
add action=masquerade chain=srcnat src-address=192.168.10.0/24
add action=masquerade chain=srcnat src-address=192.168.20.0/24
add action=masquerade chain=srcnat src-address=192.100.30.0/29
add action=masquerade chain=srcnat src-address=192.168.40.0/29
add action=masquerade chain=srcnat src-address=192.168.8.0/24
add action=masquerade chain=srcnat src-address=10.1.1.0/24
add action=masquerade chain=srcnat src-address=10.2.1.0/24
add action=dst-nat chain=dstnat comment=DCOS dst-address=213.7.231.xx \
    dst-port=1-40000 protocol=tcp src-port="" to-addresses=172.168.188.2 \
    to-ports=1-40000
add action=dst-nat chain=dstnat dst-address=213.7.231.xx dst-port=53 \
    protocol=udp to-addresses=172.168.188.2 to-ports=53
add action=dst-nat chain=dstnat dst-address=213.7.231.xx dst-port=1194 \
    protocol=udp to-addresses=172.168.188.2 to-ports=1194
add action=dst-nat chain=dstnat comment=NTP dst-address=213.7.231.xx \
    dst-port=123 protocol=udp to-addresses=172.168.188.2 to-ports=123
add action=dst-nat chain=dstnat comment=CCTV dst-address=213.7.231.xx \
    dst-port=65000 protocol=tcp to-addresses=192.100.30.2 to-ports=65000
add action=dst-nat chain=dstnat dst-address=213.7.231.xx dst-port=65090 \
    protocol=tcp to-addresses=192.100.30.2 to-ports=65090
add action=dst-nat chain=dstnat comment=WoL dst-address=213.7.231.xx \
    dst-port=7 protocol=udp to-addresses=172.168.188.0/24 to-ports=7
add action=redirect chain=dstnat comment="DNS Server" dst-port=53 protocol=\
    tcp to-ports=53
add action=redirect chain=dstnat dst-port=53 protocol=udp to-ports=53
/ip route
add check-gateway=ping comment=PPPoE distance=1 gateway=pppoe-ctfiber
add check-gateway=ping comment=LTE-Backup disabled=yes distance=2 gateway=\
    192.168.8.1
/ip service
set telnet disabled=yes
set ftp address=172.168.188.0/24,10.1.1.0/24,10.2.1.1/32 port=60021
set www address=172.168.188.0/24,10.1.1.0/24,10.2.1.1/32 port=60080
set ssh address=172.168.188.0/24,10.1.1.0/24,10.2.1.1/32 port=62222
set api disabled=yes
set winbox address=172.168.188.0/24,10.1.1.0/24,10.2.1.1/32 port=60090
set api-ssl disabled=yes
/ppp secret
add name=ch***** profile=OVPN service=ovpn
add name=hb***** profile=L2TP service=l2tp
add disabled=yes name=ck**** profile=L2TP service=l2tp
add name=ad***** profile=L2TP remote-address=10.2.1.150 service=l2tp
add name=ad***** profile=L2TP remote-address=10.2.1.151 service=l2tp
/snmp
set contact=ch****@hotmail.com enabled=yes location=HQ \
    trap-community=dcos_com_only_ trap-target=172.168.188.2 trap-version=2
/system clock
set time-zone-name=Asia/Nicosia
/system identity
set name=bbhq.ck******.com
/system logging
add action=email topics=critical
add action=email disabled=yes topics=interface
add action=email topics=firewall
/system ntp client
set enabled=yes primary-ntp=213.7.231.xx secondary-ntp=172.168.188.2
/tool e-mail
set address=mail.ck******.com from=r1@ck******.com port=587 start-tls=yes \
    user=r1@ck******.com
/tool graphing interface
add interface=ether1
add interface=ether2
add interface=ether3
add interface=ether4
add interface=pppoe-ctfiber
/tool graphing resource
add
/tool netwatch
add disabled=yes down-script="interface set ether5 disable=no" host=\
    213.7.231.xx interval=1s up-script="interface set ether5 disable=yes"
add disabled=yes down-script="tool e-mail send to=ch****@hotmail.com s\
    ubject=Uplink_from_CPE_DOWN start-tls=yes body=Uplink_from_CPE_is_DOWN" \
    host=213.7.231.xx interval=10s up-script="tool e-mail send to=ch*****\
    **@hotmail.com subject=Uplink_from_CPE_UP start-tls=yes body=Uplink_from_C\
    PE_is_UP"