Hi all!
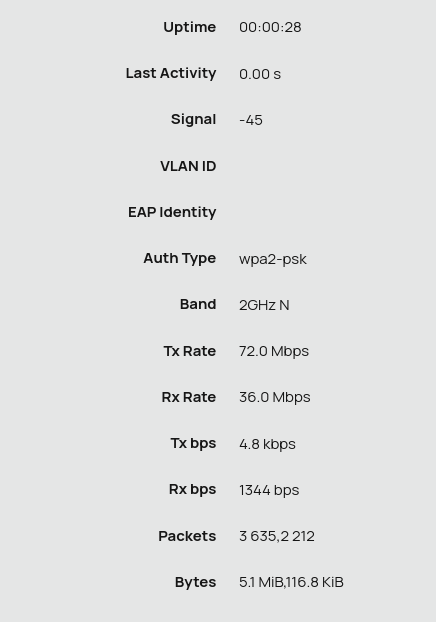
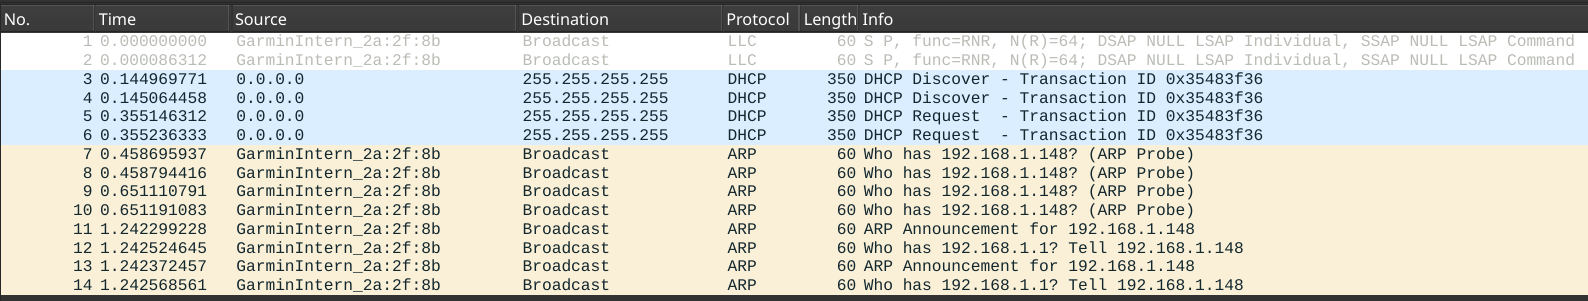
I have an hap ac3 running a capsman instance with a connected cAP ac. After switching to the new wifi-qcam-ac package, my Garmin Forerunner 955 drops the connection to the Wifi after receiving ~5.1MiB of data. How can I be so sure about the data size? Because I am trying to debug this thing for weeks now - data amount is always the same. The watch is transfering with good bandwith and then suddenly it drop to zero until it will just disconnect. The logs will give no more information than just:
XX:XX:XX:XX:2F:8B@wifi1(mpb-net) disconnected, connection lost, signal strength -70
The watch is working fine in other Wifi networks. The ONLY THING that helps to solve the issue in my network, is to downgrade the 2.4Ghz band to the G standard - everything is working fine then, but of course I am limitting all the other devices to slow bandwith as well. Since I tried nearly everything from setting manual frequency to disabling all the roaming settings, etc. I assume that this has to be a bug either in the Mikrotik software or the Garmin device. Since it worked fine for years with the old Wifi package, I guess it is related to the wifiwave2/qcom package.
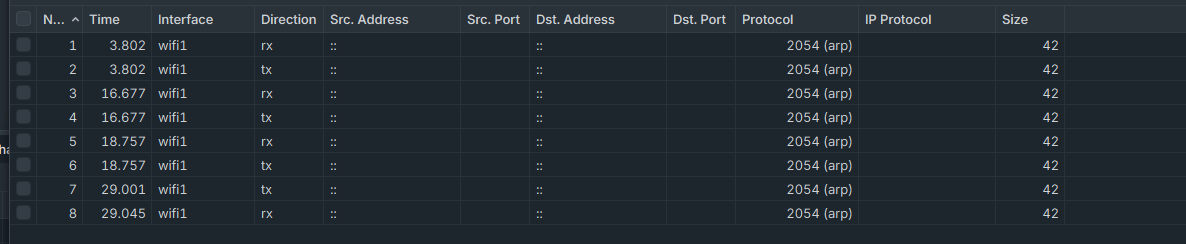
I really would like to further debug this issue, but I have no more ideas to gather more information?! Or maybe I am missing something in my config that can cause this?
Here is the config that is NOT working with the Garmin watch:
# 2025-12-14 19:05:17 by RouterOS 7.20.6

# software id = YC5S-YUYC

#

# model = RBD53iG-5HacD2HnD

# serial number =

/interface bridge

add name=bridge port-cost-mode=short

/interface list

add name=WAN

add name=LAN

/interface lte apn

set [ find default=yes ] ip-type=ipv4 use-network-apn=no

/interface wifi channel

add band=2ghz-n disabled=no name="mpb-net 2GHz" reselect-interval=23h30m..23h59m

add band=5ghz-ac disabled=no name="mpb-net 5GHz" reselect-interval=23h30m..23h59m skip-dfs-channels=all

/interface wifi datapath

add bridge=bridge disabled=no name=mpb-net

/interface wifi security

add authentication-types=wpa2-psk connect-priority=0/1 disabled=no encryption=ccmp ft=yes ft-over-ds=yes name="mpb-net WPA2"

/interface wifi steering

add 2g-probe-delay=yes disabled=no name=mpb-steering neighbor-group=dynamic-mpb-net-a860b91a rrm=yes wnm=yes

/interface wifi configuration

add channel="mpb-net 2GHz" country=Germany datapath=mpb-net disabled=no manager=local mode=ap name="mpb-net 2G" security="mpb-net WPA2" ssid=mpb-net steering=mpb-steering

add channel="mpb-net 5GHz" country=Germany datapath=mpb-net disabled=no manager=local mode=ap name="mpb-net 5G" security="mpb-net WPA2" ssid=mpb-net steering=mpb-steering

/interface bridge port

add bridge=bridge ingress-filtering=no interface=ether2 internal-path-cost=10 path-cost=10

add bridge=bridge ingress-filtering=no interface=ether1 internal-path-cost=10 path-cost=10

add bridge=bridge ingress-filtering=no interface=ether3 internal-path-cost=10 path-cost=10

add bridge=bridge ingress-filtering=no interface=ether4 internal-path-cost=10 path-cost=10

add bridge=bridge ingress-filtering=no interface=ether5 internal-path-cost=10 path-cost=10

/ip firewall connection tracking

set enabled=no udp-timeout=10s

/ipv6 settings

set disable-ipv6=yes max-neighbor-entries=8192

/interface detect-internet

set detect-interface-list=all

/interface list member

add interface=ether1 list=WAN

add interface=ether2 list=LAN

add interface=ether3 list=LAN

add interface=ether4 list=LAN

add interface=ether5 list=LAN

add interface=wifi1 list=LAN

add interface=wifi2 list=LAN

/interface ovpn-server server

add auth=sha1,md5 mac-address=FE:4C:EF:30:33:EE name=ovpn-server1

/interface wifi cap

set certificate=none discovery-interfaces=bridge slaves-datapath=mpb-net slaves-static=no

/interface wifi capsman

set ca-certificate=auto certificate=auto enabled=yes interfaces=bridge package-path="" require-peer-certificate=no upgrade-policy=none

/interface wifi provisioning

add action=create-dynamic-enabled disabled=no master-configuration="mpb-net 2G" supported-bands=2ghz-n

add action=create-dynamic-enabled disabled=no master-configuration="mpb-net 5G" supported-bands=5ghz-n

/ip address

add address=192.168.1.2/24 interface=ether2 network=192.168.1.0

/ip dns

set servers=192.168.1.1

/ip firewall filter

add action=accept chain=input disabled=yes in-interface=bridge protocol=udp src-port=5246,5247

add action=accept chain=input disabled=yes dst-port=5246,5247 in-interface=bridge protocol=udp

/ip ipsec profile

set [ find default=yes ] dpd-interval=2m dpd-maximum-failures=5

/ip route

add disabled=no dst-address=0.0.0.0/0 gateway=192.168.1.1

/routing bfd configuration

add disabled=no

/system clock

set time-zone-name=Europe/Berlin

/system identity

set name=ac3

/system routerboard settings

set auto-upgrade=yes
And here is the config, that is working flawlessly:
# 2025-12-14 19:08:27 by RouterOS 7.20.6

# software id = YC5S-YUYC

#

# model = RBD53iG-5HacD2HnD

# serial number =

/interface bridge

add name=bridge port-cost-mode=short

/interface list

add name=WAN

add name=LAN

/interface lte apn

set [ find default=yes ] ip-type=ipv4 use-network-apn=no

/interface wifi channel

add band=2ghz-g disabled=no name="mpb-net 2GHz" reselect-interval=23h30m..23h59m

add band=5ghz-ac disabled=no name="mpb-net 5GHz" reselect-interval=23h30m..23h59m skip-dfs-channels=all

/interface wifi datapath

add bridge=bridge disabled=no name=mpb-net

/interface wifi security

add authentication-types=wpa2-psk connect-priority=0/1 disabled=no encryption=ccmp ft=yes ft-over-ds=yes name="mpb-net WPA2"

/interface wifi steering

add 2g-probe-delay=yes disabled=no name=mpb-steering neighbor-group=dynamic-mpb-net-a860b91a rrm=yes wnm=yes

/interface wifi configuration

add channel="mpb-net 2GHz" country=Germany datapath=mpb-net disabled=no manager=local mode=ap name="mpb-net 2G" security="mpb-net WPA2" ssid=mpb-net steering=mpb-steering

add channel="mpb-net 5GHz" country=Germany datapath=mpb-net disabled=no manager=local mode=ap name="mpb-net 5G" security="mpb-net WPA2" ssid=mpb-net steering=mpb-steering

/interface bridge port

add bridge=bridge ingress-filtering=no interface=ether2 internal-path-cost=10 path-cost=10

add bridge=bridge ingress-filtering=no interface=ether1 internal-path-cost=10 path-cost=10

add bridge=bridge ingress-filtering=no interface=ether3 internal-path-cost=10 path-cost=10

add bridge=bridge ingress-filtering=no interface=ether4 internal-path-cost=10 path-cost=10

add bridge=bridge ingress-filtering=no interface=ether5 internal-path-cost=10 path-cost=10

/ip firewall connection tracking

set enabled=no udp-timeout=10s

/ipv6 settings

set disable-ipv6=yes max-neighbor-entries=8192

/interface detect-internet

set detect-interface-list=all

/interface list member

add interface=ether1 list=WAN

add interface=ether2 list=LAN

add interface=ether3 list=LAN

add interface=ether4 list=LAN

add interface=ether5 list=LAN

add interface=wifi1 list=LAN

add interface=wifi2 list=LAN

/interface ovpn-server server

add auth=sha1,md5 mac-address=FE:4C:EF:30:33:EE name=ovpn-server1

/interface wifi cap

set certificate=none discovery-interfaces=bridge slaves-datapath=mpb-net slaves-static=no

/interface wifi capsman

set ca-certificate=auto certificate=auto enabled=yes interfaces=bridge package-path="" require-peer-certificate=no upgrade-policy=none

/interface wifi provisioning

add action=create-dynamic-enabled disabled=no master-configuration="mpb-net 2G" supported-bands=2ghz-n

add action=create-dynamic-enabled disabled=no master-configuration="mpb-net 5G" supported-bands=5ghz-n

/ip address

add address=192.168.1.2/24 interface=ether2 network=192.168.1.0

/ip dns

set servers=192.168.1.1

/ip firewall filter

add action=accept chain=input disabled=yes in-interface=bridge protocol=udp src-port=5246,5247

add action=accept chain=input disabled=yes dst-port=5246,5247 in-interface=bridge protocol=udp

/ip ipsec profile

set [ find default=yes ] dpd-interval=2m dpd-maximum-failures=5

/ip route

add disabled=no dst-address=0.0.0.0/0 gateway=192.168.1.1

/routing bfd configuration

add disabled=no

/system clock

set time-zone-name=Europe/Berlin

/system identity

set name=ac3

/system routerboard settings

set auto-upgrade=yes
Any ideas, hints or known issues regarding this?
Thanks!