I bought a hEX S (2025) E60iUGS a week ago with the idea to gain more knowledge over networking.
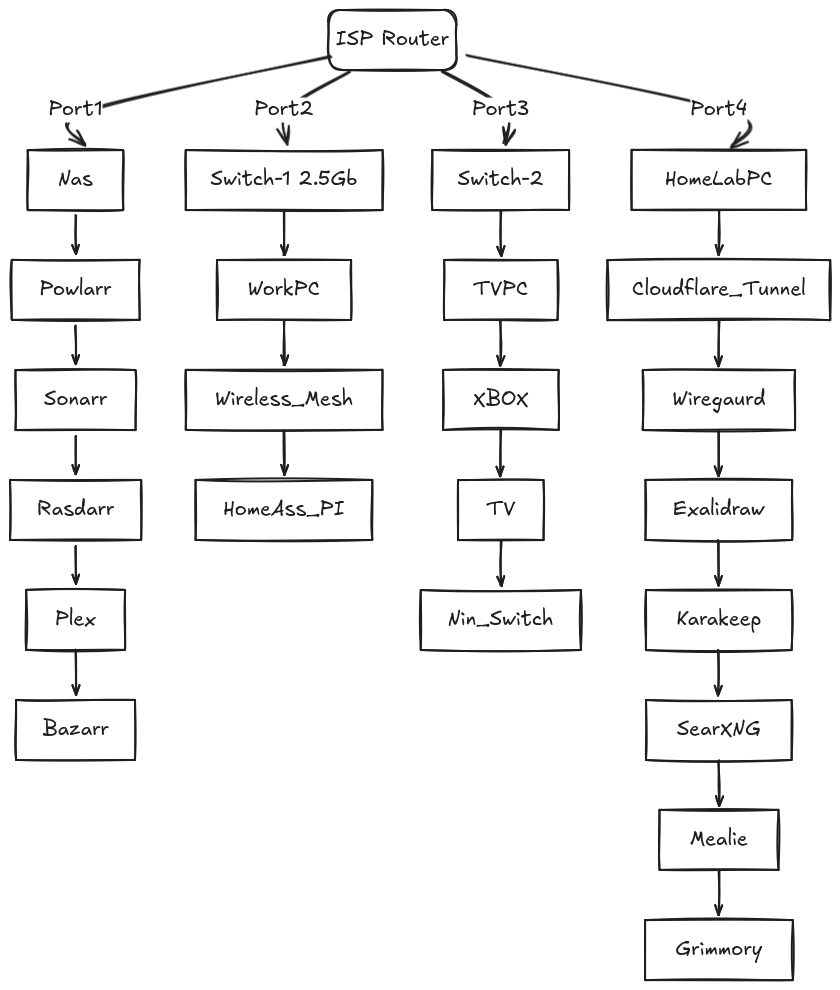
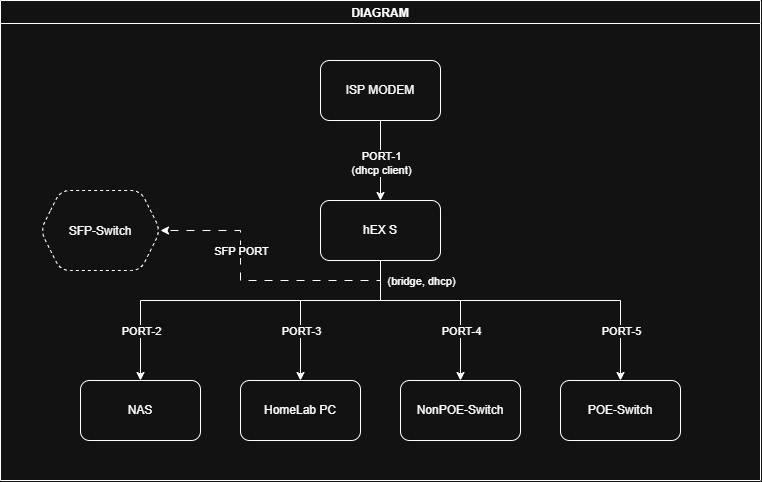
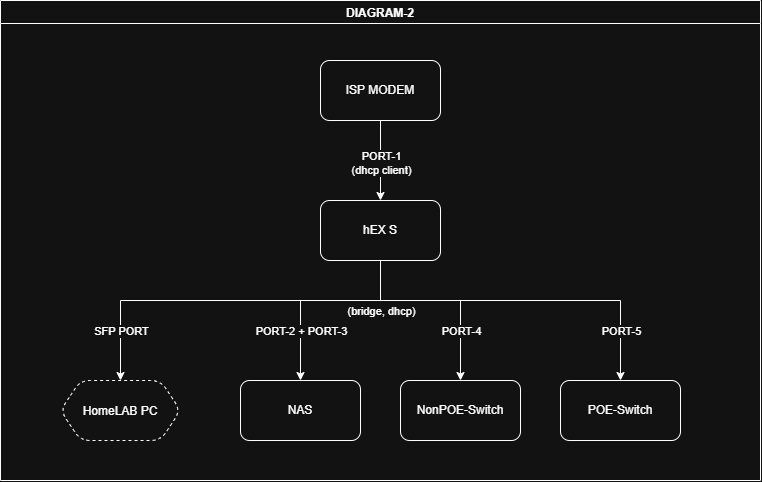
I have created a simple image, with what I have now and I would like to ask for a lot of help.
Is here a good place for that, as I would like to script most of what I do. Not use the GUI.
As they will be some really dumb questions?
My intent to understand more and also not use the ISP modem as a router and use the Mikrotik instead.
So I hope it makes some sense, ISP modem/Router has 4 ports.
All have cables, the wireless mesh just for the WIFI so, phones, tablets, and HomeAssient decices
I have 2 switches connected to 2 of the routers ports.
So I am thinking what the first good step, as I need to plug in the Mikrotik as I need a port.
As I said I want to script all of the work to create the network how I want, and I assume that is possible.
So is this forum a good place for dumb questions, so tolerant of dumb people?
and to script everything so it is reproducible when i make mistakes?
regards,
Tek
My thoughts as well . . . . The basic MikroTik router config does this pretty much out of the box . . . I see no mentions of VLANs or other more advanced features or subnetting. As long as the ISP will work with the MikroTik, you are close to done.
So, not sure your addressing/DHCP/?? setup, but that might need tweaking to align with what you have (default on Mikrotik is 192.168.88.x).
I realize that you are GUI-averse, but one thing you can do, is test getting things how you want them, and then export the config - it will give the specific CLI commands, and you can use that to help learn the platform along with the docs (the docs at times can be vague regarding some use cases).
We will gladly assist here as well, but as others have noted, don't expect the community to do all the work for you. (There are also excellent videos on YouTube . . . the trick is to find ones that relate to the current software - many are deprecated and will only confuse you more.)
That is a great bit of help already I didn't know that.
I did miss sharing some info, I do use port forwarding(plex and nas sync) and DHCP with mac addresses.
I don't use vlans as I don't understand yet.
I did plug the mikrotik in but I had a lot I just could get working, got lost very quickly.
Followed a youtube video and got something up but then was missing lots of other services.
So will start again bit by bit and this time try and make sense, so the headline "a little knowledge is a dangerous thing"
The problem I know am struggling with and that is way to deal with multiple networks.
So the ISP router gives a DHCP request an range 192.168.178.0/24
Then I will setup the Mikrotek to give 192.168.78.0/24 then slowly move stuff from ISP to Mikrotek.
With the intent to make the ISP a bridge and Mitrotek the router.
And this is where I struggled, how does the devices on one network to able to work with the other.
I seem to have to do "something" so the ISP and/or Mikrotik know they both exist.
As you can see I miss something in my understanding..
In the "stock" router config, the ISP would be the "WAN" device, which would by default be on MikroTik ether1, and run a dhcp client which should pick up an IP from the ISP. All other ports will be on the bridge, on the "LAN" side, and will have a dhcp server offering 192.168.88.x block addresses on all ports but ether1.
(Interfaces are assigned to LAN or WAN via "interface list", and the groups drive what firewall rules get applied.)
If you run different internal IP's, you will need to edit the local bridge IP (in "IP/Addresses" to what your router needs to be on, and adjust the dhcp server to offer your range.
At this point, I would expect basic connectivity to be there. (It will actually be there prior to these changes, just on the other IP block.)
Start small, and build. While there are others who are also likely good, I have found that the vids from "TheNetworkBerg" on YouTube are very good, and written for RouterOS 7 (a lot are for ROS 6, which are not terribly useful since there have been lot of changes.)
The stock config will route between the LAN and WAN side by default, but will NAT/masquerade the LAN to the WAN for security.
Draw a network diagram together with IP addresses (static) and plan for DHCP clients in the network
Go through the basics - use the default config as reference and try to understand, what is going on there (especially /ip/address/, /ip/dhcp-client and /ip/dhcp-server. You can use export command to see the current configuration.
Try to modify the configuration according to your preferences and test everything thoroughly during the process (it takes time, but it is worth it, trust me!)
once your local network works like you want it to work, go to the next stage - firewall. you need to understand Filter rules (and chains - especially input and forward) and NAT (srcnat and dstnat)
when you are sure that your firewall is OK, just try to place the MikroTik right between your ISP router and your network. Now the local network should be working without any problems and if you have set up everything correctly, you also should have internet connection (NATted yet, not bridged)
then try to change your ISP router/modem configuration to bridge mode and be prepared to set up PPPoE Client, because probably you will need it
It takes time, but don't worry, once you have any problem, you can always ask here (ideally specific questions, not general ones).
And don't forget to use https://manual.mikrotik.com and AI before you give up.
PS: Never trust AI without confirmation and always check what it has produced.
Cannot add much to what has been already provided. I would use vlans to securely distribute subnets within your network.
I would use an offbridge port to originally configure the router and then to keep a safe spot to access the router if something burps on the bridge itself. We are the authors of our own demise many times when 'adjusting the config' ;-).
So you need a good plan before laying out a single script.
This entails a very good and detailed network plan / diagram.
You need to capture all the required/needed data flows between users and devices and the internet including the admin. It should be self-evident when looking at your detailed diagram.
The config simply reflects the diagram..........
Finally the GUI is your friend, and using the NEW TERMINAL in winbox is a godsend to quickly see the entire config in one shot and to confirm changes have been made. Use it read it, and before you know it you will find your inner gui geek. Not to say you will be able to write code but understanding what you are seeing is half the battle, especially for troubleshooting. Dont be shy to use comments to communicate to yourself the reason for any line of script..........