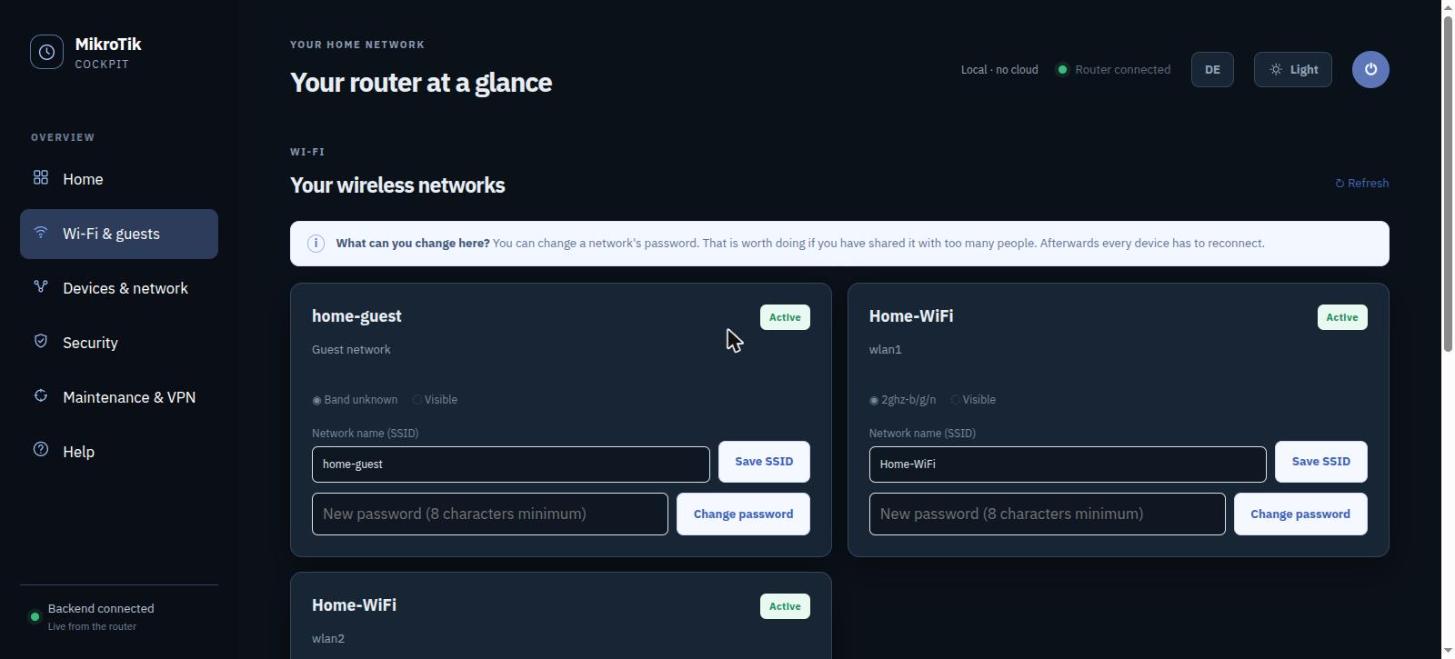
A small local UI for the everyday RouterOS tasks that scare beginners off WinBox /open source, SSH only, feedback wanted

Hello,

when I started with MikroTik at home, the hard part was not RouterOS itself. It was finding the handful of everyday things in WinBox: where the Wi-Fi password lives, why a port forward needs both a NAT and a filter rule, and which click would lock me out. WinBox is excellent once you know the tree. Before that, it is a wall, and I know a few people at home and at work who are standing in front of that wall right now.

So I built a small local UI for exactly those everyday jobs, for them and for the version of me from a few years ago. It is on GitHub under AGPL:

GitHub - BreuerM1975/mikrotik-cockpit: Local browser UI for MikroTik RouterOS β€” plain-language explanations, safety warnings, device direct links. Think WinBox, but for the 80 % of daily tasks. Β· GitHub

What it does:

  • Runs entirely on your own machine and talks to the router over SSH. No cloud, no account, no telemetry, and it never stores router credentials β€” you type them in each session, like WinBox.
  • Covers the everyday basics: router status, DHCP leases with manufacturer lookups, Wi-Fi SSID and password, port forwards with conflict detection, IP/DNS/DHCP settings, backups, and a plain-language security check.
  • Explains each setting next to the control instead of just showing the raw RouterOS field, and warns before anything that can disconnect you.
  • Changing the Wi-Fi password gives you a 5-minute undo window, in case devices stop connecting.
  • English and German interface, following the browser language.

What it is not: a WinBox replacement. VLAN design, routing, CAPsMAN, queues and troubleshooting belong in WinBox, and the idea is that people grow into WinBox from here, not that they avoid it.

Honest limitations:

  • Linux only for now. A Windows package exists only as a plan.
  • No Safe Mode β€” RouterOS drops the SSH session when you enter it, so every change applies immediately. The UI says so instead of hiding it.
  • Tested against RouterOS 7.23.1 on a hAP ac Lite. Other device families are untested, and I would genuinely like to know where it breaks.
  • 218 backend tests pass, but "tests pass" is not the same as "safe on your router".

Please try it on a lab device first, or at least keep a current backup and a second way in.

What I would find most useful: if you help beginners with MikroTik, which question do you get asked most often? Which everyday task should be on the first screen? And where would an explaining UI be actively worse than just showing the RouterOS field?

I'm too far up the learning curve for this, but I am impressed with your clarity on what it is and what it is not.

Does it overcome the limitations of Quick Set? ie Can it work with a configuration which has already been set with WinBox or WebFig, without reverting settings unobserved?

Overall, I am not sure what the place for the software would be: Is it adequate for ordinary users who are just dissatisfied with the wireless on the ISP supplied router but don't want to get involved beyond setting SSIDs and a guest network and setting up their own DHCP? If your software can meet the needs of this market, perhaps it opens up choices for them other than consumer orientated routers.

Thank you, and both questions go straight to the point.

Quick Set: It does not do what Quick Set does. There is no template and no "apply everything" step. Each time you open a page it reads the live state from the router (print terse), and each action is one targeted command on the object you clicked: set on that wireless interface's SSID or password, set on the DNS servers, set on the IP address of that interface. Where it creates something new (a port forward, a DHCP range, a static lease) it names the object cockpit-… and only ever removes objects it created itself, found by that name. It never runs Quick Set, never loads defconf, never touches a rule or interface you built in WinBox unless you point at it. So: yes, it works on an existing configuration, and nothing is reverted behind your back.

Two honest limits on that: it does not "repair" an existing configuration either, and a DHCP server it did not create (for example the one from the default config) is shown with its leases, but not edited; Cockpit adds its own, tagged one next to it. And since RouterOS drops the SSH session when entering Safe Mode, changes apply immediately. Thβ–Ž Thank you, and both questions go straight to the point.

Quick Set: It does not do what Quick Set does. There is no template and no "apply everything" step. Each time you open a page it reads the live state from the router (print terse), and each action is one targeted command on the object you clicked: set on that wireless interface's SSID or password, set on the DNS servers, set on the IP address of that interface. Where it creates something new (a port forward, a DHCP range, a static lease) it names the object cockpit-… and only ever removes objects it created itself, found by that name. It never runs Quick Set, never loads defconf, never touches a rule or interface you built in WinBox unless you point at it. So: yes, it works on an existing configuration, and nothing is reverted behind your back.

Two honest limits on that: it does not "repair" an existing configuration either, and a DHCP server it did not create (for example the one from the default config) is shown with its leases, but not edited; Cockpit adds its own, tagged one next to it. And since RouterOS drops the SSH session when entering Safe Mode, changes apply immediately. The UI says so, and there is a backup button on the same screen.

Ordinary users: Partly, today. For the person you describe, on a hAP that already has internet through the default config, the public version covers SSID and password (both the legacy wireless and the wifi package), DHCP ranges and fixed addresses, DNS, backups, port forwards and the security check. What it does not cover in this repository is exactly two things you named: guest network on/off, and PPPoE as the WAN login. Both exist, but in the part I have kept separate for a paid tier later. I would rather say that plainly than let someone install it and find out.

Your framing is the one I had in mind: not replacing WinBox for people who know it, but giving people who would otherwise buy a consumer box a way to run a MikroTik without learning the tree first.e UI says so, and there is a backup button on the same screen.

Ordinary users: Partly, today. For the person you describe, on a hAP that already has internet through the default config, the public version covers SSID and password (both the legacy wireless and the wifi package), DHCP ranges and fixed addresses, DNS, backups, port forwards and the security check. What it does not cover in this repository is exactly two things you named: guest network on/off, and PPPoE as the WAN login. Both exist, but in the part I have kept separate for a paid tier later. I would rather say that plainly than let someone install it and find out.

Your framing is the one I had in mind: not replacing WinBox for people who know it, but giving people who would otherwise buy a consumer box a way to run a MikroTik without learning the tree first.

Like mikrodash....

Are you aware of the naming conflict?

Perhaps you can turn that to your advantage: recast this as a Cockpit plugin, giving your tool broader reach.

MikroDash is a great monitoring dashboard, but it's a different job: it shows you what the router is doing. MikroTik Cockpit is for changing things without WinBox: Wi-Fi password, guest network, a plain-language security check, and every change comes with an undo. Read-only vs. operate, if you like. Both can run side by side.

Good point, I'm aware of the Cockpit Project. That's why it's always "MikroTik Cockpit" in full, never just "Cockpit". A Cockpit plugin is an interesting idea for people who already run a Linux server with Cockpit, but my target group is the home network with one router and no server at all, so it stays a standalone tool for now. I'll keep the plugin idea on the list, thanks.