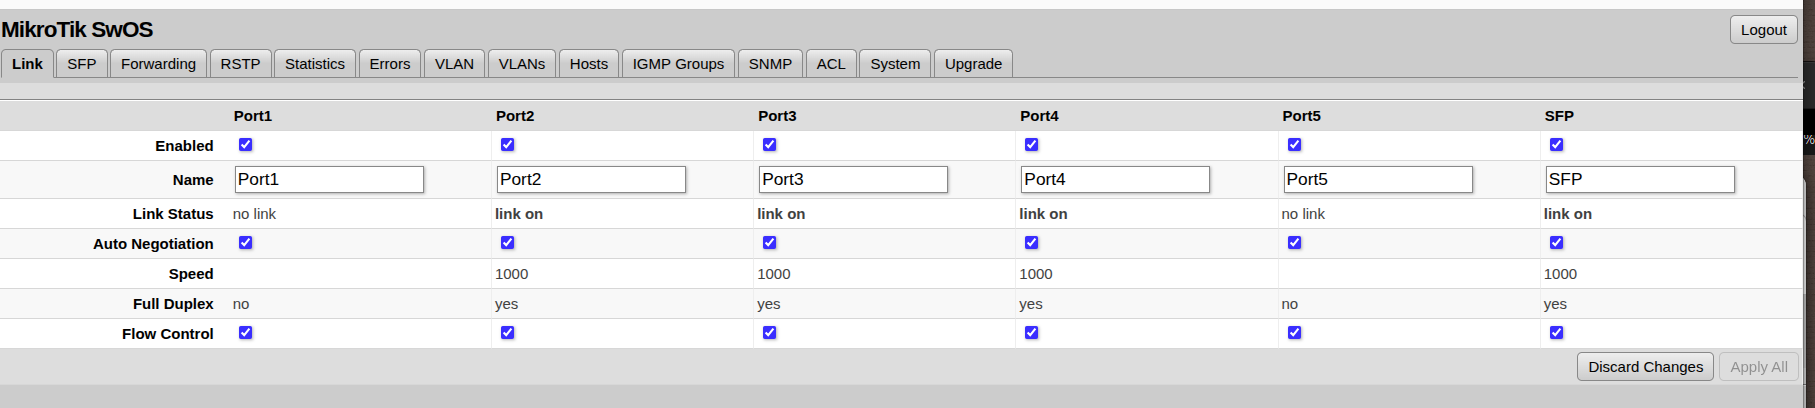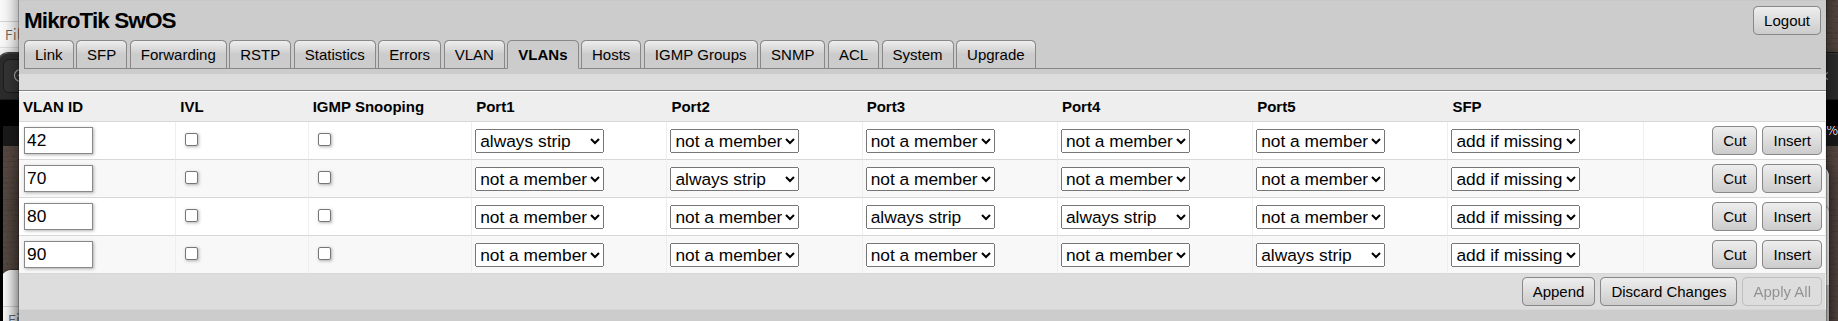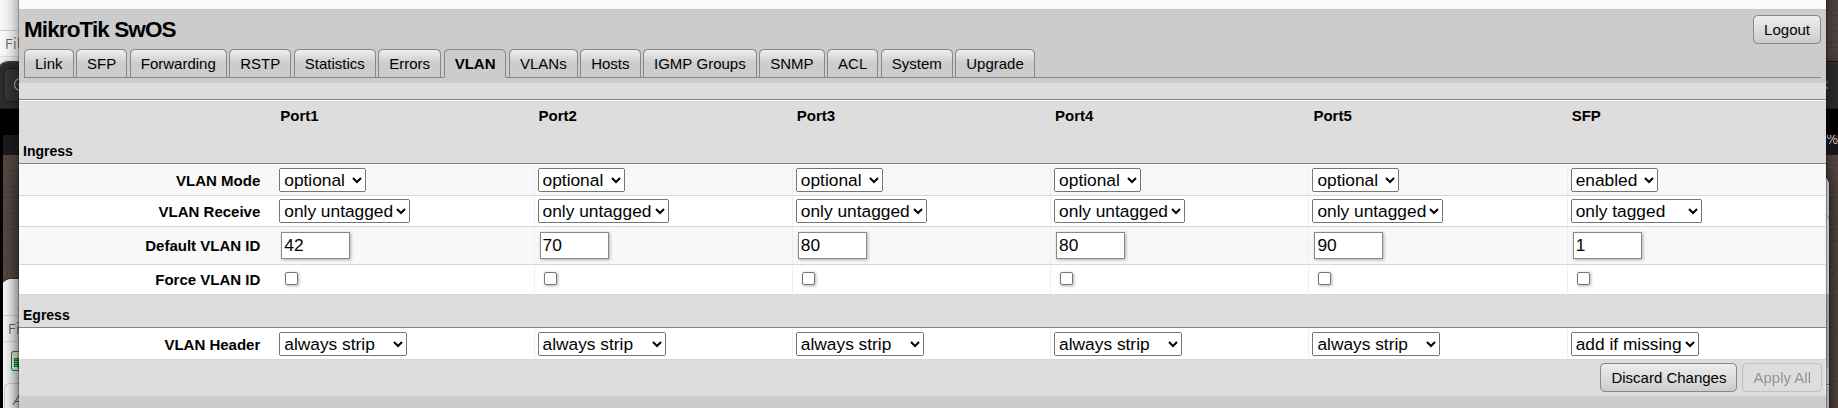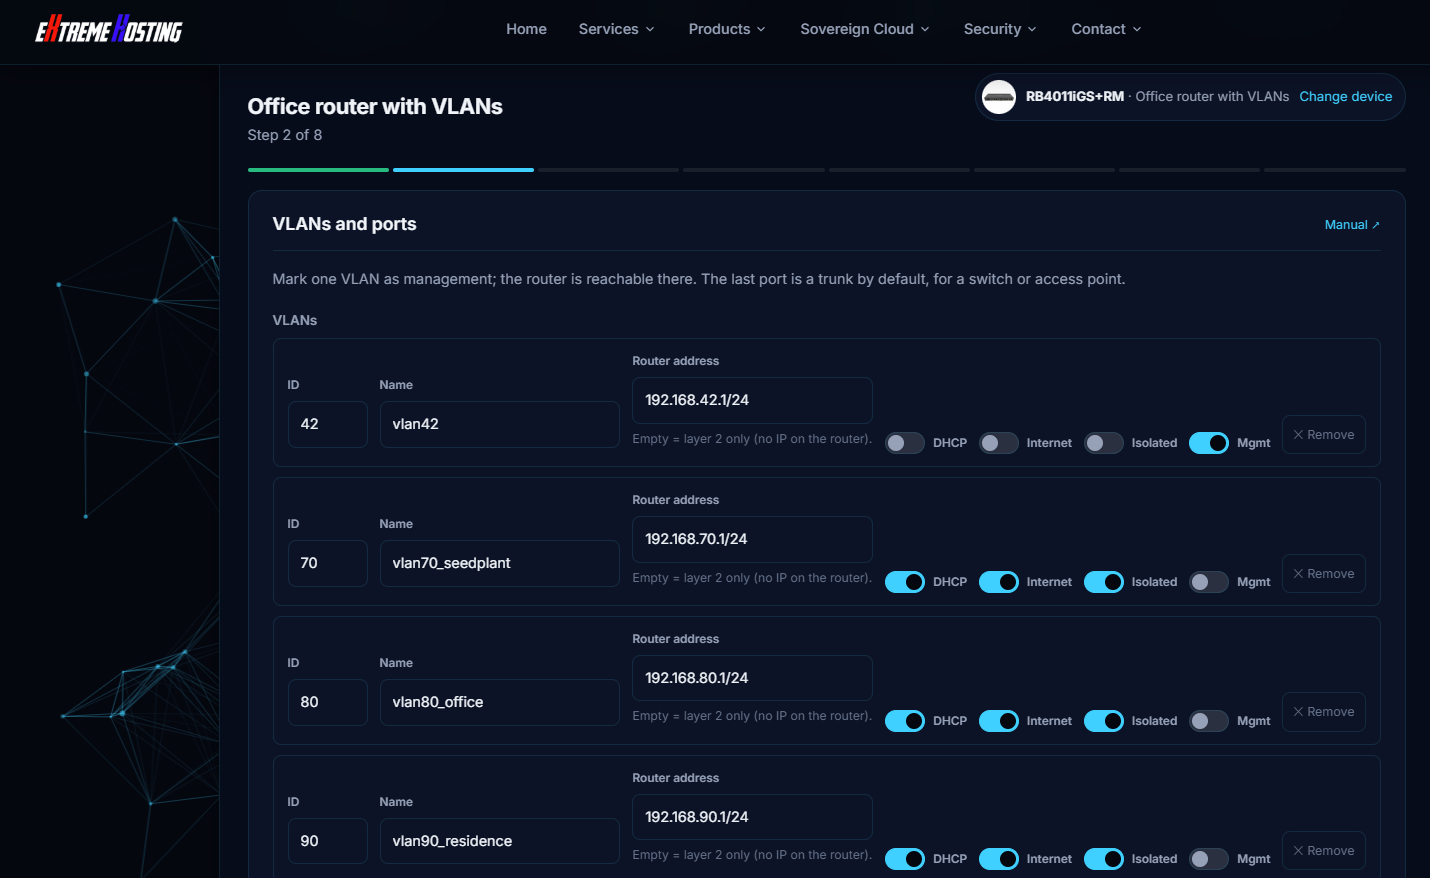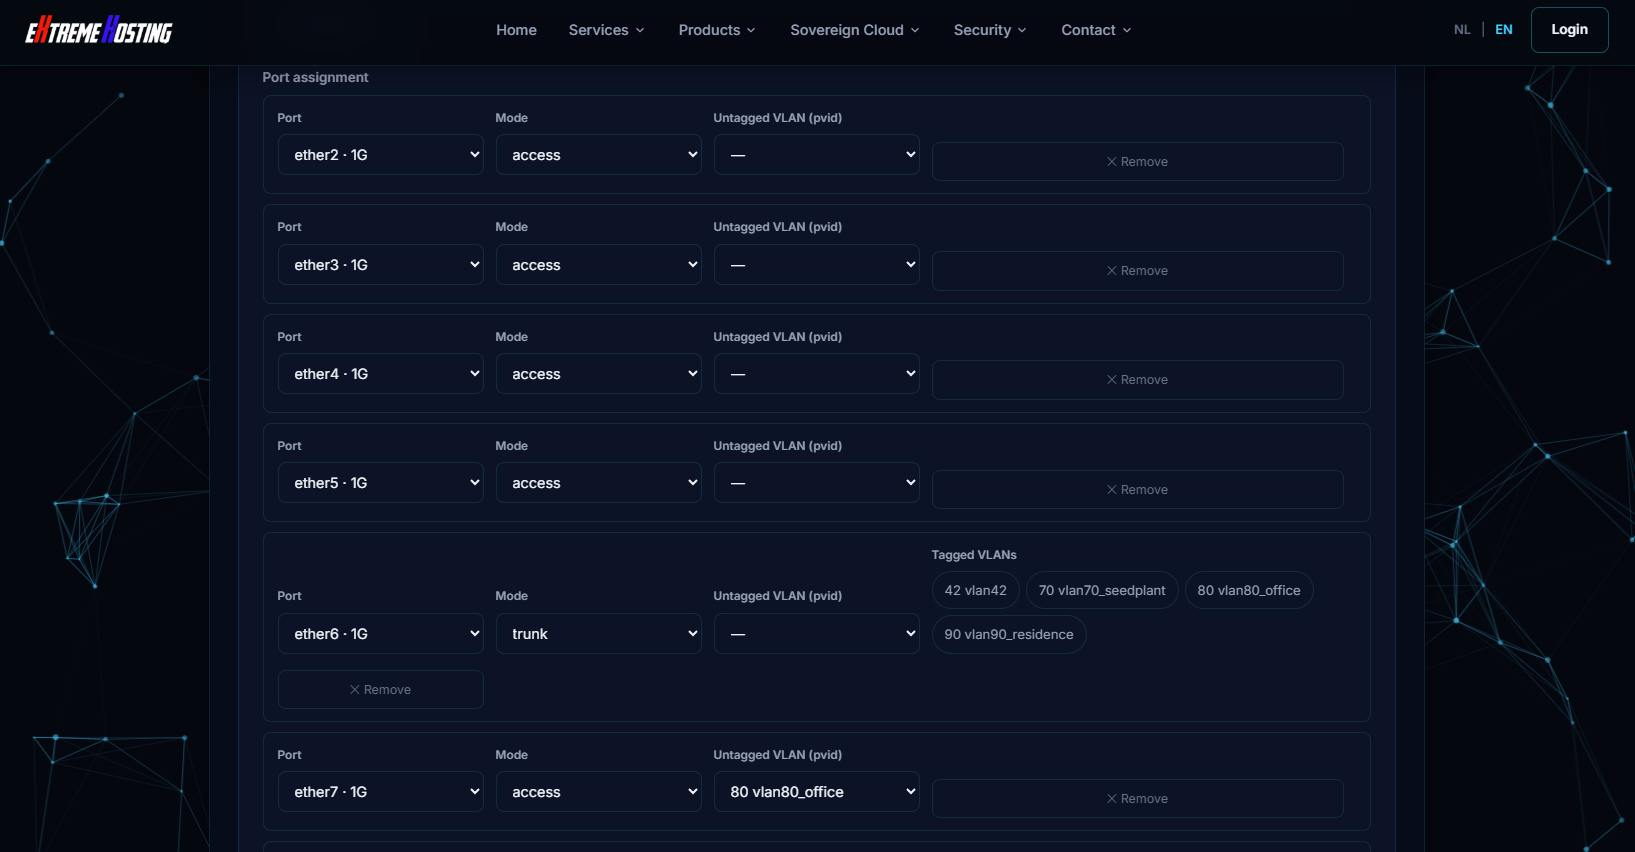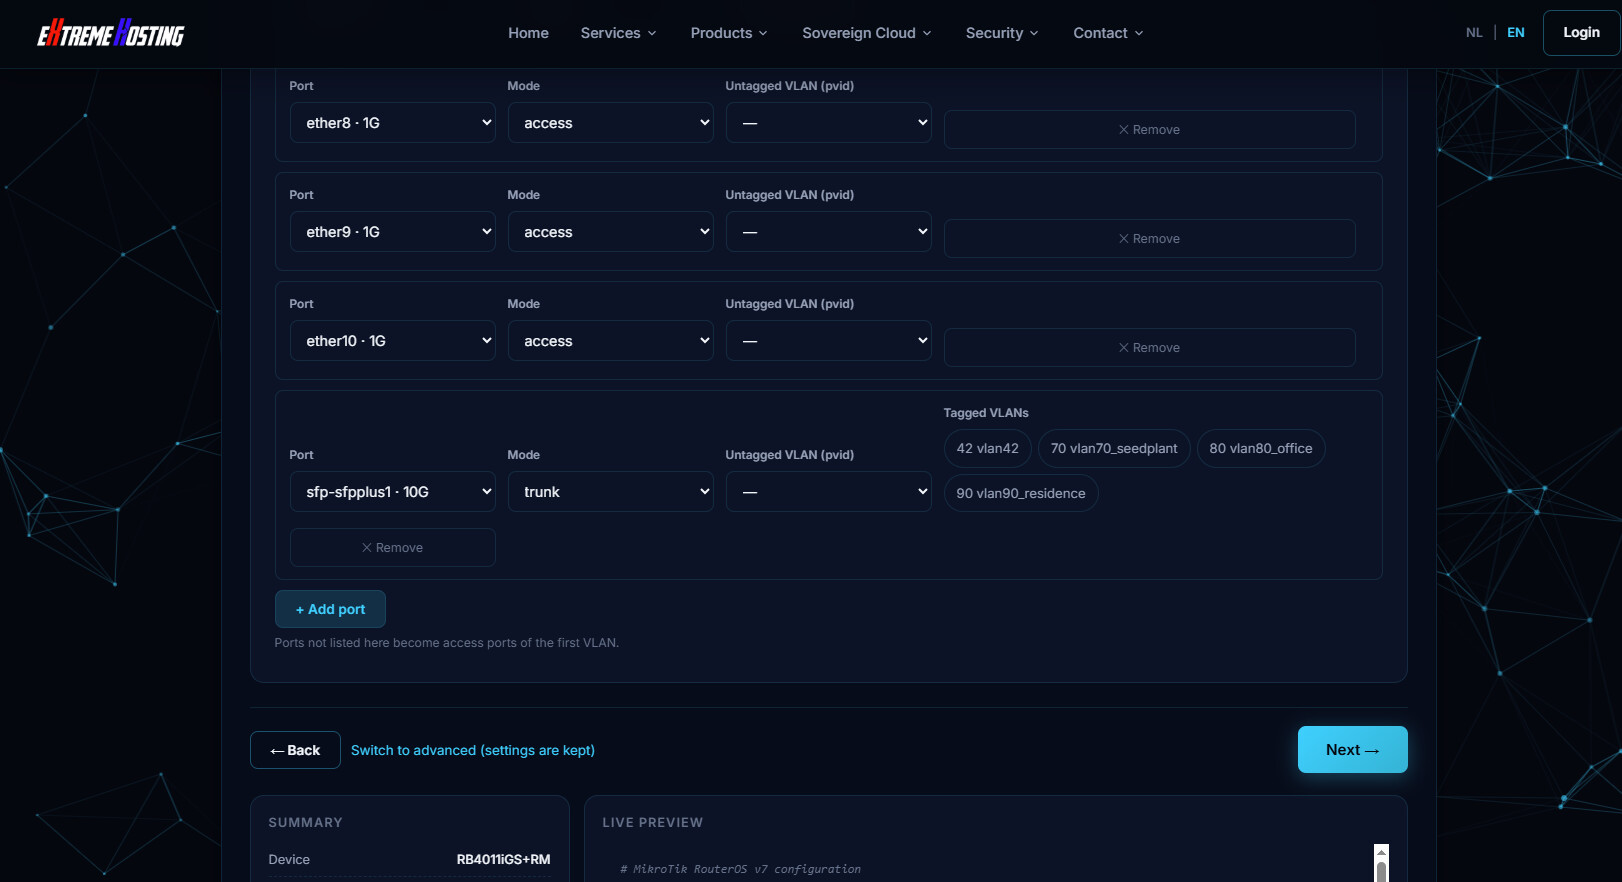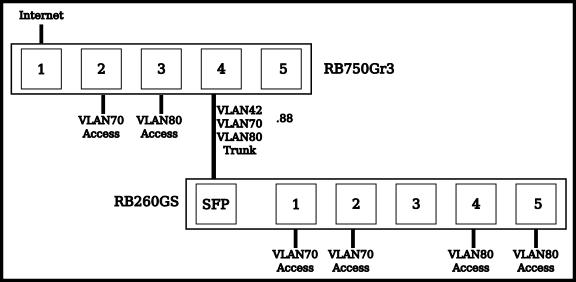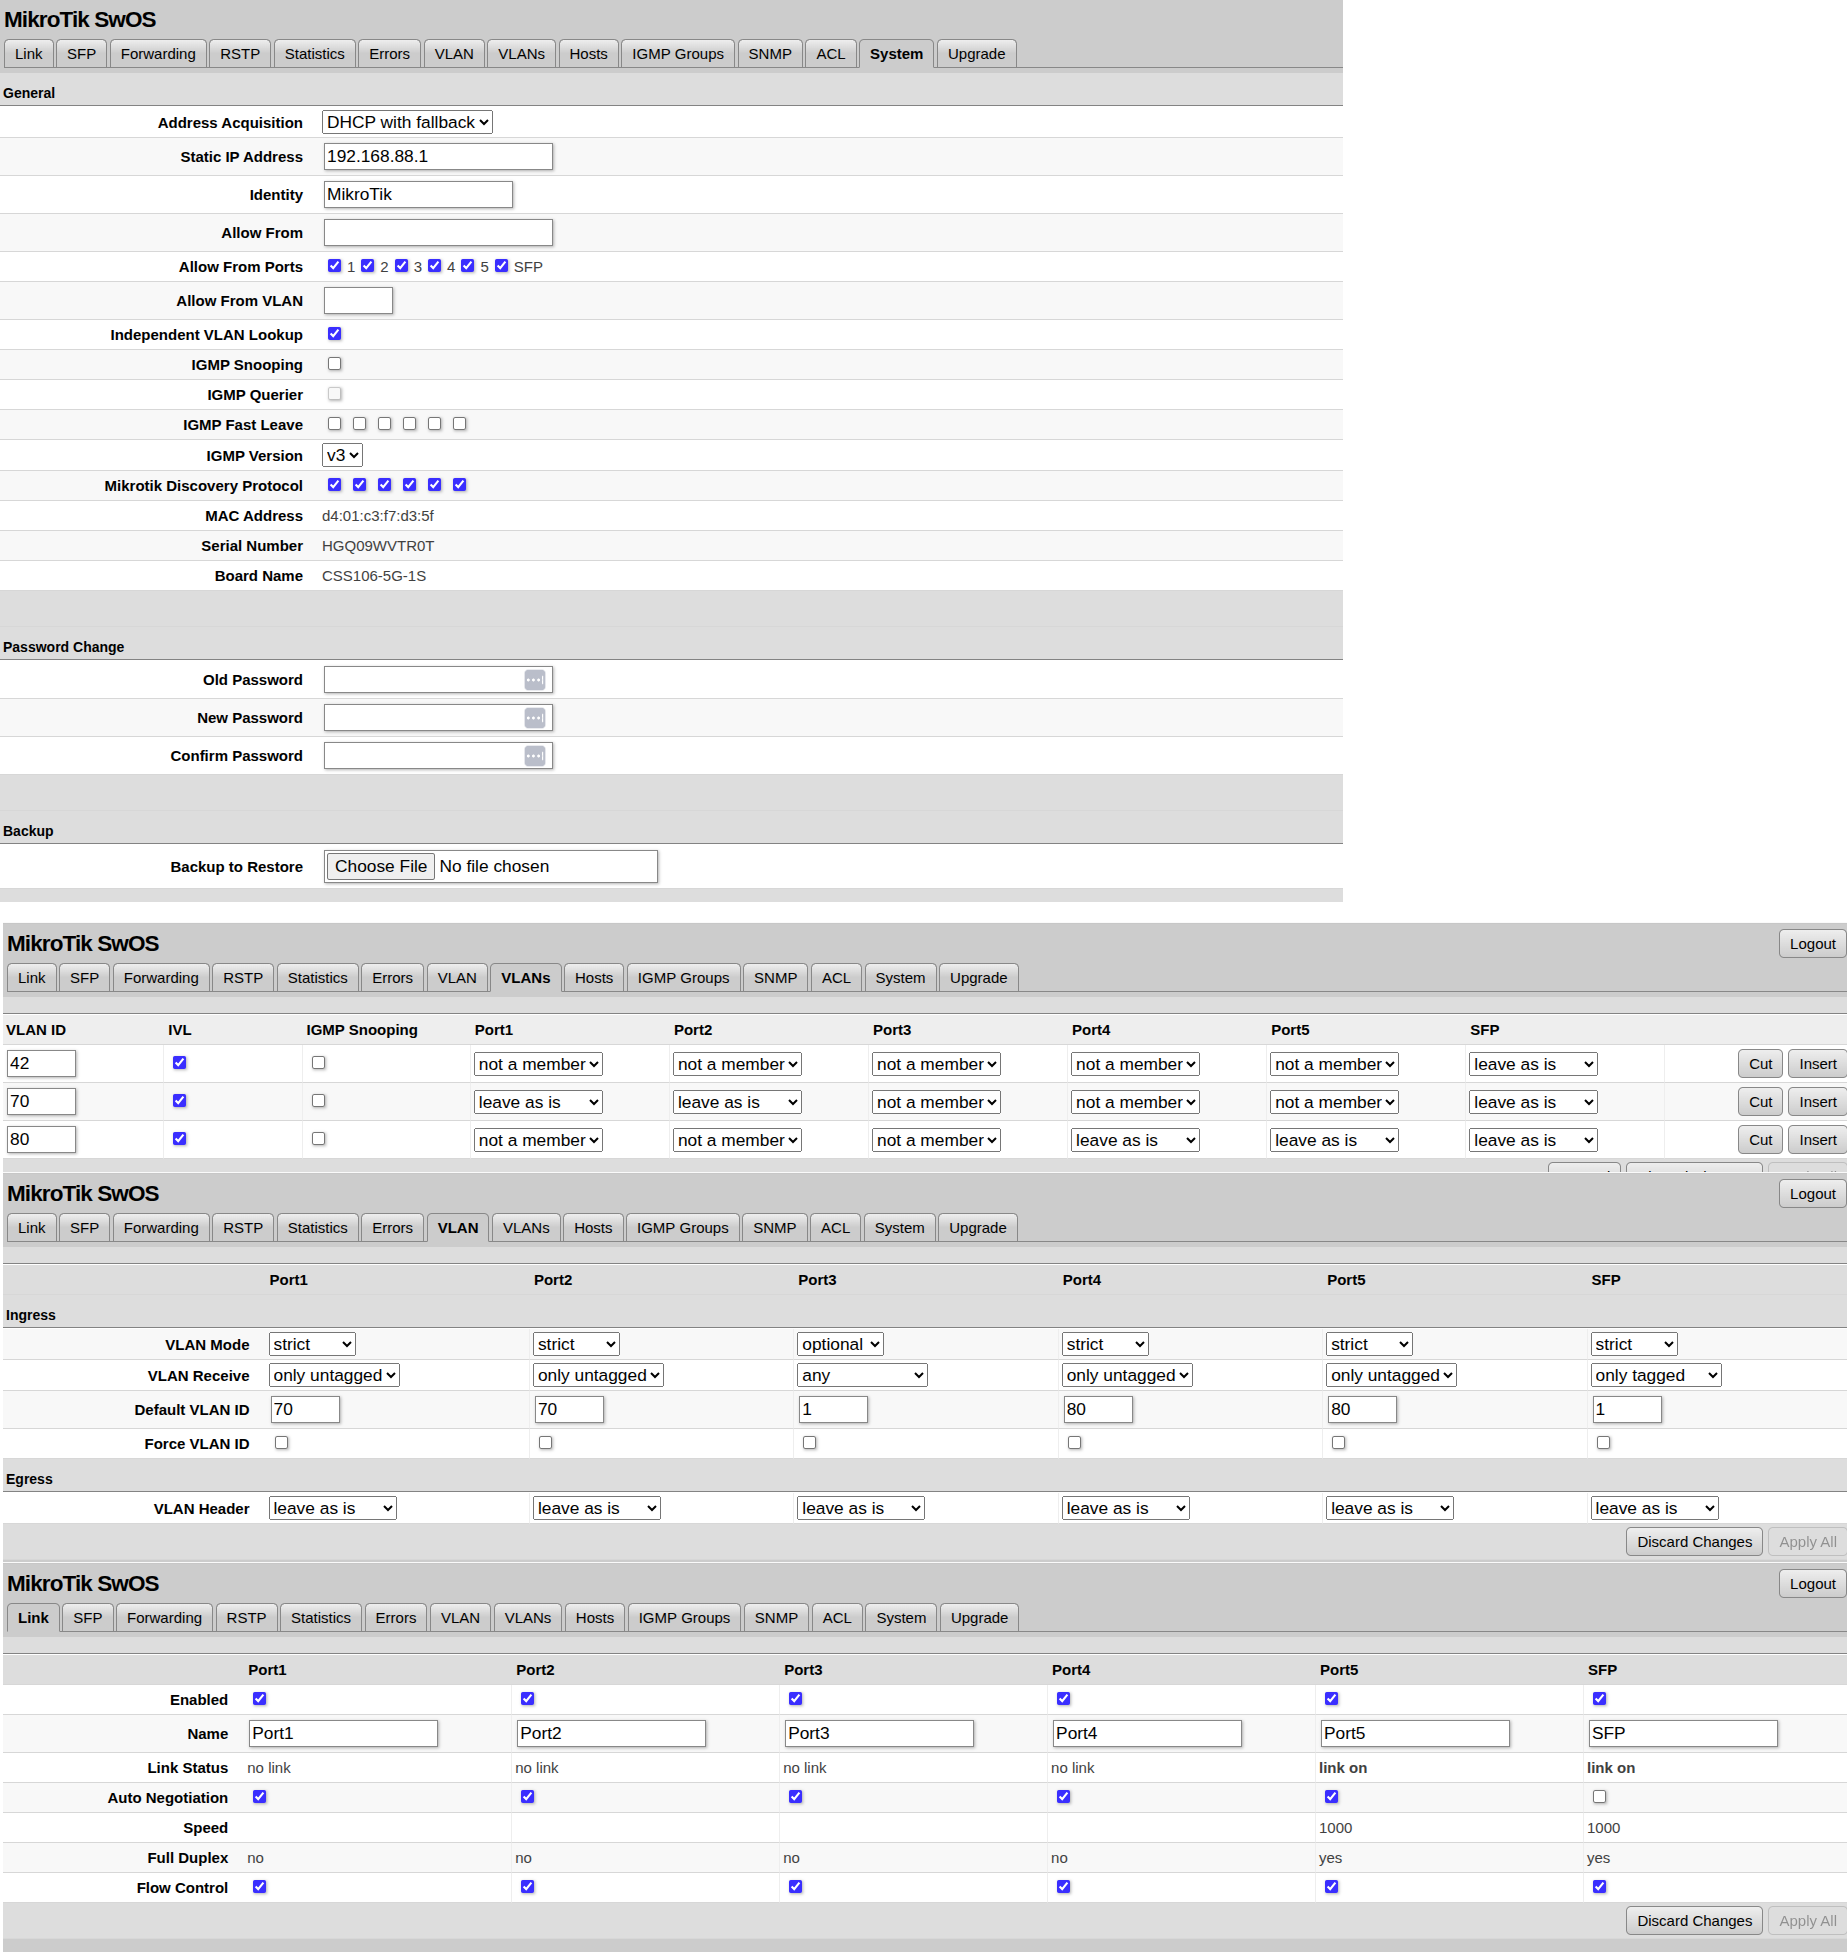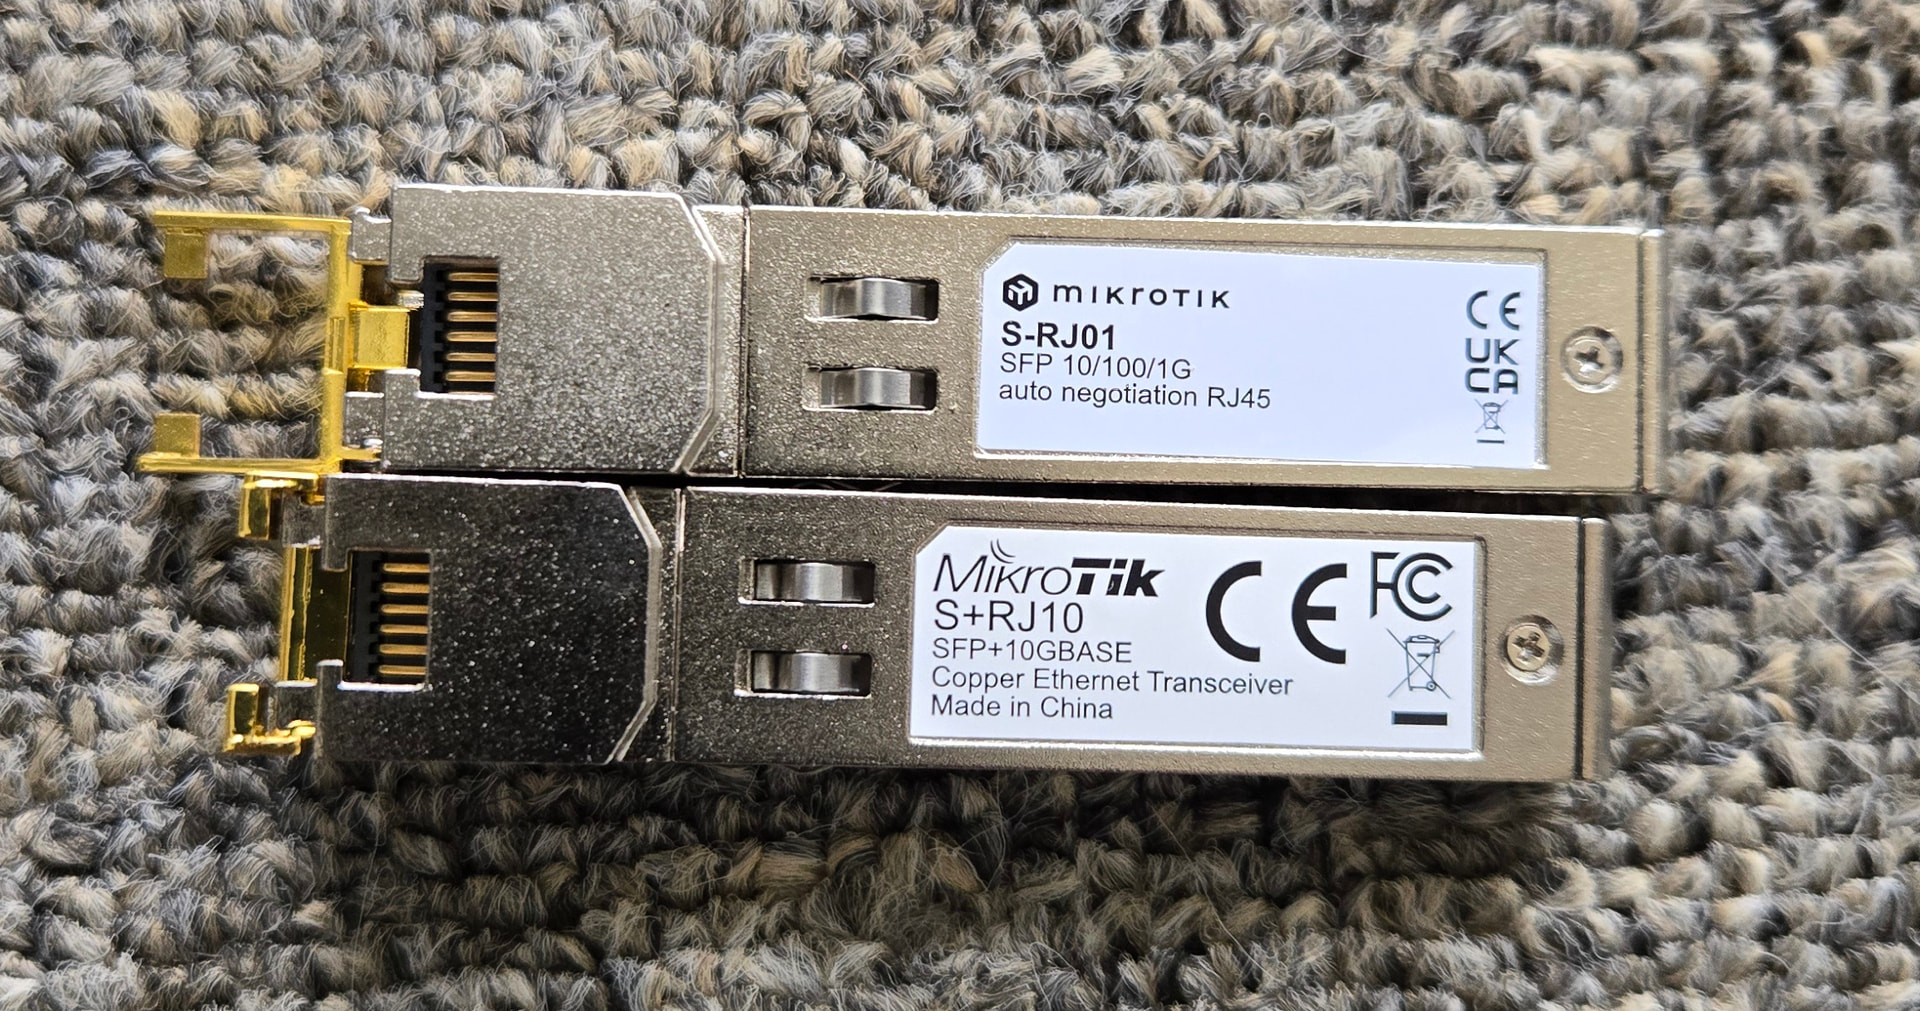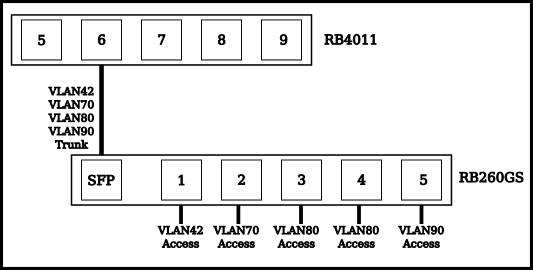
I have spent considerable time trying to configure the RB4011 router and RB260 switch to support a trunk between port 6 connected via CAT6 cable to copper media converter in SFP port.
My test is getting DHCP to be available at ports 3 & 4. I've confirmed DHCP is not working on any vlans with the expection of vlan42 it doesn't have dhcp.
The router is in a dev environment. It has internet access from 192.168.2.0/24 subnet. The switch was working just as a standalone switch on the same subnet with no vlans. It is currently running swos ver 2.18
I've made this type of configuration in August 2025 when I first started building the network. I shared some of my finding in a post in this forum. For the life of me, I can't figure out what I am doing or not doing that is preventing this from working.
I've attached parts of the router export and three screen shots for the switch. After two days off-and-on working on this with not success, I could use some help. Maybe a fresh pair of eyes will see my mistake.
# 2026-08-22 18:35:31 by RouterOS 7.20.4
# software id =
#
# model = RB4011iGS+5HacQ2HnD
# serial number =
/interface bridge
add admin-mac= auto-mac=no comment=defconf name=bridge \
    port-cost-mode=short

add comment=residence_VLAN name=bridge_VLAN vlan-filtering=yes
add comment=development_subnet name=bridge_dev

add comment="guest wifi build" name=guest-bridge
/interface wireless
set [ find default-name=wlan2 ] band=5ghz-a/n/ac comment="guest wifi build" \
    country=canada default-forwarding=no disabled=no distance=indoors \
    frequency=5720 installation=indoor mode=ap-bridge name=wlan1 ssid=\
    RRS_Guest_5G_bck wireless-protocol=802.11
set [ find default-name=wlan1 ] band=2ghz-b/g/n comment="guest wifi build" \
    country=canada default-forwarding=no disabled=no distance=indoors \
    frequency=2462 mode=ap-bridge name=wlan2 ssid=RRS_Guest_2G_bck \
    wireless-protocol=802.11
/interface ethernet
set [ find default-name=ether10 ] comment="offbridge build" name=OFFBridge
set [ find default-name=ether1 ] comment=ISP
set [ find default-name=ether9 ] comment=res_VLAN_trunk
set [ find default-name=sfp-sfpplus1 ] auto-negotiation=no comment=\
    SP_VLAN_trunk disabled=yes speed=1G-baseT-full
/interface wireless manual-tx-power-table
set wlan1 comment="guest wifi build"
set wlan2 comment="guest wifi build"
/interface wireless nstreme
set wlan1 comment="guest wifi build"
set wlan2 comment="guest wifi build"

/interface vlan
add comment=VLAN42 interface=bridge_VLAN name=vlan42 vlan-id=42
add comment=VLAN70 interface=bridge_VLAN name=vlan70 vlan-id=70
add comment=VLAN80 interface=bridge_VLAN name=vlan80 vlan-id=80
add comment=VLAN90 interface=bridge_VLAN name=vlan90 vlan-id=90
/interface list
add comment=defconf name=WAN
add comment=defconf name=LAN
/interface wifi channel
add band=5ghz-ax frequency=5180 name=5GHZ::CH36 width=20mhz
add band=5ghz-ax frequency=5200 name=5GHZ::CH40 width=20mhz
add band=5ghz-ax frequency=5220 name=5GHZ::CH44 width=20mhz
add band=5ghz-ax frequency=5240 name=5GHZ::CH48 width=20mhz
add band=5ghz-ax frequency=5745 name=5GHZ::CH149 width=20mhz
add band=5ghz-ax frequency=5765 name=5GHZ::CH153 width=20mhz
add band=5ghz-ax frequency=5785 name=5GHZ::CH157 width=20mhz
add band=5ghz-ax frequency=5805 name=5GHZ::CH161 width=20mhz
add band=5ghz-ax frequency=5825 name=5GHZ::CH165 width=20mhz
add band=5ghz-ax disabled=no frequency=5180,5200,5220,5240 name=5GHZ::UNII-1 \
    width=20mhz
add band=5ghz-ax disabled=no frequency=5745,5765,5785,5805,5825 name=\
    5GHZ::UNII-3 width=20mhz
add band=5ghz-ax disabled=no frequency=\
    5180,5200,5220,5240,5745,5765,5785,5805,5825 name=5GHZ::NON-DFS width=\
    20mhz
add band=2ghz-ax frequency=2412 name=2GHZ::CH1 width=20mhz
add band=2ghz-ax frequency=2437 name=2GHZ::CH6 width=20mhz
add band=2ghz-ax frequency=2462 name=2GHZ::CH11 width=20mhz
add band=2ghz-ax disabled=no frequency=2412,2437,2462 name=2GHZ::AUTO width=\
    20mhz
/interface wireless security-profiles
set [ find default=yes ] authentication-types=wpa-psk,wpa2-psk comment=\
    "guest wifi build" mode=dynamic-keys supplicant-identity=MikroTik
/ip pool
add name=default-dhcp ranges=192.168.88.10-192.168.88.254
add comment="guest wifi build" name=guest-pool ranges=\
    192.168.99.200-192.168.99.254
add comment=seedplant_subnet name="pool 70" ranges=\
    192.168.70.200-192.168.70.254
add comment=office_subnet name="pool 80" ranges=192.168.80.200-192.168.80.254
add comment=residence_subnet name="pool 90" ranges=\
    192.168.90.200-192.168.90.254
add comment="l2tp config" name=l2tp-pool ranges=192.168.50.200-192.168.50.254
add comment=development_subnet name="pool 2" ranges=\
    192.168.2.200-192.168.2.254
add name=dhcp_pool8 ranges=192.168.121.200-192.168.121.254
/ip dhcp-server
add address-pool=default-dhcp interface=bridge name=defconf
add address-pool=guest-pool comment="guest wifi build" interface=guest-bridge \
    name=guest-server
add address-pool="pool 2" comment=development_subnet interface=bridge_dev \
    name="server 2"
add address-pool="pool 90" comment=VLAN90 interface=vlan90 name=dhcp_vlan90
add address-pool="pool 70" comment=VLAN70 interface=vlan70 name=dhcp_vlan70
add address-pool="pool 80" comment=VLAN80 interface=vlan80 name=dhcp_vlan80

/port
set 0 name=serial0
set 1 name=serial1
/ppp profile

/snmp community

/system logging action
set 1 disk-file-count=3 disk-lines-per-file=4096
/certificate settings
set builtin-trust-anchors=not-trusted
/disk settings
set auto-media-interface=bridge auto-media-sharing=yes auto-smb-sharing=yes
/interface bridge port
add bridge=bridge comment=defconf interface=ether2 internal-path-cost=10 \
    path-cost=10

add bridge=guest-bridge comment="guest wifi build" interface=wlan1 \
    internal-path-cost=10 path-cost=10
add bridge=guest-bridge comment="guest wifi build" interface=wlan2 \
    internal-path-cost=10 path-cost=10
add bridge=bridge_dev comment=development_subnet interface=ether3
add bridge=bridge_VLAN comment=res_VLAN interface=ether9
add bridge=bridge_VLAN comment=off_VLAN interface=ether8
add bridge=bridge_VLAN comment=sp_VLAN interface=sfp-sfpplus1

add bridge=bridge_VLAN comment=sunroom interface=ether6
/ip neighbor discovery-settings
set discover-interface-list=none
/interface bridge vlan
add bridge=bridge_VLAN comment=VLAN90 tagged=ether9,bridge_VLAN,ether6 \
    vlan-ids=90
add bridge=bridge_VLAN comment=VLAN42 tagged=\
    ether9,sfp-sfpplus1,ether8,bridge_VLAN,ether6 vlan-ids=42
add bridge=bridge_VLAN comment=VLAN80 tagged=ether8,bridge_VLAN,ether6 \
    vlan-ids=80
add bridge=bridge_VLAN comment=VLAN70 tagged=sfp-sfpplus1,bridge_VLAN,ether6 \
    vlan-ids=70
/interface l2tp-server server
set authentication=mschap2 default-profile=l2tp-profile enabled=yes \
    use-ipsec=yes
/interface list member
add comment=defconf interface=bridge list=LAN
add comment=development_subnet interface=bridge_dev list=LAN
add interface=ether1 list=WAN
add comment=VLAN interface=bridge_VLAN list=LAN


/interface wireguard peers

/ip address
add address=192.168.88.1/24 comment=defconf interface=bridge network=\
    192.168.88.0
add address=192.168.69.1/30 comment="offbridge build" interface=bridge \
    network=192.168.69.0
add address=192.168.99.1/24 comment="guest wifi build" interface=guest-bridge \
    network=192.168.99.0
add address=192.168.2.1/24 comment=development_subnet interface=bridge_dev \
    network=192.168.2.0

add address=192.168.90.1/24 comment=VLAN90 interface=vlan90 network=\
    192.168.90.0
add address=192.168.42.1/24 comment=VLAN42 interface=vlan42 network=\
    192.168.42.0
add address=192.168.80.1/24 comment=VLAN80 interface=vlan80 network=\
    192.168.80.0
add address=192.168.70.1/24 comment=VLAN70 interface=vlan70 network=\
    192.168.70.0

/ip cloud
set ddns-enabled=yes ddns-update-interval=1h
/ip dhcp-client
add comment=defconf interface=ether1
/ip dhcp-server lease
add address=192.168.2.201 client-id=1:a0:ad:9f:87:ad:7c mac-address=\
    A0:AD:9F:87:AD:7C server="server 2"
add address=192.168.2.200 client-id=1:d4:93:90:16:5a:e8 mac-address=\
    D4:93:90:16:5A:E8 server="server 2"
add address=192.168.2.254 client-id=1:10:5a:95:c4:5a:5d mac-address=\
    10:5A:95:C4:5A:5D server="server 2"
/ip dhcp-server network
add address=192.168.2.0/24 comment=development_subnet dns-server=\
    192.168.2.199 gateway=192.168.2.1
add address=192.168.70.0/24 comment=seedplant_subnet dns-server=192.168.70.1 \
    gateway=192.168.70.1
add address=192.168.80.0/24 comment=office_subnet dns-server=192.168.80.1 \
    gateway=192.168.80.1
add address=192.168.88.0/24 comment=defconf dns-server=192.168.88.1 gateway=\
    192.168.88.1
add address=192.168.99.0/24 comment="guest wifi build" dns-server=\
    149.112.121.20,149.112.122.20 gateway=192.168.99.1
add address=192.168.121.0/24 dns-server=149.112.121.20,149.112.122.20 \
    gateway=192.168.121.1
/ip dns
set allow-remote-requests=yes servers=149.112.121.20,149.112.122.20
/ip dns static
add address=192.168.88.1 comment=defconf name=router.lan type=A
/ip firewall address-list

/ip firewall filter


/ip ipsec policy
# bad proposal
add comment=agriflow dst-address=192.168.80.0/24 peer=*2 proposal=*1 \
    src-address=192.168.2.0/24 tunnel=yes
/ip route
add comment=vlan80 disabled=no distance=1 dst-address=192.168.80.0/24 \
    gateway=wg1 routing-table=main scope=30 suppress-hw-offload=no \
    target-scope=10
add comment=vlan70 disabled=no distance=1 dst-address=192.168.70.0/24 \
    gateway=wg1 routing-table=main scope=30 suppress-hw-offload=no \
    target-scope=10
add comment=vlan90 disabled=no distance=1 dst-address=192.168.90.0/24 \
    gateway=wg1 routing-table=main scope=30 suppress-hw-offload=no \
    target-scope=10
add comment=vlan42 disabled=no distance=1 dst-address=192.168.42.0/24 \
    gateway=wg1 routing-table=main scope=30 suppress-hw-offload=no \
    target-scope=10

/ip service
set ftp disabled=yes
set ssh disabled=yes
set telnet disabled=yes
set www disabled=yes
set www-ssl certificate=
set api disabled=yes
set api-ssl disabled=yes
/ip ssh
set always-allow-password-login=yes
/ipv6 firewall filter
add action=drop chain=input comment="ipv6 removed"
add action=drop chain=forward comment="ipv6 removed"
/ppp secret

/snmp
set enabled=yes
/system clock
set time-zone-autodetect=no time-zone-name=
/system identity
set name=edgerouterbck
/system leds
add interface=wlan2 leds="wlan1_signal1-led,wlan1_signal2-led,wlan1_signal3-le\
    d,wlan1_signal4-led,wlan1_signal5-led" type=wireless-signal-strength
add interface=wlan2 leds=wlan1_tx-led type=interface-transmit
add interface=wlan2 leds=wlan1_rx-led type=interface-receive
/system logging
add action=disk topics=critical
add action=disk topics=error
add action=disk topics=info
add action=disk topics=warning
/system ntp client
set enabled=yes
/system ntp client servers
add address=ca.pool.ntp.org
/system routerboard settings
set enter-setup-on=delete-key
/system scheduler

/tool bandwidth-server
set authenticate=no enabled=no
/tool e-mail

/tool graphing interface
add disabled=yes interface=bridge
add interface=sfp-sfpplus1
/tool graphing resource
add
/tool mac-server
set allowed-interface-list=none
/tool mac-server mac-winbox
set allowed-interface-list=LAN
/tool mac-server ping
set enabled=no