Hi, I bought an HAP AX3 to use with a Behringer Wing mixer. Everything is working fine, except for access via the Wing-Q app on mobile phones; the app works with other routers, so does anyone have any idea what the issue might be?
Contact the app makers,
who will purchase a MikroTik router for testing.
Or contact support@mikrotik.com so they can purchase the mixer and use the app for testing.
Is this a guessing game?
If you need help from forum users, show the device configuration:
the output of the /export command on terminal, omitting the serial number and password, if any are visible.
The likelihood that someone has that mixer and uses that app is obviously very low here.
You should contact the manufacturer of the app or mixer...
Whatever happens, at most, here on the forum we can tell you to make hAP ax³ work in a compatible old-WiFi manner,
as the mixer might not support any of the latest nonsense and frills implemented in latest WiFi versions...
Or you've left your firewall on, or disabled IPv6, or something else, which is blocking communication between the app and the mixer.
Concur, the standard is to provide your config for review to see if anything you have setup may be blocking traffic...... If not then we can narrow it down to the app......
/export file=anynameyouwish ( minus router serial number, any public WANIP information, keys, dhcp lease lists)
Just go to Terminal menu selection in winbox and type the entry above. Download it and open in notepad++ do any deletions required and then post back here.
Thanks for your support , this is ouput export the device is only in local , no internet.
Gabriele
# 2026-08-26 18:24:33 by RouterOS 7.23.3
# software id = LJAN-6CBH
#
# model = RBD53iG-5HacD2HnD
# serial number = <REDACTED>

/interface bridge
add admin-mac=D0:EA:11:21:B9:E1 auto-mac=no comment=defconf dhcp-snooping=yes dhcpv6-snooping=yes fast-forward=no igmp-snooping=yes igmp-version=3 mld-version=2 multicast-querier=yes name=bridge
vlan-filtering=yes
/interface ethernet
set \[ find default-name=ether1 \] l2mtu=1598
set \[ find default-name=ether2 \] l2mtu=1598
set \[ find default-name=ether3 \] l2mtu=1598
set \[ find default-name=ether4 \] l2mtu=1598
set \[ find default-name=ether5 \] l2mtu=1598
/interface wireless
set \[ find default-name=wlan1 \] band=2ghz-b/g/n channel-width=20/40mhz-XX country=italy disabled=no distance=indoors frequency=auto mode=ap-bridge ssid=WING2G wds-mode=dynamic wireless-protocol=
802.11
set \[ find default-name=wlan2 \] band=5ghz-a/n/ac channel-width=20/40/80mhz-XXXX country=italy disabled=no distance=indoors frequency=auto mode=ap-bridge ssid=WING5G wireless-protocol=802.11
/interface wireless nstreme
set wlan1 enable-nstreme=yes
/interface ethernet switch port-isolation
set ether1 forwarding-override=""
set ether2 forwarding-override=""
set ether3 forwarding-override=""
set ether4 forwarding-override=""
set ether5 forwarding-override=""
/interface list
add comment=defconf name=WAN
add comment=defconf name=LAN
/interface wireless security-profiles
set \[ find default=yes \] authentication-types=wpa-psk,wpa2-psk comment=defconf disable-pmkid=yes mode=dynamic-keys supplicant-identity=MikroTik
add authentication-types=wpa-psk,wpa2-psk mode=dynamic-keys name=profile supplicant-identity=MikroTik
add authentication-types=wpa-psk,wpa2-psk comment=defconf disable-pmkid=yes mode=dynamic-keys name=profile1 supplicant-identity=MikroTik
/interface wireless
add arp=disabled disabled=no mac-address=D2:EA:11:21:B9:E5 master-interface=wlan1 name=wlan4 security-profile=profile1 ssid=WINGIEM wds-default-bridge=bridge wds-mode=static wmm-support=enabled
wps-mode=disabled
/ip pool
add name=dhcp ranges=192.168.1.60-192.168.1.150
add name=dhcp_pool1 ranges=192.168.1.22
add name=dhcp_pool2 ranges=192.168.1.20-192.168.1.60
/ip dhcp-server
add address-pool=dhcp interface=bridge name=defconf
/ipv6 dhcp-server option sets
add name=set1 options=""
/system script
add comment=defconf dont-require-permissions=no name=dark-mode owner=\*sys policy=ftp,reboot,read,write,policy,test,password,sniff,sensitive,romon source="\\r
\\n   :if (\[system leds settings get all-leds-off\] = "never") do={\\r
\\n     /system leds settings set all-leds-off=immediate \\r
\\n   } else={\\r
\\n     /system leds settings set all-leds-off=never \\r
\\n   }\\r
\\n "
/interface wireless
add disabled=no mac-address=D2:EA:11:21:B9:E6 master-interface=wlan2 name=wlan3 security-profile=\*2 ssid=WINGIEM
/disk settings
set auto-media-interface=bridge auto-media-sharing=yes auto-smb-sharing=yes
/interface bridge port
add bridge=bridge comment=defconf disabled=yes interface=ether2 trusted=yes trusted-dhcpv6=yes trusted-ra=yes
add bridge=bridge comment=defconf disabled=yes interface=ether3 trusted=yes trusted-ra=yes
add bridge=bridge comment=defconf disabled=yes interface=ether4 trusted=yes trusted-dhcpv6=yes trusted-ra=yes
add bridge=bridge comment=defconf disabled=yes interface=ether5 trusted=yes trusted-dhcpv6=yes trusted-ra=yes
add bridge=bridge comment=defconf disabled=yes interface=wlan1 trusted=yes trusted-dhcpv6=yes trusted-ra=yes
add bridge=bridge comment=defconf interface=wlan2 trusted=yes trusted-dhcpv6=yes trusted-ra=yes
add bridge=bridge interface=wlan3 trusted=yes trusted-dhcpv6=yes trusted-ra=yes
add bridge=bridge interface=wlan4 multicast-router=permanent point-to-point=yes trusted=yes trusted-dhcpv6=yes trusted-ra=yes
add bridge=bridge interface=LAN
/ip neighbor discovery-settings
set discover-interface-list=LAN
/interface ethernet switch host
add ports=ether3 share-vlan-learned=no switch=switch1 vlan-id=auto
/interface list member
add comment=defconf interface=ether2 list=LAN
add comment=defconf interface=ether1 list=WAN
add interface=ether3 list=LAN
add interface=ether4 list=LAN
add interface=ether5 list=LAN
add interface=wlan1 list=LAN
add interface=wlan2 list=LAN
add interface=wlan3 list=LAN
add interface=wlan4 list=LAN
/interface wireless sniffer
set multiple-channels=yes
/ip address
add address=192.168.1.220/24 comment=defconf interface=bridge network=192.168.1.0
add address=192.168.1.0/8 interface=ether1 network=192.0.0.0
/ip dhcp-client
add comment=defconf disabled=yes interface=ether1 name=ether1
/ip dhcp-server network
add address=192.168.1.0/24 comment=defconf dns-none=yes gateway=192.168.1.1 netmask=24
add address=192.168.1.20/30 dns-none=yes gateway=192.168.1.21
/ip dns
set allow-remote-requests=yes servers=1.1.1.1,8.8.8.8
/ip dns static
add address=192.168.1.220 comment=defconf name=router.lan type=A
/ip firewall filter
add action=accept chain=input comment="defconf: accept established,related,untracked" connection-nat-state=! connection-state=invalid,established,related,new,untracked connection-type=! disabled=
yes fragment=no
add action=accept chain=input comment="defconf: accept ICMP" protocol=icmp
add action=accept chain=input comment="defconf: accept to local loopback (for CAPsMAN)" dst-address=127.0.0.1
add action=accept chain=forward comment="defconf: accept in ipsec policy" ipsec-policy=in,ipsec
add action=accept chain=forward comment="defconf: accept out ipsec policy" ipsec-policy=out,ipsec
add action=fasttrack-connection chain=forward comment="defconf: fasttrack" connection-state=established,related disabled=yes
add action=accept chain=forward comment="defconf: accept established,related, untracked" connection-state=established,related,untracked
add action=accept chain=forward
add action=accept chain=forward in-interface=all-wireless log=yes out-interface=bridge src-address-list=""
add action=accept chain=forward in-interface=all-wireless out-interface=bridge
add action=accept chain=input
/ip firewall nat
add action=masquerade chain=srcnat comment="defconf: masquerade" ipsec-policy=out,none out-interface-list=WAN
/ip firewall service-port
set irc disabled=no
set rtsp disabled=no
/ipv6 dhcp-client
add interface=\*15 request=address
/ipv6 dhcp-relay
add dhcp-server=:: interface=ether1 name=relay1
/ipv6 dhcp-server
add interface=\*15 name=server1 use-radius=yes
/ipv6 firewall address-list
add address=::/128 comment="defconf: unspecified address" list=bad_ipv6
add address=::1/128 comment="defconf: lo" list=bad_ipv6
add address=fec0::/10 comment="defconf: site-local" list=bad_ipv6
add address=::ffff:0.0.0.0/96 comment="defconf: ipv4-mapped" list=bad_ipv6
add address=::/96 comment="defconf: ipv4 compat" list=bad_ipv6
add address=100::/64 comment="defconf: discard only " list=bad_ipv6
add address=2001:db8::/32 comment="defconf: documentation" list=bad_ipv6
add address=2001:10::/28 comment="defconf: ORCHID" list=bad_ipv6
add address=3ffe::/16 comment="defconf: 6bone" list=bad_ipv6
/ipv6 firewall filter
add action=accept chain=input comment="defconf: accept established,related,untracked" connection-state=established,related,untracked
add action=accept chain=input comment="defconf: accept ICMPv6" protocol=icmpv6
add action=accept chain=input comment="defconf: accept UDP traceroute" dst-port=33434-33534 protocol=udp
add action=accept chain=input comment="defconf: accept DHCPv6-Client prefix delegation." dst-port=546 protocol=udp src-address=fe80::/10
add action=accept chain=input comment="defconf: accept IKE" dst-port=500,4500 protocol=udp
add action=accept chain=input comment="defconf: accept ipsec AH" protocol=ipsec-ah
add action=accept chain=input comment="defconf: accept ipsec ESP" protocol=ipsec-esp
add action=accept chain=input comment="defconf: accept all that matches ipsec policy" ipsec-policy=in,ipsec
add action=fasttrack-connection chain=forward comment="defconf: fasttrack6" connection-state=established,related
add action=accept chain=forward comment="defconf: accept established,related,untracked" connection-state=established,related,untracked
add action=accept chain=forward comment="defconf: accept ICMPv6" protocol=icmpv6
add action=accept chain=forward comment="defconf: accept HIP" protocol=139
add action=accept chain=forward comment="defconf: accept IKE" dst-port=500,4500 protocol=udp
add action=accept chain=forward comment="defconf: accept ipsec AH" protocol=ipsec-ah
add action=accept chain=forward comment="defconf: accept ipsec ESP" protocol=ipsec-esp
add action=accept chain=forward comment="defconf: accept all that matches ipsec policy" ipsec-policy=in,ipsec
add action=accept chain=forward comment=all
/system clock
set time-zone-name=Europe/Rome
/system routerboard mode-button
set enabled=yes on-event=dark-mode
/tool mac-server
set allowed-interface-list=LAN
/tool mac-server mac-winbox
set allowed-interface-list=LAN
/tool traffic-monitor
add interface=wlan4 name=tmon1 traffic=receivedIs ether1 a WAN/internet, or are you trying to use it as a switch? Perhaps suggest where the ports are going where?
Few odd things:
- If your intent is that ether1 is bridged (not a WAN)...
- You need to mark trusted=yes on ether1 (assuming that's the upstream switch and already has DHCP server)
- You need to remove ether1 from the
/interface/listso it not in WAN interface-list.
- In either case I'm not use you want the DHCP relay...
- I'm not sure where the
/interface ethernet switch port-isolationis coming from... but this seems wrong. - Are you sure the Behringer is not acting as a multicast queierrer
- Using
/ipv6 dhcp-serverand/ipv6 dhcp-relayand/ipv6 dhcp-clientalso seem wrong. Now since it appears they do not reference an current interface (interface=\*15), I'm not sure any of them are doing anything.
Also, it might help if you check if the mixing console's IP address is in same subnet as your phone with the Behringer app. It also possible the console uses a self-assigned address (perhaps due to a race condition that it comes up before the MikroTik and does not retry DHCP)... or, some one set the Wing to use a static IP address that does not match the MikroTik subnet.
then ether1 lan1 is not used
Hi , All device have 192.168.1.xxx and respond at the ping , also the phone
tnks
Okay so this is simply attach a device to a non-internet connected wifi router such that one can locally, use an app and access device over wifi network.
No vlans do not enable bridge vlan filtering
Simple wifi nstreme NOT enalbed
What is the purpose of multiple wifi
wlan1 = 2ghz wifi purpose =?
wlan2 = 5ghz wifi purpose =?
wlan4 = master wlan1 purpose= ?
wlan3 =master wlan2 purpose=?
No internet, all on same subnet structure so what is the purpose of a second 2ghz network? and second 5ghz network?? { you have *2 by security profile which indicates some mismatch in settings)
Single pool!
WHY all bridge ports disabled?? okay no need for connectivity,
Save to administer the router, so lets use ether2
Suggest doing so on ether1. will be an off bridge access
This will serve as an emergency access to the router in case the bridge burps and you cannot access through ether port2 on the bridge subnet. Simply plug your laptop into ether1, change ipv4 settings to 192.168.77.2 and with username and password you should be in.
What you have done with addresses assigning one to bridge and to port is too funky for me.
Keep it clean and separate.
Simplify and back to standard defaults for the most on firewall rules. Although in this case none really needed.
Remove ipv6 crap, a because Im allergic to it, and also not needed for mixer.
++++++++++++++++++++++++++++++++++++++++++++++++++++
interface bridge
add name=bridge vlan-filtering=NO
/interface ethernet
set \[ find default-name=ether1 \] name=OffBridge1
set \[ find default-name=ether2 \] l2mtu=1598
set \[ find default-name=ether3 \] l2mtu=1598
set \[ find default-name=ether4 \] l2mtu=1598
set \[ find default-name=ether5 \] l2mtu=1598
/interface wireless
set \[ find default-name=wlan1 \] band=2ghz-b/g/n channel-width=20/40mhz-XX country=italy disabled=no distance=indoors frequency=auto mode=ap-bridge ssid=WING2G wds-mode=dynamic wireless-protocol=
802.11
set \[ find default-name=wlan2 \] band=5ghz-a/n/ac channel-width=20/40/80mhz-XXXX country=italy disabled=no distance=indoors frequency=auto mode=ap-bridge ssid=WING5G wireless-protocol=802.11
/interface wireless nstreme
set wlan1 enable-nstreme=NO
/interface list
add comment=defconf name=LAN
add name=MGMT
/interface wireless security-profiles
set \[ find default=yes \] authentication-types=wpa-psk,wpa2-psk comment=defconf disable-pmkid=yes mode=dynamic-keys supplicant-identity=MikroTik
add authentication-types=wpa-psk,wpa2-psk mode=dynamic-keys name=profile supplicant-identity=MikroTik
add authentication-types=wpa-psk,wpa2-psk comment=defconf disable-pmkid=yes mode=dynamic-keys name=profile1 supplicant-identity=MikroTik
/interface wireless
add arp=disabled disabled=no mac-address=D2:EA:11:21:B9:E5 master-interface=wlan1 name=wlan4 security-profile=profile1 ssid=WINGIEM wds-default-bridge=bridge wds-mode=static wmm-support=enabled
wps-mode=disabled
/ip pool
add name=dhcp ranges=192.168.1.60-192.168.1.150
/ip dhcp-server
add address-pool=dhcp interface=bridge name=defconf
/system script
add comment=defconf dont-require-permissions=no name=dark-mode owner=\*sys policy=ftp,reboot,read,write,policy,test,password,sniff,sensitive,romon source="\\r
\\n :if (\[system leds settings get all-leds-off\] = "never") do={\\r
\\n /system leds settings set all-leds-off=immediate \\r
\\n } else={\\r
\\n /system leds settings set all-leds-off=never \\r
\\n }\\r
\\n "
/interface wireless
add disabled=no mac-address=D2:EA:11:21:B9:E6 master-interface=wlan2 name=wlan3 security-profile=\*2 ssid=WINGIEM
/disk settings
set auto-media-interface=bridge auto-media-sharing=yes auto-smb-sharing=yes
/interface bridge port
add bridge=bridge disabled=NO interface=ether2 comment="admin access via bridge"
add bridge=bridge disabled=yes interface=ether3
add bridge=bridge disabled=yes interface=ether4
add bridge=bridge disabled=yes interface=ether5
add bridge=bridge disabled=NO interface=wlan1
add bridge=bridge disabled=NO interface=wlan2
add bridge=bridge disabled=NO interface=wlan3
add bridge=bridge disabled=NO interface=wlan4
/ip neighbor discovery-settings
set discover-interface-list=MGMT
/interface list member
add defconf interface=bridge list=LAN
add interface=OffBridge1 list=LAN
add interface=bridge list=MGMT
add interface=OffBridge1 list=MGMT
/interface wireless sniffer
set multiple-channels=yes
/ip address
add address=192.168.1.1/24 comment=defconf interface=bridge network=192.168.1.0
add address=192.168.77.1/30 interface=ether1 network=192.168.77.0
/ip dhcp-client
add comment=defconf disabled=yes interface=ether1 name=ether1
/ip dhcp-server network
add address=192.168.1.0/24 comment=defconf dns-none=yes gateway=192.168.1.1
/ip dns
set allow-remote-requests=no
/ip firewall filter
add action=accept chain=input connection-state=established,related,untracked
add action=drop chain=input connection-state=invalid
add action=accept chain=input comment="defconf: accept ICMP" protocol=icmp
add action=accept chain=input comment="defconf: accept to local loopback (for CAPsMAN)" dst-address=127.0.0.1
add action=accept chain=input comment="admin access" in-interface-list=MGMT
add action=drop chain=input comment="drop all else"
++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
add action=fasttrack-connection chain=forward connection-state=established,related
add action=accept chain=forward connection-state=established,related,untracked
add action=drop chain=forward connection-state=invalid
add action=accept chain=forward comment="admin access" in-interface-list=MGMT \
out-interface-list=LAN
add action=drop chain=forward comment="drop all else"
{ Note traffic between devices on same subnet is at level 2, not level 3 }
/ip firewall nat
add action=masquerade chain=srcnat comment="defconf: masquerade" ipsec-policy=out,none out-interface-list=WAN disabled=yes
/ip firewall service-port
set irc disabled=no
set rtsp disabled=no
/ipv6 services disabled
/system clock
set time-zone-name=Europe/Rome
/system routerboard mode-button
set enabled=yes on-event=dark-mode
/tool mac-server
set allowed-interface-list=none
/tool mac-server mac-winbox
set allowed-interface-list=MGMT
/tool traffic-monitor
add interface=wlan4 name=tmon1 traffic=received
put all this into a code block
interface bridge
add name=bridge vlan-filtering=NO
/interface ethernet
set \[ find default-name=ether1 \] name=OffBridge1
set \[ find default-name=ether2 \] l2mtu=1598
set \[ find default-name=ether3 \] l2mtu=1598
set \[ find default-name=ether4 \] l2mtu=1598
set \[ find default-name=ether5 \] l2mtu=1598
/interface wireless
set \[ find default-name=wlan1 \] band=2ghz-b/g/n channel-width=20/40mhz-XX country=italy disabled=no distance=indoors frequency=auto mode=ap-bridge ssid=WING2G wds-mode=dynamic wireless-protocol=
802.11
set \[ find default-name=wlan2 \] band=5ghz-a/n/ac channel-width=20/40/80mhz-XXXX country=italy disabled=no distance=indoors frequency=auto mode=ap-bridge ssid=WING5G wireless-protocol=802.11
/interface wireless nstreme
set wlan1 enable-nstreme=NO
/interface list
add comment=defconf name=LAN
add name=MGMT
/interface wireless security-profiles
set \[ find default=yes \] authentication-types=wpa-psk,wpa2-psk comment=defconf disable-pmkid=yes mode=dynamic-keys supplicant-identity=MikroTik
add authentication-types=wpa-psk,wpa2-psk mode=dynamic-keys name=profile supplicant-identity=MikroTik
add authentication-types=wpa-psk,wpa2-psk comment=defconf disable-pmkid=yes mode=dynamic-keys name=profile1 supplicant-identity=MikroTik
/interface wireless
add arp=disabled disabled=no mac-address=D2:EA:11:21:B9:E5 master-interface=wlan1 name=wlan4 security-profile=profile1 ssid=WINGIEM wds-default-bridge=bridge wds-mode=static wmm-support=enabled
wps-mode=disabled
/ip pool
add name=dhcp ranges=192.168.1.60-192.168.1.150
/ip dhcp-server
add address-pool=dhcp interface=bridge name=defconf
/system script
add comment=defconf dont-require-permissions=no name=dark-mode owner=\*sys policy=ftp,reboot,read,write,policy,test,password,sniff,sensitive,romon source="\\r
\\n :if (\[system leds settings get all-leds-off\] = "never") do={\\r
\\n /system leds settings set all-leds-off=immediate \\r
\\n } else={\\r
\\n /system leds settings set all-leds-off=never \\r
\\n }\\r
\\n "
/interface wireless
add disabled=no mac-address=D2:EA:11:21:B9:E6 master-interface=wlan2 name=wlan3 security-profile=\*2 ssid=WINGIEM
/disk settings
set auto-media-interface=bridge auto-media-sharing=yes auto-smb-sharing=yes
/interface bridge port
add bridge=bridge disabled=NO interface=ether2 comment="admin access via bridge"
add bridge=bridge disabled=yes interface=ether3
add bridge=bridge disabled=yes interface=ether4
add bridge=bridge disabled=yes interface=ether5
add bridge=bridge disabled=NO interface=wlan1
add bridge=bridge disabled=NO interface=wlan2
add bridge=bridge disabled=NO interface=wlan3
add bridge=bridge disabled=NO interface=wlan4
/ip neighbor discovery-settings
set discover-interface-list=MGMT
/interface list member
add defconf interface=bridge list=LAN
add interface=OffBridge1 list=LAN
add interface=bridge list=MGMT
add interface=OffBridge1 list=MGMT
/interface wireless sniffer
set multiple-channels=yes
/ip address
add address=192.168.1.1/24 comment=defconf interface=bridge network=192.168.1.0
add address=192.168.77.1/30 interface=ether1 network=192.168.77.0
/ip dhcp-client
add comment=defconf disabled=yes interface=ether1 name=ether1
/ip dhcp-server network
add address=192.168.1.0/24 comment=defconf dns-none=yes gateway=192.168.1.1
/ip dns
set allow-remote-requests=no
/ip firewall filter
add action=accept chain=input connection-state=established,related,untracked
add action=drop chain=input connection-state=invalid
add action=accept chain=input comment="defconf: accept ICMP" protocol=icmp
add action=accept chain=input comment="defconf: accept to local loopback (for CAPsMAN)" dst-address=127.0.0.1
add action=accept chain=input comment="admin access" in-interface-list=MGMT
add action=drop chain=input comment="drop all else"
++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
add action=fasttrack-connection chain=forward connection-state=established,related
add action=accept chain=forward connection-state=established,related,untracked
add action=drop chain=forward connection-state=invalid
add action=accept chain=forward comment="admin access" in-interface-list=MGMT \
out-interface-list=LAN
add action=drop chain=forward comment="drop all else"
{ Note traffic between devices on same subnet is at level 2, not level 3 }
/ip firewall nat
add action=masquerade chain=srcnat comment="defconf: masquerade" ipsec-policy=out,none out-interface-list=WAN disabled=yes
/ip firewall service-port
set irc disabled=no
set rtsp disabled=no
/ipv6 services disabled
/system clock
set time-zone-name=Europe/Rome
/system routerboard mode-button
set enabled=yes on-event=dark-mode
/tool mac-server
set allowed-interface-list=none
/tool mac-server mac-winbox
set allowed-interface-list=MGMT
/tool traffic-monitor
add interface=wlan4 name=tmon1 traffic=received
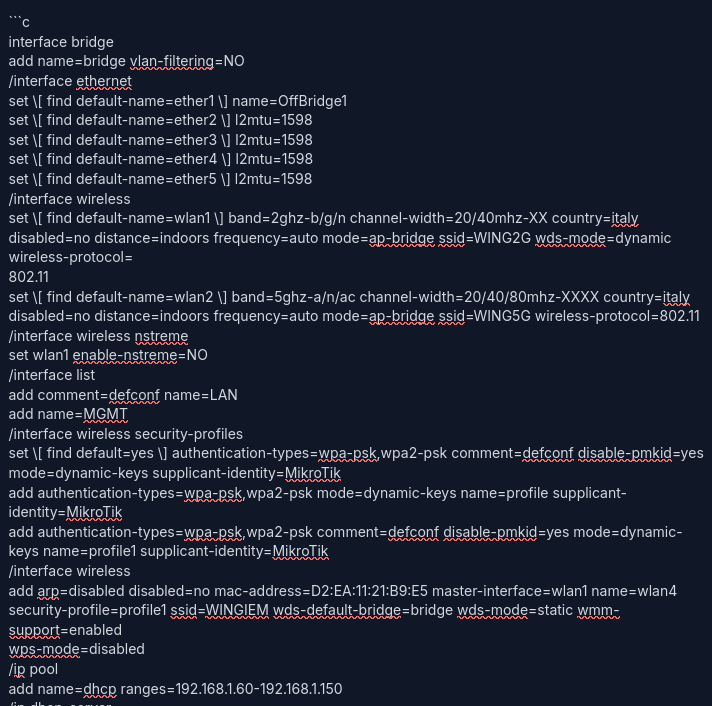
u end it the same way u start it
works for you ever since MT change the website, I can never get an output the way I like it, or for it to show up clean so I have given up trying
try again or you'll never know.
maybe with green eggs and ham, I may like it!!
[admin@hAP] > ping 192.168.1.145
SEQ HOST SIZE TTL TIME STATUS
0 192.168.1.145 56 64 808us
1 192.168.1.145 56 64 765us
2 192.168.1.145 56 64 796us
3 192.168.1.145 56 64 731us
4 192.168.1.145 56 64 780us
5 192.168.1.145 56 64 789us
6 192.168.1.145 56 64 786us
7 192.168.1.145 56 64 774us
8 192.168.1.145 56 64 803us
9 192.168.1.145 56 64 846us
sent=10 received=10 packet-loss=0% min-rtt=731us avg-rtt=787us
max-rtt=846us
[admin@hAP] > ping 192.168.1.103
SEQ HOST SIZE TTL TIME STATUS
0 192.168.1.103 56 128 583us
1 192.168.1.103 56 128 465us
2 192.168.1.103 56 128 484us
3 192.168.1.103 56 128 364us
4 192.168.1.103 56 128 546us
5 192.168.1.103 56 128 496us
6 192.168.1.103 56 128 518us
7 192.168.1.103 56 128 479us
8 192.168.1.103 56 128 463us
sent=9 received=9 packet-loss=0% min-rtt=364us avg-rtt=488us max-rtt=583us
[admin@hAP] > ping 192.168.1.91
SEQ HOST SIZE TTL TIME STATUS
0 192.168.1.91 56 64 319ms221us
1 192.168.1.91 56 64 240ms563us
2 192.168.1.91 56 64 169ms375us
3 192.168.1.91 56 64 284ms145us
4 192.168.1.91 56 64 115ms214us
5 192.168.1.91 56 64 130ms613us
6 192.168.1.91 56 64 58ms29us
sent=7 received=7 packet-loss=0% min-rtt=58ms29us avg-rtt=188ms165us
max-rtt=319ms221us
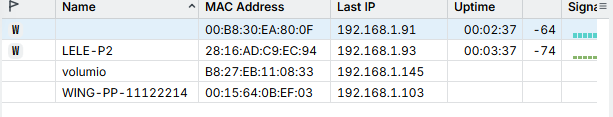
if I connect the phone in wireless router TPLINK ac80 AND connect THE AC80 lan on mikrotik router lan the app WING-Q work corretly
103 is mixer wing
145 is player music volumio
93 is my pc
91 is the phone
all ping work correctly
for each address
Drotz : same condition don't work