I missed this orginally. I think this is an hAP ac3... And you still using the older wireless package. You may have better luck with that wireless package overall. See Wi-Fi 6 / 7 (802.11ax/be) | RouterOS Manual - but it bit more involved to change it, and not sure that's your issue... since you can say it pings.
And even with the now older "wireless" drivers you have... a quick thing to do is set a frequency (and avoid "auto"), and set the 2ghz wlan1 to channel-width=20mhz and wlan2 to channel-width=20/40mhz. Since OSC protocol used by WING/Behringer is minimum data, you don't need 40 or 80mhz, so a smaller channel size likely gets lower latency/stability on average (although lower "top speed"). Even if you use want "auto", set the DFS skip-dfs-channels=all so it avoid one that could drop - which is last thing you want with audio console.
What is easy to try on more possibility the issue... is on you bridge interface, I'd change the IGMP setting... so igmp-snooping=no and multicast-querier=no - you don't have enough devices to worry about multicast flooding. IDK but how that work could be related to your specific issues with WING app since I'd image it does use multicast for device discovery. Those settings should be fine, but it adds complexity if things are not working.
But you may have better luck starting from scratch here. Upgrade the router to the latest version (System > Packages > Check for Update), also update the fireware in System > Routerboard (which be a 2nd reboot to cause after upgraded). I'd then do a System > Reset Configuration, selecting "keep user" to yes (assuming you set already have a password), but this get you back to a basic bridge LAN setup on ether2-5. This get you the latest default configuration applied, so we don't have to unwind some of the "non-defaults" your currently. You can setup the Wi-Fi using QuickSet with your desired password/SSID name.
I do think long-term you'd be better off with the newer wireless driver. If you wanted to do that after upgrade/reet-configuration.... go to System > Packages, do another "Check for Update" (which should be current, but will refresh the available packages. By click "uninstall" on the wireless package, and "enable" the wifi-qcom-ac driver, and clicking "Apply Changes", it will reboot a 4th time. Aften then you can use the new "Wi-Fi" menu in webfig/winbox to setup your SSID/password. The new driver will use Wi-Fi 5, which is more modern than legacy Wi-Fi 4 used by the wireless package.
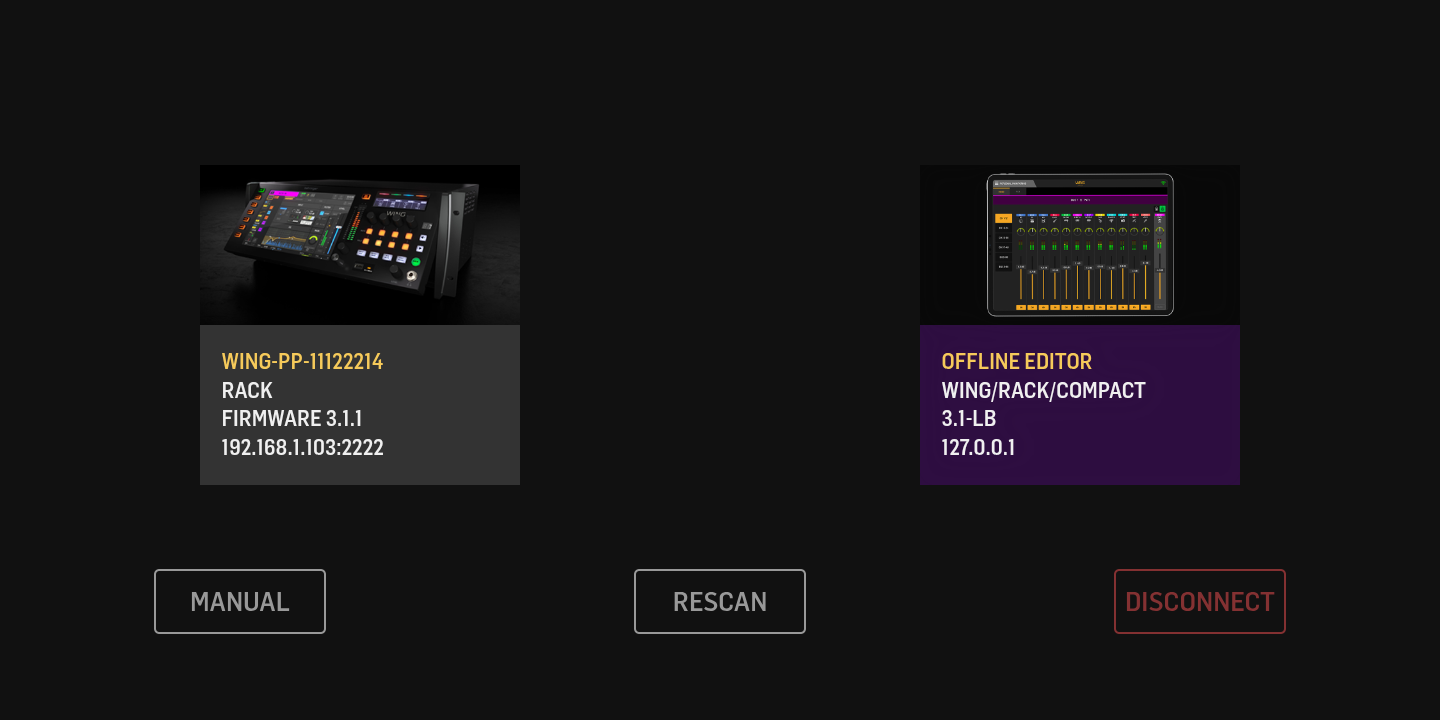
Hi AMM0 , i follow your istructions , bat the situation is immutate 
So at this point what's working and what's not working?
Perhaps do another /export terse file=config.rsc, and then use Files to download/cut-and-paste it here.
Some of my customers have Behringer/Midas X32s, and I know they worked with Audience (~generation as your hAPac2) with the X32 app - both with wireless package Wi-Fi driver in past, and even better with wifiwave2/wifi-qcom-qc. I think WING uses the same OSC protocol as X32, so something is odd here.
the application wing edit from pcwork correcly !
2026-09-03 07:35:31 by RouterOS 7.23.5
software id = LJAN-6CBH
model = RBD53iG-5HacD2HnD
serial number = HM30B0VNX8P
/interface bridge add admin-mac=D0:EA:11:21:B9:E1 auto-mac=no comment=defconf name=bridge
/interface wifi set [ find default-name=wifi1 ] channel.skip-dfs-channels=10min-cac configuration.country=Italy .mode=ap .ssid=WING2G disabled=no security.authentication-types=wpa2-psk,wpa3-psk .ft=yes .ft-over-ds=yes
/interface wifi set [ find default-name=wifi2 ] channel.reselect-time=00:00:00 .skip-dfs-channels=all configuration.country=Italy .mode=ap .ssid=WING5G disabled=no security.authentication-types=wpa2-psk,wpa3-psk .ft=yes .ft-over-ds=yes
/interface wifi add configuration.mode=ap .multicast-enhance=disabled .ssid=WINGIEM disabled=no mac-address=D2:EA:11:21:B9:E6 master-interface=wifi2 name=wifi3
/interface wifi add configuration.mode=ap .multicast-enhance=disabled .ssid=WINGIEM disabled=no mac-address=D2:EA:11:21:B9:E5 master-interface=wifi1 name=wifi4
/interface ethernet switch port-isolation set ether2 forwarding-override=ether3,ether1,ether4,ether5
/interface ethernet switch port-isolation set ether3 forwarding-override=ether1,ether2,ether4,ether5
/interface ethernet switch port-isolation set ether4 forwarding-override=ether1,ether2,ether3,ether5
/interface ethernet switch port-isolation set ether5 forwarding-override=ether1,ether2,ether3,ether4
/interface list add comment=defconf name=WAN
/interface list add comment=defconf name=LAN
/ip pool add name=dhcp ranges=192.168.1.30-192.168.1.150
/ip dhcp-server add address-pool=dhcp interface=bridge name=defconf
/system script add comment=defconf dont-require-permissions=no name=dark-mode owner=*sys policy=ftp,reboot,read,write,policy,test,password,sniff,sensitive,romon source="\r
\n :if ([system leds settings get all-leds-off] = "never") do={\r
\n /system leds settings set all-leds-off=immediate \r
\n } else={\r
\n /system leds settings set all-leds-off=never \r
\n }\r
\n "
/system script add comment=defconf dont-require-permissions=no name=wps-accept owner=*sys policy=ftp,reboot,read,write,policy,test,password,sniff,sensitive,romon source="\r
\n :foreach iface in=[/interface/wifi find where (configuration.mode="ap" && disabled=no)] do={\r
\n /interface/wifi wps-push-button $iface;}\r
\n "
/disk settings set auto-media-interface=bridge auto-media-sharing=yes auto-smb-sharing=yes
/interface bridge filter add action=drop chain=forward disabled=yes in-interface=wifi3
/interface bridge filter add action=drop chain=forward disabled=yes out-interface=wifi3
/interface bridge filter add action=drop chain=forward disabled=yes in-interface=wifi4
/interface bridge filter add action=drop chain=forward disabled=yes out-interface=wifi4
/interface bridge filter add action=accept chain=forward in-bridge=bridge out-bridge=bridge
/interface bridge port add bridge=bridge comment=defconf interface=ether2 trusted-dhcpv6=yes trusted-ra=yes
/interface bridge port add bridge=bridge comment=defconf interface=ether3 trusted=yes trusted-dhcpv6=yes trusted-ra=yes
/interface bridge port add bridge=bridge comment=defconf interface=ether4 trusted=yes trusted-dhcpv6=yes trusted-ra=yes
/interface bridge port add bridge=bridge comment=defconf interface=ether5 trusted=yes trusted-dhcpv6=yes trusted-ra=yes
/interface bridge port add bridge=bridge comment=defconf interface=wifi1 multicast-router=disabled trusted=yes trusted-dhcpv6=yes trusted-ra=yes
/interface bridge port add bridge=bridge comment=defconf interface=wifi2 multicast-router=disabled trusted=yes trusted-dhcpv6=yes trusted-ra=yes
/interface bridge port add bridge=bridge interface=wifi3 multicast-router=disabled trusted=yes trusted-dhcpv6=yes trusted-ra=yes
/interface bridge port add bridge=bridge interface=wifi4 multicast-router=disabled trusted=yes trusted-dhcpv6=yes trusted-ra=yes
/ip neighbor discovery-settings set discover-interface-list=LAN
/interface list member add comment=defconf interface=bridge list=LAN
/interface list member add comment=defconf interface=ether1 list=WAN
/ip address add address=192.168.1.220/24 comment=defconf interface=bridge network=192.168.1.0
/ip address add address=192.168.1.220/8 interface=ether1 network=192.0.0.0
/ip dhcp-client add comment=defconf disabled=yes interface=ether1 name=client1
/ip dhcp-server network add address=192.168.1.0/24 comment=defconf dns-server=192.168.1.220 gateway=192.168.1.220 netmask=24
/ip dns set allow-remote-requests=yes
/ip dns static add address=192.168.1.220 comment=defconf name=router.lan type=A
/ip firewall filter add action=accept chain=input comment="defconf: accept established,related,untracked" connection-state=established,related,untracked
/ip firewall filter add action=drop chain=input comment="defconf: drop invalid" connection-state=invalid disabled=yes
/ip firewall filter add action=accept chain=input comment="defconf: accept ICMP" protocol=icmp
/ip firewall filter add action=accept chain=input comment="defconf: accept to local loopback (for CAPsMAN)" dst-address=127.0.0.1 in-interface=lo src-address=127.0.0.1
/ip firewall filter add action=drop chain=input comment="defconf: drop all not coming from LAN" disabled=yes in-interface-list=!LAN
/ip firewall filter add action=accept chain=forward comment="defconf: accept in ipsec policy" ipsec-policy=in,ipsec
/ip firewall filter add action=accept chain=forward comment="defconf: accept out ipsec policy" ipsec-policy=out,ipsec
/ip firewall filter add action=fasttrack-connection chain=forward comment="defconf: fasttrack" connection-state=established,related
/ip firewall filter add action=accept chain=forward comment="defconf: accept established,related, untracked" connection-state=established,related,untracked
/ip firewall filter add action=drop chain=forward comment="defconf: drop invalid" connection-state=invalid disabled=yes
/ip firewall filter add action=drop chain=forward comment="defconf: drop all from WAN not DSTNATed" connection-nat-state=!dstnat disabled=yes in-interface-list=WAN
/ip firewall nat add action=masquerade chain=srcnat comment="defconf: masquerade" ipsec-policy=out,none out-interface-list=WAN
/ip route add disabled=no dst-address=0.0.0.0/0 gateway=192.168.1.1
/ip upnp set enabled=yes
/ip upnp interfaces add interface=bridge type=internal
/ip upnp interfaces add interface=ether1 type=external
/ipv6 firewall address-list add address=::/128 comment="defconf: unspecified address" list=bad_ipv6
/ipv6 firewall address-list add address=::1/128 comment="defconf: lo" list=bad_ipv6
/ipv6 firewall address-list add address=fec0::/10 comment="defconf: site-local" list=bad_ipv6
/ipv6 firewall address-list add address=::ffff:0.0.0.0/96 comment="defconf: ipv4-mapped" list=bad_ipv6
/ipv6 firewall address-list add address=::/96 comment="defconf: ipv4 compat" list=bad_ipv6
/ipv6 firewall address-list add address=100::/64 comment="defconf: discard only " list=bad_ipv6
/ipv6 firewall address-list add address=2001:db8::/32 comment="defconf: documentation" list=bad_ipv6
/ipv6 firewall address-list add address=2001:10::/28 comment="defconf: ORCHID" list=bad_ipv6
/ipv6 firewall address-list add address=3ffe::/16 comment="defconf: 6bone" list=bad_ipv6
/ipv6 firewall filter add action=accept chain=input comment="defconf: accept established,related,untracked" connection-state=established,related,untracked
/ipv6 firewall filter add action=drop chain=input comment="defconf: drop invalid" connection-state=invalid disabled=yes
/ipv6 firewall filter add action=accept chain=input comment="defconf: accept ICMPv6" protocol=icmpv6
/ipv6 firewall filter add action=accept chain=input comment="defconf: accept UDP traceroute" dst-port=33434-33534 protocol=udp
/ipv6 firewall filter add action=accept chain=input comment="defconf: accept DHCPv6-Client prefix delegation." dst-port=546 protocol=udp src-address=fe80::/10
/ipv6 firewall filter add action=accept chain=input comment="defconf: accept IKE" dst-port=500,4500 protocol=udp
/ipv6 firewall filter add action=accept chain=input comment="defconf: accept ipsec AH" protocol=ipsec-ah
/ipv6 firewall filter add action=accept chain=input comment="defconf: accept ipsec ESP" protocol=ipsec-esp
/ipv6 firewall filter add action=accept chain=input comment="defconf: accept all that matches ipsec policy" ipsec-policy=in,ipsec
/ipv6 firewall filter add action=drop chain=input comment="defconf: drop everything else not coming from LAN" disabled=yes in-interface-list=!LAN
/ipv6 firewall filter add action=fasttrack-connection chain=forward comment="defconf: fasttrack6" connection-state=established,related
/ipv6 firewall filter add action=accept chain=forward comment="defconf: accept established,related,untracked" connection-state=established,related,untracked
/ipv6 firewall filter add action=drop chain=forward comment="defconf: drop invalid" connection-state=invalid disabled=yes
/ipv6 firewall filter add action=drop chain=forward comment="defconf: drop packets with bad src ipv6" disabled=yes src-address-list=bad_ipv6
/ipv6 firewall filter add action=drop chain=forward comment="defconf: drop packets with bad dst ipv6" disabled=yes dst-address-list=bad_ipv6
/ipv6 firewall filter add action=drop chain=forward comment="defconf: rfc4890 drop hop-limit=1" disabled=yes hop-limit=equal:1 protocol=icmpv6
/ipv6 firewall filter add action=accept chain=forward comment="defconf: accept ICMPv6" protocol=icmpv6
/ipv6 firewall filter add action=accept chain=forward comment="defconf: accept HIP" protocol=139
/ipv6 firewall filter add action=accept chain=forward comment="defconf: accept IKE" dst-port=500,4500 protocol=udp
/ipv6 firewall filter add action=accept chain=forward comment="defconf: accept ipsec AH" protocol=ipsec-ah
/ipv6 firewall filter add action=accept chain=forward comment="defconf: accept ipsec ESP" protocol=ipsec-esp
/ipv6 firewall filter add action=accept chain=forward comment="defconf: accept all that matches ipsec policy" ipsec-policy=in,ipsec
/ipv6 firewall filter add action=drop chain=forward comment="defconf: drop everything else not coming from LAN" disabled=yes in-interface-list=!LAN
/ipv6 firewall filter add action=accept chain=forward in-interface=all-ethernet out-interface=all-wireless
/ipv6 firewall filter add action=accept chain=forward in-interface=bridge out-interface=bridge protocol=udp src-port=""
/system routerboard mode-button set enabled=yes on-event=dark-mode
/system routerboard wps-button set enabled=yes on-event=wps-accept
/tool mac-server set allowed-interface-list=LAN
/tool mac-server mac-winbox set allowed-interface-list=LAN
Sorry, new users can not upload attachments.
That won't prevent you from putting it in a code block to make it more readable, though . . .
Well... I was trying to steer you away from the "customizations" until you saw it working in isolation. So I fear you're making this more complicated than needed.
And if you were going to put back or ignore some of the previous suggestions...it not easy to unwind what you're trying to do.
If I had to guess, there is some upstream router with the same subnet and you're trying to link those two networks. If so, we need to talk about bridging, vs routing... as right now you're your config is mixing the two concepts in some weird ways....
For example,
- You're WAN/
ether1should be a real internet connection... not another router in same network. So one clear problem is you're using the 192.168.1.220 on both the WAN and LAN side. While the /8 on upstream maybe fine, using a duplicate IP is not. But the fact you're doing this indicating some important details on your desired topology. Perhaps some diagram of the device and what port is going where might help...
- Nothing should be set under
/interface ethernet switch port-isolation, so whileforwarding-overridefor the members of the bridged (ether2...ether5) likely cancels some of the port-isolation... but since you have wireless interfaces on the bridge you need for the app, these may be blocking that configuration. And also includingether1which is not part of the bridge so is certainly wrong.
So I'd delete all of the following, and see if that fixes you're issues with the WING APP, since wifi1...wifi4 may be blocked by the port-isolation.
For readers at home... the device is a hAP ac³, not the "ax":
(and confirmed since earlier thread export showed wireless drivers)
Hi , I try this .. is ok ? thankyou
2026-09-04 01:03:50 by RouterOS 7.23.5
software id = LJAN-6CBH
model = RBD53iG-5HacD2HnD
serial number = EDITED
/interface bridge
add admin-mac=D0:EA:11:21:B9:E1 auto-mac=no comment=defconf name=bridge
/interface wifi
set [ find default-name=wifi1 ] channel.skip-dfs-channels=10min-cac configuration.country=Italy .mode=ap .ssid=WING2G disabled=no security.authentication-types=wpa2-psk,wpa3-psk .ft=yes
.ft-over-ds=yes
set [ find default-name=wifi2 ] channel.reselect-time=00:00:00 .skip-dfs-channels=all configuration.country=Italy .mode=ap .ssid=WING5G disabled=no security.authentication-types=wpa2-psk,wpa3-psk
.ft=yes .ft-over-ds=yes
add configuration.mode=ap .multicast-enhance=disabled .ssid=WINGIEM disabled=no mac-address=D2:EA:11:21:B9:E6 master-interface=wifi2 name=wifi3
add configuration.hide-ssid=no .mode=ap .multicast-enhance=disabled .ssid=WINGIEM disabled=no mac-address=D2:EA:11:21:B9:E5 master-interface=wifi1 name=wifi4
/interface list
add comment=defconf name=WAN
add comment=defconf name=LAN
/ip pool
add name=dhcp ranges=192.168.1.30-192.168.1.150
/ip dhcp-server
add address-pool=dhcp interface=bridge name=defconf
/system script
add comment=defconf dont-require-permissions=no name=dark-mode owner=*sys policy=ftp,reboot,read,write,policy,test,password,sniff,sensitive,romon source="\r
\n :if ([system leds settings get all-leds-off] = "never") do={\r
\n /system leds settings set all-leds-off=immediate \r
\n } else={\r
\n /system leds settings set all-leds-off=never \r
\n }\r
\n "
add comment=defconf dont-require-permissions=no name=wps-accept owner=*sys policy=ftp,reboot,read,write,policy,test,password,sniff,sensitive,romon source=
"\r
\n :foreach iface in=[/interface/wifi find where (configuration.mode="ap" && disabled=no)] do={\r
\n /interface/wifi wps-push-button $iface;}\r
\n "
/disk settings
set auto-media-interface=bridge auto-media-sharing=yes auto-smb-sharing=yes
/interface bridge filter
add action=drop chain=forward disabled=yes in-interface=wifi3
add action=drop chain=forward disabled=yes out-interface=wifi3
add action=drop chain=forward disabled=yes in-interface=wifi4
add action=drop chain=forward disabled=yes out-interface=wifi4
add action=accept chain=forward in-bridge=bridge out-bridge=bridge
/interface bridge port
add bridge=bridge comment=defconf interface=ether2 trusted-dhcpv6=yes trusted-ra=yes
add bridge=bridge comment=defconf interface=ether3 trusted=yes trusted-dhcpv6=yes trusted-ra=yes
add bridge=bridge comment=defconf interface=ether4 trusted=yes trusted-dhcpv6=yes trusted-ra=yes
add bridge=bridge comment=defconf interface=ether5 trusted=yes trusted-dhcpv6=yes trusted-ra=yes
add bridge=bridge comment=defconf interface=wifi1 multicast-router=disabled trusted=yes trusted-dhcpv6=yes trusted-ra=yes
add bridge=bridge comment=defconf interface=wifi2 multicast-router=disabled trusted=yes trusted-dhcpv6=yes trusted-ra=yes
add bridge=bridge interface=wifi3 multicast-router=disabled trusted=yes trusted-dhcpv6=yes trusted-ra=yes
add bridge=bridge interface=wifi4 multicast-router=disabled trusted=yes trusted-dhcpv6=yes trusted-ra=yes
/ip neighbor discovery-settings
set discover-interface-list=LAN
/interface list member
add comment=defconf interface=bridge list=LAN
add comment=defconf interface=ether1 list=WAN
/ip address
add address=192.168.1.220/24 comment=defconf interface=bridge network=192.168.1.0
/ip dhcp-client
Interface not active
add comment=defconf interface=ether1 name=client1
/ip dhcp-server network
add address=192.168.1.0/24 comment=defconf dns-server=192.168.1.220 gateway=192.168.1.220 netmask=24
/ip dns
set allow-remote-requests=yes
/ip dns static
add address=192.168.1.220 comment=defconf name=router.lan type=A
/ip firewall filter
add action=accept chain=input comment="defconf: accept established,related,untracked" connection-state=established,related,untracked
add action=drop chain=input comment="defconf: drop invalid" connection-state=invalid disabled=yes
add action=accept chain=input comment="defconf: accept ICMP" protocol=icmp
add action=accept chain=input comment="defconf: accept to local loopback (for CAPsMAN)" dst-address=127.0.0.1 in-interface=lo src-address=127.0.0.1
add action=drop chain=input comment="defconf: drop all not coming from LAN" disabled=yes in-interface-list=!LAN
add action=accept chain=forward comment="defconf: accept in ipsec policy" ipsec-policy=in,ipsec
add action=accept chain=forward comment="defconf: accept out ipsec policy" ipsec-policy=out,ipsec
add action=fasttrack-connection chain=forward comment="defconf: fasttrack" connection-state=established,related
add action=accept chain=forward comment="defconf: accept established,related, untracked" connection-state=established,related,untracked
add action=drop chain=forward comment="defconf: drop invalid" connection-state=invalid disabled=yes
add action=drop chain=forward comment="defconf: drop all from WAN not DSTNATed" connection-nat-state=!dstnat disabled=yes in-interface-list=WAN
/ip firewall nat
add action=masquerade chain=srcnat comment="defconf: masquerade" ipsec-policy=out,none out-interface-list=WAN
/ip route
add disabled=yes dst-address=0.0.0.0/0 gateway=192.168.1.1
/ip upnp
set enabled=yes
/ip upnp interfaces
add interface=bridge type=internal
add interface=ether1 type=external
/ipv6 firewall address-list
add address=::/128 comment="defconf: unspecified address" list=bad_ipv6
add address=::1/128 comment="defconf: lo" list=bad_ipv6
add address=fec0::/10 comment="defconf: site-local" list=bad_ipv6
add address=::ffff:0.0.0.0/96 comment="defconf: ipv4-mapped" list=bad_ipv6
add address=::/96 comment="defconf: ipv4 compat" list=bad_ipv6
add address=100::/64 comment="defconf: discard only " list=bad_ipv6
add address=2001:db8::/32 comment="defconf: documentation" list=bad_ipv6
add address=2001:10::/28 comment="defconf: ORCHID" list=bad_ipv6
add address=3ffe::/16 comment="defconf: 6bone" list=bad_ipv6
/ipv6 firewall filter
add action=accept chain=input comment="defconf: accept established,related,untracked" connection-state=established,related,untracked
add action=drop chain=input comment="defconf: drop invalid" connection-state=invalid disabled=yes
add action=accept chain=input comment="defconf: accept ICMPv6" protocol=icmpv6
add action=accept chain=input comment="defconf: accept UDP traceroute" dst-port=33434-33534 protocol=udp
add action=accept chain=input comment="defconf: accept DHCPv6-Client prefix delegation." dst-port=546 protocol=udp src-address=fe80::/10
add action=accept chain=input comment="defconf: accept IKE" dst-port=500,4500 protocol=udp
add action=accept chain=input comment="defconf: accept ipsec AH" protocol=ipsec-ah
add action=accept chain=input comment="defconf: accept ipsec ESP" protocol=ipsec-esp
add action=accept chain=input comment="defconf: accept all that matches ipsec policy" ipsec-policy=in,ipsec
add action=drop chain=input comment="defconf: drop everything else not coming from LAN" disabled=yes in-interface-list=!LAN
add action=fasttrack-connection chain=forward comment="defconf: fasttrack6" connection-state=established,related
add action=accept chain=forward comment="defconf: accept established,related,untracked" connection-state=established,related,untracked
add action=drop chain=forward comment="defconf: drop invalid" connection-state=invalid disabled=yes
add action=drop chain=forward comment="defconf: drop packets with bad src ipv6" disabled=yes src-address-list=bad_ipv6
add action=drop chain=forward comment="defconf: drop packets with bad dst ipv6" disabled=yes dst-address-list=bad_ipv6
add action=drop chain=forward comment="defconf: rfc4890 drop hop-limit=1" disabled=yes hop-limit=equal:1 protocol=icmpv6
add action=accept chain=forward comment="defconf: accept ICMPv6" protocol=icmpv6
add action=accept chain=forward comment="defconf: accept HIP" protocol=139
add action=accept chain=forward comment="defconf: accept IKE" dst-port=500,4500 protocol=udp
add action=accept chain=forward comment="defconf: accept ipsec AH" protocol=ipsec-ah
add action=accept chain=forward comment="defconf: accept ipsec ESP" protocol=ipsec-esp
add action=accept chain=forward comment="defconf: accept all that matches ipsec policy" ipsec-policy=in,ipsec
add action=drop chain=forward comment="defconf: drop everything else not coming from LAN" disabled=yes in-interface-list=!LAN
add action=accept chain=forward in-interface=all-ethernet out-interface=all-wireless
add action=accept chain=forward in-interface=bridge out-interface=bridge protocol=udp src-port=""
/system routerboard mode-button
set enabled=yes on-event=dark-mode
/system routerboard wps-button
set enabled=yes on-event=wps-accept
/tool mac-server
set allowed-interface-list=LAN
/tool mac-server mac-winbox
set allowed-interface-list=LAN
While running various tests, I connected my mobile phone to wifi1 (I usually connect it to wifi4), while keeping the PC on wifi1.
if I make several connection attempts using WING-Q and then WinBox on the PC, the connection WINBOX drops and I have to reconnect the pc , maybe the wifi1 crash ?.
Is there no way for the log to detect potential interface crashes?
Thanks,
Gabriele
3 DC 192.168.1.148 00:B8:30:EA:80:0F bridge main stale ?
[admin@hAP] /ip/arp> print
Flags: D - DYNAMIC; C - COMPLETE
Columns: ADDRESS, MAC-ADDRESS, INTERFACE, VRF, STATUS
ADDRESS MAC-ADDRESS INTERFACE VRF STATUS
0 DC 192.168.1.149 28:16:AD:C9:EC:94 bridge main reachable
1 DC 169.254.192.165 28:16:AD:C9:EC:94 bridge main stale
2 D 192.168.1.1 bridge main failed
3 DC 192.168.1.148 00:B8:30:EA:80:0F bridge main stale
Last night GIG using the WING and "hAP ac³ . Distance from the stage was 30 meters, with no disconnections, no interference, or slowdowns;
this was with a crowd of 1,500 people, meaning 1,500 mobile phones in the area between the wing and the mixer.
Excellent!