Yes exactly!
I got it working last night using the variables of my RB2011UAS-2HnD, hardcoding them into the update URL of the RB3011UIAS-RM:
/tool fetch mode=https dst-path="/dynamic.rsc" \
   url="https://mikrotikfilters.com/download.php?get=dynamic&model=RB2011UAS-2HnD&version=6.38.5+(stable)&memory=128.0MiB&id=MikroTik+router&ver=2016.7.4a";
Out of curiosity, what does your router say to the following if you paste it in the terminal?
:put [/system resource get board-name]
:put [/system resource get version]
:put [/system resource get total-memory]
:put [/system identity get name]
Give this a try…
# Import Intrus Managed Filter Lists
# ©2016-2017 David Joyce, Intrus Technologies

:log warning "Blacklist update in 30 seconds";
# :delay 10

:local model 	[/system resource get board-name]
:local version	[/system resource get version]
:local memory	[/system resource get total-memory]
:local uname	[/system identity get name]
:local scriptVer   2017.5.2b

:local name ""
:local ver ""

:for i from=0 to=([:len $uname] - 1) do={
  :local char [:pick $uname $i]
  :if ($char = " ") do={ :set $char "%20" }
  :set name ($name . $char)
}

:for i from=0 to=([:len $version] - 1) do={
  :local char [:pick $version $i]
  :if ($char = " ") do={
    :set $char "%20"
  }
  :set ver ($ver . $char)
}


:log warning "Downloading current Blacklist for this model";
/tool fetch mode=https dst-path="/dynamic.rsc" \
	url="https://mikrotikfilters.com/download.php?get=dynamic&model=$model&version=$ver&memory=$memory&id=$name&ver=$scriptVer";

:log warning "Disabling info logging...";
/system logging disable 0

:log warning "Removing expiring address-list entries...";
:foreach i in=[/ip firewall address-list find ] \
	do={ :if ( [/ip firewall address-list get $i list] = "dynamicBlacklist" ) \
    do={ /ip firewall address-list remove $i } }

:log warning "Importing current Blacklist...";
/import file-name=/dynamic.rsc

:log warning "Removing temp file...";
/file remove dynamic.rsc

:log warning "Blacklist Update Complete.";
/system logging enable 0
[quote=“mhyll”]Your firewall rules are great. Only DST-NAT is not working…
Last two filter rules needs to be modded like this:
add action=drop chain=forward comment="Drop everything else on WAN1" in-interface=wan1 connection-nat-state=!dstnat
add action=drop chain=forward comment="Drop everything else on WAN2" in-interface=wan2 connection-nat-state=!dstnat
Thanks to your observation, I was able to make my security cameras visible from outside my house; However for the “raw” rule in prerouting the “connection-nat-state =! Dstnat” is not possible, and I have it disabled.
You know how I could make this rule work without blocking the cameras, Thanks!
Resolved!!!
I had to put the rules of accepting the list of white IPs from first into “RAW”, and everything was fine now. Thanks!!!
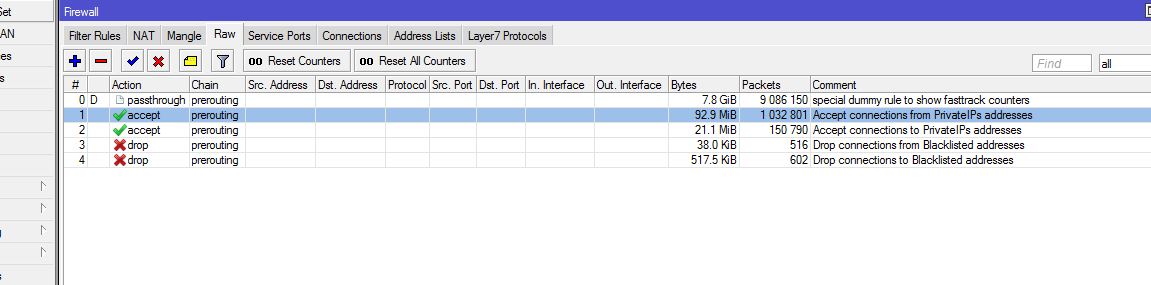
Hi,
I need help for this script. Im using this script but some times my wan adress comes to the list OR my ipblock. i create new rule to accept my ip but traffic down when i try to use. here is my rules, can some one help me to solve this issue ?
Thanks.
8  ;;; Exceptions
      chain=prerouting action=accept log=no log-prefix="" src-address-list=exceptions

 9  ;;; Exceptions
      chain=prerouting action=accept log=no log-prefix="" dst-address-list=exceptions

10  ;;; Exceptions
      chain=output action=accept log=no log-prefix="" src-address-list=exceptions

11  ;;; Exceptions
      chain=output action=accept log=no log-prefix="" dst-address-list=exceptions

12    ;;; BlackList
      chain=prerouting action=drop log=no log-prefix="" src-address-list=dynamicBlacklist

13    ;;; BlackList
      chain=prerouting action=drop log=no log-prefix="" dst-address-list=dynamicBlacklist

14    ;;; BlackList
      chain=output action=drop log=no log-prefix="blcklist src" src-address-list=dynamicBlacklist

15    ;;; BlackList
      chain=output action=drop log=no log-prefix="blcklist dst" dst-address-list=dynamicBlacklist

16    chain=prerouting action=drop dst-port=22,23,8290,8291 log=no log-prefix="" protocol=tcp src-address-list=!secure

17    chain=prerouting action=drop dst-port=22,23,8290,8291 log=no log-prefix="" protocol=udp src-address-list=!secure

18    chain=output action=drop dst-port=22,23,8290,8291 log=no log-prefix="" protocol=tcp src-address-list=!secure

19    chain=output action=drop dst-port=22,23,8290,8291 log=no log-prefix="" protocol=udp src-address-list=!secure

20    chain=prerouting action=drop in-interface=wan dst-port=53 log=no log-prefix="" protocol=tcp

21    chain=prerouting action=drop in-interface=wan dst-port=53 log=no log-prefix="" protocol=udp
Thanks! I will check it out when I’m on location.
Actually, Im glad to inform you today that the current release has added a new patch for greatly improved import speed for the importing of static dns entries, one thing you will notice is that, the cpu usage is no longer at 100% during import and the import process is much faster. I will be doing some benchmarks of RouterOS before and after the patch to demonstrate the difference, and it is a remarkable improvement indeed.
My list will not be moving to DNS. It over complicates the process and provides little if any advantages.
What is the command to write the blacklist to a usb-stick?
Thanks
The list is stored in memory while active.
If you need to use a flash drive for the update, just add the path of the usb drive to the path of the fetch and import lines.
Hi,
First of all thank you for this great script. I have a few questions:
- Why there are 2 schedules? And if there are 2 it can’t have the same name as in your example.
 /system scheduler
add interval=1d name=UpdateBlackList on-event="/system script run updateBlacklist" policy=ftp,reboot,read,write,policy,test,password,sniff,sensitive \
    start-date=jan/01/1970 start-time=05:00:0
/system scheduler
add interval=00:00:00 name=UpdateBlackList on-event="/system script run blacklistUpdate" policy=ftp,reboot,read,write,policy,test,password,sniff,sensitive \
    start-date=jan/01/1970 start-time=00:00:0
- What kind of chain is this “Attacks” ? It should be input or forward chain, am I right ?
/ip firewall filter
add action=drop chain=Attacks comment="Drop connections FROM blacklisted hosts" src-address-list=dynamicBlacklist
add action=drop chain=Attacks comment="Drop connections TO blacklisted hosts" dst-address-list=dynamicBlacklist
Two schedulers can have the same name, it is weird to have though.
Also not sure the second scheduler is totally correct. At least it can be written better.
See: http://forum.mikrotik.com/t/radius-server-not-working-in-2-8-11/127/1
The “Attacks” chain is a custom chain, take a look at the jump rules further down.
/ip firewall filter
#...
add action=jump chain=input comment="Check for bad stuff in \"Attack\" chain" jump-target=Attacks
#...
add action=jump chain=forward comment="Check for bad stuff in \"Attack\" chain" jump-target=Attacks
You can read more here: https://wiki.mikrotik.com/wiki/Manual:IP/Firewall/Filter
The firewall shown in the first post is just an example, you might want you edit it for your own use or make your own.
Thanks for explanation.
can some one share firewall rules for this script ? which is correct ? using raw or filter for this script. also sometimes my puplic ip’s come to the list. how can i remove them ? and how can i create expection rule for them ?
Thanks.
Hello Dave!
Works perfectly on hAp AC lite , RB951G-2Hnd.
Thank you very much for this! Great work!!
cheers
Here is the script i use to save and execute the blacklist (dynamic.rsc) from a usb drive (named usb1)
/system script add name=updateBlacklist-usb1 owner=admin policy=read,write,test source=“# Import Intrus Managed Filter Lists\r\n# (C)2016 David Joyce, Intrus Technologies\r\n\r\n:log warning "Blacklist update in 30 seconds";\r\n# :delay 10\r\n\r\n:local model \t[/system resource get board-name]\r\n:local version\t[/system resource get version]\r\n:local memory\t[/system resource get total-memory]\r\n:local uname\t[/system identity get name]\r\n:local scriptVer 2017.5.2a\r\n\r\n:local name ""\r\n:local ver ""\r\n\r\n:for i from=0 to=([:len $uname] - 1) do={ \r\n :local char [:pick $uname $i]\r\n :if ($char = " ") do={ :set $char "%20" }\r\n :set name ($name . $char)\r\n}\r\n\r\n:for i from=0 to=([:len $version] - 1) do={ \r\n :local char [:pick $version $i]\r\n :if ($char = " ") do={\r\n :set $char "%20"\r\n }\r\n :set ver ($ver . $char)\r\n}\r\n\r\n\r\n:log warning "Downloading current Blacklist for this model";\r\n/tool fetch mode=https dst-path="/usb1/dynamic.rsc" \\r\n\turl="https://mikrotikfilters.com/download.php?get=dynamic&model=$model&version=$ver&memory=$memory&id=$name&ver=$scriptVer";\r\n\r\n:log warning "Disabling info logging…";\r\n/system logging disable 0\r\n\r\n:log warning "Removing expiring address-list entries…";\r\n:foreach i in=[/ip firewall address-list find ] \\r\n\tdo={ :if ( [/ip firewall address-list get $i list] = "dynamicBlacklist" ) \\r\n do={ /ip firewall address-list remove $i } }\r\n\r\n:log warning "Importing current Blacklist…";\r\n/import file-name=/usb1/dynamic.rsc\r\n\r\n:log warning "Removing temp file…";\r\n/file remove usb1/dynamic.rsc\r\n\r\n:log warning "Blacklist Update Complete.";\r\n/system logging enable 0”
so far, so good.
Could you please edit your post and use “Code” tag to paste script content once again. It is hard to read it now.
here you go 
# Import Intrus Managed Filter Lists
# (C)2016 David Joyce, Intrus Technologies

:log warning "Blacklist update in 30 seconds";
# :delay 10

:local model 	[/system resource get board-name]
:local version	[/system resource get version]
:local memory	[/system resource get total-memory]
:local uname	[/system identity get name]
:local scriptVer   2017.5.2a

:local name ""
:local ver ""

:for i from=0 to=([:len $uname] - 1) do={
  :local char [:pick $uname $i]
  :if ($char = " ") do={ :set $char "%20" }
  :set name ($name . $char)
}

:for i from=0 to=([:len $version] - 1) do={
  :local char [:pick $version $i]
  :if ($char = " ") do={
    :set $char "%20"
  }
  :set ver ($ver . $char)
}


:log warning "Downloading current Blacklist for this model";
/tool fetch mode=https dst-path="/usb1/dynamic.rsc" \
	url="https://mikrotikfilters.com/download.php?get=dynamic&model=$model&version=$ver&memory=$memory&id=$name&ver=$scriptVer";

:log warning "Disabling info logging...";
/system logging disable 0

:log warning "Removing expiring address-list entries...";
:foreach i in=[/ip firewall address-list find ] \
	do={ :if ( [/ip firewall address-list get $i list] = "dynamicBlacklist" ) \
    do={ /ip firewall address-list remove $i } }

:log warning "Importing current Blacklist...";
/import file-name=/usb1/dynamic.rsc

:log warning "Removing temp file...";
/file remove usb1/dynamic.rsc

:log warning "Blacklist Update Complete.";
/system logging enable 0
I’ve updated the script with support for USB Flash as well as the new RB1100AHx4 with internal storage.
I has also reworked the backend and script for more accurate accounting. Please update your scripts.
# Import Intrus Managed Filter Lists
# © 2016-2017 David Joyce, Intrus Technologies

##### Update your path, is you are using a USB Flash or other storage

:global datapath "disk1/dynamic.rsc"

###### DO NOT EDIT BELOW THIS POINT ######

##### Delay for 10 seconds to allow the WAN to come online after a reboot
:log warning "Blacklist update in 10 seconds";
:delay 10

##### Pull info to report to the server, used to download the correct list as well as stats collecting
##### software ID is used as the unique ID on the server side, this allows us to identify different
##### routers behind a NAT router. Please do not remove it.
:local model 	[/system resource get board-name]
:local version	[/system resource get version]
:local memory	[/system resource get total-memory]
:local uname	[/system identity get name]
:local softid        [/system license get software-id]
:local scriptVer   2017.5.30c

##### Scrub the device name and version to prevent http errors
:local name ""
:local ver ""

:for i from=0 to=([:len $uname] - 1) do={
  :local char [:pick $uname $i]
  :if ($char = " ") do={ :set $char "%20" }
  :set name ($name . $char)
}

:for i from=0 to=([:len $version] - 1) do={
  :local char [:pick $version $i]
  :if ($char = " ") do={
    :set $char "%20"
  }
  :set ver ($ver . $char)
}

#### Begin download of current blacklist
:log warning "Downloading current Blacklist for this model";
/tool fetch mode=https dst-path="$datapath" \
	url="https://mikrotikfilters.com/download.php?get=dynamic&model=$model&version=$ver&memory=$memory&id=$name&ver=$scriptVer&softid=$softid";

##### Disable the log (We don't need 20k lines of adds and removes in the log
:log warning "Disabling info logging...";
/system logging disable 0

##### Find the "dynamicBlacklist" entries and remove them
:log warning "Removing expiring address-list entries...";
:foreach i in=[/ip firewall address-list find ] \
	do={ :if ( [/ip firewall address-list get $i list] = "dynamicBlacklist" ) \
    do={ /ip firewall address-list remove $i } }

##### Import the downloaded blacklist
:log warning "Importing current Blacklist...";
/import file-name="$datapath"

##### Find and remove the downloaded file
:log warning "Removing temp file...";
/file remove [find name=$datapath]

##### Turn the logging back on
:log warning "Blacklist Update Complete.";
/system logging enable 0
Also - The server is now blocking routers that excessively download the list. (I have several people that are trying to update every minute.)