Haha, very funny 
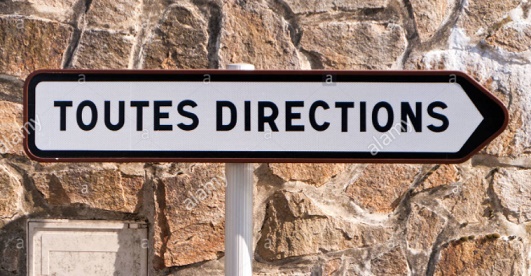
Same with this in french, I did not under stand what city this sign will take you to, did not find it on the map.
.
Haha, very funny
Same with this in french, I did not under stand what city this sign will take you to, did not find it on the map.
.
If we started to nitpick over your numbers, it would be interesting to see the malicious_ping-per-capita table/ranking … I guess that would completely change the ranking. Vatican might end up on top (not sure if there’s actually any IP address space allocated to that country?).
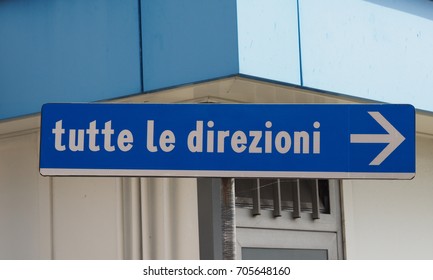
Seems like French won another war (just like they did with roundabouts) … I seem to notice more and more traffic signs around Europe, which read something like “other directions” (but in country’s official language which makes it as undecipherable as the sign you posted).
The intelligence agencies G7 + rogue know how to pattern match based on AI systems that constantly monitor/scan the terabytes^42 of data they collect on a constant and persistent basis. In the USA/Canada they have 20+ data centers in secret locations where each data center is humongous is size and scope. Once that pattern is identified they follow that stream with unbridled enthusiasm. Believe it or not 
meanwhile I accept ICMP which allows me to do the troubleshooting I need for such things as wireguard connections and to no detrimental impact on my router performance…
Off course all IP I do white-list manually or trough port knock can ping my router. This way I can test stuff from remote location.
Not only on France:
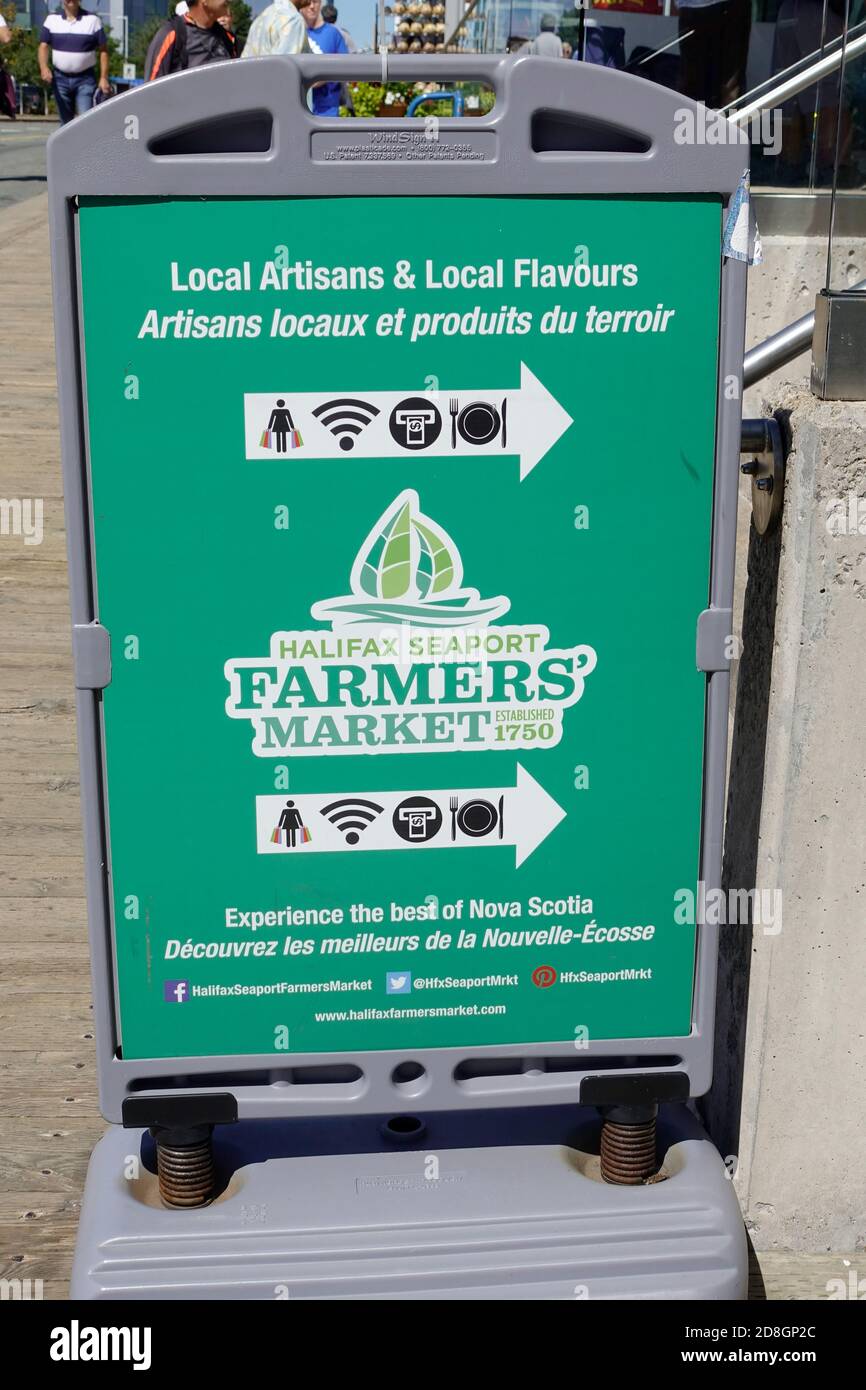
I did not know that in Canada they are so sexist that the woman is pictured with shopping bags !!!
And they put, in order of preference, Women, Wi-Fi, Money and Food…
:)))))))
But with all the seriousness… why people block ICMP? It’s harmful. Even blocking just ECHO and leaving rest of the ICMP alone is at best annoying. Rate limiting this to a reasonable value - sure, but blocking it flat-out is imho more harmful than helpful.
Point taken rextended, but it could be a man wearing a dress…
THis however is clearly “over the top”
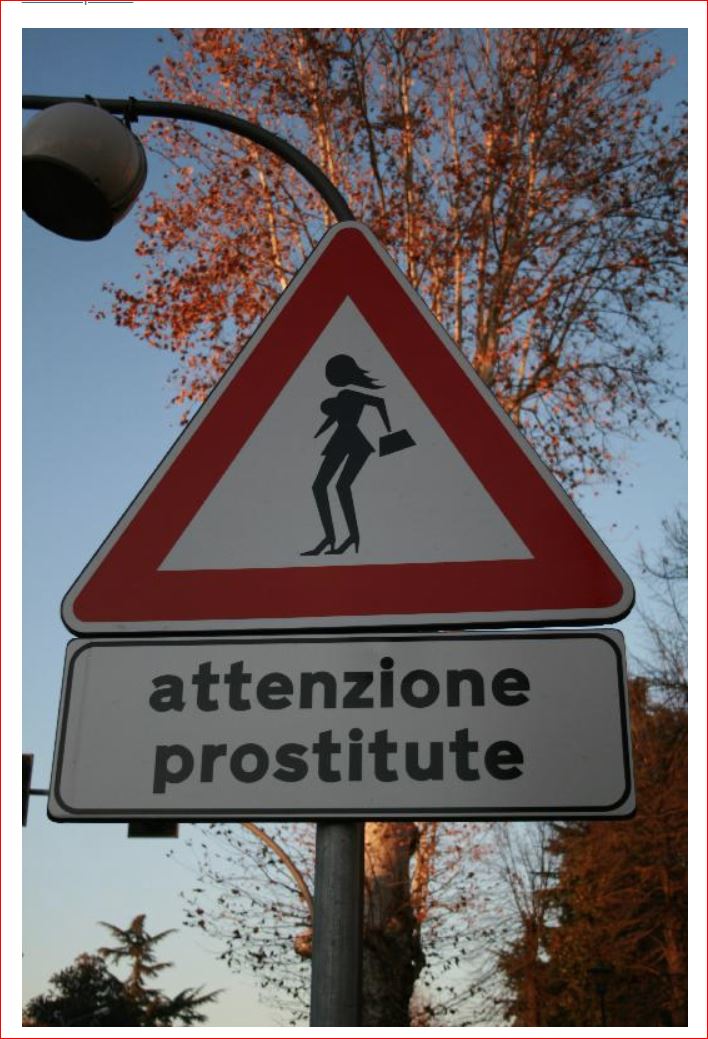
It’s not a photomanipulation…
Is TRUE…
It is the same person who tries to limit torrents nowadays or insists on restricting sites on the internet with layer7…
With the bandwidth available these days, compared to the past,
only blocking malformed ICMPs makes sense (ehm… read the page linked to my signature…).
The right way is to block the “malformed” and limit the number of pings, in order not to collaborate with the ICMP Storm Attack…
The counterfeit IP comes as a source and the ECHO response goes to join the DDoS attack …
Edit, NM read the whole thread it ended up in the sewer LOL.
Okay, but I am a minimalist.
If my home network should have it then I will add it.
If its strictly hobby fun and not necessary then I dont want to add it.
I did once monkey with ICMP settings and jump rules and it was a disaster.
Microsoft suggested it years ago as best practice.. I think it is still blocked in the default OS’s firewall rules..
For example, none of the M$ servers are pingable, but all of Google’s are.
Hello,
In order not to create a new topic I want to ask how to properly block ICMP ping? There are many examples that block all icmp. Experts say this is not right. How is it right?
as follows?
/ip firewall filter
add action=accept chain=input comment="Access Normal Ping" in-interface-list=WAN limit=50/5s,2:packet protocol=icmp
add action=drop chain=input comment="Drop excess pings" in-interface-list=WAN protocol=icmp
or as follows?
/ip firewall filter
add chain=input protocol=icmp action=jump jump-target=icmp
add chain=icmp protocol=icmp icmp-options=0:0 action=accept comment="ICMP echo reply"
add chain=icmp protocol=icmp icmp-options=3:0 action=accept comment="ICMP net unreachable"
add chain=icmp protocol=icmp icmp-options=3:1 action=accept comment="ICMP host unreachable"
add chain=icmp protocol=icmp icmp-options=3:4 action=accept comment="ICMP host unreachable fragmentation required"
add chain=icmp protocol=icmp icmp-options=4:0 action=accept comment="ICMP allow source quench"
add chain=icmp protocol=icmp icmp-options=8:0 action=accept comment="ICMP allow echo request"
add chain=icmp protocol=icmp icmp-options=11:0 action=accept comment="ICMP allow time exceed"
add chain=icmp protocol=icmp icmp-options=12:0 action=accept comment="ICMP allow parameter bad"
add chain=icmp action=drop comment="ICMP deny all other types"
or..
/ip firewall filter
add action=drop chain=input comment="drop echo request" icmp-options=8:0 \ in-interface-list=WAN protocol=icmp
is there a better method?
Thank you!
Yes, there is, as suggested above. Allow ICMP to flow freely, except ICMP echo requests if you feel like throttling them to max N per unit of time.
Blocking ICMP completely causes many things to stop working (most notably, path MTU discovery); blocking ping requests completely doesn’t prevent other methods of discovery that your device exists, so you may get too little benefit for too much work.
Yes there is a better method.. Leave ICMP alone.
Do you have an actual issue you are trying to fix by blocking ICMP?
You can add this to block ping from user who tries more than just ping.
If anyone for some reason try to reach any port on my router(s) that are not open, they are blocked to access any thing on my router (ICMP/web ++) for 24 hours. If they are testing out my router, they have nothing here to do.
More info here: http://forum.mikrotik.com/t/configuration-to-block-users-that-tries-to-access-router-on-non-open-port-s/151840/1
Kevinds,
Yes, there is a ping flood on my device at least twice a week, which puts a lot of strain on the channel. So I wanted to ask which example would be the best.
Is this?
/ip firewall filter
add chain=input protocol=icmp action=jump jump-target=icmp
add chain=icmp protocol=icmp icmp-options=0:0 action=accept comment="ICMP echo reply"
add chain=icmp protocol=icmp icmp-options=3:0 action=accept comment="ICMP net unreachable"
add chain=icmp protocol=icmp icmp-options=3:1 action=accept comment="ICMP host unreachable"
add chain=icmp protocol=icmp icmp-options=3:4 action=accept comment="ICMP host unreachable fragmentation required"
add chain=icmp protocol=icmp icmp-options=4:0 action=accept comment="ICMP allow source quench"
add chain=icmp protocol=icmp icmp-options=8:0 [b][u]action=DROP [/u][/b]comment="ICMP allow echo request"  << =====
add chain=icmp protocol=icmp icmp-options=11:0 action=accept comment="ICMP allow time exceed"
add chain=icmp protocol=icmp icmp-options=12:0 action=accept comment="ICMP allow parameter bad"
add chain=icmp action=drop comment="ICMP deny all other types"
Sindy,
will this option be good?
To which channel, the one between the router and the internet or the one between the router and the rest of your own network?
If the one towards internet, blocking the ping requests will only mean you won’t respond them, but you cannot prevent them from coming.
So to reduce the load of the router and the upload direction of the uplink channel, the right thing would be to add the ping sources to an address list if they exceed some rate, and to drop anything matching that address list as source in /ip firewall raw, as @Jotne suggests. But this won’t lower the load of the channel in download direction. To do that, you’d have to agree with your upstream ISP.
between the router and the internet.
Flood packets are coming from the Internet (Wan). OK, I’ll try the @Jotne version.
/ip firewall raw
add action=drop chain=prerouting comment="Drop user that has tried ports that are not open and has been added to block list" in-interface=ether1  src-address-list=FW_Block_unkown_port
But those icmp rules i showed but needed?