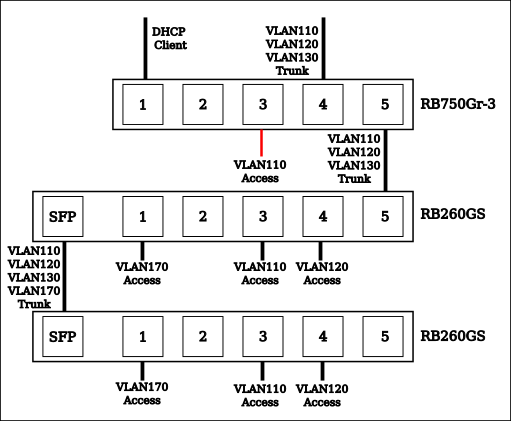
Expanding on VLAN solution

With hat in hand I am back to the MikroTik knowledge well looking for some insight. How do I create an access VLAN on the router port 3, within the current configuration?

With the help of the community Implementing a VLAN solution - #47 by colporteur I managed to get the above setup working using bridge VLANs.

I wanted to build on the success by expand the configuration, adding a VLAN acces port 3 on the router. My goal was a device would connect to port 3 and receive an IP address from the associated DHCP pool. I am unable to get it working.

I can expand access ports on any of the switches but no success on adding an access port on the router. I’ve tried numerous configurations, to many to list here before seeking help. After countless hours I have run out of attempts.

What changes do I need to make in the router code to configure a VLAN110 as an access port 3?

# 2026-01-07 15:44:29 by RouterOS 7.20.6
# software id = JPC6-9H6F
#
# model = RB750Gr3

/interface bridge
add admin-mac= auto-mac=no comment=defconf name=bridge
/interface vlan
add comment=VLAN interface=ether5 name=vlan110 vlan-id=110
add comment=VLAN interface=ether5 name=vlan120 vlan-id=120
add comment=VLAN interface=ether5 name=vlan130 vlan-id=130
/interface list
add comment=defconf name=WAN
add comment=defconf name=LAN
/ip pool
add name=dhcp ranges=192.168.87.200-192.168.87.254
add name=dhcp_pool1 ranges=192.168.110.200-192.168.110.254
add name=dhcp_pool2 ranges=192.168.120.200-192.168.120.254
/ip dhcp-server
add address-pool=dhcp interface=bridge name=defconf
add address-pool=dhcp_pool1 interface=vlan110 name=dhcp1
add address-pool=dhcp_pool2 interface=vlan120 name=dhcp2
/disk settings
set auto-media-interface=bridge auto-media-sharing=yes auto-smb-sharing=yes
/interface bridge port
add bridge=bridge comment=defconf interface=ether2
add bridge=bridge comment=defconf interface=ether3
add bridge=bridge comment=defconf interface=ether4
add bridge=bridge comment=defconf interface=ether5
/ip neighbor discovery-settings
set discover-interface-list=LAN
/interface list member
add comment=defconf interface=bridge list=LAN
add comment=defconf interface=ether1 list=WAN
/ip address
add address=192.168.87.1/24 comment=defconf interface=bridge network=\
    192.168.87.0
add address=192.168.110.1/24 comment=VLAN interface=vlan110 network=\
    192.168.110.0
add address=192.168.120.1/24 comment=VLAN interface=vlan120 network=\
    192.168.120.0
add address=192.168.130.1/24 comment=VLAN interface=vlan130 network=\
    192.168.130.0
/ip dhcp-client
add comment=defconf interface=ether1
/ip dhcp-server network
add address=192.168.87.0/24 comment=defconf dns-server=192.168.87.1 gateway=\
    192.168.87.1 netmask=24
add address=192.168.110.0/24 gateway=192.168.110.1
add address=192.168.120.0/24 gateway=192.168.120.1
/ip dns
set allow-remote-requests=yes
/ip dns static
add address=192.168.87.1 comment=defconf name=router.lan type=A
/ip firewall filter
add action=accept chain=input comment=VLAN
add action=accept chain=input comment=\
    "defconf: accept established,related,untracked" connection-state=\
    established,related,untracked
add action=drop chain=input comment="defconf: drop invalid" connection-state=\
    invalid
add action=accept chain=input comment="defconf: accept ICMP" protocol=icmp
add action=accept chain=input comment=\
    "defconf: accept to local loopback (for CAPsMAN)" dst-address=127.0.0.1
add action=drop chain=input comment="defconf: drop all not coming from LAN" \
    in-interface-list=!LAN
add action=accept chain=forward comment="defconf: accept in ipsec policy" \
    ipsec-policy=in,ipsec
add action=accept chain=forward comment="defconf: accept out ipsec policy" \
    ipsec-policy=out,ipsec
add action=fasttrack-connection chain=forward comment="defconf: fasttrack" \
    connection-state=established,related hw-offload=yes
add action=accept chain=forward comment=\
    "defconf: accept established,related, untracked" connection-state=\
    established,related,untracked
add action=drop chain=forward comment="defconf: drop invalid" \
    connection-state=invalid
add action=drop chain=forward comment=\
    "defconf: drop all from WAN not DSTNATed" connection-nat-state=!dstnat \
    connection-state=new in-interface-list=WAN
/ip firewall nat
add action=masquerade chain=srcnat comment=VLAN src-address=192.168.110.0/24
add action=masquerade chain=srcnat src-address=192.168.120.0/24
add action=masquerade chain=srcnat comment="defconf: masquerade" \
    ipsec-policy=out,none out-interface-list=WAN
/ipv6 firewall address-list
add address=::/128 comment="defconf: unspecified address" list=bad_ipv6
add address=::1/128 comment="defconf: lo" list=bad_ipv6
add address=fec0::/10 comment="defconf: site-local" list=bad_ipv6
add address=::ffff:0.0.0.0/96 comment="defconf: ipv4-mapped" list=bad_ipv6
add address=::/96 comment="defconf: ipv4 compat" list=bad_ipv6
add address=100::/64 comment="defconf: discard only " list=bad_ipv6
add address=2001:db8::/32 comment="defconf: documentation" list=bad_ipv6
add address=2001:10::/28 comment="defconf: ORCHID" list=bad_ipv6
add address=3ffe::/16 comment="defconf: 6bone" list=bad_ipv6
/ipv6 firewall filter
add action=accept chain=input comment=\
    "defconf: accept established,related,untracked" connection-state=\
    established,related,untracked
add action=drop chain=input comment="defconf: drop invalid" connection-state=\
    invalid
add action=accept chain=input comment="defconf: accept ICMPv6" protocol=\
    icmpv6
add action=accept chain=input comment="defconf: accept UDP traceroute" \
    dst-port=33434-33534 protocol=udp
add action=accept chain=input comment=\
    "defconf: accept DHCPv6-Client prefix delegation." dst-port=546 protocol=\
    udp src-address=fe80::/10
add action=accept chain=input comment="defconf: accept IKE" dst-port=500,4500 \
    protocol=udp
add action=accept chain=input comment="defconf: accept ipsec AH" protocol=\
    ipsec-ah
add action=accept chain=input comment="defconf: accept ipsec ESP" protocol=\
    ipsec-esp
add action=accept chain=input comment=\
    "defconf: accept all that matches ipsec policy" ipsec-policy=in,ipsec
add action=drop chain=input comment=\
    "defconf: drop everything else not coming from LAN" in-interface-list=\
    !LAN
add action=fasttrack-connection chain=forward comment="defconf: fasttrack6" \
    connection-state=established,related
add action=accept chain=forward comment=\
    "defconf: accept established,related,untracked" connection-state=\
    established,related,untracked
add action=drop chain=forward comment="defconf: drop invalid" \
    connection-state=invalid
add action=drop chain=forward comment=\
    "defconf: drop packets with bad src ipv6" src-address-list=bad_ipv6
add action=drop chain=forward comment=\
    "defconf: drop packets with bad dst ipv6" dst-address-list=bad_ipv6
add action=drop chain=forward comment="defconf: rfc4890 drop hop-limit=1" \
    hop-limit=equal:1 protocol=icmpv6
add action=accept chain=forward comment="defconf: accept ICMPv6" protocol=\
    icmpv6
add action=accept chain=forward comment="defconf: accept HIP" protocol=139
add action=accept chain=forward comment="defconf: accept IKE" dst-port=\
    500,4500 protocol=udp
add action=accept chain=forward comment="defconf: accept ipsec AH" protocol=\
    ipsec-ah
add action=accept chain=forward comment="defconf: accept ipsec ESP" protocol=\
    ipsec-esp
add action=accept chain=forward comment=\
    "defconf: accept all that matches ipsec policy" ipsec-policy=in,ipsec
add action=drop chain=forward comment=\
    "defconf: drop everything else not coming from LAN" in-interface-list=\
    !LAN
/system clock
set 
/system identity
set name=Farmstar
/tool mac-server
set allowed-interface-list=LAN
/tool mac-server mac-winbox
set allowed-interface-list=LAN


The VLAN configuration on the RB750Gr3 is currently wrong, having one of the L2 misconfigurations, namely "VLAN interface on a slave interface":

ether5 is a slave interface of bridge, but then you put the 3 VLAN interfaces on ether5. You will need to fix this:

  • First, connect your device to ether2 or ether4 while making the changes.

  • Edit the 3 /interface vlan entries to have the parent interface as bridge instead of ether5:

    /interface vlan set [find interface=ether5] interface=bridge
    
  • At this point, you can already safely turn on vlan-filtering=yes on the bridge interface already, no need to do it at the end like the guides usually instructed:

    /interface bridge set bridge vlan-filtering=yes 
    
  • If you want ether5 to be only a trunk port instead of a hybrid port, change frame-types of ether5 to admit-only-vlan-tagged instead of the default admit-all.

    /interface bridge port
    set [find bridge=bridge interface=ether5] frame-types=admit-only-vlan-tagged
    

    If hybrid port is ok for you then you don't need this step.

  • Then add /interface bridge vlan entries to have the 3 VLANs as tagged on ether5:

    /interface bridge vlan
    add bridge=bridge tagged=bridge,ether5 vlan-ids=110
    add bridge=bridge tagged=bridge,ether5 vlan-ids=120
    add bridge=bridge tagged=bridge,ether5 vlan-ids=130
    

    Note: with current RouterOS version you can also only put tagged=ether5 instead of tagged=bridge,ether5 and it will work too. The router will add dynamic entries with tagged=bridge for you.

After these steps, your configuration is working like before the changes, with the 3 VLAN tagged on ether5. Now, to have ether3 becomes an access port of VLAN 110, you only need to:

  • Set the PVID of port ether3 to 110 and frame-types to admit-only-untagged-and-priority-tagged:

    /interface bridge port
    set [find bridge=bridge interface=ether3] frame-types=admit-only-untagged-and-priority-tagged pvid=110
    
  • That is actually enough. The router will create a dynamic entry in /interface bridge vlan for you to have ether3 in the untagged list of VLAN 110. If you don't like seeing dynamic entries, they you can optionally make the explicit change, by editing the entry of VLAN 110 and put ether3 in the untagged list:

    /interface bridge vlan
    set [find bridge=bridge vlan-ids=110] untagged=ether3 
    

The hEX RB750Gr3 has hardware offload support for Bridge VLAN Filtering, so switching and VLAN filtering will still be handled by the switch chip and work at wire-speed.


Another note: To match your diagram, you would need to make ether4 a trunk port of the 3 VLANs too. Before doing that, plug your WinBox PC to ether2 instead of ether4! Then:

  • Set frame types for ether4 like with ether5 (optional, not needed if admit-all is ok for you).

    /interface bridge port
    set [find bridge=bridge interface=ether4] frame-types=admit-only-vlan-tagged
    
  • Update the tagged list of the 3 /interface bridge vlan entries to include ether4 too:

    /interface bridge vlan
    set [find bridge=bridge vlan-ids=110] tagged=bridge,ether4,ether5
    set [find bridge=bridge vlan-ids=120] tagged=bridge,ether4,ether5
    set [find bridge=bridge vlan-ids=130] tagged=bridge,ether4,ether5
    

That's it!

Another update:

Your firewall currently has this rule at the top of the input chain:

Which is very unsafe, because you are opening the router wide open to the attackers on the internet. Instead of that, add the 3 VLAN interfaces to the interface list LAN:

/interface list member
add interface=vlan110 list=LAN
add interface=vlan120 list=LAN
add interface=vlan130 list=LAN

and DELETE that rule at the top of the input chain immediately afterwards.

Furthermore, you don't need the first two masquerade rules at the top of the NAT firewall table. You only need keep the masquerade rule with the defconf: masquerade comment.

Very little of what you have makes sense to me.
The diagram does not match the config.
You have vlans attached to an etherport not to the bridge.
You have the bridge ports overlapping the ports you assigned to vlans directly etc...
you have assigned a bridge an address and thus mixing apples and oranges in your approach which is clearly not warranted in this scenario.
Where is the pool and other settings for vlan130?
If you need another subnet for whatever reason, create another vlan etc and remove bridge from doing any dhcp etc.....

If you are not using ipv6 disable it. As noted, your first firewall rule is a hackers wet dream. So much so that if this has been connected to the internet, the first thing I would do is netinstall a fresh firmware and start from scratch.

I screwed up! I posted the wrong code. I wondered why the comments were not making sense. I had made the post after a long shift. I was tired and frustrated at not being able to make the configuration work. I thought, if I engaged the community before I go to sleep, I could revisit the problem with new eyes. My apologies, fatigue is not excuse. I should have been more diligent.

What I have to share is a working configuration! It seems when I am wrong, you folks are still right. You would figure garbage in equals garbage out. Not the case CGGXANNX suggestion was the bread crumbs I needed to resolve the issue.

I made a lot of config changes before I came to the well. After selecting an interface in the ports tab under bridge I notice the VLANs tab. That was were I needed to be.

[admin@FarmStar] > export show-sensitive 
# 2026-01-14 15:58:49 by RouterOS 7.20.6
# software id = JPC6-9H6F
#
# model = RB750Gr3
# serial number = 
/interface bridge
add comment=bridge_LAN name=bridge_LAN
add comment=bridge_VLAN name=bridge_VLAN vlan-filtering=yes
/interface vlan
add comment=VLAN interface=bridge_VLAN name=vlan110 vlan-id=110
add comment=VLAN interface=bridge_VLAN name=vlan120 vlan-id=120
add comment=VLAN interface=bridge_VLAN name=vlan130 vlan-id=130
/interface list
add comment=defconf name=WAN
add comment=defconf name=LAN
/ip hotspot profile
set [ find default=yes ] html-directory=hotspot
/ip pool
add name=default-dhcp ranges=192.168.88.10-192.168.88.254
add name=dhcp_pool1 ranges=192.168.87.200-192.168.87.254
add name=dhcp_pool2 ranges=192.168.110.200-192.168.110.254
add name=dhcp_pool3 ranges=192.168.120.200-192.168.120.254
/ip dhcp-server
add address-pool=dhcp_pool1 comment=bridge_LAN interface=bridge_LAN name=dhcp1
add address-pool=dhcp_pool2 comment=VLAN interface=vlan110 name=dhcp2
add address-pool=dhcp_pool3 comment=VLAN interface=vlan120 name=dhcp3
/disk settings
set auto-media-interface=*7 auto-media-sharing=yes auto-smb-sharing=yes
/interface bridge port
add bridge=bridge_VLAN comment=trunk_VLAN interface=ether5
add bridge=bridge_LAN comment=bridge_LAN interface=ether2
add bridge=bridge_VLAN comment=access_VLAN frame-types=admit-only-untagged-and-priority-tagged interface=ether3 pvid=110
/ip neighbor discovery-settings
set discover-interface-list=LAN
/ipv6 settings
set accept-redirects=no accept-router-advertisements=no
/interface bridge vlan
add bridge=bridge_VLAN comment=VLAN tagged=ether5,bridge_VLAN untagged=ether3 vlan-ids=110
add bridge=bridge_VLAN comment=VLAN tagged=ether5,bridge_VLAN vlan-ids=120
add bridge=bridge_VLAN comment=VLAN tagged=ether5,bridge_VLAN vlan-ids=130
/interface list member
add comment=defconf interface=ether1 list=WAN
add comment=bridge_LAN interface=bridge_LAN list=LAN
/ip address
add address=192.168.87.1/24 comment=bridge_LAN interface=bridge_LAN network=192.168.87.0
add address=192.168.110.1/24 comment=VLAN interface=vlan110 network=192.168.110.0
add address=192.168.120.1/24 comment=VLAN interface=vlan120 network=192.168.120.0
add address=192.168.130.1/24 comment=VLAN interface=vlan130 network=192.168.130.0
/ip dhcp-client
add comment=defconf interface=ether1
/ip dhcp-server network
add address=192.168.87.0/24 dns-server=192.168.87.1 gateway=192.168.87.1
add address=192.168.110.0/24 dns-server=192.168.1.110 gateway=192.168.110.1
add address=192.168.120.0/24 dns-server=192.168.120.1 gateway=192.168.120.1
/ip dns
set allow-remote-requests=yes
/ip firewall filter
add action=accept chain=input src-address=192.168.2.200
add action=accept chain=input comment="defconf: accept established,related,untracked" connection-state=established,related,untracked
add action=drop chain=input comment="defconf: drop invalid" connection-state=invalid
add action=accept chain=input comment="defconf: accept ICMP" protocol=icmp
add action=accept chain=input comment="defconf: accept to local loopback (for CAPsMAN)" dst-address=127.0.0.1
add action=drop chain=input comment="defconf: drop all not coming from LAN" in-interface-list=!LAN
add action=accept chain=forward comment="defconf: accept in ipsec policy" ipsec-policy=in,ipsec
add action=accept chain=forward comment="defconf: accept out ipsec policy" ipsec-policy=out,ipsec
add action=fasttrack-connection chain=forward comment="defconf: fasttrack" connection-state=established,related hw-offload=yes
add action=accept chain=forward comment="defconf: accept established,related, untracked" connection-state=established,related,untracked
add action=drop chain=forward comment="defconf: drop invalid" connection-state=invalid
add action=drop chain=forward comment="defconf: drop all from WAN not DSTNATed" connection-nat-state=!dstnat connection-state=new in-interface-list=WAN
/ip firewall nat
add action=masquerade chain=srcnat comment="defconf: masquerade" ipsec-policy=out,none out-interface-list=WAN
/ip service
set ftp disabled=yes
set ssh disabled=yes
set telnet disabled=yes
set www disabled=yes
set api disabled=yes
set api-ssl disabled=yes
/system clock
set time-zone-name=
/system identity
set name=FarmStar
/tool mac-server
set allowed-interface-list=LAN
/tool mac-server mac-winbox
set allowed-interface-list=LAN   

My thanks to those that responded.

  1. why two bridges,
    either one bridge and all vlans
    OR
    one bridge and simply assign ether2 the address 192.168.87.1

  2. This can be simplified too:

/interface bridge vlan
add bridge=bridge_VLAN comment=VLAN tagged=ether5,bridge_VLAN untagged=ether3 vlan-ids=110
add bridge=bridge_VLAN comment=VLAN tagged=ether5,bridge_VLAN vlan-ids=120,130
  1. Why do you have a pool for a non-existent subnet?

/ip pool
add name=default-dhcp ranges=192.168.88.10-192.168.88.254
add name=dhcp_pool1 ranges=192.168.87.200-192.168.87.254
add name=dhcp_pool2 ranges=192.168.110.200-192.168.110.254
add name=dhcp_pool3 ranges=192.168.120.200-192.168.120.254

4.How can your input chain have an allow rule for a non-existent address??

add action=accept chain=input src-address=192.168.2.200

Much appreciated A. I tried eliminating the bridge and assigning an interface an IP 192.168.87.1/30 but it didn’t work. I will go back and try it again.

I thought I had tried your simplified suggestion during my wash-rinse-repeat failed exercise of getting it working. I will try this again.

My bad. I thought I had removed all vestiges of.88 subnet. Looks like I missed something.

That IP was my management IP I deleted in the FW rules put not on the router. Looks like I missed something else.

I never pass the MTCNA at this rate:)