Looking at the block diagram for the hap be3 (https://cdn.mikrotik.com/web-assets/product_files/MA53UGHbeH_260229.png), I should be able to get hardware offload on ports 2-5, right? Bridge is configured with vlan filtering, I'm using it as a glorified switch/ap combo with eth1 as a trunk port.
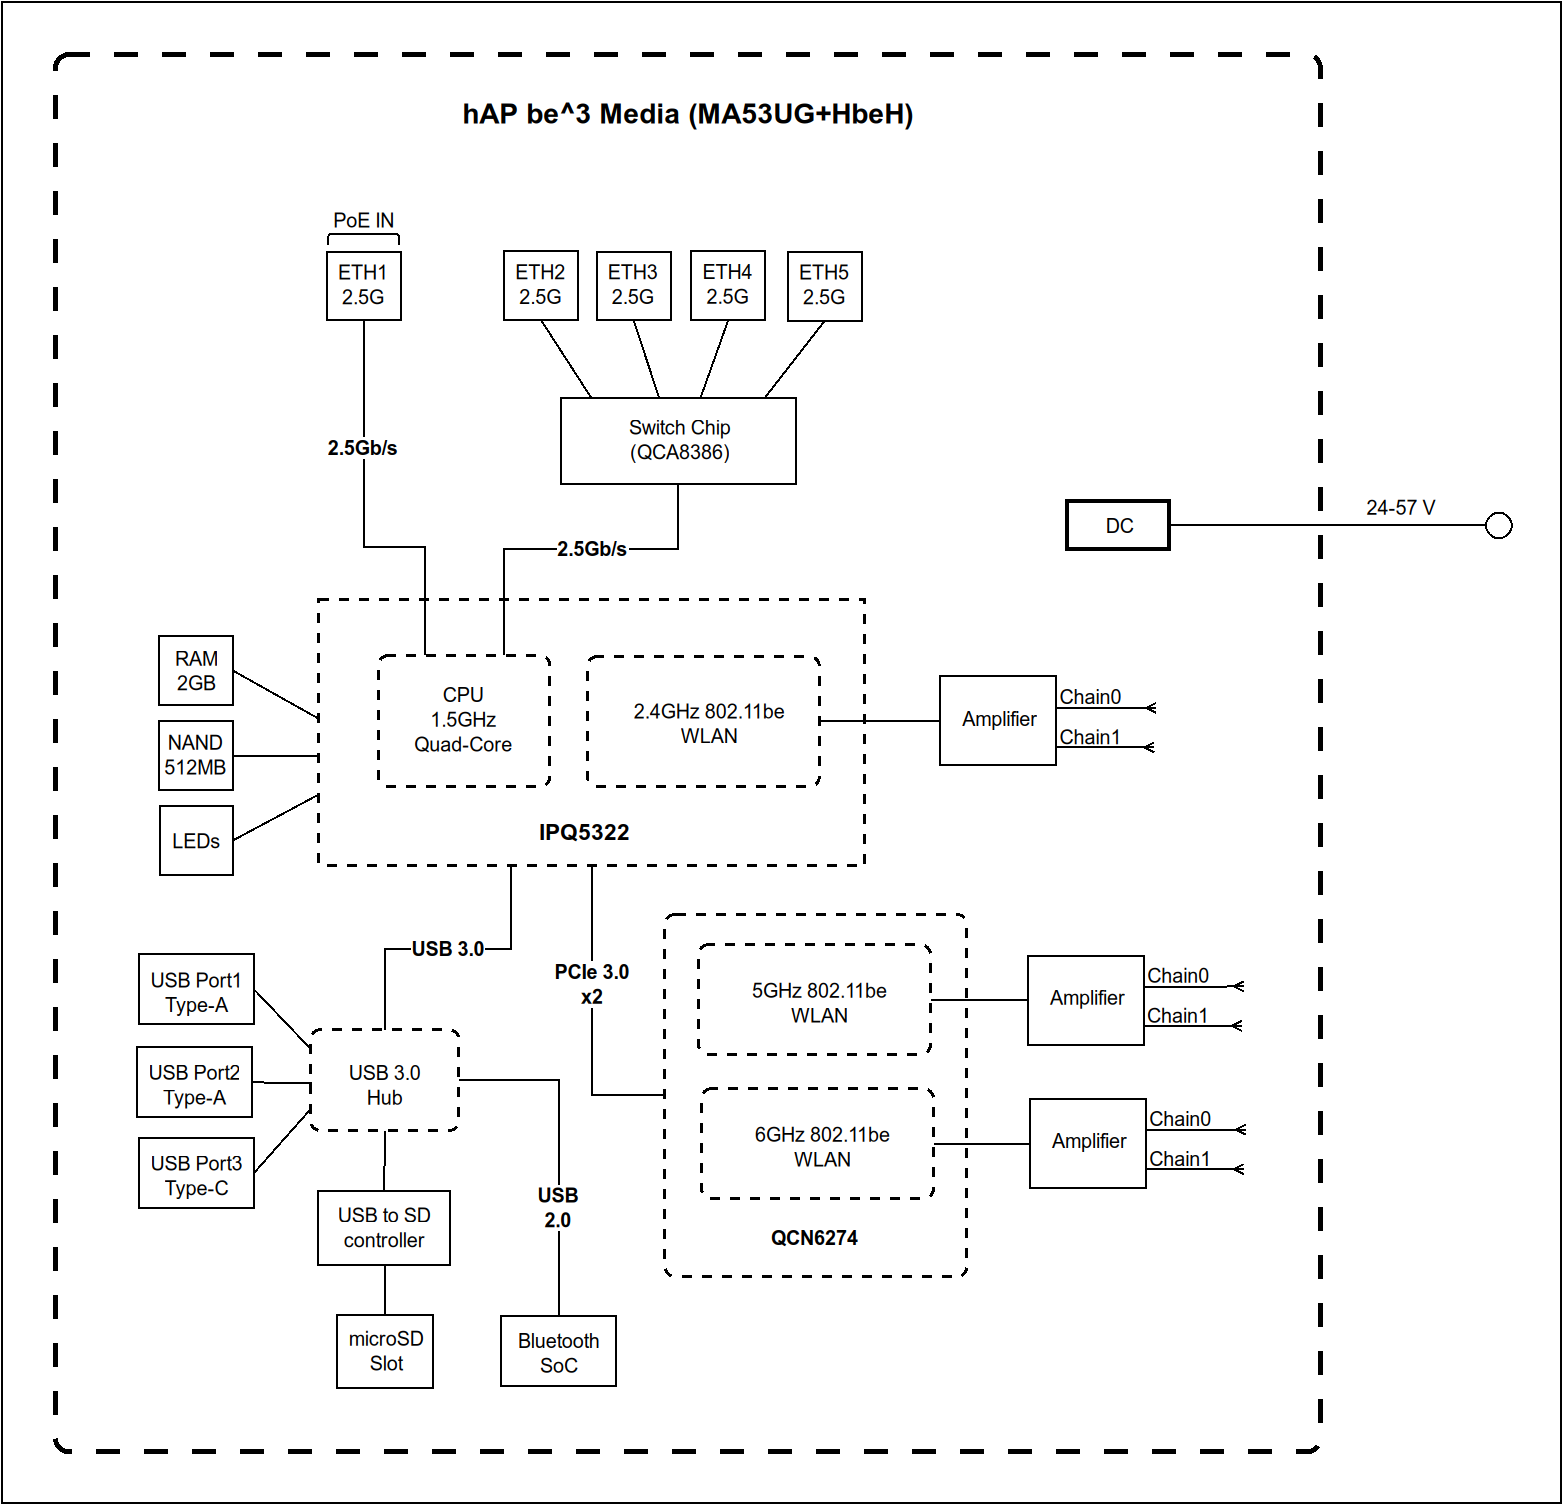
Also, should I move my trunk port to one of the ports connected to the switch chip?
[admin@hAP] > /interface bridge port print
Flags: I - INACTIVE; D - DYNAMIC
Columns: INTERFACE, BRIDGE, HW, HORIZON, TRUSTED, TRUSTED-RA, TRUSTED-DHCPV6, FAST-LEAVE, BPDU-GUARD, EDGE, POINT-TO-POINT, PVID, FRAME-TYPES
#    INTERFACE  BRIDGE   HW   HORIZON  TRUSTED  TRUSTED-RA  TRUSTED-DHCPV6  FAST-LEAVE  BPDU-GUARD  EDGE  POINT-TO-POINT  PVID  FRAME-TYPES
;;; defconf
0    ether1     bridge1  yes  none     no       no          no              no          no          auto  auto              99  admit-all
;;; defconf
1 I  ether2     bridge1  yes  none     no       no          no              no          no          auto  auto              20  admit-only-untagged-and-priority-tagged
;;; defconf
2 I  ether3     bridge1  yes  none     no       no          no              no          no          auto  auto              20  admit-only-untagged-and-priority-tagged
;;; defconf
3 I  ether4     bridge1  yes  none     no       no          no              no          no          auto  auto              20  admit-only-untagged-and-priority-tagged
;;; defconf
4 I  ether5     bridge1  yes  none     no       no          no              no          no          auto  auto              20  admit-only-untagged-and-priority-tagged
5  D wifi1      bridge1       none     no       no          no              no          no          auto  no                 1  admit-all
6  D wifi2      bridge1       none     no       no          no              no          no          auto  no                 1  admit-all
7  D wifi8      bridge1       none     no       no          no              no          no          auto  no                 1  admit-all
[admin@hAP] > /interface bridge print Flags: R - RUNNING0 R ;;; defconfname="bridge1" mtu=auto actual-mtu=1500 l2mtu=1596 arp=enabled arp-timeout=auto mac-address=38:32:7A:06:50:33 protocol-mode=rstp fast-forward=yes igmp-snooping=no auto-mac=no ageing-time=5m priority=0x8000 max-message-age=20s forward-delay=15s transmit-hold-count=6 vlan-filtering=yes ether-type=0x8100 pvid=1 frame-types=admit-only-vlan-tagged ingress-filtering=yes dhcp-snooping=nodhcpv6-snooping=no ra-guard=no port-cost-mode=long mvrp=no max-learned-entries=auto mlag-peer-port=none mlag-priority=128 mlag-heartbeat=5s