Hello,
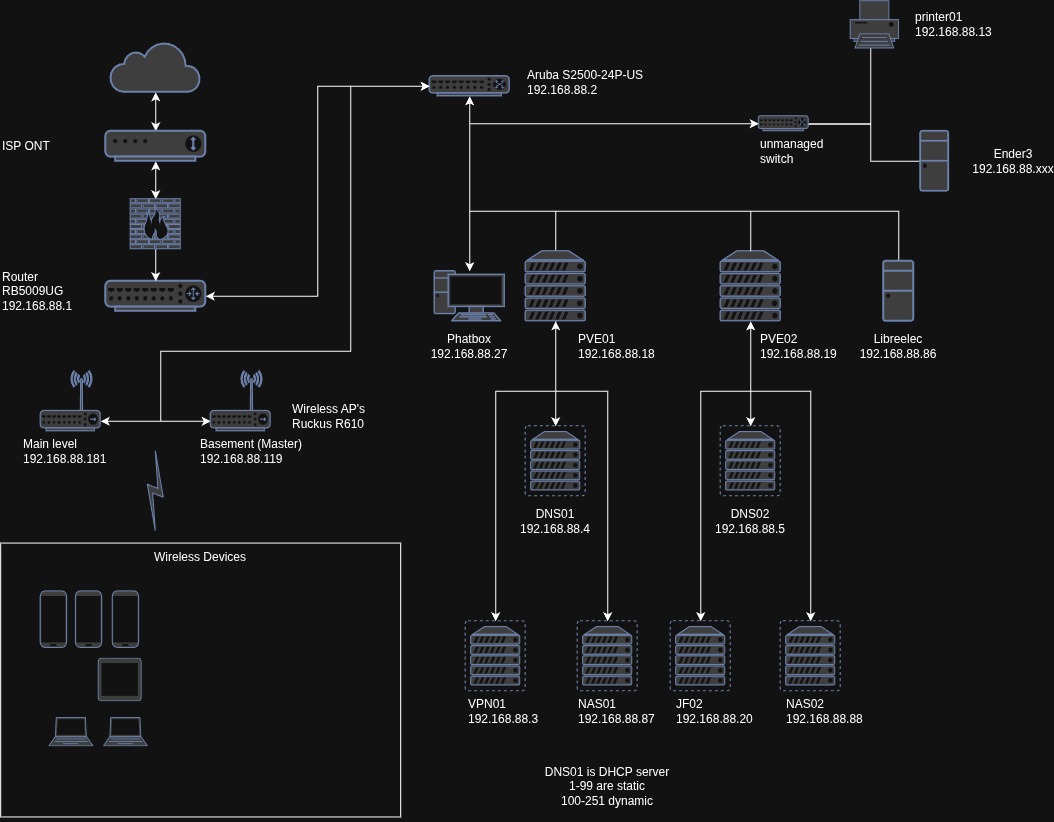
I've been successfully using wireguard for a few years now, running it on a dedicated VM within my network. The only configuration needed in my router was to NAT the UDP port to my vpn server.
I recently decided I'd like to try running wireguard on my 5009 and then I can eliminate the vpn VM.
I've successfully configured the WG on the Mikrotik, and a peer for my phone and the tunnel appears to work, although I cannot seem to access the internet or any network node on my network.
Here's how I was trying to set it up:
Router IP is 192.168.88.1
WG IP 10.0.0.1
Peer IP 10.0.0.2
I run my own DNS servers, and I'd like to continue using those for the wireguard peers. Hosts on my network are static. DHCP service is handled by the primary DNS server.
I've tried various firewall rules and NAT rules and nothing seems to work. Do you guys have any ideas what I'm missing?
Thanks
# 2026-08-26 17:30:17 by RouterOS 7.24.1
# software id =
#
# model = RB5009UG+S+
# serial number =
/interface bridge
add admin-mac=78:9A:18:BB:B9:3D auto-mac=no comment=defconf name=bridge \
    port-cost-mode=short
/interface ethernet
set [ find default-name=ether1 ] l2mtu=1514
set [ find default-name=ether2 ] l2mtu=1514
set [ find default-name=ether3 ] l2mtu=1514
set [ find default-name=ether4 ] l2mtu=1514
set [ find default-name=ether5 ] l2mtu=1514
set [ find default-name=ether6 ] l2mtu=1514
set [ find default-name=ether7 ] l2mtu=1514
set [ find default-name=ether8 ] l2mtu=1514
set [ find default-name=sfp-sfpplus1 ] l2mtu=1514
/interface wireguard
add listen-port=13231 mtu=1420 name=wg1
/interface bonding
add mode=802.3ad name=bonding1 slaves=ether7,ether8 transmit-hash-policy=\
    layer-2-and-3
/interface list
add comment=defconf name=WAN
add comment=defconf name=LAN
/interface wireless security-profiles
set [ find default=yes ] supplicant-identity=MikroTik
/ip kid-control
add disabled=yes fri=8h-21h30m mon=8h-21h30m name=kids rate-limit=100M sat=\
    8h-21h30m sun=8h-21h30m thu=8h-21h30m tue=8h-21h30m wed=8h-21h30m
/ip pool
add name=default-dhcp ranges=192.168.88.10-192.168.88.254
/ip smb users
set [ find default=yes ] disabled=yes
/queue type
add kind=fq-codel name=fq-codel
/queue tree
add bucket-size=0.01 max-limit=250M name=upload packet-mark=no-mark parent=\
    ether1 queue=fq-codel
add bucket-size=0.01 max-limit=250M name=download packet-mark=no-mark parent=\
    bridge queue=fq-codel
/interface bridge port
add bridge=bridge comment=defconf interface=ether2 internal-path-cost=10 \
    path-cost=10
add bridge=bridge comment=defconf interface=ether3 internal-path-cost=10 \
    path-cost=10
add bridge=bridge comment=defconf interface=ether4 internal-path-cost=10 \
    path-cost=10
add bridge=bridge comment=defconf interface=ether5 internal-path-cost=10 \
    path-cost=10
add bridge=bridge comment=defconf interface=ether6 internal-path-cost=10 \
    path-cost=10
add bridge=bridge comment=defconf interface=sfp-sfpplus1 internal-path-cost=\
    10 path-cost=10
add bridge=bridge interface=bonding1 internal-path-cost=10 path-cost=10
/ip firewall connection tracking
set udp-timeout=10s
/ip neighbor discovery-settings
set discover-interface-list=LAN
/interface list member
add comment=defconf interface=bridge list=LAN
add comment=defconf interface=ether1 list=WAN
add interface=wg1 list=LAN
/interface ovpn-server server
add mac-address=FE:F9:5B:31:91:D7 name=ovpn-server1
/interface wireguard peers
add allowed-address=10.0.0.2/32 interface=wg1 name="aaron iphone" public-key=\
    "<pub key>"
/ip address
add address=192.168.88.1/24 comment=defconf interface=bridge network=\
    192.168.88.0
add address=10.0.0.1/24 interface=wg1 network=10.0.0.0
/ip cloud
set ddns-enabled=yes update-time=no
/ip dhcp-client
add comment=defconf interface=ether1 name=ether1
/ip dhcp-server
add address-pool=default-dhcp disabled=yes interface=bridge lease-time=10m \
    name=defconf
/ip dhcp-server network
add address=192.168.88.0/24 comment=defconf dns-server=192.168.88.1 gateway=\
    192.168.88.1
/ip dns
set allow-remote-requests=yes
/ip dns static
add address=192.168.88.1 comment=defconf name=router.lan type=A
/ip firewall address-list
add address=<serialnumber>.sn.mynetname.net list=WAN-IP
add address=192.168.88.4 list=allowedDNS
add address=192.168.88.5 list=allowedDNS
/ip firewall filter
add action=jump chain=forward comment="jump to kid-control rules" \
    jump-target=kid-control
add action=accept chain=input comment="Allow Wireguard" disabled=yes \
    dst-port=13231 protocol=udp
add action=accept chain=input comment="Allow Wireguard" disabled=yes \
    dst-port=51820 protocol=udp
add action=accept chain=input comment=\
    "defconf: accept established,related,untracked" connection-state=\
    established,related,untracked
add action=drop chain=input comment="defconf: drop invalid" connection-state=\
    invalid
add action=accept chain=input comment="defconf: accept ICMP" \
    in-interface-list=LAN protocol=icmp
add action=drop chain=input comment="drop ICMP" disabled=yes \
    in-interface-list=WAN protocol=icmp
add action=accept chain=input comment=\
    "defconf: accept to local loopback (for CAPsMAN)" dst-address=127.0.0.1
add action=drop chain=input comment="defconf: drop all not coming from LAN" \
    in-interface-list=!LAN
add action=accept chain=forward comment="defconf: accept in ipsec policy" \
    ipsec-policy=in,ipsec
add action=drop chain=forward comment="drop port 53 TCP" dst-port=53 \
    protocol=tcp src-address-list=!allowedDNS
add action=drop chain=forward comment="drop port 53 UDP" dst-port=53 \
    protocol=udp src-address-list=!allowedDNS
add action=accept chain=forward comment="defconf: accept out ipsec policy" \
    ipsec-policy=out,ipsec
add action=fasttrack-connection chain=forward comment="defconf: fasttrack" \
    connection-state=established,related disabled=yes
add action=accept chain=forward comment=\
    "defconf: accept established,related, untracked" connection-state=\
    established,related,untracked
add action=drop chain=forward comment="defconf: drop invalid" \
    connection-state=invalid
add action=drop chain=forward comment=\
    "defconf: drop all from WAN not DSTNATed" connection-nat-state=!dstnat \
    connection-state=new in-interface-list=WAN
/ip firewall nat
add action=masquerade chain=srcnat comment="defconf: masquerade" \
    ipsec-policy=out,none out-interface-list=WAN
add action=masquerade chain=srcnat comment="HAIRPIN NAT" dst-address=\
    192.168.88.0/24 src-address=192.168.88.0/24
add action=dst-nat chain=dstnat comment="passive xdcc enable" \
    dst-address-list=WAN-IP dst-port=2500-2525 protocol=tcp to-addresses=\
    192.168.88.27
add action=dst-nat chain=dstnat comment="wireguard vpn port forward" \
    dst-address-list=WAN-IP dst-port=51820 protocol=udp to-addresses=\
    192.168.88.3
add action=dst-nat chain=dstnat comment="port forward for bittorrent" \
    dst-port=54321 in-interface-list=WAN protocol=tcp to-addresses=\
    192.168.88.27
add action=dst-nat chain=dstnat comment="port forward for bittorrent" \
    dst-port=54321 in-interface-list=WAN protocol=udp to-addresses=\
    192.168.88.27
add action=dst-nat chain=dstnat comment="port forward for mumble" disabled=\
    yes dst-port=64738 in-interface-list=all protocol=udp to-addresses=\
    192.168.88.12
add action=dst-nat chain=dstnat comment="port forward for mumble" disabled=\
    yes dst-port=64738 in-interface-list=all protocol=tcp to-addresses=\
    192.168.88.12
add action=dst-nat chain=dstnat comment="port forward for iperf3" disabled=\
    yes dst-port=5201 in-interface-list=WAN protocol=tcp to-addresses=\
    192.168.88.3
/ip ipsec profile
set [ find default=yes ] dpd-interval=2m dpd-maximum-failures=5
/ip kid-control device
add mac-address=D0:50:99:9C:97:CE name=winPC user=kids
/ip service
set ftp disabled=yes
set telnet disabled=yes
set www available-from=192.168.88.0/24
set api disabled=yes
set api-ssl disabled=yes
/ipv6 firewall address-list
add address=::/128 comment="defconf: unspecified address" list=bad_ipv6
add address=::1/128 comment="defconf: lo" list=bad_ipv6
add address=fec0::/10 comment="defconf: site-local" list=bad_ipv6
add address=::ffff:0.0.0.0/96 comment="defconf: ipv4-mapped" list=bad_ipv6
add address=::/96 comment="defconf: ipv4 compat" list=bad_ipv6
add address=100::/64 comment="defconf: discard only " list=bad_ipv6
add address=2001:db8::/32 comment="defconf: documentation" list=bad_ipv6
add address=2001:10::/28 comment="defconf: ORCHID" list=bad_ipv6
add address=3ffe::/16 comment="defconf: 6bone" list=bad_ipv6
/ipv6 firewall filter
add action=drop chain=forward comment="rule to drop all IPv6 traffic"
add action=accept chain=input comment=\
    "defconf: accept established,related,untracked" connection-state=\
    established,related,untracked
add action=drop chain=input comment="defconf: drop invalid" connection-state=\
    invalid
add action=accept chain=input comment="defconf: accept ICMPv6" protocol=\
    icmpv6
add action=accept chain=input comment="defconf: accept UDP traceroute" port=\
    33434-33534 protocol=udp
add action=accept chain=input comment=\
    "defconf: accept DHCPv6-Client prefix delegation." dst-port=546 protocol=\
    udp src-address=fe80::/10
add action=accept chain=input comment="defconf: accept IKE" dst-port=500,4500 \
    protocol=udp
add action=accept chain=input comment="defconf: accept ipsec AH" protocol=\
    ipsec-ah
add action=accept chain=input comment="defconf: accept ipsec ESP" protocol=\
    ipsec-esp
add action=accept chain=input comment=\
    "defconf: accept all that matches ipsec policy" ipsec-policy=in,ipsec
add action=drop chain=input comment=\
    "defconf: drop everything else not coming from LAN" in-interface-list=\
    !LAN
add action=accept chain=forward comment=\
    "defconf: accept established,related,untracked" connection-state=\
    established,related,untracked
add action=drop chain=forward comment="defconf: drop invalid" \
    connection-state=invalid
add action=drop chain=forward comment=\
    "defconf: drop packets with bad src ipv6" src-address-list=bad_ipv6
add action=drop chain=forward comment=\
    "defconf: drop packets with bad dst ipv6" dst-address-list=bad_ipv6
add action=drop chain=forward comment="defconf: rfc4890 drop hop-limit=1" \
    hop-limit=equal:1 protocol=icmpv6
add action=accept chain=forward comment="defconf: accept ICMPv6" protocol=\
    icmpv6
add action=accept chain=forward comment="defconf: accept HIP" protocol=139
add action=accept chain=forward comment="defconf: accept IKE" dst-port=\
    500,4500 protocol=udp
add action=accept chain=forward comment="defconf: accept ipsec AH" protocol=\
    ipsec-ah
add action=accept chain=forward comment="defconf: accept ipsec ESP" protocol=\
    ipsec-esp
add action=accept chain=forward comment=\
    "defconf: accept all that matches ipsec policy" ipsec-policy=in,ipsec
add action=drop chain=forward comment=\
    "defconf: drop everything else not coming from LAN" in-interface-list=\
    !LAN
/ipv6 nd
# automatic dns option advertising is not started, re-apply dns config
set [ find default=yes ] advertise-dns=yes
/system clock
set time-zone-name=America/Chicago
/system ntp client
set enabled=yes
/system ntp server
set enabled=yes manycast=yes
/system ntp client servers
add address=74.208.117.38
add address=4.53.160.75
add address=162.159.200.123
/tool graphing interface
add
/tool graphing resource
add
/tool mac-server
set allowed-interface-list=LAN
/tool mac-server mac-winbox
set allowed-interface-list=LAN
 Step 1 is check the obvious, right?