Hello team,
am fairly new to Mikrotik equipments and learning the ropes so to say. Need your support to get best practices implemented in our project.
Idea is to have one RB3011 act as ISP router for traffic coming from L3 Switches via Trunks.
Checked some of online articles and found that earlier implementation for VLANs has given way to the New Bridge architecture,
where they act as switch for traffic transport between VLAN Ports.
With this understanding am checking on following scenario:
3 VLANs : VLAN10 → Management → Would need Internet access but excluded from VLAN30.
: VLAN20 → Backhaul → ISP link may terminate into this VLAN - So that other VLANs requiring internet access (e.g. VLAN10) may have it through this one via Inter-VLAN routing.
: VLAN30 → Service → Does not require internet access, traffic needs to be excluded from all VLANs.
So on RB3011, bridges are defined for separate VLANs and VLANs are linked to respective ports.
Queries:
To carry ISP traffic across VLAN20, WAN IP is assigned to interface eth2 and is linked with VLAN 20 bridge.
Since WAN IP is from public range, attaching it with a VLAN (VLAN 20) having private range the right way to implement? or do we have better solutions?
Idea is to have interface eth2 communicate with ISP while VLAN20 do Inter-VLAN routing to provide www access to other VLAN’s traffic.
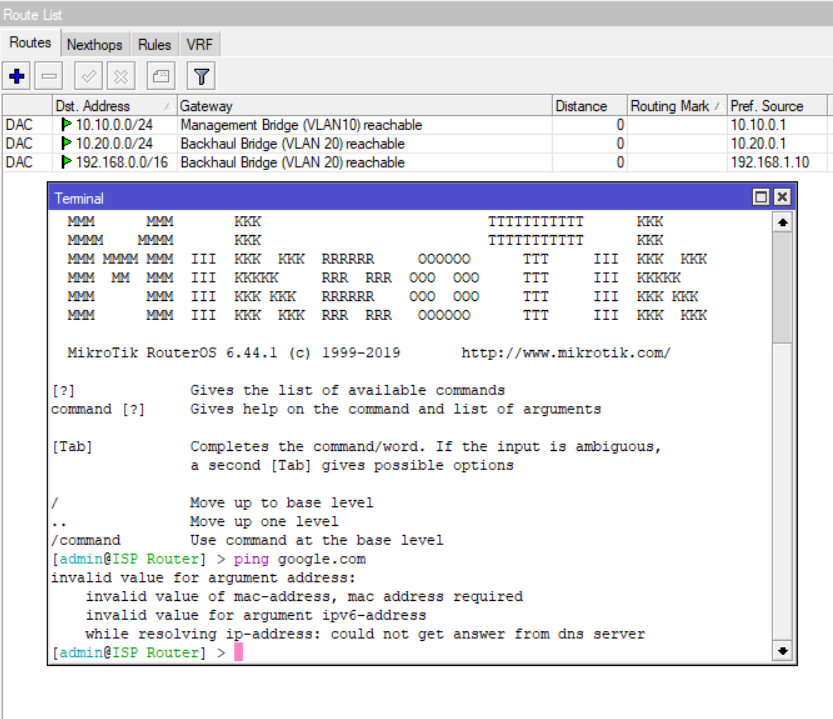
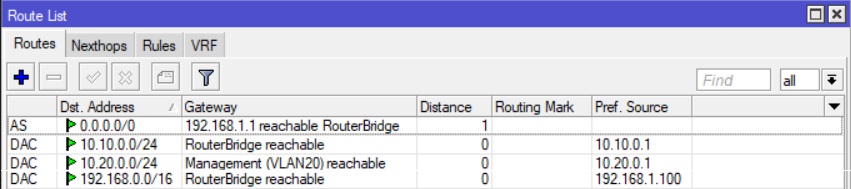
To get this working had to add default route towards ISP gateway otherwise traffic was dropping just at the ISP border (ISP Gateway was not pingable).
Any reasons why WAN routes are not getting published automatically? (Screenshots attached - With/Without Default route)
How to Allow or Block Inter-VLAN traffic routing? Right now all VLANs are pinging from all VLANs. Have set VLAN filtering ON but NO Firewall rules.
Finally thanks for taking time to go though this lengthy writeup.
Would appreciate any and every response/suggestion you wish to make.
Thanks again.
Raunak
Best thing would be to have a read through this excellent reference.
Then work on your config and when you think its almost there… post your complete config.
/export hide-sensitive file=yourconfig
Many thanks Anav,
its really a Good reference for anyone starting.
Going through it and checking my config, but in the mean while could you give some quick advice on the following:
Is it better to have one Bridge for all VLANs or have separate bridge for each of the VLANs?
How do we best terminate WAN links into the bridge - Just attach WAN interface to the bridge?
OR
Attach WAN interface to a VLAN and which then goes to a bridge (Common/ separate)?
Also if possible could you help explain these inbuilt network types - WAN, LAN - How do they work internally- are they internal labels with some standard functioning logic?
Personally, I tend to use one bridge for all my vlans.
There is no need to add WANS to bridges for normal setups. There are cases where it is required or possibly advantageous but my experience is limited.
Traffic is directed via routing not bridges.
WAN generally describes the external interface (that faces the internet). LAN refers in general terms to all the subnets behind the router.
You can make any lists you want on interface list members so the router is very flexible on configuration.
In RouterOS speak, input refers TO the ROUTER, forward refers to across the router (wan to lan, lan to wan and lan to lan).
Just to add a few bits to what @anav already answered:
It’s better to have single bridge. On certain device family (namely CRS3xx) operations are HW-offloaded when configured on single bridge. Other devices might get HW offload (or not, don’t hold your breath) … Anyhow, bridge mimics behaviour of a switch and switches have all ports served by single chip.
If you really want to attach WAN to bridge (regardless the reason), use dedicated VLAN on a common bridge. You have to ask yourself though if you really want to just attach WAN interfaces to bridge … you probably want to have firewall and routing engine between WAN and LANs so you need to be careful when attaching WAN interface to bridge not to create a by-pass around firewall.
These are not network types, they are simple network interface lists. You can construct as many as you want. Then you can use those interface lists in certain configurations, such as firewall rules - when a rule should match in-interface or out-interface, you can change it to using in-interface-list or out-interface-list. This comes handy when you have a few interfaces that you want to treat in same way and this saves you from constructing a few copies of identical rules (except for interface part). Or it comes handy when you need to change interface (i.e. when you move from one WAN technology to another, e.g. from IP with DHCP to PPPoE or from wired to wireless) and you only adjust interface membership instead of rewriting a few (hundred) firewall rules.
Thanks Anav & MKx for the help.
Every bit is valuable.
@anav > That tag line ======>>>> "Follow my advice at your own risk! (Sob & mkx forced me to write that!)"
You are a Good Help, all across the Forum!
@MKx: As suggested, Trying to get WAN traffic (eth2-ISP Link) to internal VLAN20 (codenamed Backhaul) which is attached to the common Bridge (RouterBridge).
Would you please review following config if it fits the bill, getting worked up for no structured implementation procedure in place
Here are the excerpts:
Idea is to
*Define Interface 2 for WAN link:
set [ find default-name=ether2 ] name="ISP Link"
*set 2 IP interface on VLAN10 -> One for WAN other for internal VLAN:
add address=10.10.0.1/24 interface="Backhaul (VLAN10)" network=10.10.0.0
add address=192.168.1.100/16 interface="Backhaul (VLAN10)" network=192.168.0.0
*Attach Interface to VLAN10:
add interface="ISP Link" name="Backhaul (VLAN10)" vlan-id=10
*Add VLAN10 to the bridge:
add bridge=RouterBridge interface="Backhaul (VLAN10)" pvid=10
So ideally any traffic on the bridge should be able to find its path through Bridge->VLAN10-> int eth2(192.168.1.100)->Gateway (192.168.1.1)
While I'm able to ping all defined internal interfaces, traffic is getting stuck on the int eth:
[admin@ISP Router] > ping 192.168.1.1
SEQ HOST SIZE TTL TIME STATUS
0 192.168.1.1 timeout
1 192.168.1.1 timeout
2 192.168.1.100 84 64 990ms host unreachable
3 192.168.1.1 timeout
sent=4 received=0 packet-loss=100%
// Route list attached for ref.
Also for some reason, DHCP is not through.
Attaching my system on Port eth 5 should get it a 10.50.X.X IP, but it doesn't seem to be working. VLAN filtering OFF at the moment I think.
Easy things first: you have /interface bridge port setup in place, but corresponding /interface bridge vlan part is missing.
The hard one: what exactly are you trying to get at with the “Backhaul (VLAN10)” interface? Try to answer in plain words (perhaps add a simple graphic) without trying to comment your current setup.
Idea is to have a separate VLAN with Internet access, so that other VLANs can share it.
In doing so, am trying to attach one physical interface(eth2) to a VLAN(VLAN10) which in-turn makes use of Bridge for Inter-VLAN routing.
Conceptually unsure of configuration hierarchy/ structure though.
Draw a diagram of what you require. Then we will able to dissect your config with more assurances.
Bridgeports are not set to vlans but are set to etherports or wlans. Because bridgeports also serve to communicate ingress, pvids are used when an etherport or a WLAN is to be an access port type connection (in other words the device at the other end of the cable cannot dish out tagged frames (such as a PC, a printer, a standard access point, an unmanaged switch etc…)
One conceptual thing: bridge acts similarly to ethernet switch. Meaning that any ports, members of same bridge, can communicate with each other directly, bypassing any routing/firewall functionality. If your LAN hosts are in different IP subnet than your public IP address, this won’t work for them.
Most users, though, want to use routing/firewall engine, which meany you can’t just bridge WAN and LAN ports (or VLAN interfaces for that matter) …
The other thing: when it comes to different VLANs, separated by routing/firewall engine, inherently they are all equal, none of them are “main”. Firewall rules might allow some of them more liberal communications than the other ones, but that’s firewall configuration. So it’s not that one VLAN has internet access and other VLANs share it. Actually it’s that router has internet access and it provides that internet access to other VLANs according to routing/firewall rules.
Follow @anav’s suggestion: draw your logical topology which is likely a star-shaped topology with a few VLANs radiating out of router/firewall … WAN/internet is, conceptually, yet another branch radiating out of your router/firewall (and only routing/firewall rules make it quite distinct from other “legs”). Then read excellent tutorial linked in @anav’s first reply to your original post.
Hello Anav, MKx
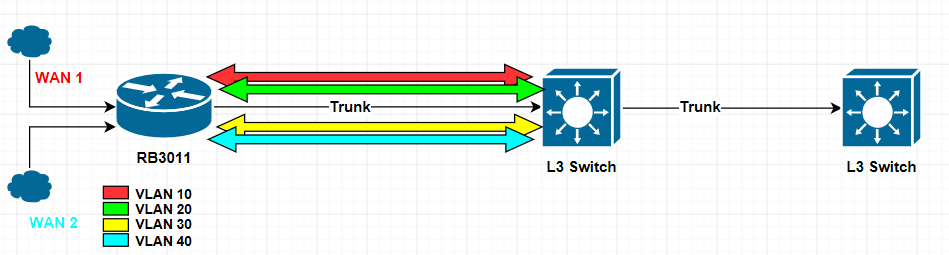
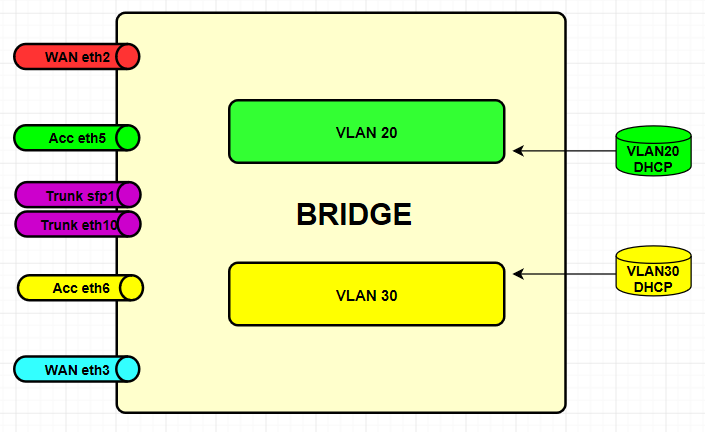
here are some simplified diagrams:
1st the Topology :
Lets say we have 2 seperate WAN links, that are supposed to serve different set of subscribers (VLANs).
WAN1 caters to VLAN 20 subscribers while WAN2 caters to VLAN30 subscribers.
To make this distinction happen, original though was to attach WAN1 interface to VLAN10 and WAN2 to VLAN40
and then make use of firewall policies to perform inter-VLAN routing.
From the latest info, this doesn’t seem conceptually correct.
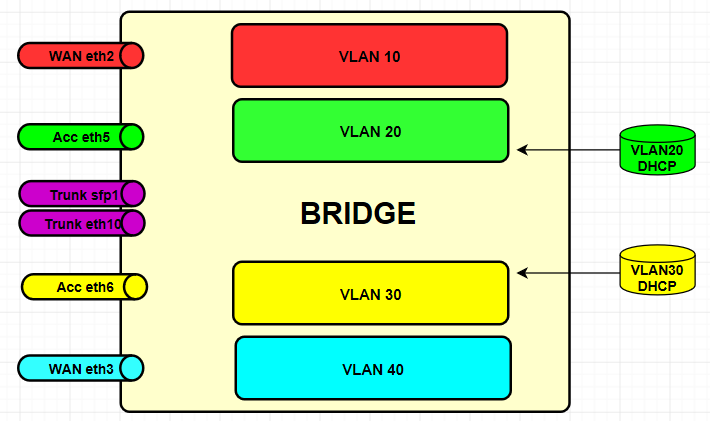
Checking on the bridge:
has now given way to…
From what you shared in the last post about functioning of the bridge, it seems original idea is flawed and we can not terminate WAN directly to a specific VLAN.
If each VLAN is just another Interface on the switch, it would not hold any special characteristic to encapsulate Internet traffic and/or distribute it privately to certain VLANs.
Coming to implementation does the new bridge arrangement looks conceptually coherent?
Both WAN interfaces are terminating directly on the bridge and firewall filters could be used to shape traffic across VLAN.
Also do you see any possibility for traffic may move freely, going around the firewall rules? What other way then??
and how are we supposed to mark default gateway at bridge for multiple WANs?
On the DHCP side is it fine to attach all DHCP servers to the base bridge and allow DHCP traffic in firewall? Tried attaching DHCP with individual VLANs but it doesn’t seem to work.
Neither of concepts are entirely correct, but the second try looks slightly better. From connectivity point of view (either physical or VLAN connections) you have 6 logical connections of same importance:
WAN1
WAN2
VLAN 10
VLAN 20
VLAN 30
VLAN 40
Both ether ports that will act as connection for WAN1 and WAN2 will be used solely for single purpose and it’s not needed to join them to bridge.
After you set L2 config correctly (that includes port membership … e.g. set port ether5 as access (untagged) port of VLAN20, set sfp1 and ether10 as trunk ports - tagged member port of VLAN20 … and similarly for the rest of VLANs), you can proceed to L3 (IP) setup. Assign appropriate IP address (either statically, for VLAN interfaces you probably want that, or dynamically, depending on ISP requirements per WAN link) to all logical interfaces (logical interfaces include VLAN interfaces and both physical interfaces for WAN connections). Add basic LAN services to logical interfaces where you need them (e.g. DHCP server for individual VLANs).
When you’re done with IP3 configuration, you can proceed with routing stuff. If you only had single WAN interface, routing setup would be really trivial. In case where you have two WAN interfaces, you’ll have to play with routing rules to achieve wanted outcome (WAN1 for some subnets, WAN2 for other subnets … do you want to use WAN2 as backup WAN for first group of subnets in case WAN1 link fails? And the same for WAN1 link as backup for the second group?).
When you’re done with routing rules, you proceed to firewall rules … which subnet can communicate with which other networks (including internet) … which services on LAN do you want to expose to internet via port forwarding … etc.
After you’ve done all of the above conceptually, you start to make configuration changes on your RB3011.