L22UGS-5HaxD2HaxD + SXTsq-5axD

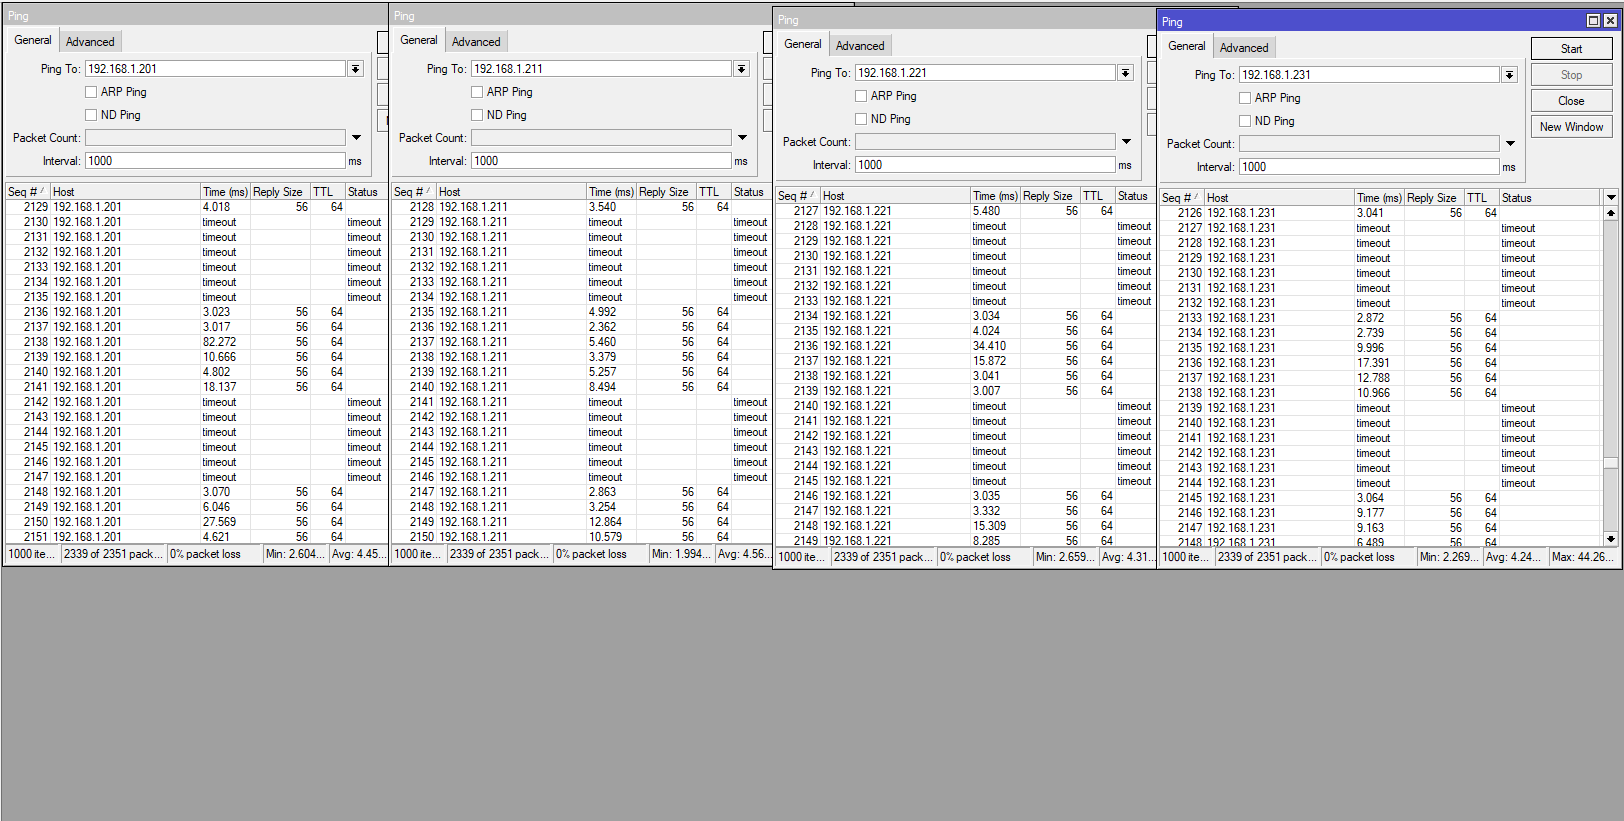
Have a small network using L22UGS-5HaxD2HaxD and 4 x SXTsq-5axD as stations, so only 5GHz enabled.
All stations are within 350meters from the AP with clear line of sight.
Average of -61db signal
Tx Rate=450-500Mbps
Rx Rate=200-300Mbps

At random times, all communication is dropped to all 4 stations at the same time, this lasts for 6 Pings each time:

This sometimes happens once in a few hours, or a few times within the same minute.

I tried the following already:

  • I have updated to 7.24.4 on all devices which did not seem to bring improvement.
  • Using Freq. Usage tool to determine best channel, changing to 3 different channels.
  • Dropping channel width.
  • Changing security type from WPA3 to WPA2

The customer is in a very remote location, no other properties are within 1.5km from them.
Anyone with advise would be greatly appreciated.

/export

add name=bridge1
/interface wifi
set [ find default-name=wifi1 ] configuration.mode=ap
interworking.realms-raw=""
/interface pppoe-client
add add-default-route=yes disabled=no interface=ether1 name=Parys-Internet
use-peer-dns=yes user=meteornek-757
/interface wifi channel
add band=5ghz-ax disabled=no frequency=5660 name=channel1
/interface wifi configuration
add disabled=no interworking.realms-raw="" name=wifi
add channel=channel1 channel.band=5ghz-ax .width=20/40mhz country=
"South Africa" disabled=no interworking.realms-raw="" name=
Kommandonek-TowerAP security.authentication-types=wpa2-psk ssid=
PI-Kommandonek
/interface wifi security
add authentication-types=wpa2-psk disabled=no name=Kommandonek
/interface wifi
set [ find default-name=wifi2 ] channel=channel1 channel.band=5ghz-ax
.frequency=5700 .width=20/40mhz configuration=Kommandonek-TowerAP
configuration.country="South Africa" .mode=ap .ssid=PI-Kommandonek
disabled=no interworking.realms-raw="" security=Kommandonek
/ip pool
add name=dhcp_pool0 ranges=192.168.1.100-192.168.1.200
/ip dhcp-server
add address-pool=dhcp_pool0 interface=bridge1 lease-time=1w name=dhcp1
/system logging action
set 1 disk-file-count=5
/dude
set enabled=yes
/interface bridge port
add bridge=bridge1 interface=wifi1
add bridge=bridge1 interface=wifi2
/ip address
add address=192.168.1.254/24 interface=bridge1 network=192.168.1.0
/ip dhcp-server network
add address=192.168.1.0/24 gateway=192.168.1.254
/ip firewall address-list
add address=service.parys.co.za list=Venga
add address=0.za.pool.ntp.org list=Venga
add address=1.ntp.za.pool.org list=Venga
add address=2.ntp.za.pool.org list=Venga
add address=3.ntp.za.pool.org list=Venga
add address=10.0.252.0/28 list=Venga
add address=upgrade.mikrotik.com list=Venga
add address=upgrade1.mikrotik.com list=Venga
add address=upgrade2.mikrotik.com list=Venga
add address=cloud.mikrotik.com list=Venga
add address=cloud1.mikrotik.com list=Venga
add address=cloud2.mikrotik.com list=Venga
add address=8.8.8.8 list=Venga
add address=172.16.1.3-172.16.1.4 list=Venga
add address=172.16.1.50 list=Venga
add address=172.16.1.1 list=Venga
add address=196.216.116.56 list=Venga
add address=172.16.1.12 list=Venga
/ip firewall filter
add action=drop chain=input in-interface=Parys-Internet protocol=!icmp
src-address-list=!Venga
/ip firewall nat
add action=masquerade chain=srcnat out-interface=Parys-Internet
add action=dst-nat chain=dstnat comment=Clubhouse-CPE dst-port=8292
in-interface=Parys-Internet protocol=tcp to-addresses=192.168.1.201
to-ports=8291
add action=dst-nat chain=dstnat comment=Lodge/Boma-CPE dst-port=8293
in-interface=Parys-Internet protocol=tcp to-addresses=192.168.1.211
to-ports=8291
add action=dst-nat chain=dstnat comment=Homestead/Chalet-CPE dst-port=8294
in-interface=Parys-Internet protocol=tcp to-addresses=192.168.1.221
to-ports=8291
add action=dst-nat chain=dstnat comment="Eagle's Nest-CPE" dst-port=8295
in-interface=Parys-Internet protocol=tcp to-addresses=192.168.1.231
to-ports=8291
/snmp
set enabled=yes
/system clock
set time-zone-name=Africa/Johannesburg
/system identity
set name=Kommandonek-Tower-AP
/system logging
add action=disk prefix=Wireless- topics=wireless
/system ntp client
set enabled=yes
/system ntp client servers
add address=0.za.pool.ntp.org
add address=1.za.pool.ntp.org
/system scheduler
add !days interval=1w name=Reboot-Weekly on-event="system reboot" policy=
ftp,reboot,read,write,policy,test,password,sniff,sensitive,romon
start-date=2026-09-23 start-time=06:00:00

Ignoring the fact that I mentioned the export—and you cut out parts that should have been left in (while it is correct to remove serial numbers, usernames, passwords, emails, etc.)— you used Winbox 3 and thus compromised the Wi-Fi configuration. That is the first point.

Paste this on terminal, of all devices, ans stop using WinBox 3 for manage wifi of that devices.

/int wifi
set [find] !interworking.realms
set [find] !interworking.realms-raw
/int wifi configuration
set [find] !interworking.realms
set [find] !interworking.realms-raw

Could you please provide clarity as I only removed the top 4 lines of the export file, nothing else was removed.

I now used Winbox V4.4 and pasted the provided code in the terminal of each device. Was Winbox 3 the cause of the issue?

Likely.

See:
After RouterOS version 7.22, CAPsMAN causes only iPhones (iOS) to be unable to connect to Wi-Fi

I have the same problem. Did you manage to solve it?

Hi @cristianm

Yes, the solution as supplied by @rextended fixed the issue. First get rid of Winbox3 and run this on AP and all Stations:

/int wifi
set [find] !interworking.realms
set [find] !interworking.realms-raw
/int wifi configuration
set [find] !interworking.realms
set [find] !interworking.realms-raw

Post from Rex marked as solution so it becomes more clear for others visiting this thread.