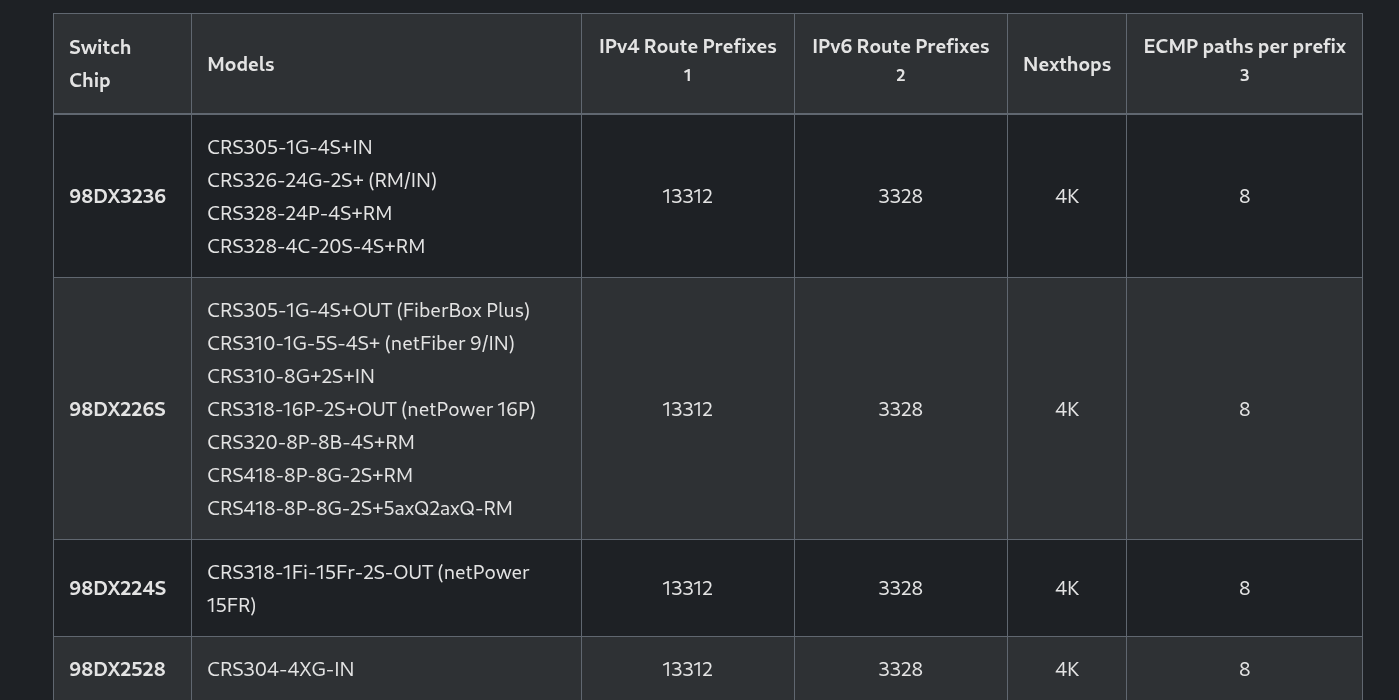
L3HW VXLAN finally works on the CRS317!

After seeing the notes in 7.24 about Hardware VXLAN now supporting vlans, I thought I'd give it a shot again (After my previous attempts here: Hardware VXLAN Broken recently? )

It works, AND it works using bridged ports, so you don't need to jump through hoops to try to only use a routed, non-bridged interface like the Howto says.

What they MEAN to say is that 'traffic can not leave the same interface it enters, otherwise it leaves untagged'. I kinda think this is a bug in the programming of the switch chip, but whatever.

Here's how I managed to get it to work.

In this example, your VTEP Peers are on VLAN999, and your VTEP traffic is going to be entering, tagged, via sfp1. You want to bring VLAN888 into this switch and have it leave via sfp2 (or any other ports. Just not sfp1)

  1. Start with a factory-reset CRS317, with two DACs to your main switch, in sfp1 (for ingress) and sfp2 (for normal traffic)
  2. Fix l2mtu on all the interfaces (set [ find ] l2mtu=10218)
  3. Create a bridge br0, and add sfp2 (and anything else you want, EXCEPT for sfp1) to it, creating your normal VLANs and IPs so you can access the switch. When you're happy with it, enable VLAN Filtering on it. If you lose access to the switch, factory reset and start again.
  4. Add VL888 to br0, and set it to be tagged on sfp2 (and any other ports, again, NOT SFP1)
  5. Enable L3 Hardware Offloading (Switch->Settings->switch1->L3 Hw Offloading). Also double check that the bridge ports have H next to them to confirm they're all being switched in hardware.
  6. Tricky Bit! Add sfp1 to br0, BUT, you need to remove sfp1 from the spanning tree domain. The easiest way to do this is to set it to be an edge port when you're adding it and ensure that it's set to 'admit only VLAN Tagged'
  7. Add VL999 to the bridge, and set it to be tagged on br0 and sfp1 ONLY. DO NOT ASSIGN IT TO ANY OTHER PORTS (If you do, the switch chip gets confused and you will have to reboot the switch. Yes seriously)
  8. Create br0/VL999 and assign the VTEP IP address to it
  9. If you're using OSPF or BGP, get that sorted out so that you can reach the other VTEP endpoints.

At this point you should be able to ping your other VTEP endpoints. Check your bridge ports to confirm sfp1 is an edge port, and all the rest are Forwarding=yes.

Basically, you have a bridge set up, you can ping your vtep endpoints, and VL888 is ready to go.

Create your VXLAN interface, in this example, 'vxlan888', with the VNI of 10888 (or whatever you want, I just don't like to accidentally mix up a VLAN and VXLAN, so I make sure the numbers are different), and set the bridge to be br0 and PVID being 888.

Add your VTEP Endpoints to the vxlan and it will switch to hardware mode (A 'H' will appear in the first column of the interface)

That's it! That's all it needs.

The most common issue I discovered when working this out is that if the switch chip gets confused it will either send traffic out the egress port (sfp2 in this example) as untagged, or, it won't send BUM traffic to the other endpoints. The only way to resolve this is to reboot the switch. Disabling/re-enabling L3HW does not fix it. It needs a complete reset.

The end result is this! https://mastodon.au/@xrobau/117142965429483736

Remember: If things aren't working as expected, just reboot the switch. If you've done everything right, it's a bug. Reboot!

Good luck!
that's very weird configuration. is it typical for crs317? because on my crs309 you just bridge vxlan tunel with sfp port as untagged, use ether type 9100 and that's it. you can send untagged and tagged traffic over vxlan

Nice, could you please provide your " /export compact"?

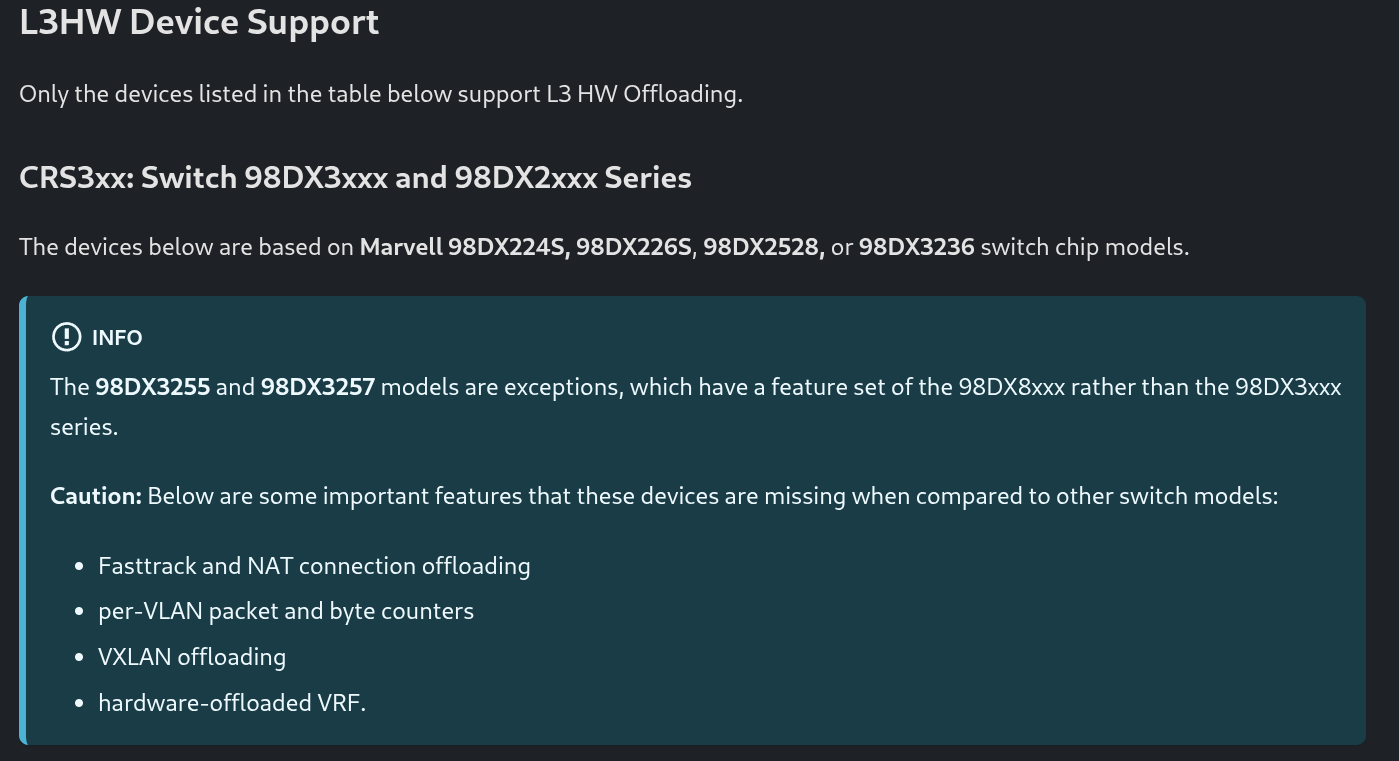
I have the same problem on MikroTik · CRS305-1G-4S+IN , I had to disable L3 HW offloading to make it work, I have configured tagged and untagged ports for VLAN4080 in bridge and It does not work with hw offload.

that's because crs305 doesn't support vxlan in hardware


but i dont even use vxlan there, I have vlan id 4080 taged for Bridge and sfpplus1 an untagged for ether1 and it does not work until I disable L3 hw

With the CRS305 and similar switches, you have a choice of either L3HW or Hardware Switching. You can't have both.

This is documented poorly, but I did find that information in a thread elsewhere. I have a few CRS305s but I just use them as 4 port 10g switches. I wouldn't think of using them for L3HW stuff.

Nice, could you please provide your " /export compact"?

There is far more information here than is required. I strongly suggest you just follow the instructions I provided, as trying to figure out what is happening here is just going to make you more confused.

However, this is the working switch. I've been working on L3 routing, which is why there is basic BGP and OSPF settings. You should ignore those bits!


[admin@Maurice-VXLAN] > /export compact 
# 2026-08-15 04:38:29 by RouterOS 7.24
# software id = GJ8I-2YA0
#
# model = CRS317-1G-16S+
# serial number = HGK09K672NY
/interface bridge
add mtu=10218 name=br0 vlan-filtering=yes
/interface ethernet
set [ find default-name=ether1 ] l2mtu=10218
set [ find default-name=sfp-sfpplus1 ] l2mtu=10218 mtu=10218
set [ find default-name=sfp-sfpplus2 ] disabled=yes l2mtu=10218 mtu=10218
set [ find default-name=sfp-sfpplus3 ] l2mtu=10218
set [ find default-name=sfp-sfpplus4 ] l2mtu=10218
set [ find default-name=sfp-sfpplus5 ] l2mtu=10218
set [ find default-name=sfp-sfpplus6 ] disabled=yes l2mtu=10218
set [ find default-name=sfp-sfpplus7 ] l2mtu=10218
set [ find default-name=sfp-sfpplus8 ] l2mtu=10218
set [ find default-name=sfp-sfpplus9 ] l2mtu=10218
set [ find default-name=sfp-sfpplus10 ] l2mtu=10218
set [ find default-name=sfp-sfpplus11 ] comment="Eth1/45 on sw2" disabled=yes \
    l2mtu=10218
set [ find default-name=sfp-sfpplus12 ] l2mtu=10218
set [ find default-name=sfp-sfpplus13 ] l2mtu=10218
set [ find default-name=sfp-sfpplus14 ] l2mtu=10218
set [ find default-name=sfp-sfpplus15 ] l2mtu=10218 mtu=10218
set [ find default-name=sfp-sfpplus16 ] disabled=yes l2mtu=10218 mtu=10218
/interface vxlan
add bridge=br0 bridge-pvid=1481 mac-address=C6:25:72:F7:23:6D mtu=9000 name=\
    vxlan1481 vni=101481
add bridge=br0 bridge-pvid=2220 mac-address=8A:21:37:38:51:FF mtu=9000 name=\
    vxlan2220 vni=102220
/interface vlan
add interface=br0 name=VL4 vlan-id=4
add interface=br0 mtu=9000 name=VL1480 vlan-id=1480
/routing bgp instance
add as=7546 disabled=no name=default routing-table=main
/routing ospf instance
add disabled=no name=ospf-instance-1
/routing ospf area
add disabled=no instance=ospf-instance-1 name=ospf-area-1
/interface bridge port
add bridge=br0 edge=yes frame-types=admit-only-vlan-tagged interface=\
    sfp-sfpplus1
add bridge=br0 edge=yes frame-types=admit-only-vlan-tagged interface=\
    sfp-sfpplus2
add bridge=br0 interface=sfp-sfpplus15
/interface ethernet switch l3hw-settings
set autorestart=yes ipv6-hw=yes
/interface bridge vlan
add bridge=br0 tagged=br0,sfp-sfpplus1 vlan-ids=1480
add bridge=br0 tagged=br0,sfp-sfpplus1 vlan-ids=4
add bridge=br0 tagged=sfp-sfpplus15 vlan-ids=1481
add bridge=br0 tagged=sfp-sfpplus15 vlan-ids=2220
/interface ethernet switch
set switch1 l3-hw-offloading=yes qos-hw-offloading=yes
/interface vxlan vteps
add interface=vxlan1481 remote-ip=10.14.80.101
add interface=vxlan2220 remote-ip=10.14.80.101
/ip address
add address=10.14.80.51/24 interface=VL1480 network=10.14.80.0
add address=100.127.4.222/24 interface=VL4 network=100.127.4.0
/ip route
add dst-address=0.0.0.0/0 gateway=10.14.80.11
/routing bgp connection
add as=7546 connect=yes disabled=no instance=default listen=yes local.address=\
    100.127.4.222 .role=ibgp name=rr-maurice-4 remote.address=100.127.2.10/32 \
    .as=7546 routing-table=main
/routing filter rule
add chain=ospf-l3hw-filter disabled=no rule="if (dst == 0.0.0.0/0) { accept; }"
add chain=ospf-l3hw-filter disabled=no rule="if (dst-len == 24) { accept; }"
add chain=ospf-l3hw-filter disabled=no rule="if (dst-len == 30) { accept; }"
add chain=ospf-l3hw-filter disabled=no rule="reject;"
/routing ospf interface-template
add area=ospf-area-1 disabled=no networks=100.127.2.0/24 priority=0
add area=ospf-area-1 disabled=no networks=100.127.4.0/24 priority=0
/system identity
set name=Maurice-VXLAN
/system routerboard settings
set auto-upgrade=yes enter-setup-on=delete-key
[admin@Maurice-VXLAN] >