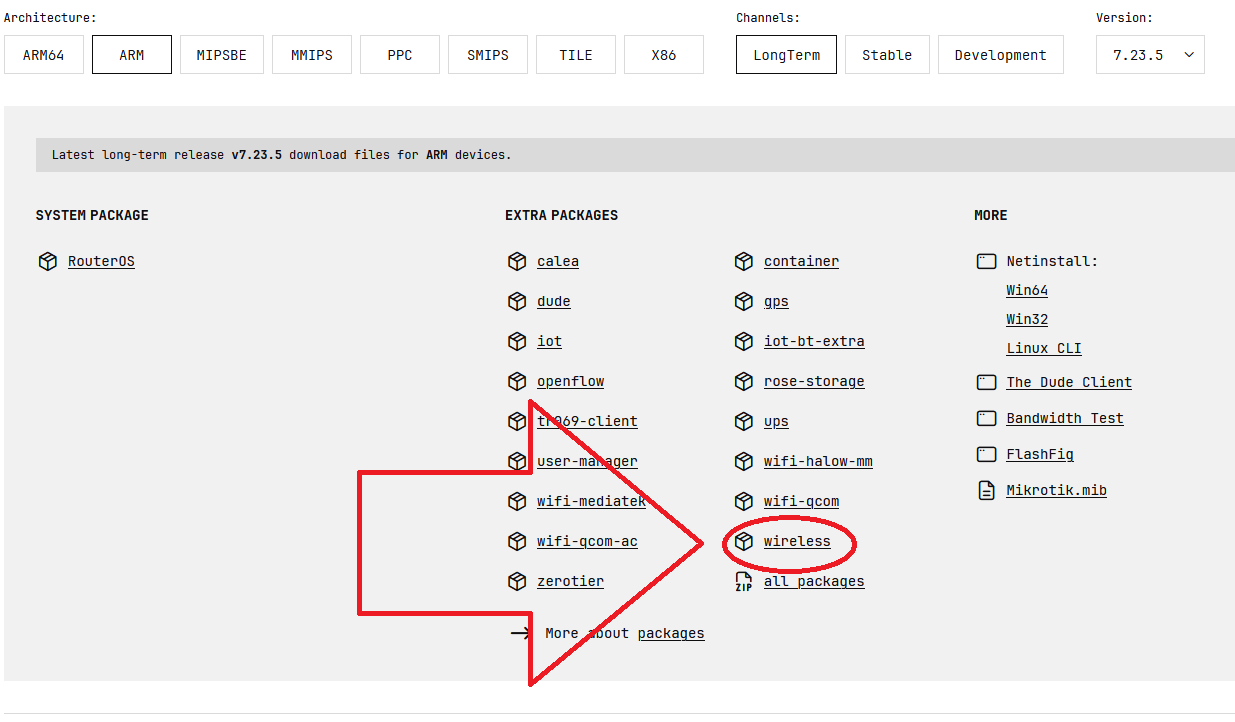
I still can't provide my config. Its about 80000 line but 32... are only allowed.
# 2026-09-04 17:09:29 by RouterOS 7.23.5
# software id = UCYE-VK1K
#
# model = RB3011UiAS
# serial number = E7E60FD836A5
/interface bridge
add admin-mac=DC:2C:6E:9A:55:0D auto-mac=no comment=defconf name=bridge \
    port-cost-mode=short
add name=bridge-vlan vlan-filtering=yes
/interface ethernet
set [ find default-name=ether10 ] disabled=yes name=DMZ
set [ find default-name=ether1 ] mtu=1504 name=Stadtwerke
/interface vxlan
add dont-fragment=disabled mac-address=92:9A:FF:D2:E6:E8 name=vxlan1 vni=1
/interface list
add comment=defconf name=WAN
add comment=defconf name=LAN
/interface lte apn
set [ find default=yes ] ip-type=ipv4 use-network-apn=no
/interface wireless security-profiles
set [ find default=yes ] supplicant-identity=MikroTik
/ip smb users
set [ find default=yes ] disabled=yes
/system logging action
add disk-file-name=logg name=logfiless target=disk
/interface bridge port
add bridge=bridge comment=defconf ingress-filtering=no interface=ether2 \
    internal-path-cost=10 path-cost=10
add bridge=bridge comment=defconf ingress-filtering=no interface=ether3 \
    internal-path-cost=10 path-cost=10
add bridge=bridge comment=defconf ingress-filtering=no interface=ether4 \
    internal-path-cost=10 path-cost=10
add bridge=bridge comment=defconf ingress-filtering=no interface=ether5 \
    internal-path-cost=10 path-cost=10
add bridge=bridge comment=defconf ingress-filtering=no interface=ether6 \
    internal-path-cost=10 path-cost=10
add bridge=bridge comment=defconf ingress-filtering=no interface=ether7 \
    internal-path-cost=10 path-cost=10
add bridge=bridge comment=defconf ingress-filtering=no interface=ether8 \
    internal-path-cost=10 path-cost=10
add bridge=bridge comment=defconf ingress-filtering=no interface=ether9 \
    internal-path-cost=10 path-cost=10
add bridge=bridge comment=defconf disabled=yes ingress-filtering=no \
    interface=DMZ internal-path-cost=10 path-cost=10
add bridge=bridge comment=defconf ingress-filtering=no interface=sfp1 \
    internal-path-cost=10 path-cost=10
/ip firewall connection tracking
set udp-timeout=10s
/ip neighbor discovery-settings
set discover-interface-list=LAN
/ip settings
set max-neighbor-entries=8192
/ipv6 settings
set disable-ipv6=yes max-neighbor-entries=8192 soft-max-neighbor-entries=8191
/interface detect-internet
set internet-interface-list=WAN wan-interface-list=WAN
/interface list member
add comment=defconf interface=bridge list=LAN
add comment=defconf interface=Stadtwerke list=WAN
/interface ovpn-server server
add auth=sha1,md5 mac-address=FE:6B:20:D3:81:6C name=ovpn-server1
/ip address
add address=192.168.0.253/24 comment=defconf interface=bridge network=\
    192.168.0.0
add address=91.136.133.54/24 interface=Stadtwerke network=91.136.133.0
/ip dhcp-client
add comment=defconf disabled=yes interface=Stadtwerke name=client1
/ip dhcp-server
add address-pool=*1 disabled=yes interface=bridge lease-time=10m name=defconf
/ip dns
set allow-remote-requests=yes servers=9.9.9.9,1.1.1.1,192.168.0.78
/ip dns static
add address=192.168.0.253 comment=defconf name=router.lan type=A
/ip firewall filter
add action=accept chain=forward out-interface=Stadtwerke src-address=\
    192.168.0.253
add action=drop chain=input comment="Adresslist Blacklists" in-interface=\
    Stadtwerke log-prefix=Blacklist___ protocol=tcp src-address-list=\
    black-list
add action=drop chain=input comment="Adresslist Blacklists" in-interface=\
    Stadtwerke log-prefix=Blacklist___ protocol=tcp src-address-list=\
    blacklist
add action=drop chain=input comment="Adresslist Blacklists" in-interface=\
    Stadtwerke log-prefix=Blacklist___ protocol=tcp src-address-list=\
    digitalocean
add action=accept chain=input comment=\
    "accept established and related from the router itself" connection-state=\
    established,related in-interface=!Stadtwerke
add action=accept chain=input comment=\
    "defconf: accept to local loopback (for CAPsMAN)" dst-address=127.0.0.1
add action=drop chain=input comment="drop icmp" disabled=yes protocol=icmp
add action=drop chain=input in-interface=Stadtwerke src-address-list=\
    Hurricane
add action=drop chain=input in-interface=Stadtwerke protocol=tcp \
    src-address-list=OHV
add action=drop chain=input in-interface=Stadtwerke protocol=tcp \
    src-address-list=M247
add action=drop chain=input in-interface=Stadtwerke protocol=tcp \
    src-address-list=leaseweb
add action=drop chain=input in-interface=Stadtwerke protocol=tcp \
    src-address-list=Linode
add action=drop chain=input disabled=yes in-interface=Stadtwerke protocol=tcp \
    src-address-list=CountryIPBlocks
add action=drop chain=input comment="defconf: drop invalid" connection-state=\
    invalid
add action=drop chain=input comment="anti Ping Flood" in-interface=Stadtwerke \
    limit=2,2:packet protocol=icmp
add action=drop chain=input comment="defconf: drop all not coming from LAN" \
    in-interface-list=!LAN log-prefix=!LAN_
add action=fasttrack-connection chain=forward comment="defconf: fasttrack" \
    connection-state=established,related
add action=accept chain=forward comment="defconf: accept in ipsec policy" \
    ipsec-policy=in,ipsec
add action=accept chain=forward comment="defconf: accept out ipsec policy" \
    ipsec-policy=out,ipsec
add action=accept chain=forward comment="Alllowed Adresslist" in-interface=\
    Stadtwerke log=yes log-prefix=allowed_blacklist_foward_ src-address-list=\
    allowed_blacklist
add action=accept chain=forward comment=\
    "defconf: accept established,related, untracked" connection-state=\
    established,related
add action=drop chain=forward comment="Adresslist Blacklist" in-interface=\
    Stadtwerke log-prefix=Blacklist___forward protocol=tcp src-address-list=\
    black-list
add action=drop chain=forward comment="Adresslist Blacklist" in-interface=\
    Stadtwerke log-prefix=Blacklist___forward protocol=tcp src-address-list=\
    blacklist
add action=drop chain=forward comment="Adresslist Blacklist" in-interface=\
    Stadtwerke log-prefix=Blacklist___forward protocol=tcp src-address-list=\
    digitalocean
add action=drop chain=forward in-interface=Stadtwerke protocol=tcp \
    src-address-list=Linode
add action=drop chain=forward in-interface=Stadtwerke protocol=tcp \
    src-address-list=leaseweb
add action=drop chain=forward disabled=yes in-interface=Stadtwerke protocol=\
    tcp src-address-list=M247
add action=drop chain=forward comment=CountryBlocks in-interface=Stadtwerke \
    log-prefix=Country_FORWARD_ src-address-list=CountryIPBlocks
add action=drop chain=forward comment="defconf: drop invalid" \
    connection-state=invalid
add action=drop chain=forward disabled=yes dst-address=192.168.0.78 \
    in-interface=Stadtwerke
add action=accept chain=forward comment="Proxy 113" disabled=yes log=yes \
    protocol=tcp src-address=192.168.0.113
add action=drop chain=forward comment="Windows 7 (118)" log-prefix=113_gen_ \
    src-address=192.168.0.118
add action=drop chain=forward comment=\
    "Drop all traffic from this virtual machine Win10 (114)" log-prefix=114_ \
    src-address=192.168.0.114
add action=drop chain=forward comment=\
    "Drop all traffic from this virtual machine Win10 (116)" \
    dst-address-list=!windows_update log-prefix=116_WInUpdate_ src-address=\
    192.168.0.116
add action=drop chain=forward comment=\
    "Drop all traffic from this virtual machine (113)" log-prefix=\
    116_WInUpdate_ src-address=192.168.0.113
add action=drop chain=forward comment=\
    "Drop all traffic from virtual machine (94)" src-address=192.168.0.94
add action=drop chain=forward comment=XP src-address=192.168.0.11
add action=drop chain=forward comment=saveDB dst-address-list=!windows_update \
    log=yes log-prefix=64_ src-address=192.168.0.64
add action=accept chain=output comment="UDP Connect towards ptbtime1.ptb.de" \
    dst-address-list="NTP List" dst-port=123 log-prefix=\
    "UDP Out to ptbtime1.ptb.de" protocol=udp
add action=drop chain=output comment="WIN98 VM" dst-address-list=\
    windows_update src-address=192.168.0.111
add action=drop chain=output comment=Emotet dst-port=449 log=yes log-prefix=\
    Emotet_ protocol=tcp
add action=accept chain=output comment="DNS TCP" disabled=yes dst-port=53 \
    protocol=tcp
add action=accept chain=output comment="DNS UDP" disabled=yes dst-port=53 \
    protocol=udp
add action=accept chain=output comment="Router Output" disabled=yes protocol=\
    tcp src-address=192.168.0.253
add action=accept chain=output comment="Router Output" disabled=yes protocol=\
    icmp src-address=192.168.0.253
add action=passthrough chain=forward disabled=yes
/ip firewall nat
add action=masquerade chain=srcnat comment="defconf: masquerade" \
    ipsec-policy=out,none out-interface=Stadtwerke packet-mark=""
add action=dst-nat chain=dstnat comment="Dovecot access on server" dst-port=\
    993 in-interface=Stadtwerke log=yes log-prefix=993_ protocol=tcp \
    to-addresses=192.168.0.78 to-ports=993
add action=dst-nat chain=dstnat comment="smtps on mailserver" dst-port=587 \
    in-interface=Stadtwerke log=yes log-prefix=587_ protocol=tcp \
    to-addresses=192.168.0.78
add action=dst-nat chain=dstnat comment="stmp port on muskatnuss" dst-port=25 \
    in-interface=Stadtwerke log=yes log-prefix=25_ protocol=tcp to-addresses=\
    192.168.0.78 to-ports=25
add action=dst-nat chain=dstnat comment="letsencrypt update" dst-port=80 \
    in-interface=Stadtwerke log=yes log-prefix=NAT_80_ protocol=tcp \
    to-addresses=192.168.0.78 to-ports=80
add action=dst-nat chain=dstnat comment="https webserver " dst-port=443 \
    in-interface=Stadtwerke log=yes log-prefix=HTTPS_ protocol=tcp src-port=\
    "" to-addresses=192.168.0.78 to-ports=443
add action=dst-nat chain=dstnat comment="HG1500 UDP SIP Traffic" disabled=yes \
    dst-port=5060 in-interface=Stadtwerke protocol=udp to-addresses=\
    192.168.0.79 to-ports=5060
add action=dst-nat chain=dstnat comment="SSH Port" dst-port=18729 \
    in-interface=Stadtwerke log=yes protocol=tcp to-addresses=192.168.0.78 \
    to-ports=22
add action=dst-nat chain=dstnat disabled=yes protocol=udp to-addresses=\
    192.168.10.1 to-ports=14856
add action=src-nat chain=srcnat disabled=yes in-interface=Stadtwerke \
    protocol=tcp to-addresses=0.0.0.0
add action=accept chain=dstnat disabled=yes dst-port=18730 log=yes \
    log-prefix=Wiregurd_ protocol=udp
/ip firewall raw
add action=accept chain=prerouting disabled=yes dst-address-list=\
    allowed_blacklist
add action=drop chain=prerouting disabled=yes dst-address=192.168.0.78 \
    dst-port=80 protocol=tcp
add action=drop chain=prerouting disabled=yes src-address-list=\
    CountryIPBlocks
/ip ipsec profile
set [ find default=yes ] dpd-interval=2m dpd-maximum-failures=5
/ip route
add disabled=no dst-address=0.0.0.0/0 gateway=91.136.133.53
/ip service
set www disabled=yes
set www-ssl certificate=Webfig
/ipv6 address
add address=::ffff:192.168.0.253 interface=ether2
/ipv6 firewall address-list
add address=::/128 comment="defconf: unspecified address" list=bad_ipv6
add address=::1/128 comment="defconf: lo" list=bad_ipv6
add address=fec0::/10 comment="defconf: site-local" list=bad_ipv6
add address=::ffff:0.0.0.0/96 comment="defconf: ipv4-mapped" list=bad_ipv6
add address=::/96 comment="defconf: ipv4 compat" list=bad_ipv6
add address=100::/64 comment="defconf: discard only " list=bad_ipv6
add address=2001:db8::/32 comment="defconf: documentation" list=bad_ipv6
add address=2001:10::/28 comment="defconf: ORCHID" list=bad_ipv6
add address=3ffe::/16 comment="defconf: 6bone" list=bad_ipv6
/ipv6 firewall filter
add action=accept chain=input comment=\
    "defconf: accept established,related,untracked" connection-state=\
    established,related,untracked
add action=drop chain=input comment="defconf: drop invalid" connection-state=\
    invalid
add action=accept chain=input comment="defconf: accept UDP traceroute" \
    dst-port=33434-33534 protocol=udp
add action=accept chain=input comment=\
    "defconf: accept DHCPv6-Client prefix delegation." dst-port=546 protocol=\
    udp src-address=fe80::/10
add action=accept chain=input comment="defconf: accept IKE" dst-port=500,4500 \
    protocol=udp
add action=accept chain=input comment="defconf: accept ipsec AH" protocol=\
    ipsec-ah
add action=accept chain=input comment="defconf: accept ipsec ESP" protocol=\
    ipsec-esp
add action=accept chain=input comment=\
    "defconf: accept all that matches ipsec policy" ipsec-policy=in,ipsec
add action=drop chain=input comment=\
    "defconf: drop everything else not coming from LAN" in-interface-list=\
    !LAN
add action=accept chain=forward comment=\
    "defconf: accept established,related,untracked" connection-state=\
    established,related,untracked
add action=drop chain=forward comment="defconf: drop invalid" \
    connection-state=invalid
add action=drop chain=forward comment=\
    "defconf: drop packets with bad src ipv6" src-address-list=bad_ipv6
add action=drop chain=forward comment=\
    "defconf: drop packets with bad dst ipv6" dst-address-list=bad_ipv6
add action=drop chain=forward comment="defconf: rfc4890 drop hop-limit=1" \
    hop-limit=equal:1 protocol=icmpv6
add action=accept chain=forward comment="defconf: accept ICMPv6" protocol=\
    icmpv6
add action=accept chain=forward comment="defconf: accept HIP" protocol=139
add action=accept chain=forward comment="defconf: accept IKE" dst-port=\
    500,4500 protocol=udp
add action=accept chain=forward comment="defconf: accept ipsec AH" protocol=\
    ipsec-ah
add action=accept chain=forward comment="defconf: accept ipsec ESP" protocol=\
    ipsec-esp
add action=accept chain=forward comment=\
    "defconf: accept all that matches ipsec policy" ipsec-policy=in,ipsec
add action=drop chain=forward comment=\
    "defconf: drop everything else not coming from LAN" in-interface-list=\
    !LAN
/ipv6 nd
# automatic dns option advertising is not started, re-apply dns config
set [ find default=yes ] advertise-dns=yes
/lcd
set backlight-timeout=15m default-screen=stats-all
/routing bfd configuration
add disabled=no
/system clock
set time-zone-name=Europe/Berlin
/system identity
set name=gateway002
/system ntp client
set enabled=yes
/system ntp client servers
add address=192.53.103.108
add address=192.53.103.104
/system package update
set channel=long-term
/system routerboard reset-button
set enabled=yes
/system scheduler
add interval=5d1m30s name=Emailbackup on-event=backup policy=\
    ftp,reboot,read,write,policy,test,password,sniff,sensitive,romon \
    start-date=2022-02-26 start-time=05:46:00
add comment="2026-09-02 16:01:46" interval=1d30s name="Log gateway002" \
    on-event=droplog policy=\
    ftp,reboot,read,write,policy,test,password,sniff,sensitive,romon \
    start-date=2022-02-26 start-time=05:48:10
add interval=1d3m name=LogAlert on-event=LogAlert policy=\
    ftp,reboot,read,write,policy,test,password,sniff,sensitive,romon \
    start-date=2022-02-26 start-time=07:46:45
add disabled=yes interval=1d4m name="addres list RU" on-event="/tool fetch url\
    =http://www.iwik.org/ipcountry/mikrotik/RU\
    \n/import file-name=RU" policy=\
    ftp,reboot,read,write,policy,test,password,sniff,sensitive,romon \
    start-date=2022-02-26 start-time=07:47:15
add disabled=yes interval=1d4m30s name="adress list CN" on-event=\
    "http://www.iwik.org/ipcountry/mikrotik/CN\r\
    \n/import file-name=CN" policy=\
    ftp,reboot,read,write,policy,test,password,sniff,sensitive,romon \
    start-date=2022-02-26 start-time=07:48:03
add comment="2025-12-08 14:54:15" interval=1d1h name=droplog on-event=droplog \
    policy=ftp,reboot,read,write,policy,test,password,sniff,sensitive,romon \
    start-date=2022-02-26 start-time=10:50:30
add disabled=yes interval=1w23h55m name="ROUTERBAORD UPGRADE" on-event=":globa\
    l Var1\r\
    \n:global Var2\r\
    \n:set Var1 \"\$[/system package get system version]\"\r\
    \n:set Var2 \"\$[/system routerboard get current-firmware]\"\r\
    \n:if (\$Var1>\$Var2) do={/system routerboard upgrade; /system reboot;}" \
    policy=ftp,reboot,read,write,policy,test,password,sniff,sensitive,romon \
    start-date=2022-02-26 start-time=14:00:00
add disabled=yes interval=1w23h55m name="system package upgrade" on-event=\
    "system package/upgrade install" policy=\
    ftp,reboot,read,write,policy,test,password,sniff,sensitive,romon \
    start-date=2022-02-26 start-time=14:30:00
/tool e-mail
set certificate-verification=no from=gateway001@broesecke.eu port=587 server=\
    192.168.0.78 tls=starttls user=petereit
/tool mac-server
set allowed-interface-list=LAN
/tool mac-server mac-winbox
set allowed-interface-list=LAN
/tool traffic-monitor
add interface=Stadtwerke name=In_Stadtwerke threshold=10 traffic=received
add interface=bridge name=tmon1