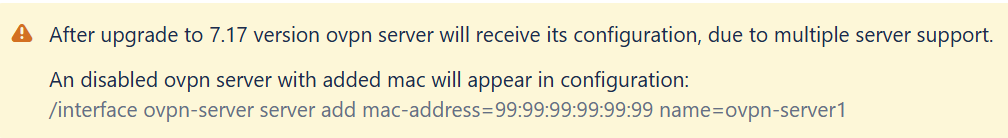
Round 1
• Q1: Who can tell me the purpose of this "disabled" configuration entry? (Why was it created?)
• Q2: What specific part of this entry indicates that the server is disabled?
• Q3: Why does this entry not appear in the Winbox UI or when running the /interface/print command?
Round 2 Q1: How can we be sure there are no other hidden 'server' or 'client' entries missing from the UI, print command, or configuration export?
Q2: To thoroughly check the router's configuration, the responsible administrator should use:
• A) The Winbox UI
• B) The /"what_you_want"/printcommand
• C) A line-by-line reading of the full configuration export
• D) None of the above— Nah!!! | I`m | ROS is | (underline your selection) always right and don`t need it at all!
Q3: What happens if you delete this entry from the configuration?
• A) Nothing will change.
• B) The entry will reappear after a device reboot or a ROS upgrade. • C) Everything will break.
R1 Q1: You want a copy-paste of the image, or you are not able to read one image?
R1 Q2: The missing disabled=no
R1 Q3: Interface? What interface? Is on PPP OVPN server.
R2 Q1: In the same way that you are sure it isn't raining meatballs.
R2 Q2: C + daily "diff" or better R2-D2 + C-3PO
R2 Q3: None of the above but: The entry is removed.
Yes, you are right.
I should have dug deeper, but I was hoping in vain for logic in the ROS hierarchy—it's not guaranteed that you will get information about objects one level lower at a higher level.
And the missing information about the server is more of a rhetorical question about the 'logic' behind the hierarchy's implementation—meaning, a question for MT.
BTW - I have this entry only on the E50UG, and none on the few hAP ax2 devices with the same ROS version.
Where or when?
In the next ROS version? say v7.23.7 ?
And if the record is deleted, then the answer to the question of its purpose is completely clear — it had no purpose, and there was no point in creating it.
@rextended
I know, but It Is too funny (to me) the double negation in disabled=no, particularly when - due to being default yes It Is missing, I.e. It has a status of missing-in-export=yes (as opposed to present-in-export=no )
Well, just as you didn't understand the image,
you didn't understand the answer either.
You just need to reread what I wrote, not reading into it whatever you feel like,
but exactly what I actually wrote.
I never mentioned other versions of RouterOS,
if I state that none of the three proposed answers is correct,
but rather that the entry gets removed (from the configuration),
how could you possibly think I’m talking about a different version of RouterOS?
If this is a joke, it’s stupid,
if it’s not a joke, is why you failing to understand what is written in the image,
you’re just reading whatever you want into it
Of course, I don't understand the image as deeply as you do.
Not everyone here is a Сelestiale being; there are also people like me who just want to figure it out and understand 'why?'.
.. and I've reread what you actually wrote...
Regarding
Let's look at the logic: if this entry did not exist before version 7.17, then it must have been introduced in the v7.17 update code, just as the documentation states.
This means the entry was created by RouterOS update v7.17.
When you say 'The entry is removed.' and immediately deny that it was done by RouterOS update, then tell me: do you know how it was removed?
It could only have been done either by RouterOS update or manually by the administrator.
So does the RouterOS version really have nothing to do with it??
And I repeat: why is it that, despite running identical RouterOS versions, some devices (E50UG) have it while others (hAP ax2) do not?
It doesn't take a celestial mind to realize you're making things up.
The answer to your question is more than obvious.
You wrote "if you delete this entry from the configuration",
so you didn't mention on question updates or anything else.
It isn't that I have a celestial mind; rather, yours is confused.
Usually, when you delete something, It stays deleted.
There may be exceptions, of course, but this particular one seems not one of them.
So the original quiz missed the simplest option:
?) It stays deleted
The:
A) Nothing will change
Is partially accurate, as having something disabled or having It deleted should change nothing.
The decision by the good Mikrotik guys to add a disabled setting Is anyway queer, they may have their reasons, but they are not apparent.
In a perfect (or only slightly better ) world a setting wouldn't have a disabled=yes|no setting that Is shown sometimes and sometimes not depending on It being default or having been changed once before from default (sometimes) but rather a clear way, such as REM, #, // or similar, prepended to the setting line, like in any other scripting language, but of course It Is too late for RouterOS.
The newly created entry inherits its settings (if any) from single OVPN server config from older versions. It could be argued that if there were no changes to it then entry should not be created though as there is nothing to preserve.
@rextended The point of the questions is to show that for unexplained reasons, when updating Roteros, configuration entries may appear that cannot be explained in any way.
Moreover, developers subsequently forget about them and it remains as "garbage" in the configuration.
The first question was: What is the purpose of this entity?
You didn't answer it.
And you answered the question about deleting the record by trolling - the entity is deleted. It's like answering the question: why clouds move? - because they change their position.
And one more question - has anyone tried to calculate how many resources are spent on converting "Disabled=yes" from configuration to "Enabled=no" in the Winbox user interface?
Especially because my answer is crystal clear: None of the three suggested answers is correct.
The actual answer, however, is precise...
What happens if I delete it? IT STAYS DELETED.
Where is that option among the ones proposed?
And the answer "Nothing will change" is completely wrong, not just partially.
To me, "Nothing" means "Nothing"
If it no longer appears in the export after deletion, then to me that is something, not "Nothing".
It is one thing not to be able to explain it,
but quite another not to grasp it.
Other users in this thread have already told you the reason,
not to mention the fact that it is still stated in the guide you took a screenshot yourself...
It's a good thing I'm not the only "Сelestiale being" here...
At first (until 7.16.x) it was only possible to have one,
then they introduced the option on 7.17 to have more than one,
so the existing one (even if unused) is created anew, exactly as it was, as the first entry in the new multiple-entry database.
The way it was handled is correct: it avoids any issues regarding judging whether or not it was actually being used.
Unfortunately, there are people who don't understand and accuse others of trolling.
Throughout history, there has always been a witch hunt whenever someone fails to grasp the situation.
Then again, the first rule is not to feed the troll... And here I am, making the mistake of doing just that.