Router with few VLANs - help needed #2

Hi guys,

I opened separate topic because this time I wish to fix thruput issues on my Hex (2025) router.
Configuration is like below, I know VLAN1 should be removed and will be very soon but must be there for few more days.
All the VLAN’s: 99,100,110,120 are build to replace VLAN1 and VLAN88.

Problem: computer wired connected on VLAN99 is able to generate max ~500Mbit/s download speed instead of 1Gb/s which should be available.

Goal: implement successfully FastTrack rules.

I’ve read Mikrotik manual, googled for some solutions and I’m stuck a bit.
I’ve found also this webpage https://itorakul.com.ua/en/setting-up-fasttrack-connection-on-mikrotik/
Author from ^^^ link recommends to implement rules like below:

/ip firewall filter
add action=accept chain=forward ipsec-policy=in,ipsec
add action=accept chain=forward ipsec-policy=out,ipsec
add action=fasttrack-connection chain=forward connection-state=established,related in-interface=bridge out-interface=WAN
add action=fasttrack-connection chain=forward connection-state=established,related in-interface=WAN out-interface=bridge
add chain=forward action=accept connection-state=established,related
add chain=forward action=drop connection-state=invalid

While Mikrotik in the doc Connection tracking - RouterOS - MikroTik Documentation saing:
FastPath and Route cache is enabled under IP/Settings while later While FastPath and FastTrack both are enabled on the device only one can be active at a time.
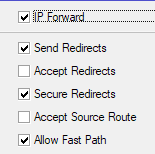
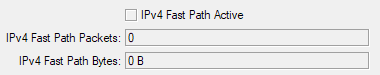
I do have FastPath under IP>Settings, there is no Route cache option, however there are IPv4 Fast Patch option not enabled. Should I change anything here as well?
Can I safety implement Fasttrack rule remotely?
I know that my Firewall rules needs to be adjusted. Hope you will help me do that too. I count on you!
RouterOS 7.20.6

model = E60iUGS

/interface bridge
add admin-mac=D4:01:C3:64:94:BB auto-mac=no name=bridge vlan-filtering=yes
/interface ethernet
set [ find default-name=ether3 ] name=CCTV
set [ find default-name=ether2 ] name=OffBridgeMGMT
set [ find default-name=ether4 ] name=PPoE
set [ find default-name=ether5 ] name=Trunk
set [ find default-name=ether1 ] name=WAN
/interface vlan
add comment=ADA_VLAN interface=bridge name=ADA_VLAN vlan-id=120
add comment=MGMT_VLAN interface=bridge name=MGMT_VLAN vlan-id=99
add comment=WiFi2_VLAN interface=bridge name=WiFi2_VLAN vlan-id=110
add comment=WiFi_VLAN interface=bridge name=WiFi_VLAN vlan-id=100
add comment="CCTV vlan" interface=bridge name=vlan1 vlan-id=1
add comment="PPoE vlan" interface=bridge name=vlan88 vlan-id=88
/interface list
add name=MGMT
add include=none name=VLAN
/ip ipsec policy group
add name=vpn
/ip ipsec profile
add dh-group=modp1024 enc-algorithm=aes-256 hash-algorithm=sha256 name=vpn
/ip ipsec peer
add exchange-mode=ike2 name=vpn passive=yes profile=vpn
/ip ipsec proposal
add enc-algorithms=aes-256-cbc name=vpn pfs-group=none
/ip pool
add name=dhcp_CCTV ranges=192.168.0.10-192.168.0.254
add name=dhcp_PPoE ranges=192.168.88.10-192.168.88.254
add name=vpn ranges=10.22.22.10-10.22.22.20
add name=ADA_POOL ranges=192.168.120.100-192.168.120.254
add name=WiFi2_POOL ranges=192.168.110.100-192.168.110.254
add name=WiFi_POOL ranges=192.168.100.100-192.168.100.254
add name=MGMT_POOL ranges=192.168.99.100-192.168.99.254
/ip dhcp-server
add address-pool=dhcp_CCTV disabled=yes interface=vlan1 lease-time=1d name=
dhcp_CCTV
add address-pool=dhcp_PPoE disabled=yes interface=vlan88 lease-time=1d name=
dhcp_PPoE
add address-pool=WiFi_POOL interface=WiFi_VLAN lease-time=6h name=WiFi_DHCP
add address-pool=ADA_POOL interface=ADA_VLAN lease-time=6h name=ADA_DHCP
add address-pool=WiFi2_POOL interface=WiFi2_VLAN lease-time=6h name=
WiFi2_DHCP
add address-pool=MGMT_POOL interface=MGMT_VLAN lease-time=6h name=MGMT_DHCP
/ip ipsec mode-config
add address-pool=vpn name=vpn
/ppp profile
set *0 use-encryption=no
add change-tcp-mss=yes local-address=192.168.88.1 name=5Mbps rate-limit=1M/5M 
remote-address=dhcp_PPoE
add change-tcp-mss=yes local-address=192.168.88.1 name=30Mbps rate-limit=
5.1M/35M remote-address=dhcp_PPoE
add change-tcp-mss=yes local-address=192.168.88.1 name=15Mbps rate-limit=
2M/15M remote-address=dhcp_PPoE
add change-tcp-mss=yes local-address=192.168.88.1 name=10Mbps rate-limit=
2M/10M remote-address=dhcp_PPoE
add change-tcp-mss=yes local-address=192.168.88.1 name=20Mbps rate-limit=
5M/20M remote-address=dhcp_PPoE
add change-tcp-mss=yes local-address=192.168.88.1 name=Unlimited 
remote-address=dhcp_PPoE session-timeout=0s
add change-tcp-mss=yes local-address=192.168.88.1 name=60Mbps rate-limit=
10M/60M remote-address=dhcp_PPoE
set *FFFFFFFE use-encryption=no
/interface bridge port
add bridge=bridge comment=CCTV interface=CCTV
add bridge=bridge comment=PPoE interface=PPoE pvid=88
add bridge=bridge comment=Trunk ingress-filtering=no interface=Trunk
/ip neighbor discovery-settings
set discover-interface-list=MGMT
/ip settings
set rp-filter=strict
/interface bridge vlan
add bridge=bridge comment="CCTV VLAN" tagged=Trunk,bridge untagged=CCTV 
vlan-ids=1
add bridge=bridge comment="PPoE VLAN" tagged=Trunk,bridge untagged=PPoE 
vlan-ids=88
add bridge=bridge comment=WiFi_VLAN tagged=bridge,Trunk vlan-ids=100
add bridge=bridge comment=WiFi2_VLAN tagged=Trunk,bridge vlan-ids=110
add bridge=bridge comment=ADA_VLAN tagged=Trunk,bridge vlan-ids=120
add bridge=bridge comment=MGMT tagged=Trunk,bridge vlan-ids=99
/interface list member
add interface=vlan1 list=MGMT
add interface=OffBridgeMGMT list=MGMT
add interface=MGMT_VLAN list=MGMT
add interface=ADA_VLAN list=MGMT
add interface=ADA_VLAN list=VLAN
add interface=MGMT_VLAN list=VLAN
add interface=WiFi2_VLAN list=VLAN
add interface=WiFi_VLAN list=VLAN
/interface pppoe-server server
add default-profile=30Mbps disabled=no interface=vlan88 max-mru=1480 max-mtu=
1480 service-name=PPoE_server
/ip address
add address=192.168.77.1/24 interface=OffBridgeMGMT network=192.168.77.0
add address=192.168.0.1/24 comment=CCTV interface=vlan1 network=192.168.0.0
add address=192.168.88.1/24 comment=PPoE interface=vlan88 network=
192.168.88.0
add address=192.168.188.222 comment="WAN Gateway" interface=WAN network=
192.168.188.1
add address=x.x.x.x/30 comment="WAN Gateway" interface=WAN network=
x.x.x.x
add address=192.168.110.1/24 interface=WiFi2_VLAN network=192.168.110.0
add address=192.168.120.1/24 interface=ADA_VLAN network=192.168.120.0
add address=192.168.100.1/24 interface=WiFi_VLAN network=192.168.100.0
add address=192.168.99.1/24 interface=MGMT_VLAN network=192.168.99.0
/ip dhcp-server network
add address=192.168.0.0/24 dns-server=8.8.8.8,8.8.4.4 gateway=192.168.0.1
add address=192.168.88.0/24 dns-server=8.8.8.8,8.8.4.4 gateway=192.168.88.1
add address=192.168.99.0/24 dns-server=8.8.8.8 gateway=192.168.99.1
add address=192.168.100.0/24 dns-server=8.8.8.8 gateway=192.168.100.1
add address=192.168.110.0/24 dns-server=8.8.8.8 gateway=192.168.110.1
add address=192.168.120.0/24 dns-server=8.8.8.8 gateway=192.168.120.1
/ip dns
set allow-remote-requests=yes servers=8.8.8.8,8.8.4.4
/ip firewall address-list
add address=xxxxxxx.ddns.net list=slv_ddns
/ip firewall filter
add action=drop chain=input comment="Drop Invalid connections" 
connection-state=invalid
add action=accept chain=input comment="Allow Established connections" 
connection-state=established,related
add action=accept chain=input comment="Allow VLAN to router services" 
in-interface-list=VLAN
add action=accept chain=input comment="Allow Base_Vlan Full Access" 
in-interface=MGMT_VLAN
add action=accept chain=input dst-port=8291 protocol=tcp src-address=
192.168.0.0/24
add action=accept chain=input dst-port=8291 in-interface=WAN protocol=tcp 
src-address-list=slv_ddns
add action=drop chain=input dst-port=8291 protocol=tcp
add action=accept chain=input comment=
"Allow access to router from known network" src-address=192.168.0.0/24
add action=accept chain=input comment="Allow IPSEC/IKE2 connections" 
dst-port=500,4500 log=yes protocol=udp
add action=drop chain=input comment="Drop anything else"
add action=accept chain=forward connection-state=new dst-address=
192.168.0.251 dst-port=443 protocol=tcp src-address-list=slv_ddns
add action=accept chain=forward comment=
"Allow already established connections" connection-state=
established,related
add action=accept chain=forward comment="VLAN Internet Access only" 
connection-state=new in-interface-list=VLAN out-interface=WAN
add action=accept chain=forward connection-nat-state=dstnat connection-state=
established,related in-interface=WAN
add action=drop chain=forward comment="Drop to bogon list" dst-address-list=
bogons
add action=drop chain=forward disabled=yes in-interface=WAN
add action=accept chain=forward out-interface=WAN
add action=accept chain=forward comment="Accept in ipsec policy" 
ipsec-policy=in,ipsec
add action=accept chain=forward comment="Accept out ipsec policy" 
ipsec-policy=out,ipsec
add action=drop chain=forward comment="Drop invalid connections" 
connection-state=invalid protocol=tcp
add action=drop chain=forward
/ip firewall nat
add action=masquerade chain=srcnat out-interface=WAN
add action=dst-nat chain=dstnat dst-port=8038 in-interface=WAN protocol=tcp 
to-addresses=192.168.0.251 to-ports=443
/ip ipsec identity
add auth-method=digital-signature certificate="Home server" comment=
"Home client1" generate-policy=port-strict match-by=certificate 
mode-config=vpn peer=vpn policy-template-group=vpn remote-certificate=
"Home client1"
/ip ipsec policy
add dst-address=0.0.0.0/0 group=vpn proposal=vpn src-address=0.0.0.0/0 
template=yes
/ip route
add distance=1 gateway=x.x.x.x
/ip service
set ftp disabled=yes
set ssh disabled=yes
set telnet disabled=yes
set www disabled=yes
set api disabled=yes
/ppp secret
add name=m05 profile=60Mbps service=pppoe
[....]

/system clock
set time-zone-name=Europe/Warsaw
/system identity
set name=Router
/system logging
add disabled=yes topics=pppoe
add disabled=yes topics=ipsec,!packet
/system note
set note=">>>> Authorized administrator only. Access to this device is monitor
ed <<<<"
/system ntp client
set enabled=yes
/system ntp client servers
add address=3.pl.pool.ntp.org
add address=0.pl.pool.ntp.org
/system package update
set channel=long-term
/tool bandwidth-server
set enabled=no
/tool graphing interface
add allow-address=192.168.0.0/24 interface=WAN
/tool graphing resource
add allow-address=192.168.0.0/24
/tool mac-server
set allowed-interface-list=MGMT
/tool mac-server mac-winbox
set allowed-interface-list=MGMT
/tool traffic-monitor
add interface=WAN name=tmon1

Hi guys

I know that this is not easy example, but there is a a lot of easy examples but here on forum some peoples are also looking for more advanced examples and it’s really hard to find such examples.

I gave here full router configuration, ready to clone for anyone.
Could you help me adjust it a bit to implement Fasttrack rules with one condition, the traffic from LAN could be IPsec traffic as well. This router is also providing VPN connectivity for remote users.

I hope that someone will help me here

Regards

SLawek

You are using VLANs, which means if you blindly apply those two fasttrack rules from that "guide", then fasttrack will have no effects (because your VLAN interfaces are not bridge), and you won't be able to reach Gbps routing throughput.

Use the rules from the default firewall configuration provided by MikroTik:

the relevant parts are:

/ip firewall filter
add chain=forward action=accept ipsec-policy=in,ipsec comment="defconf: accept in ipsec policy"
add chain=forward action=accept ipsec-policy=out,ipsec comment="defconf: accept out ipsec policy"
add chain=forward action=fasttrack-connection connection-state=established,related comment="defconf: fasttrack"
add chain=forward action=accept connection-state=established,related,untracked comment="defconf: accept established,related, untracked"
add chain=forward action=drop connection-state=invalid comment="defconf: drop invalid"

Those are the rules normally placed at the top of the forward chain, before any other specific blocking rules.

Your configuration does not use mangle mark-routing/mark-packet rules, so the fasttrack rule can stay as-is without problem. IPsec exceptions are already handled by the first two rules.

If you later use mangle marking rules, try to use mark-connection on the connections that need special handling by mangling, then you can add an additional condition connection-mark=no-mark to the fasttrack rule, and it will be skipped for all connections with connection mark. Connections requiring no mangling are still sped up. The alternative is to disable the fasttrack rule completely, which is less efficient.

You can keep the settings like this:

which is the default, and it will work. Route cache was in RouterOS 6 but has been removed in RouterOS 7.

This showing all zeros and not active:

image

is not an issue at all.

Hi guys

CGGXANNX based on your advice and my current config I’ve prepared summary. This is a part of my firewall config specific to Forward chain:

add action=accept chain=forward comment="Accept in ipsec policy" ipsec-policy=in,ipsec
add action=accept chain=forward comment="Accept out ipsec policy" ipsec-policy=out,ipsec
add chain=forward action=fasttrack-connection connection-state=established,related comment="defconf: fasttrack"
add action=accept chain=forward connection-state=new dst-address=192.168.0.251 dst-port=443 protocol=tcp src-address-list=slv_ddns
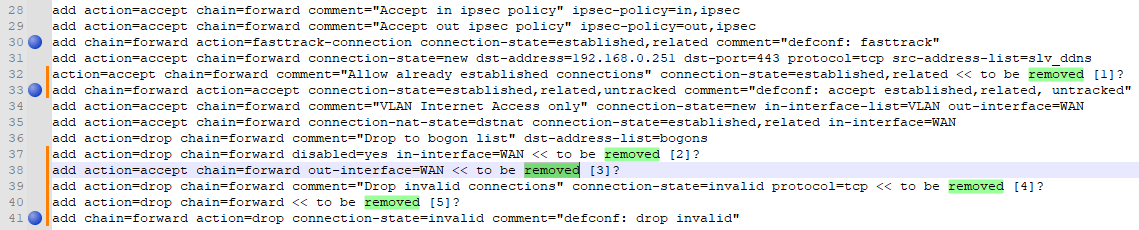
action=accept chain=forward comment="Allow already established connections" connection-state=established,related << to be removed [1]?
add chain=forward action=accept connection-state=established,related,untracked comment="defconf: accept established,related, untracked"
add action=accept chain=forward comment="VLAN Internet Access only" connection-state=new in-interface-list=VLAN out-interface=WAN
add action=accept chain=forward connection-nat-state=dstnat connection-state=established,related in-interface=WAN
add action=drop chain=forward comment="Drop to bogon list" dst-address-list=bogons
add action=drop chain=forward disabled=yes in-interface=WAN << to be removed [2]?
add action=accept chain=forward out-interface=WAN << to be removed [3]?
add action=drop chain=forward comment="Drop invalid connections" connection-state=invalid protocol=tcp << to be removed [4]?
add action=drop chain=forward << to be removed [5]?
add chain=forward action=drop connection-state=invalid comment="defconf: drop invalid"

Maybe for better visibility I'm attaching screenshot:

Rules with blue ball are added (exact copy from recommended example), those with “to be removed [x]” are problematic for me.
Those [1] and [2] are obvious to be removed, but I need your advice with [3], [4] and [5] and maybe others need to be adjusted. Could you help me here?

Regards
Slawek

Finally, It’s implemented and working. Almost perfectly :wink:

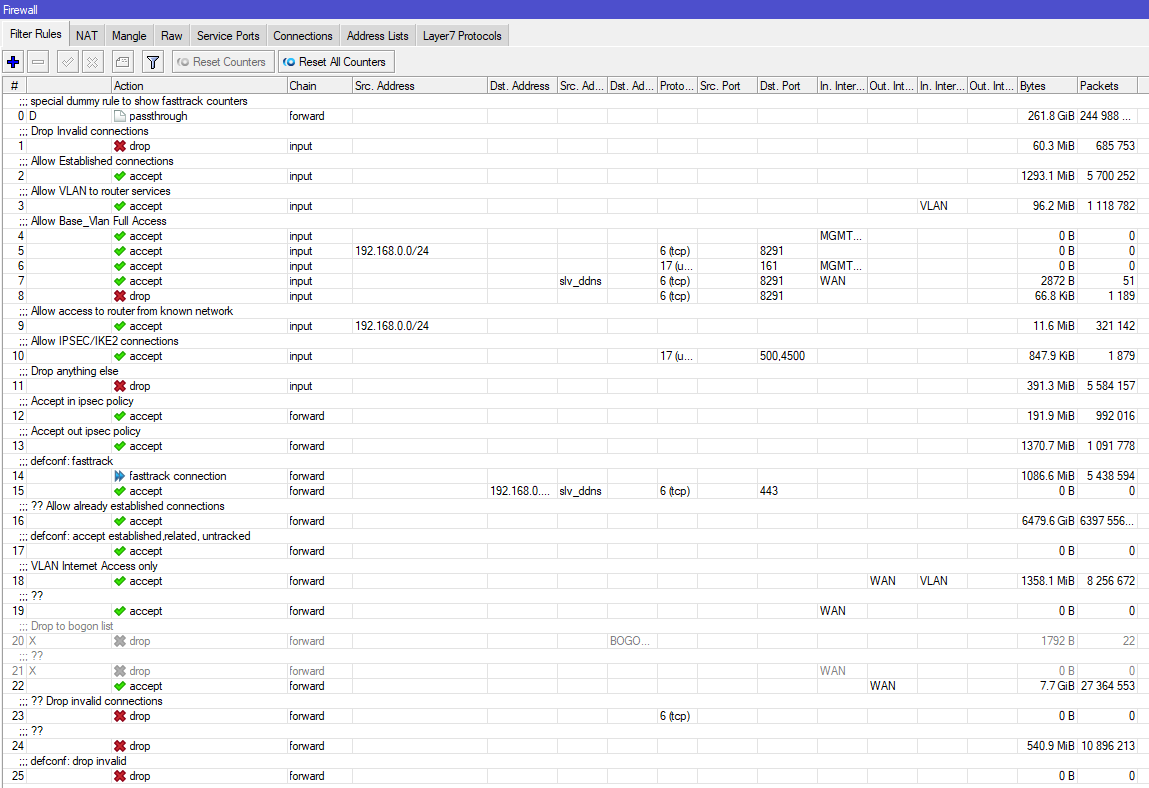
Yesterday, I turned on rules: 14, 17 and 25.

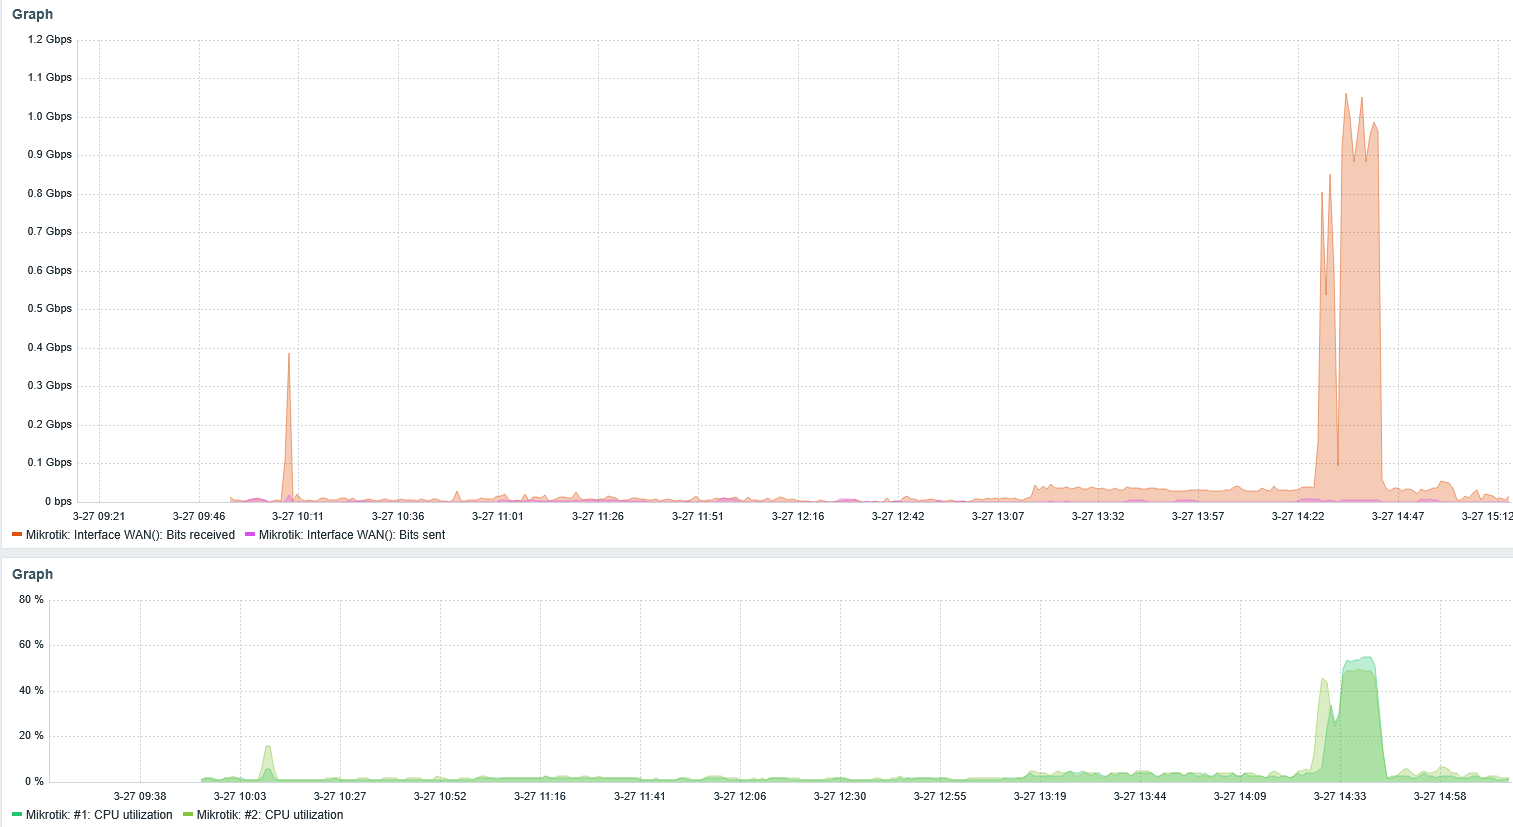
This is the situation after ~12h.
I still have doubs about rules 16, 21, 22, 23 and 24. Can I remove them safetly?
Should I change something in my rule set? any recommendation?

There is one annoing problem which started exactly once I did all the changes.
From laptop (W11) using build in VPN client I have trouble to estabilish c2s session. It’s hanging on “verification user logon”. I found workaround - just open winbox and connect to my router helps to estabilish VPN to the same router.
No idea how it’s connected with yday changes. Maybe you can help me with this problem too?

Here you can see the Hex S performance (just router with few VLANs, no PPPoE)


Regards
Slawek

Screenshots don't include enough settings of firewall filter rules to be sure whether some rules do anything or not. Post output of /ip/firewall/filter/print (run from CLI), that one is more or less complete with all properties.

Here you are:

[admin@Router] > /ip firewall/filter/print
Flags: X - disabled, I - invalid; D - dynamic
0 D ;;; special dummy rule to show fasttrack counters
chain=forward action=passthrough

1 ;;; Drop Invalid connections
chain=input action=drop connection-state=invalid

2 ;;; Allow Established connections
chain=input action=accept connection-state=established,related

3 ;;; Allow VLAN to router services
chain=input action=accept in-interface-list=VLAN

4 ;;; Allow Base_Vlan Full Access
chain=input action=accept in-interface=MGMT_VLAN

5 chain=input action=accept protocol=tcp src-address=192.168.0.0/24 dst-port=8291

6 ;;; access from VPN to the router
chain=input action=accept src-address=10.22.22.10-10.22.22.20 log=no log-prefix=""

7 chain=input action=accept protocol=udp in-interface=MGMT_VLAN dst-port=161 log=no log-prefix=""

8 chain=input action=accept protocol=tcp src-address-list=slv_ddns in-interface=WAN dst-port=8291 log=no log-prefix=""

9 chain=input action=drop protocol=tcp dst-port=8291

10 ;;; Allow access to router from known network
chain=input action=accept src-address=192.168.0.0/24

11 ;;; Allow IPSEC/IKE2 connections
chain=input action=accept protocol=udp dst-port=500,4500 log=yes log-prefix=""

12 ;;; Drop anything else
chain=input action=drop

13 ;;; Accept in ipsec policy
chain=forward action=accept ipsec-policy=in,ipsec

14 ;;; Accept out ipsec policy
chain=forward action=accept ipsec-policy=out,ipsec

15 ;;; defconf: fasttrack
chain=forward action=fasttrack-connection hw-offload=yes connection-state=established,related log=no log-prefix=""

16 chain=forward action=accept connection-state=new protocol=tcp dst-address=192.168.0.251 src-address-list=slv_ddns dst-port=443

17 ;;; ?? Allow already established connections
chain=forward action=accept connection-state=established,related log=no log-prefix=""

18 ;;; defconf: accept established,related, untracked
chain=forward action=accept connection-state=established,related,untracked log=no log-prefix=""

19 ;;; VLAN Internet Access only
chain=forward action=accept connection-state=new out-interface=WAN in-interface-list=VLAN

20 ;;; ??
chain=forward action=accept connection-state=established,related connection-nat-state=dstnat in-interface=WAN log=no log-prefix=""

21 X ;;; Drop to bogon list
chain=forward action=drop dst-address-list=BOGONS log=yes log-prefix="bogons"

22 X ;;; ??
chain=forward action=drop in-interface=WAN log=no log-prefix=""

23 chain=forward action=accept out-interface=WAN

24 ;;; ?? Drop invalid connections
chain=forward action=drop connection-state=invalid protocol=tcp log=no log-prefix=""

25 ;;; ??
chain=forward action=drop log=no log-prefix=""

26 ;;; defconf: drop invalid
chain=forward action=drop connection-state=invalid log=no log-prefix=""

[admin@Router] >

At first sight:

#17 looks like a subset of #18
#26 a subset of #25 (#26 will never be hit, after a "drop everything" rule)

  • As @jaclaz wrote, you can remove #17 and keep #18.

  • Current rule #16 should be moved below the "established,related,untracked" original rule #18 (and also after the "drop invalid" rule, see below).

    For the bulk of the traffic (the very large majority of the packets), the connection state would be established. When you download a 150KB JPG image for example, then usually only one packet has state new, while the other 100+ ones will have state established. You would want the packets in the established to be handled as soon as possible, skipping the other rules below immediately. Of course, fasttrack already helps in this case, but for the cases where fasttrack is not working or not enabled, you don't want to have rules that only act on packets with connection state new to be placed higher than the rule that accepts established in the chain.

  • The chain=forward action=drop connection-state=invalid rule should be placed right after that original #18 rule.

  • Once you've got the "accept established,related,untracked" and "drop invalid" rules at the correct positions (high in the chain, only behind fasttrack and the two special ipsec related rules), then all the other accept or drop rules below them no longer need connection-state=new and that condition can be removed from those rules.

    The possible values for connection-state are new, established, related, untracked, invalid, which means once you already have the 3 rules (including the fasttrack rule) that catch and handle established, related, untracked, invalid, the only possible connection state for the packets caught by other rules below them is new. It is thus totally redundant and unnecessary when you also specify connection-state=new on them. Any packets they can see already only have that connection state.

  • The original rule #20 is fully redundant (already handled by original #18) and should be removed too.

  • When you have the catch all rule (original #25) then you normally don't need the original rule #22 anymore, because no other rule between them explicitly accepts things coming from WAN.

    But you can still leave it there if you want, in case you might insert some accept rules in between and forget to handle incoming connections from WAN with those. With normal traffic (not under attack) only a small ratio of the packets has connection-state=new, so having a few unnecessary rules below the rules that handle established, related, untracked, invalid doesn't affect the performance too much.

  • If in the future for some reason you are not able to use fasttrack anymore (for example you want to use simple queues, or all traffics need mangle) then when you disable the fasttrack rule you should also move the two ipsec rules below the "accept established, related, untracked" rule to prioritize it as much as possible. Without fasttrack, the difference between having to only process 1 rule instead of 3 for most of the packets is very much noticeable.

    With fasttrack enabled and active, then you need those two rules above the fasttrack rule, because from your config, it looks like IPsec is in use.

First of all, THANK YOU CGGXANNX for your time, and such detailed explanation. Hope this will help not only me, but many peoples on this forum.
I read your post few times, did what I think should be done.

Here is the final firewall rule set.

[admin@Router] > /ip firewall/filter/print
Flags: X - disabled, I - invalid; D - dynamic
0 D ;;; special dummy rule to show fasttrack counters
chain=forward action=passthrough

1 ;;; Drop Invalid connections
chain=input action=drop connection-state=invalid

2 ;;; Allow Established connections
chain=input action=accept connection-state=established,related

3 ;;; Allow VLAN to router services
chain=input action=accept in-interface-list=VLAN

4 ;;; Allow Base_Vlan Full Access
chain=input action=accept in-interface=MGMT_VLAN

5 chain=input action=accept protocol=tcp src-address=192.168.0.0/24 dst-port=8291

6 ;;; VPN
chain=input action=accept src-address=10.22.22.10-10.22.22.20 log=no log-prefix=""

7 chain=input action=accept protocol=udp in-interface=MGMT_VLAN dst-port=161 log=no log-prefix=""

8 chain=input action=accept protocol=tcp src-address-list=slv_ddns in-interface=WAN dst-port=8291 log=no log-prefix=""

9 chain=input action=drop protocol=tcp dst-port=8291

10 ;;; Allow access to router from known network
chain=input action=accept src-address=192.168.0.0/24

11 ;;; Allow IPSEC/IKE2 connections
chain=input action=accept protocol=udp dst-port=500,4500 log=yes log-prefix=""

12 ;;; Drop anything else
chain=input action=drop

13 ;;; Accept in ipsec policy
chain=forward action=accept ipsec-policy=in,ipsec

14 ;;; Accept out ipsec policy
chain=forward action=accept ipsec-policy=out,ipsec

15 ;;; defconf: fasttrack
chain=forward action=fasttrack-connection hw-offload=yes connection-state=established,related log=no log-prefix=""

16 ;;; defconf: accept established,related, untracked
chain=forward action=accept connection-state=established,related,untracked log=no log-prefix=""

17 ;;; defconf: drop invalid
chain=forward action=drop connection-state=invalid log=no log-prefix=""

18 ;;; VLAN Internet Access only
chain=forward action=accept connection-state=new out-interface=WAN in-interface-list=VLAN

19 X ;;; Drop to bogon list
chain=forward action=drop dst-address-list=BOGONS log=yes log-prefix="bogons"

20 chain=forward action=accept out-interface=WAN

21 ;;; ?? Drop invalid connections
chain=forward action=drop connection-state=invalid protocol=tcp log=no log-prefix=""

22 chain=forward action=accept connection-state=new protocol=tcp dst-address=192.168.0.251 src-address-list=slv_ddns dst-port=443

23 ;;; ??
chain=forward action=drop log=no log-prefix=""

I had a problem to establish VPN connection to the router twice, third time was successful. I need to observe this problem. Maybe it gone after rule shiftment.

Logs are not so informative:
2026-03-29 11:29:25 ipsec,info killing ike2 SA: vpn 1.1.1.154[4500]-9.9.9.233[7068] e1cea77d266235d3:313d293bff2b18e9
2026-03-29 11:29:25 ipsec,info releasing address 10.22.22.14

2026-03-29 11:30:08 ipsec,info new ike2 SA (R): vpn 1.1.1.154[500]-9.9.9.233[40200] 5ca8fb1617d1463c:d17100d99e6ffc15
2026-03-29 11:30:08 firewall,info input: in:WAN out:(unknown 0), connection-state:new src-mac 02:00:00:00:00:04, proto UDP, 9.9.9.233:40200->1.1.1.154:500, len 1132
2026-03-29 11:30:08 ipsec,info,account peer authorized: vpn 1.1.1.154[4500]-9.9.9.233[7068] 5ca8fb1617d1463c:d17100d99e6ffc15
2026-03-29 11:30:08 ipsec,info acquired 10.22.22.14 address for 9.9.9.233, CN=Home client1

Maybe I need to enable dubbuging to see problems here.

Regards

Slawek