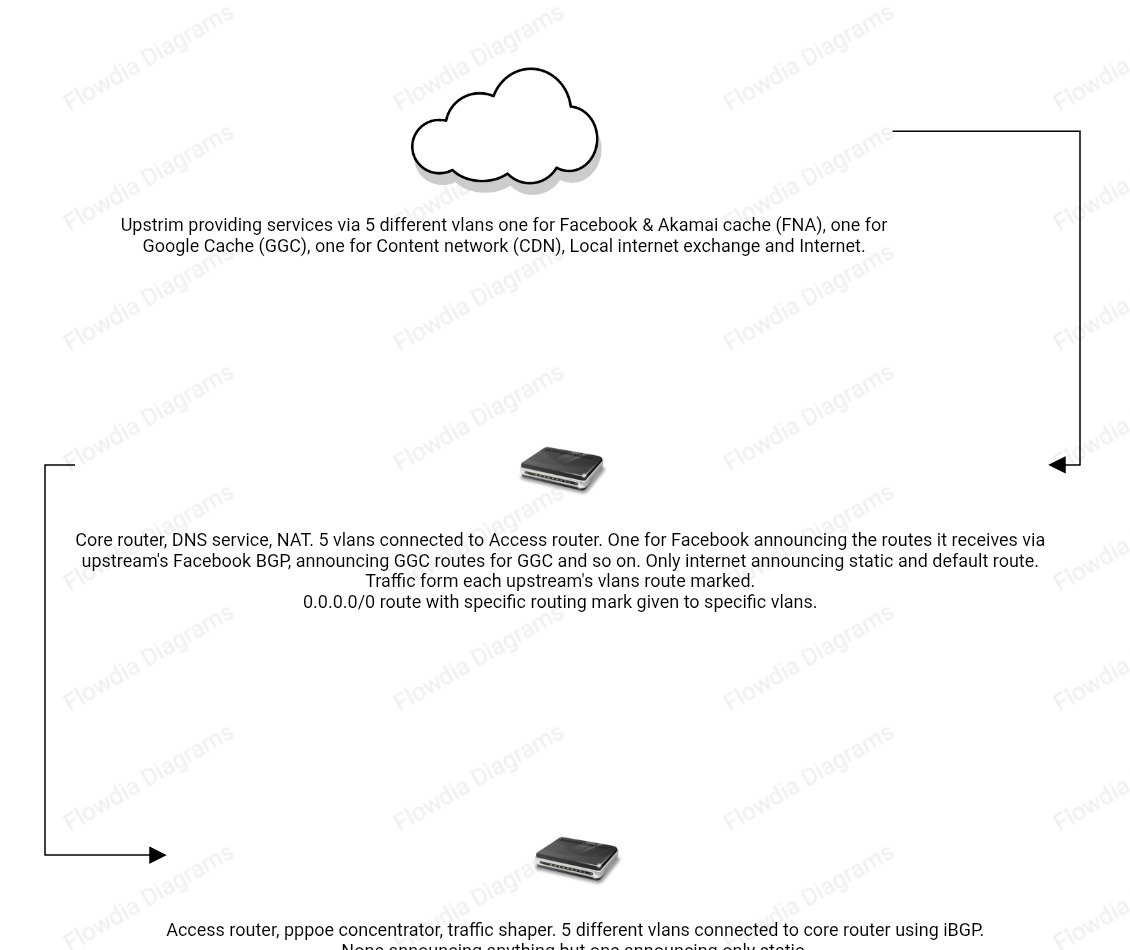
Upstream Description:
- Upstream providing services via 5 different vlans like Facebook & Akamai cache (FNA), Google Cache (GGC), Content network (CDN), Local internet exchange (IX) and Internet.
Core Router Description:
-
Core router running DNS service, NAT. 5 vlans connected to Access router, iBGP. One for Facebook announcing the routes it receives via upstream's Facebook BGP, announcing GGC routes for GGC and so on. Only internet announcing static and default route.
-
Traffic form each upstream's vlans route marked like fna, ggc, cdn, ix and internet.
-
$0.0.0.0/0 route with specific routing mark given to specific vlans. like 0.0.0.0/0 to access router’s ggc interface with ggc routing mark and so on.
Access Router Description:
-
Access router, pppoe concentrator, traffic shaper. 5 different vlans like fna, ggc, cdn, ix and internet connected to core router using iBGP.
-
None announcing anything but internet announcing only static.
-
Default route received from internet interface
Problem: Clients not getting internet. What’s wrong?