My central point was upgraded. After the upgrade it cut all OpenVPN clients (other Mikrotiks) because there seems to be some problem with a certificate. What to do now? Hopefully I don’t need to touch all the clients… the CA cert should be still valid, it is self-signed. I think this was caused by adding the built-in CA feature.
debug: <195.168.229.239>: disconnected <TLS error: ssl: no trusted CA certificate found (6)>
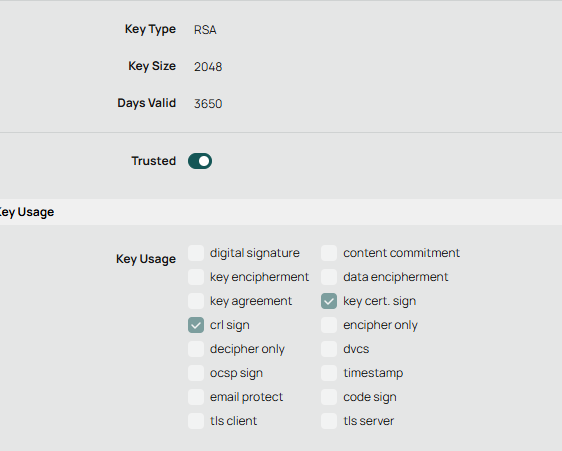
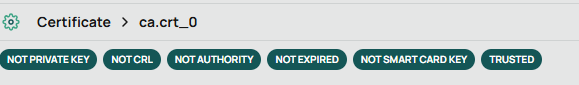
Solution: Guys really watch out, if you are upgrading remotely, this will just cut you off if you are using certificates. Disabling and enabling “Trusted” works, but this seems like a nasty bug. I was lucky my router has 4G backup.