What do you mean by:
What documentation do you have that the connection from Deutsche Telekom is untagged?
If it was untagged, why would they even specify a vlan at all?
What do you mean by:
What documentation do you have that the connection from Deutsche Telekom is untagged?
If it was untagged, why would they even specify a vlan at all?
The original post says
I am not sure what that means. Does that mean that the ONT is a two port vlan-aware switch that can be configured so the "Router side" connection is an access port for vlan 7?
What google says for the query Deutsche Telekom FTTH setup using your own router
Does the modem have SFP built in?
What is between the "modem" and the CRS309?
From the CRS309 can you see any traffic on SFP8?
That's it !!!!!!!!!!!!!!!!! 

Although I'm not sure if I've ever tried that version.
Under /IP/Addresses, I can see the dynamic IP coming in via the PPPoE-WAN-Telekom-FTTH interface.
However, I cannot select the interface in the DHCP client. Or do I not need the DHCP client?
Edit: see tdw's post (I forgot this was a pppoe connection).
But the DHCP client should be on the RB4011, not the CRS326.
The only vlan interface (what Cisco would refer to as an SVI) on the CRS309, CRS326 (and C2960) switches should be the management interface. Let the 4011 be the router and firewall (for WAN and for inter-vlan routing).
It is not needed as the connection uses PPPoE and addresses are assigned by Internet Protocol Control Protocol (IPCP), one of the PPP Network Control Protocols (NCP). DHCP is only required to obtain an IPv4 address for IPoE connections.
If the provider supports IPv6 then DHCPv6 is usually required to obtain an IPv6 prefix, and if the provider does not provide dual-stack IPv4 and IPv6 then some extra configuration is required for IPv4 connectivity. Of the various IPv4 tunnelling mechanisms Mikrotik only implement DS-Lite.
Yes, I know, I didn't mean the CRS326, I meant the RB4011.
With
/ip dhcp-client
add add-default-route=no default-route-tables=main interface=VLAN7-WAN-Telekom-FTTH name=VLAN7--WAN-FTTH script=":global dslip\r\
I'm not getting an IP address.
I forgot about the pppoe. again @tdw hit the nail on the head.
The CRS309 is just acting as a switch to pass the connection to the RB4011. The pppoe interface (PPPoE-WAN-Telekom-FTTH) is on the Rb4011. That's your internet interface.
From RB4011 config you posted.
/interface pppoe-client add allow=pap,chap,mschap2 interface=VLAN7-WAN-Telekom-FTTH name=PPPoE-WAN-Telekom-FTTH user=XXXXXXXXXXXXXXXXXXXX@t-online.de
It is using vlan 7 on the trunk between the CRS309 and the RB4011 to carry the pppoe encapsulated packets.
Is your internet connection not working?
With incomplete information one gets incomplete answers, said more familiarly, garbage in garbage out.
There was no mention that the FFTH came to the router already on vlan7.
That again as noted by others is easy to deal with, on the 309 switch, one simply changes the /bridge port setting for sp8 to admit only vlan tags and remove the pvid, and the /bridge vlan setting to tagged for sfp1 and sfp8.
Easy peasy lemon squeezy.
Not to worry Jorg, we dont do killing here, slow torture maybe! 
You have not made the necessary changes, first you have eth1 being management on the bridge but no association to it on the /bridge port settings. As I pointed this is rather useless as if the bridge burps you will not be able to access the router on this port or from any other device that goes through the bridge.
Make it an off bridge port.
Further you said it was a mnagement etherport in the ethernet name, and then promptly in bridge port settings assigned vlan20-Main to that port. Sorry thats not congruent. Do better!
I will assume you didnt want vlan20 here but our new better choice vlan-id=11
If you do want a working ethernet for a management guy cause he works right next to the switch then for shits and giggle I will use sfp3. Dont forget to add frame types.
Going to supper so cant do the router yet.
CRS309
model = CRS309-1G-8S+
/interface bridge add name=VLAN-Bridge1 vlan-filtering=yes
/interface ethernet set [ find default-name=ether1 ] name=OffBridge1
/interface ethernet set [ find default-name=sfp-sfpplus1 ] name=sfp01-Link_A1-RB4011
/interface ethernet set [ find default-name=sfp-sfpplus2 ] name=sfp02-Link_A3-CRS326
/interface ethernet set [ find default-name=sfp-sfpplus3 ] name=WorkingMGMT3
/interface ethernet set [ find default-name=sfp-sfpplus4 ] disabled=yes name=sfp04-Reserve
/interface ethernet set [ find default-name=sfp-sfpplus5 ] disabled=yes name=sfp05-Reserve
/interface ethernet set [ find default-name=sfp-sfpplus6 ] disabled=yes name=sfp06-Reserve
/interface ethernet set [ find default-name=sfp-sfpplus7 ] disabled=yes name=sfp07-Reserve
/interface ethernet set [ find default-name=sfp-sfpplus8 ] name=sfp08-WAN-FTTH
/interface vlan add interface=VLAN-Bridge1 name=VLAN1-MGMT vlan-id=11
/interface list
add name=MGMT
/interface bridge port
add bridge=VLAN-Bridge1 interface=sfp01-Link_A1-RB4011 frame-type=admit-only-vlan-tagged
add bridge=VLAN-Bridge1 interface=sfp02-Link_A3-CRS326 frame-type=admit-only-vlan-tagged
add bridge=VLAN-Bridge1 interface=WorkingMGMT3 frame-types=\
admit-only-untagged-and-priority-tagged pvid=11
add bridge=VLAN-Bridge1 interface=sfp08-WAN-FTTH interface=WorkingMGMT3 \
frame-types=admit-only-vlan-tagged
/interface list member
add interface=OffBridge1 list=MGMT
add interface=VLAN1-MGMT list=MGMT
/ip neighbor discovery-settings
set discover-interface-list=MGMT
/interface bridge vlan
add bridge=VLAN-Bridge1 tagged=VLAN-Bridge1,sfp01-Link_A1-RB4011,sfp02-Link_A3-CRS326 untagged=WorkingMGMT3 vlan-id=11
add bridge=VLAN-Bridge1 tagged=spf01-Link_A1-RB4011 \
vlan-id=5,20,22,25,30,32,40,50,53,54,55,56,60,70,74,78,80
add bridge=VLAN-Bridge1 tagged=sfp01-Link_A1-RB4011,spf08-WAN-FFTH vlan-id=7
/ip address add address=10.18.98.11/24 comment="Switch IP-Addresse" interface=VLAN1-MGMT network=10.18.98.0
/ip address add address=192.168.77.1/30 OffBridge1 network=192.168.77.0
/ip dns set servers=10.18.98.3
/ip route add disabled=no distance=1 dst-address=0.0.0.0/0 gateway=10.18.98.3 pref-src="" routing-table=main scope=30 suppress-hw-offload=no target-scope=10
/system clock set time-zone-autodetect=no time-zone-name=Europe/Berlin
/system identity set name=A2--Switch-CRS-309
/system leds set 13 interface=sfp08-WAN-FTTH type=interface-status
/system leds set 14 type=interface-receive
/system leds set 15 type=interface-transmit
/system leds add interface=VLAN-Bridge1 leds=user-led type=interface-activity
/system ntp client set enabled=yes
/system ntp client servers add address=time.98.hnet
/system routerboard settings set enter-setup-on=delete-key
/tool mac-server
set allowed-interface-list=none
/tool mac-server mac-winbox
set allowed-interface-list=MGMT
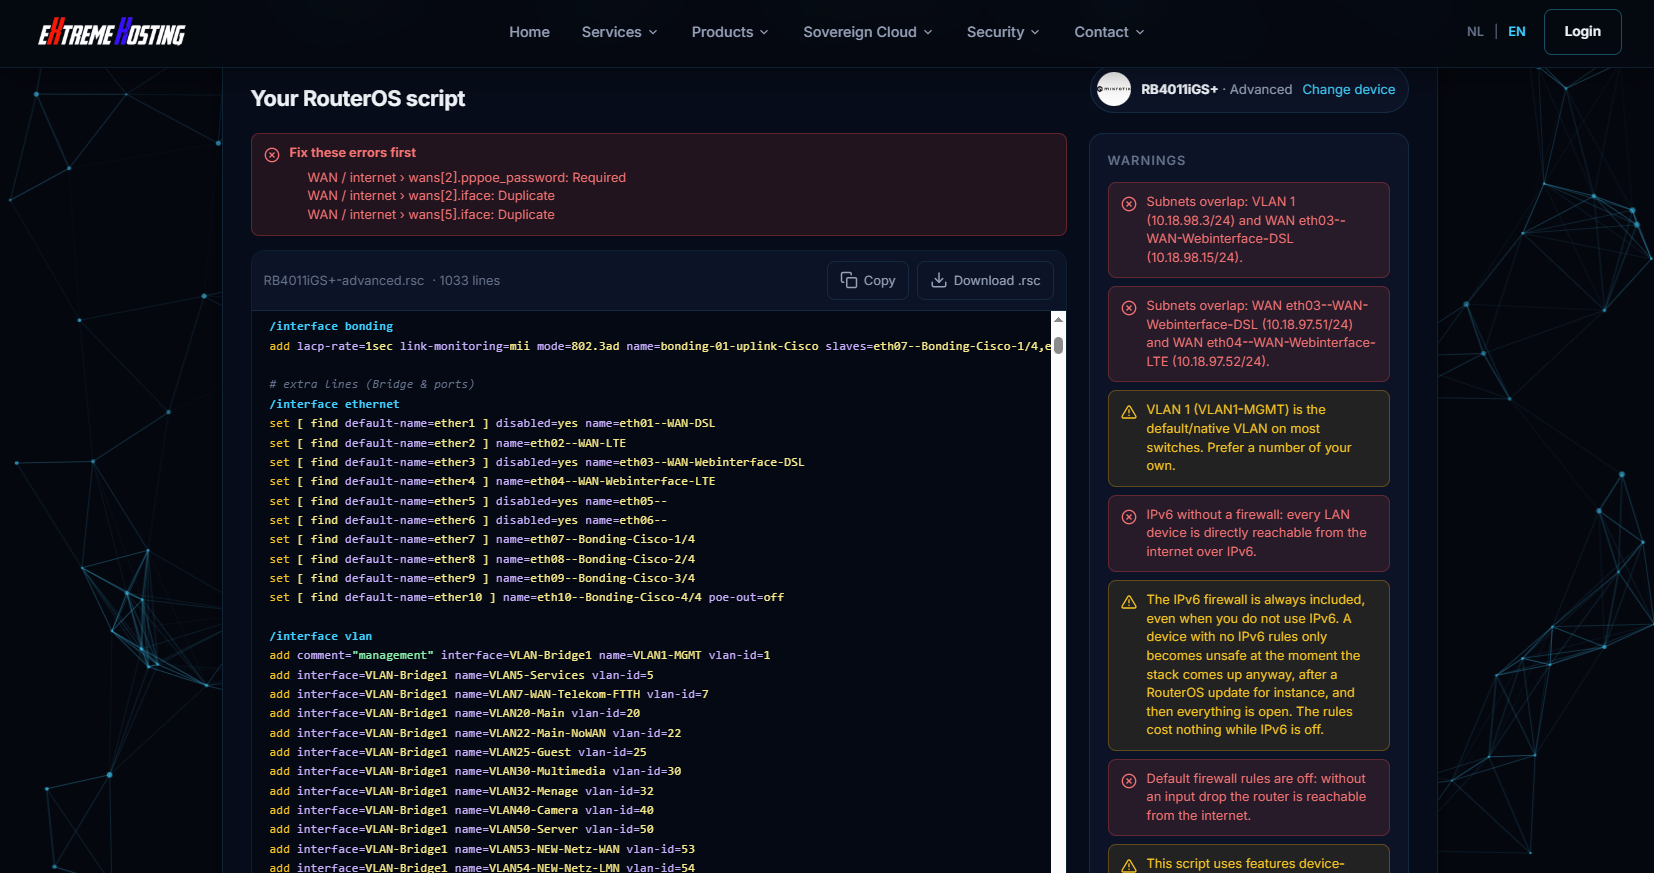
I just tried importing the RB4011_30.Aug.2026.rsc config into the MikroTik Configurator - eXtreme Hosting to see how it would work with a real configuration.
It does not like the use of vlan 1 for a vlan interface (it will accept it, but throws a warning).
Another option if you want to use vlan 1 for management and you don't mind Hybrid links (same as cisco trunk port with a native vlan), would be to just apply the ip address to the bridge instead of the vlan1 interface. This is essentially the same as choosing vlan 1 on a cisco switch. That's applying the ip address to the interface that will be associated with the native vlan on the "virtual hybrid link" between the CPU and the virtual switch portion of the bridge. If you don't change anything, the bridge will have a pvid (native/access vlan) of 1. And bridge ports will also have a pvid of 1 unless you override it. That's why you are able to turn vlan-filtering on and off without getting disconnected when you do the operation while connected to the ip address associated with the bridge.
Well, then I still have hope. 
Now, regarding VLAN 1—can that wait until the end? I don't just want to type something in; I want to understand it, too. Otherwise, it’ll be too much for me all at once. Please step by step. 
I didn't get in touch yesterday because I was writing a script that adjusts the routing—including firewall settings—whenever there is a new IP (it’s already working for IPv4).
I’m also adding a safety check so that PPPoE gets disabled if VLAN filtering is turned off.
In any case, the network is now up and running with the FTTH connection. 
However, I had to change the setting to "admit all" on the CRS309 SFP08-WAN-FTTH; otherwise, I experienced brief PPPoE interruptions. Could that become a problem?
Only you can decide how important the VLAN 1 issue is.
The forum, in general isn't a place you will get "step by step" spoon feeding specific to your individual situation. Especially for a configuration that is quite complex, where it appears you should already have the needed knowledge. What specifically is your question about vlan 1?
In general, I would never recommend anyone creating a vlan interface for vlan 1. Because there is already an implicit connection to vlan 1 via the (default) on the bridge itself. You can see this if you use the following CLI commands:
/interface bridge
/export verbose
/
The first line "sets you default CLI state to "/interface bridge"
The second exports with all options shown - including the defaults that are normally not listed with an export.
The third line resets the CLI state to the top level.
Here's the difference between an export and an export verbose
[demo@MikroTik] > /interface/bridge/
[demo@MikroTik] /interface/bridge> export
# 2025-10-21 01:45:47 by RouterOS 7.19.6
# software id = ****-****
#
# model = RB760iGS
# serial number = ************
/interface bridge
add name=bridge vlan-filtering=yes
/interface bridge port
add bridge=bridge interface=ether5 pvid=10
add bridge=bridge interface=ether4
/interface bridge vlan
# ether3 not a bridge port
add bridge=bridge tagged=ether3 vlan-ids=10
[demo@MikroTik] /interface/bridge> export verbose
# 2025-10-21 01:45:52 by RouterOS 7.19.6
# software id = ****-****
#
# model = RB760iGS
# serial number = ************
/interface bridge
add ageing-time=5m arp=enabled arp-timeout=auto auto-mac=yes dhcp-snooping=no \
    disabled=no ether-type=0x8100 fast-forward=yes forward-delay=15s \
    frame-types=admit-all igmp-snooping=no ingress-filtering=yes \
    max-learned-entries=auto max-message-age=20s mtu=auto mvrp=no name=bridge \
    port-cost-mode=long priority=0x8000 protocol-mode=rstp pvid=1 \
    transmit-hold-count=6 vlan-filtering=yes
/interface bridge port
add auto-isolate=no bpdu-guard=no bridge=bridge broadcast-flood=yes disabled=no \
    edge=auto fast-leave=no frame-types=admit-all horizon=none hw=yes \
    ingress-filtering=yes interface=ether5 !internal-path-cost learn=auto \
    multicast-router=temporary-query mvrp-applicant-state=normal-participant \
    mvrp-registrar-state=normal !path-cost point-to-point=auto priority=0x80 \
    pvid=10 restricted-role=no restricted-tcn=no tag-stacking=no trusted=no \
    unknown-multicast-flood=yes unknown-unicast-flood=yes
add auto-isolate=no bpdu-guard=no bridge=bridge broadcast-flood=yes disabled=no \
    edge=auto fast-leave=no frame-types=admit-all horizon=none hw=yes \
    ingress-filtering=yes interface=ether4 !internal-path-cost learn=auto \
    multicast-router=temporary-query mvrp-applicant-state=normal-participant \
    mvrp-registrar-state=normal !path-cost point-to-point=auto priority=0x80 \
    pvid=1 restricted-role=no restricted-tcn=no tag-stacking=no trusted=no \
    unknown-multicast-flood=yes unknown-unicast-flood=yes
/interface bridge settings
set allow-fast-path=yes use-ip-firewall=no use-ip-firewall-for-pppoe=no \
    use-ip-firewall-for-vlan=no
/interface bridge vlan
# ether3 not a bridge port
add bridge=bridge disabled=no mvrp-forbidden="" tagged=ether3 untagged="" \
    vlan-ids=10
[demo@MikroTik] /interface/bridge> /
[demo@MikroTik] >
I am not sure why "admit-all" on the CRS309 SFP08-WAN-FTTH is needed.
But since you have made changes to your config since your last upload, it would be helpful to see what the current configs are.
If you don't specify a pvid in /interface bridge port settings, the "default" pvid=1 will be used. This means any untagged traffic from the WAN will be put into vlan 1 on the switch.
If you use the cli commands
/interface/bridge print
/interface/bridge/port print
/interface/bridge/vlan print
You will get useful info
Here's an example from the same lab RB760iGS that the exports above were from.
[demo@MikroTik] > /interface/bridge print
Flags: D - dynamic; X - disabled, R - running
 0  R name="bridge" mtu=auto actual-mtu=1500 l2mtu=1596 arp=enabled arp-timeout=auto mac-address=DC:2B:AD:4D:EC:F5 protocol-mode=rstp
      fast-forward=yes igmp-snooping=no auto-mac=yes ageing-time=5m priority=0x8000 max-message-age=20s forward-delay=15s
      transmit-hold-count=6 vlan-filtering=yes ether-type=0x8100 pvid=1 frame-types=admit-all ingress-filtering=yes dhcp-snooping=no
      port-cost-mode=long mvrp=no max-learned-entries=auto
[demo@MikroTik] > /interface/bridge/port print
Flags: I - INACTIVE; H - HW-OFFLOAD
Columns: INTERFACE, BRIDGE, HW, HORIZON, TRUSTED, FAST-LEAVE, BPDU-GUARD, EDGE, POINT-TO-POINT, PVID, FRAME-TYPES
#    INTERFACE  BRIDGE  HW   HORIZON  TRUSTED  FAST-LEAVE  BPDU-GUARD  EDGE  POINT-TO-POINT  PVID  FRAME-TYPES
0 IH ether5     bridge  yes  none     no       no          no          auto  auto              10  admit-all
1  H ether4     bridge  yes  none     no       no          no          auto  auto               1  admit-all
[demo@MikroTik] > /interface/bridge/vlan print
Flags: D - DYNAMIC
Columns: BRIDGE, VLAN-IDS, CURRENT-UNTAGGED
#   BRIDGE  VLAN-IDS  CURRENT-UNTAGGED
;;; ether3 not a bridge port
0   bridge        10
;;; added by pvid
1 D bridge         1  bridge
                      ether4
[demo@MikroTik] >
The problem with creating a vlan interface for vlan 1 while still leaving the pvid of the bridge set to 1, is that now you have two separate L3 interfaces (the bridge itself using untagged, and the vlan1 interface using tags) connecting to the same vlan 1 on the switch, one using untagged traffic (implicitly assocated with vlan 1 by the pvid) and one using explicit vlan 1 IEEE 802.1Q tags. The IEEE 802.1Q standard states that only a single type of framing (either tagged on untagged) should be used by a specific vlan on a link. i.e. you shouldn't have a link where one side is expecting vlan x to be untagged and another device is expecting vlan x to be tagged. In cisco when you specify a native vlan on a trunk, that configures the switch to expect traffic for the native vlan to be untagged, and when traffic for that vlan egresses through the trunk port, if the vlan it is coming from is the same as the pvid (native vlan) then the ethernet frame is sent without a vlan tag (for that specifid vlan id). Recent version (7.16+ of ROS) will add "hidden" dynamic setting (they don't show up in export, but they do in print) when you create a vlan interface under a bridge. These will add the bridge as a tagged for that vlan id.
Here's example: I duplicated the output of /interface/bridge/vlan print at the end from before the vlan1 interace was created, so it is easier to compare the two.
[demo@MikroTik] > /interface/bridge print
Flags: D - dynamic; X - disabled, R - running
 0  R name="bridge" mtu=auto actual-mtu=1500 l2mtu=1596 arp=enabled arp-timeout=auto mac-address=DC:2B:AD:4D:EC:F5 protocol-mode=rstp
      fast-forward=yes igmp-snooping=no auto-mac=yes ageing-time=5m priority=0x8000 max-message-age=20s forward-delay=15s
      transmit-hold-count=6 vlan-filtering=yes ether-type=0x8100 pvid=1 frame-types=admit-all ingress-filtering=yes dhcp-snooping=no
      port-cost-mode=long mvrp=no max-learned-entries=auto
[demo@MikroTik] > /interface/bridge/port print
Flags: I - INACTIVE; H - HW-OFFLOAD
Columns: INTERFACE, BRIDGE, HW, HORIZON, TRUSTED, FAST-LEAVE, BPDU-GUARD, EDGE, POINT-TO-POINT, PVID, FRAME-TYPES
#    INTERFACE  BRIDGE  HW   HORIZON  TRUSTED  FAST-LEAVE  BPDU-GUARD  EDGE  POINT-TO-POINT  PVID  FRAME-TYPES
0 IH ether5     bridge  yes  none     no       no          no          auto  auto              10  admit-all
1  H ether4     bridge  yes  none     no       no          no          auto  auto               1  admit-all
[demo@MikroTik] > /interface/bridge/vlan print
Flags: D - DYNAMIC
Columns: BRIDGE, VLAN-IDS, CURRENT-UNTAGGED
#   BRIDGE  VLAN-IDS  CURRENT-UNTAGGED
;;; ether3 not a bridge port
0   bridge        10
;;; added by pvid
1 D bridge         1  bridge
                      ether4
[demo@MikroTik] > /interface print
Flags: R - RUNNING; S - SLAVE
Columns: NAME, TYPE, ACTUAL-MTU, L2MTU, MAX-L2MTU, MAC-ADDRESS
#    NAME    TYPE      ACTUAL-MTU  L2MTU  MAX-L2MTU  MAC-ADDRESS
0 R  ether1  ether           1500   1596       2026  DC:2B:AD:4D:EC:F1
1 R  ether2  ether           1500   1596       2026  DC:2B:AD:4D:EC:F2
2 R  ether3  ether           1500   1596       2026  DC:2B:AD:4D:EC:F3
3 RS ether4  ether           1500   1596       2026  DC:2B:AD:4D:EC:F4
4  S ether5  ether           1500   1596       2026  DC:2B:AD:4D:EC:F5
5    sfp1    ether           1500   1596       2026  DC:2B:AD:4D:EC:F6
6 R  bridge  bridge          1500   1596             DC:2B:AD:4D:EC:F5
7 R  lo      loopback       65536                    00:00:00:00:00:00
[demo@MikroTik] > /interface vlan add interface=bridge name=vlan1 vlan-id=1
[demo@MikroTik] > /interface print
Flags: R - RUNNING; S - SLAVE
Columns: NAME, TYPE, ACTUAL-MTU, L2MTU, MAX-L2MTU, MAC-ADDRESS
#    NAME    TYPE      ACTUAL-MTU  L2MTU  MAX-L2MTU  MAC-ADDRESS
0 R  ether1  ether           1500   1596       2026  DC:2B:AD:4D:EC:F1
1 R  ether2  ether           1500   1596       2026  DC:2B:AD:4D:EC:F2
2 R  ether3  ether           1500   1596       2026  DC:2B:AD:4D:EC:F3
3 RS ether4  ether           1500   1596       2026  DC:2B:AD:4D:EC:F4
4  S ether5  ether           1500   1596       2026  DC:2B:AD:4D:EC:F5
5    sfp1    ether           1500   1596       2026  DC:2B:AD:4D:EC:F6
6 R  bridge  bridge          1500   1596             DC:2B:AD:4D:EC:F5
7 R  lo      loopback       65536                    00:00:00:00:00:00
8 R  vlan1   vlan            1500   1592             DC:2B:AD:4D:EC:F5
[demo@MikroTik] > /interface/vlan print
Flags: R - RUNNING
Columns: NAME, MTU, ARP, VLAN-ID, INTERFACE
#   NAME    MTU  ARP      VLAN-ID  INTERFACE
0 R vlan1  1500  enabled        1  bridge
[demo@MikroTik] > /interface/bridge/vlan print
Flags: D - DYNAMIC
Columns: BRIDGE, VLAN-IDS, CURRENT-TAGGED, CURRENT-UNTAGGED
#   BRIDGE  VLAN-IDS  CURRENT-TAGGED  CURRENT-UNTAGGED
;;; ether3 not a bridge port
0   bridge        10
;;; added by pvid
1 D bridge         1                  ether4
;;; added by vlan on bridge
2 D bridge         1  bridge
[demo@MikroTik] > # compare to previous output before vlan1 was created
[demo@MikroTik] > # bridge connection to switch for vlan-id 1 has changed from untagged to tagged
[demo@MikroTik] >
Here's what it was before vlan1 created then after for easier comparison
Before creating vlan1 interface
[demo@MikroTik] > /interface/bridge/vlan print
Flags: D - DYNAMIC
Columns: BRIDGE, VLAN-IDS, CURRENT-UNTAGGED
#   BRIDGE  VLAN-IDS  CURRENT-UNTAGGED
;;; ether3 not a bridge port
0   bridge        10
;;; added by pvid
1 D bridge         1  bridge
                      ether4
[demo@MikroTik] >
After creating vlan1 interface
[demo@MikroTik] > /interface/bridge/vlan print
Flags: D - DYNAMIC
Columns: BRIDGE, VLAN-IDS, CURRENT-TAGGED, CURRENT-UNTAGGED
#   BRIDGE  VLAN-IDS  CURRENT-TAGGED  CURRENT-UNTAGGED
;;; ether3 not a bridge port
0   bridge        10
;;; added by pvid
1 D bridge         1                  ether4
;;; added by vlan on bridge
2 D bridge         1  bridge
[demo@MikroTik] >
@Buckeye
A good example on how to break BOTH rules #1 AND #2:
The twelve Rules of Mikrotik Club

Maybe I wasn't clear is what the pupose of the examples was. It was not meant as a recommendation, but as an example of what creating a vlan interface for vlan id 1 actually does on a recent version of ROS.
To go further into the weeds, here's what happens when you change the pvid of the bridge to 666, and have a vlan1 interface. After this, the device connected to ether4 will be connected to the vlan1 interface instead of the bridge, and there is no ambiquity of what is connected to vlan 1. The bridge interface is now using vlan 666 and no other ports in the switch (bridge) are members of vlan 666.
I haven't tested to see how or if this would affect rstp. Without testing, my guess is that it would still work. The reason being that there is still a connection between the CPU and the "virtual switch", it just happens to be using a different vlan than the default vlan-id 1.
I generally leave the bridge pvid at 1, and don't create a vlan interface for vlan id 1.
Whether you apply an ip address to the bridge itself has arguments for and agaist. It's more of a personal preference thing than "correct" or "incorrect". That does not imply that different people have stong opinions one way or the other.
[demo@MikroTik] > /interface/bridge/set pvid=666
numbers: 0
[demo@MikroTik] > /interface/bridge print
Flags: D - dynamic; X - disabled, R - running
 0  R name="bridge" mtu=auto actual-mtu=1500 l2mtu=1596 arp=enabled arp-timeout=auto mac-address=DC:2B:AD:4D:EC:F5 protocol-mode=rstp
      fast-forward=yes igmp-snooping=no auto-mac=yes ageing-time=5m priority=0x8000 max-message-age=20s forward-delay=15s
      transmit-hold-count=6 vlan-filtering=yes ether-type=0x8100 pvid=666 frame-types=admit-all ingress-filtering=yes dhcp-snooping=no
      port-cost-mode=long mvrp=no max-learned-entries=auto
[demo@MikroTik] > /interface/bridge port print
Flags: I - INACTIVE; H - HW-OFFLOAD
Columns: INTERFACE, BRIDGE, HW, HORIZON, TRUSTED, FAST-LEAVE, BPDU-GUARD, EDGE, POINT-TO-POINT, PVID, FRAME-TYPES
#    INTERFACE  BRIDGE  HW   HORIZON  TRUSTED  FAST-LEAVE  BPDU-GUARD  EDGE  POINT-TO-POINT  PVID  FRAME-TYPES
0 IH ether5     bridge  yes  none     no       no          no          auto  auto              10  admit-all
1  H ether4     bridge  yes  none     no       no          no          auto  auto               1  admit-all
[demo@MikroTik] > /interface/bridge vlan print
Flags: D - DYNAMIC
Columns: BRIDGE, VLAN-IDS, CURRENT-TAGGED, CURRENT-UNTAGGED
#   BRIDGE  VLAN-IDS  CURRENT-TAGGED  CURRENT-UNTAGGED
;;; ether3 not a bridge port
0   bridge        10
;;; added by pvid
1 D bridge         1                  ether4
;;; added by vlan on bridge
2 D bridge         1  bridge
;;; added by pvid
3 D bridge       666                  bridge
[demo@MikroTik] >
Worth a read (at least a skim)
RouterOS bridge mysteries explained
Vlan-aware bridge mysteries
Beginners journey into VLANs continued in this thread VLANed home network, 2nd try
Should I change that to this? (RB4011)
add bridge=VLAN-Bridge1 tagged=VLAN-Bridge1,sfp-sfpplus1,bonding-01-uplink-Cisco,eth04--WAN-Webinterface-LTE vlan-ids=1

add bridge=VLAN-Bridge1 tagged=VLAN-Bridge1,sfp-sfpplus1,bonding-01-uplink-Cisco,eth04--WAN-Webinterface-LTE vlan-ids=11
I have never used bonding on Mikrotik to a Cisco etherchannel.
If you don't have the link working with vlans between the RB4011 and the C2960, I recommend watching these two The Network Berg youtube videos. First MikroTik & Cisco - Configuring LACP then MikroTik & Cisco - VLANs over LACP
But I think your question is about vlans, not LACP.
Most people recommend against tagging vlan id 1. Here's a good writeup about why Tagged VLAN 1 In a Trunk Is a Really Bad Idea
That isn't because it is disallowed by the standard, but because there are vendors that won't allow that (an example is Ubiquiti Unifi, although Ubiquiti Edgemax devices like EdgeRouters allow it). The Unifi controller just doesn't even give vlan 1 as an option when specifying vlans for a trunk port, and when they mention vlan 1 they mean "the untagged" vlan in a hybrid port, what Cisco would refer to as the native vlan, and most other vendors use the IEEE 802.1Q standard's name "PVID" (port vlan id).
An important thing to understand when using vlans, is that the devices on both ends of the link need to agree on what vlans are allowed, and what should be done with untagged traffic (keep or drop, associate with a specific vlan - the pvid).
So the real questions are:
Yes, the PC I'm using to configure the network is connected to C2960.
###################################################################
!
interface Port-channel1
description Mikrotik Downlink
switchport mode trunk
switchport nonegotiate
switchport trunk allow vlan all
!
!
!
interface GigabitEthernet 1/0/49
description LAG RB4011 1/4
switchport mode trunk
switchport nonegotiate
switchport trunk allow vlan all
channel-group 1 mode active
duplex auto
speed auto
no macro description
macro description cisco-switch
!
interface GigabitEthernet 1/0/50
description LAG RB4011 2/4
switchport mode trunk
switchport nonegotiate
switchport trunk allow vlan all
channel-group 1 mode active
duplex auto
speed auto
no macro description
macro description cisco-switch
!
interface GigabitEthernet 1/0/51
description LAG RB4011 3/4
switchport mode trunk
switchport nonegotiate
switchport trunk allow vlan all
channel-group 1 mode active
duplex auto
speed auto
no macro description
macro description cisco-switch
!
interface GigabitEthernet 1/0/52
description LAG RB4011 4/4
switchport mode trunk
switchport nonegotiate
switchport trunk allow vlan all
channel-group 1 mode active
duplex auto
speed auto
no macro description
macro description cisco-switch
!
!
###################################################################
Did you mean that?