Yes, I was beginning to wonder if you ever have done any configs…
I will try to follow the logic…
(1) Not sure where you got
a. ether5 OR
b. that it was an access port.
The only evidence I can find above that is a trunk port with unknown purpose.
In any case lets say it was an access port to play along!!
(2) Bridge ports, look good!
(3) Bridge Vlans, hmm dont like the autogenerate method but its viable.
For some nagging reason I think you still need a rule to note that the bridge is tagged for this…
Ahh I see vlan10 is tagged in the first line by the bridge so that is covered…
/interface bridge vlan
add bridge=bridge tagged=bridge,ether2,ether3,ether4 vlan-ids=10
add bridge=bridge tagged=bridge,ether2,ether3,ether4 vlan-ids=20
add bridge=bridge tagged=bridge,ether2,ether3,ether4 vlan-ids=40
What I am saying, for example if vlan 10 was not tagged on ether2,3,4, then we would need a rule as such
add bridge=bridge tagged=bridge vlan-ids=10
Its here where manually inserting the untag makes sense or at least to make it clear why.
(4) /ip firewall nat
add chain=srcnat action=masquerade out-interface=vlan-10 in-interface-list=restricted-vlans
So this rule is designed to allow vlan20 and vlan30 traffic to reach the client computers on the vlan10 network if that the desire of the OP??
It will not allow traffic originating on vlan10 from reaching vlans20, 30 though? right?
(5) then with firewall rules you block such traffic so was a bit confusing for me… ???
add chain=forward action=drop dst-address=192.168.10.0/24 in-interface-list=restricted-vlans
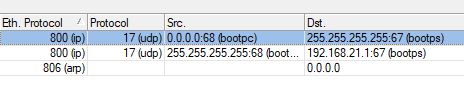
(6) The rest of the rules are sweet, I gather port 68 is the source port and 67 is the destination port for traffic originating from dhcp clients on vlan10 behind the MT??
(7) Overall one of us a bit confused in the forward chain. The input chain was clear with a drop all rule at the end, why not carry through with the forward chain as well.
It could be?
add chain=forward action=accept dst-address=192.168.10.1 in-interface-list=restricted-vlans
add chain=forward action=drop
..
 ), I think this router doesn’t need a very strict firewall. It’s job is to protect itself and to protect main LAN (as far as it can). The rest is then up to ASUS. Or, depending on ASUS configuration, even up to config on this router. And, your suggestion would block clients of those two vlans from reaching internet … because dst-address of those packets is not ASUS’ address, it’s everything else…