RouterOS Device-Mode: Complete Operational Guide
Device-mode is a hardware-enforced security feature in MikroTik RouterOS. It restricts or protects sensitive system features (like containers, traffic sniffing, scripts, or downgrades). This minimizes the attack surface if a router is compromised remotely.
To prevent unauthorized changes, any modification to the device-mode requires physical access to the router.
 1. Understanding Device-Mode States
Device-mode functions through specific features that can be individually enabled or disabled, or grouped into pre-defined profiles.
Protected Features
container: Controls the deployment of Docker/App containers.downgrade: Controls whether RouterOS can be downgraded to an older version.fetch: Controls the /tool/fetch command (often used by malware to download payloads).ramdisk: Controls booting or installing RouterOS from RAM.scheduler: Controls automated task execution via /system/scheduler.socks: Controls the SOCKS proxy server.traffic-sniffer: Controls packet capture capabilities.
Mode Profiles
advanced: All features are enabled by default (standard full-access router behavior).home: Disables high-risk network enterprise features like traffic-sniffer and socks to protect home environments.basic: Highly restrictive mode for simple deployment scenarios.
 2. Step-by-Step Configuration via CLI
Device-mode configuration cannot be modified via WebFig or WinBox GUI for security reasons. You must use the Command Line Interface (CLI).
Step 1: Check Current Device-Mode Status
Run this command to see your current mode and which features are enabled or disabled:
routeros
/system/device-mode/print
Usa il codice con cautela.
Step 2: Initiate the Update Command
You can change the overall mode or toggle specific features.
-
Example A: Switch to Advanced Mode (Enables all features)
routeros
/system/device-mode/update mode=advanced
Usa il codice con cautela.
-
Example B: Enable Containers while keeping other restrictions
routeros
/system/device-mode/update container=yes
Usa il codice con cautela.
-
Example C: Block RouterOS Downgrades for strict security
routeros
/system/device-mode/update downgrade=no
Usa il codice con cautela.
Step 3: Physical Verification (Mandatory)
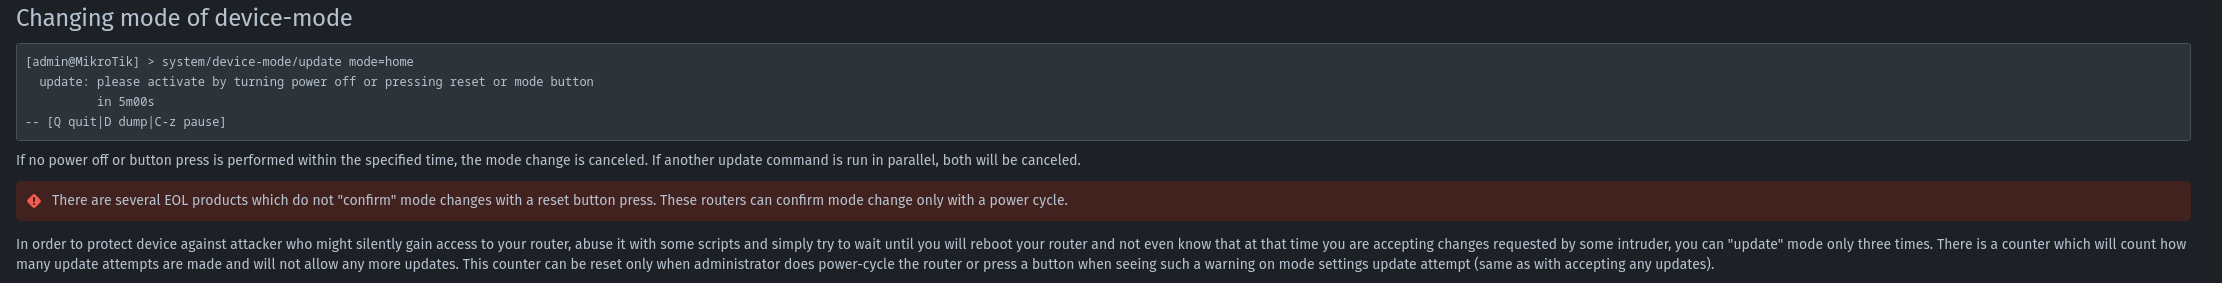
After executing an update command, RouterOS enters a pending state and outputs a message on the terminal. You have a 5-minute window to prove physical ownership of the hardware.
To confirm the changes, you must do one of the following:
- Cold Reboot: Physically unplug the power cable from the router and plug it back in. (Note: A software reboot via
/system/reboot will NOT work).
- Button Press: Press the physical RESET button (or Mode button on supported models) on the router chassis when prompted by the CLI.
 Warning: If you do not perform the physical action within 5 minutes, the task times out, and the configuration reverts to its previous state.
 3. Troubleshooting & Notes
- "Action failed: device-mode does not allow...": If you see this error while running scripts, fetch tools, or starting containers, it means the current device-mode profile is blocking that feature. You must follow the steps above to unlock it.
- Resetting Device-Mode: If you lock yourself out of a feature and cannot access the physical button easily, a full Netinstall (reflashing the router firmware via network) is required to reset the security boundaries.