It's a horrible configuration for anything beyond single LAN network. You should know very well that a lot of home owners (and by extension, "home" users) want at minimum separation for Guest network (yes, separation, not just SSID), and default does not provide that in any way.
MikroTik never catered to "out of the box, it works" audience and never will, because the defaults and QuickSet is so limited that it's worse than 2010s TP-Link router, let alone what various brands sell now. Until this changes, we can not in good conscience talk about "home users" using default configuration.
Ultimately, what I would've wanted to see in announcement is:
This version contains patches for a critical security vulnerability that is under active exploitation. Devices with management services exposed to untrusted networks are at highest risk.
Skip the entire "default configuration is secure" part here. You can put it in full writeup later, explaining advantages of it, but it has little place in basic announcement. It's also arguably untrue, as infected device (which would ordinarily contain no credentials for router, for example your kid's laptop) connected to your network can be used to exploit router in its default configuration (no network segmentation exists).
Have you seen any block of flats WiFi environment? Full of "Customer N - 5GHz" + "Customer N - 2.4GHz", "Customer N+1 - 5GHz" + "Customer N+1 - 2.4GHz" ... and so on ... networks.
They DO NOT CARE as they DO NOT KNOW what the network is. It is an INTERNET for them.
They JUST USE theirs networks and connect everything to it?
Do they care that their mobiles, TV sets, cleaners, friges, ovens, cleaning robots connect to the internet?
No, they sneez at such problems. they DEMAND Internet. That is all. How many plug&play "home user" popular brand routers/AP provide easy VLAN separation with different SSIDs? One DHCP server, one DNS, almost no firewall settings + simple port forwarding and DMZ zone. MOST of users do not go anywhere near those place, not even within a long pole's length.
You/we as a more informed users are aware ot that and could try to have separated networks but IMHO (sic!!!) is much,much exagerrated problem. Not saying that there is no problem but for an typical user it makes no sense. You are aware of many topics started for "VLAN for my lab, VLAN for my kids, VLAN for my IoT, VLAN for my heating system, for cameras, for a backyard, for my real friends, for mu not so liked friends and at last the one for my guests I do not know" + hotspot + encrypted/free one ... oh my "Holy Packet in Heaven" ... what for?
It really is wild how many people i know that call internet/ethernet/routers/switches/ just wifi, "my wifi is not working" they dont know what a network is, they dont know what that cable does, "the wifi cable got cut by [insert name] we didnt need it anymore", etc etc.
And let me tell you, nobody is gonna check ur configurations, unless its a hired networking tech + nobody really cares about 500 vlans u got at home to segment everything as if you're some kind of a enterprise.
IMO - having a network for IoT, Guests, and a private/general vlan for stuff like phones and laptops is already good enough.
They are extremly scared to unplug something and touch anything networking related, which is good in a way, but also kinda annoying when you have to drive 2 cities away to unplug a cable and move it to a different port.
It is what it is.
It's always hard to balance what should be revealed to the public at the moment when the "sh*t hit the fan". To give users time to protect themselves (these who are interested in) without giving crackers or AI the receipt on the plate just in front of their fingertips, or not to give?
I agree (as I wrote earlier) that sugercoating the problem with "improved stability" is a bad habit. It should be said clearly and loudly but, for all Gods sake, let be realistic. No way to satisfy all.
Things get better when it comes to MT's communication IMO.
Run /console clear-history once to free about 60KB. Alternatively, switch to the Development channel and upgrade to 7.25beta3 that should reduce the package size by over 300KB.
And then the user starts asking "Why my friend is not able to detect my private printer?".
Not "Why?" but "WHY?".
It should not work like that as I want such ability ... no .. "I WANT NOW".
Explaining that last week it was decided to configure VLANS to move "strangers" away from my network makes no sense as "I thought that my family, best friends and a postman could be able to connect to my ... put the name you want here"
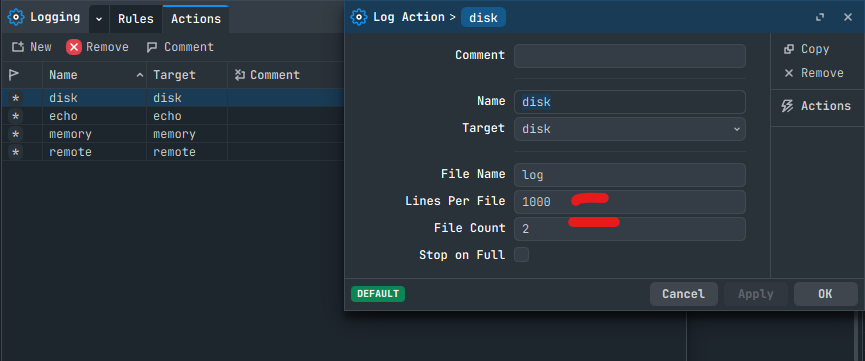
no Logging Rules were set to Action=Disk so its settings were supposedly irrelewant, nevertheless I've tried setting Lines=1 and File Count = 1 - did not help; /console clear-history did not help
but upgrade to 7.25beta3 did the trick, Thanks CGGXANNX!
The router's now refusing Winbox 3.43 but that a minor problem compared to Security. Lets see how it works.
Back to the topic... I can understand why MikroTik is remaining tight-lipped about the details. Still, it would be nice to get some basic information on what to check or secure first. Is it SSH? If so, we could disable it or block it via the firewall. Is it another service? Which one? We manage a lot of customer devices with varying configurations, and right now, we don't know where to prioritize. It was a long night upgrading and checking the first batch... Thankfully, no compromised devices found so far.
You don't need any special configuration aside from the SSH service being reachable.
Telnet / www were vulnerable to the same passing usernames as CLI arguments to /bin/login issue, but I couldn't find a route to exploitation there. Ssh is special.
Again don't want to hand attackers a blueprint, but please be assured if you had SSH on the internet you could be compromised regardless of how it was configured.
Just because SSH is the current vector doesn't mean the others couldn't become one but it'd be a different variation of the exploit.
I have two test devices where a user called "ops" has been created on 02.09.2026 via SSH from IP: 82.192.72.4. The update has been installed 5 minutes after the push notification appeared 03.09.2026 18:35 GMT+1.
Do we need to do a fresh netinstall or /system/check-installation > status: installation is ok.
What if the attackers manipulated the underlying Linux install < would check-installation (after the update) detect a tampered / compromised device?
Good question for @normis. If it reported an issue, that be a problem to report. But my guess is that "ok" does not mean you're safe since it not a complete sweep of everything, rather package integrity. So if the attacker modified config files, I'm not sure that something it catches.
I do hourly backups + config export and push them into Git.
There have no config changes been made except the added "ops" user.
According to the logs, on one device a second after creating the "ops" user I see a failed login for this user.
On the other device I don't have the log but a last login timestamp in /user/print for 2026-09-02 14:59:45.