Hello,
I need my mikrotik connected as an openvpn client to ovpn server on pfsense somewhere else.
I made it work, but not exactly always, because connection work, if it gets connected, sometimes trying for long time, sometimes never get connected
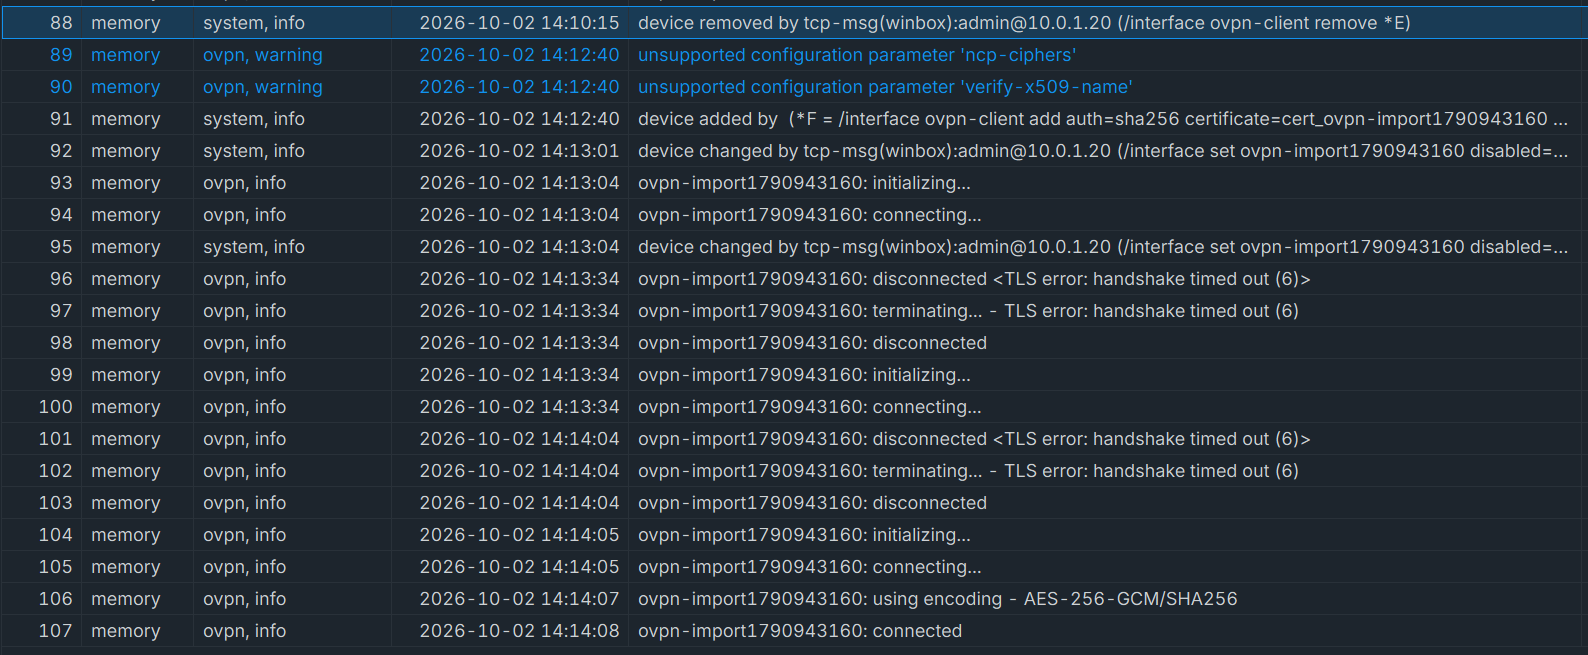
for now I've got:
as you can see i just imported profile, tried to connect, got bounced 2 times and got connected. But in that strange inconsistent openvpn client behavior i can't be sure it will reconnect after router restart, or re-enabling interface. Sometimes i get connected at first attempt, sometimes got infinite tls errors ( in pfsense I appear as UNDEF user [that one trying to connect, but not authenticated yet]).
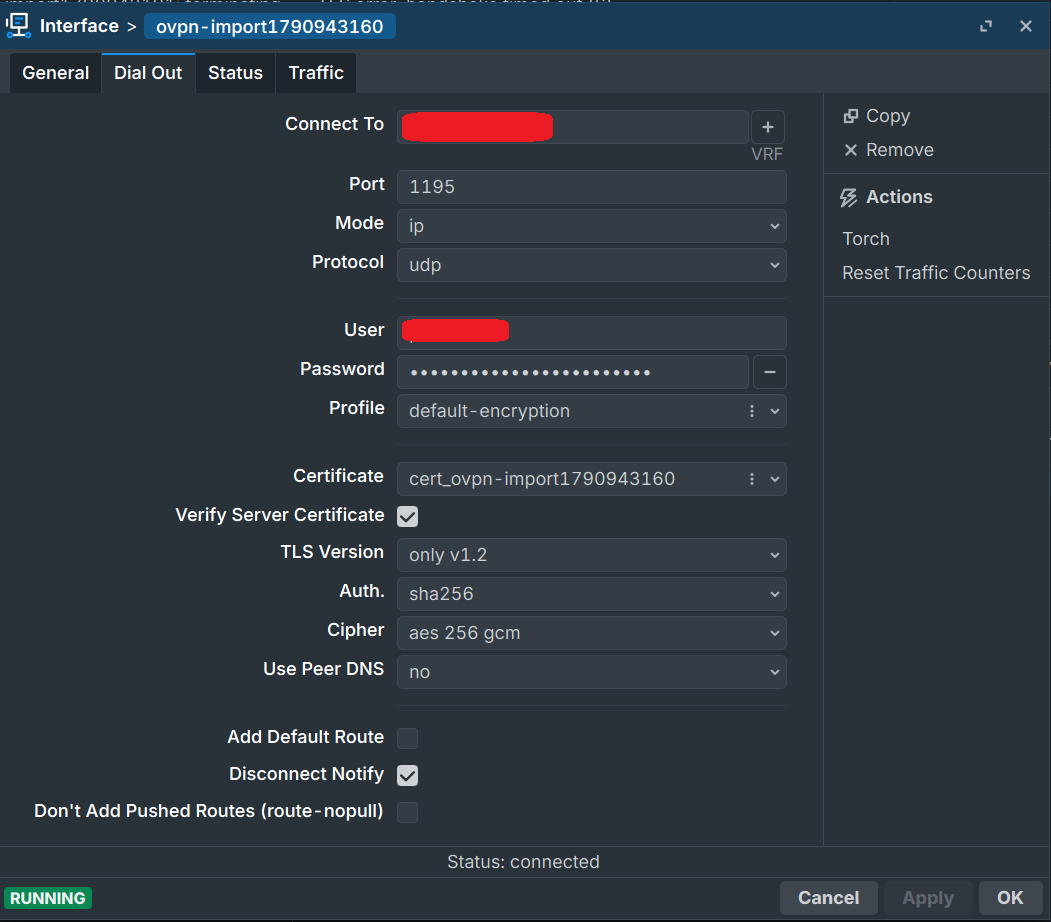
If i delete ovpn interface, certificates etc and import same profile, configure it same way it's possible to make it work that way.
And it's not problem with certs imported from .ovpn file, tried .crt too and got same results.
Anybody faced similar problem?
I have seen issues with some ciphers not working recently with OVPN to my server. The result is a hard drop of the session init by ROS. No resolution yet - I have a ticket open, and have been asked for more info by Mikrotik, but have not been able to provide it yet. In my case, it seemes like aws-128-gcm and aes-256-gcm are the only ones working, and it's possible that your sessions may be failing others before hitting one that works. You might try restricting those on your server definition if more are enabled (As well as other encryption/TLS/etc. options) to those that are known good. (This problem popped up on me with OpenVPN pretty recently after an ROS update, iirc, 7.23.3 to 7.23.5 or so.)
(This may be unrelated since you may be failing earlier, but figured that I'd at least mention it . . . )
Hello there,
Thanks for your reply. Tommorrow i will update my pfsense to latest 2.9.0 version, so i will have more recenct ovpn server too. On monday i'll try your advice out.
For now I don't remember my ROS version, most recent for rb750 board (heX 3 or something like that) I believe it can be 7.40.x something. I didn't try out earlier, cause I was waiting for ROS support TLS-auth key (that one which allow you to try to login, as a first step of connecting). I'll be back on monday with some news
I hit this with OpeenVPN 2.7.0 and update past ROS 7.23.3, for what it's worth.
The only change to cause issues was ROS, and setting supported ciphers got it to work.
(I saw the same issues with the most recent Android client as well . . . )
I've installed PfSense 2.9.0 on different machine, in different network, it has openvpn 2.7.5 and PPP Connection just work, since on earlier PfSense version with open vpn 2.6.8 i get behavior as above.
I need to get most recent PfSense there and check it out, but it's kind of delicate operation and i have to wait for good time to do it
OK, for now i made it work like a charm, even with tls-auth!
OVPN Server 2.7.5 + ROS 7.24.5
Ciphers CBC and Server keepalive helper 10/60