+1
mfry i have wireguard working with vlans but dont use VRF on beta5. Assuming same for beta6
Guys, could any one of you use the hotspot feature, I tried many things and it doesn’t seem to respond. ( used beta 5 and now trying on beta 6 and nothing yet)
now it is working, the problem i had is that DHCP add arp for leases didn’t work with reply only on the interface of the hotspot, i changed to proxy-arp and its working!
Mmmm MLAG - sounds tasty.
Any hint on how this could be configured and how it is implemented between boxes?
thx!
is ospf and ospfv3 working?
For the L3 HW off-load support on CRS3xx can you confirm if that includes even the CRS305 model?
@normis mk messaging is not clear about this. What is clear is that wifiwave2 will not come to old products.
MK will not support both packages running in v7 - I guess this is what is meant?
MK will not back port wpa3 to the old v6 wi-fi package but that package is still actively maintained, for now - am I correct?
Please be clearer. That is why we keep banging on about all this. Just give us clear messaging. I’m sure you’re just as tired of this merry-go-round as we are.
Finally, consider releasing a self downloadable module, for unsupported for old CAPac.
can’t wait to see this bad boy: crs520-4xs-16xq
In Winbox → Check for Updates, the changelog for this version is empty, all other channels show their changelogs correctly:
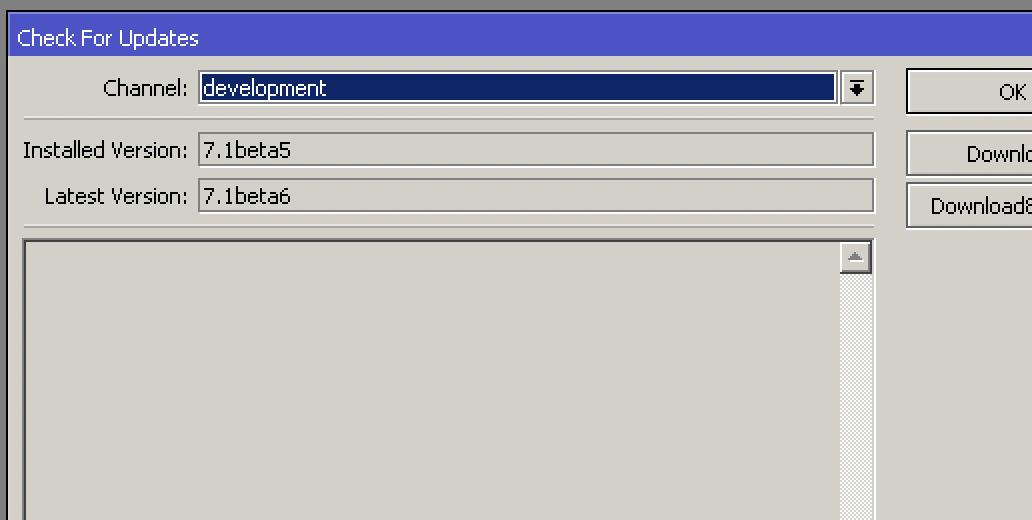
routing filters still dont working
now bgp dont send anything (sending all networks in rt in beta5)
Just noticed there’s a 7.1beta6 TheDude’s client, it’s new ? 
The CHR version seems completely broken. My router is up, I guess, but it responds to ping only 20% of the tine, lot of packet loss and I’m unable to connect to it.
EDIT: I found the problem and it’s not CHR related. When upgrading from beta5 to beta6 OSPF interface-templates lose the interface=SOMETHING restriction and start advertising EVERYTHING. Including the WAN. And routing goes crazy and flaps.
The issue with FQCODEL iss still happening with 7.1beta6. I have a verry simple queue setup with FQCODEL on my LAN interface with download of 225M and upload of 12M. Shortly after enabling the queue I got a reboot with and error in the logs stating a kernel failure in previous boot. When I change the queue to use CAKE I am for the moment not getting a kernel failure reboot and getting good resultes on the dslreports speedtest.
Well guess that was short lived even with CAKE it last longer but I still get a kernel failure after being up for not even an hour.
OSPFv3 seems to be even more broken than before, sadly. Adding an area to OSPFv3 (without any interface-templates) causes one CPU to go into high utilization and all of the OSPF menus stop responding. It is not possible to remove the configuration since the menus stop responding, and the only solution is to reset the device config and restore from backup.
I would probably advise people planning to upgrade to delete their OSPF and BGP configuration first before upgrading, and put it back in carefully taking backups beforehand at at very step of the way.
Is there is a way to use this new Lets Encrypt support without having to open www (and, by extension, webfig) to the world? The Lets Encrypt support is a great idea and I am glad it is there, it is really handy for VPNs etc, but it seems like I am having to open port 80 and webfig to the planet if I want to use it - unless I am missing something.

Me too mate. I also really hope the new CRS models have MPLS push/pop support!
Has 802.11AE / MACSEC been fixed yet ?
That is the reason I was against this feature. Don’t get me wrong - LetsEncrypt is beautiful, but opens whole can of worms because many tasks are done by custom made scripts. e.g. I want a DNS challenge on cloudflare. Someone else wants a DNS challenge on Azure etc… It would be all beautiful, but my feeling is, that full support of all (or at least major) methods of validation will take too much development effort.
In the end, it is easier for me to run separate docker/VM with fully featured certbot and a script which will push it to my router automatically
Wireguard as client is not working even with MSS Clamp fix was working in beta 5.
I don't necessarily have an issue with port 80 validation, but I would want to be able to do that without webfig and everything else being opened at the same time. For instance, certbot has the standalone mode where it runs only a limited webserver for getting the certificate. With such a solution, the www service could be left disabled. It is unusual to open the main www service on a MikroTik router to the world, to say the least - it is contrary to all recommended security practice.
Yes, all CRS3xx devices now support L3 HW offloading. That includes CRS305.