I’ve now carried out some further investigations on this and I believe I’ve figured out what’s causing it.
As previously mentioned, my ISP is spamming me with RAs, which you can see in this packet capture:
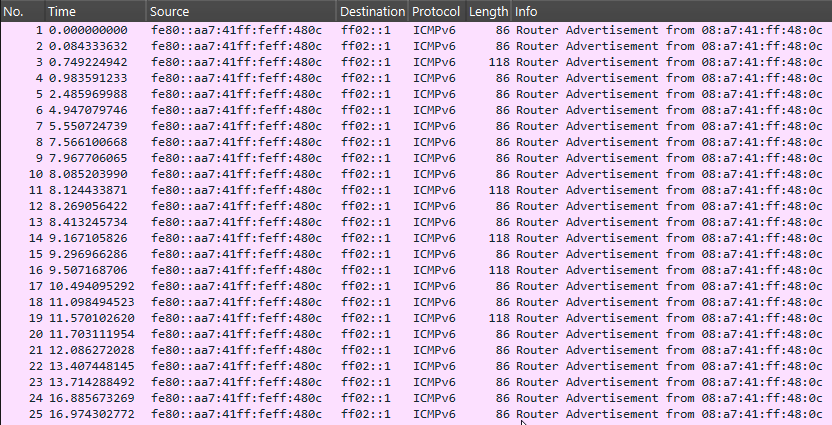
All the RA packets that are 118 B in length contain prefix info, (a /64 prefix with L and A flags set), while all the 86 B packets are missing that prefix info.
Every time an RA with prefix info is received, RouterOS adds a default route, but those are almost immediately followed by more RAs without prefix info, which seem to cause RouterOS to instantly remove the default route again, and the route just keeps ping-ponging like that continuously.
I managed to stop the default route disappearing by adding a firewall rule to drop RA packets smaller than 87 B, and it has been stable ever since, which would seemingly confirm my analysis.
While the ISP probably shouldn’t be spamming RAs in the first place, I can’t imagine it’s intended for RouterOS to react to them in this way?
As I understand it, the creation of a default route should not be dependent on the presence of prefix info in the RA, and RAs that don’t contain prefix info should not invalidate the default route. A default route should be created any time a non-zero Router Lifetime is advertised in an RA, and that route should persist for the advertised lifetime, regardless of what any subsequent RAs are advertising.