reverse-proxy let's you use a self-signed certificate, just tested it. You do need to populate the subject-alt-name= with any SNI you plan to use, and certificate need to match usages for web server.
The main issue with self-signed one is the root must be trusted on client web browsers... which happens automatically since LE is already in most deskop/mobile trust stores. And...without a valid, trusted certificate...the JavaScript inside some containers UI may not work, like code-server I've been tests as you run into CORS restrictions. And, even though you need WAN to sign LE certs, you can still use static DNS+firewall to control access to container, so only LAN access is allowed.
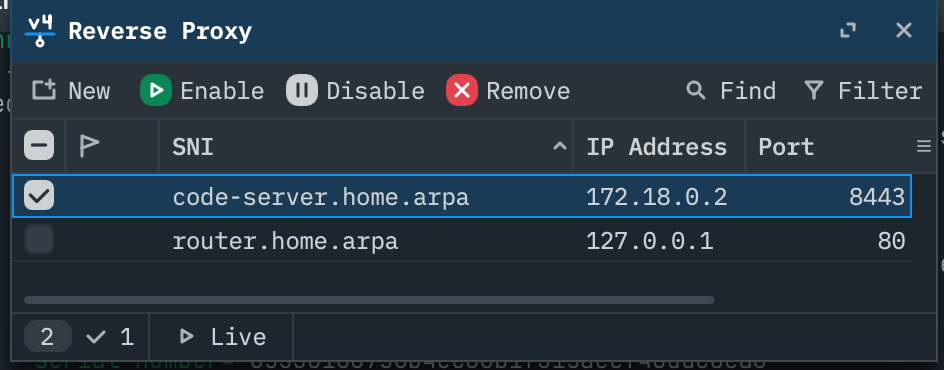
Now, I imagine MikroTIk will have some automatic support here, at some point, as it's common feature on caddy/traefik. And, they already deal with /ip/cloud certs in BackToHomeFiles, so a few SNI one should not be an hard on backend of /ip/cloud DDNS, given BTHF generates a cert for each file share today.