was hoping to see some DoH improvements especially related to this error:DoH server response not OK: 0:
l3hw - added HW offloaded support for VLAN interfaces created directly on Ethernet for CRS8xx series switches
Does this apply to QinQ as well, or only single tagged?
this exactly, just succesfully netinstalled from one mikrotik device to another,
The /app YAML syntax for "secrets" (or "secret") is a bit unclear. Perhaps it's intentional to allow both singular secret: and plural secrets:, and allow both a string and array as the secret/s... but IMO it be better is there was ONE correct way to define these things.
e.g. note the various ways "secrets" are defined:
name: librenms
services:
  db:
    image: docker.io/mariadb:10
    secrets:
      - librenms__database_password
  redis:
    image: docker.io/valkey/valkey:8
    secrets:
      librenms__valkey_password
name: roundcube
services:
  roundcubedb:
    image: docker.io/library/postgres:17
    secrets:
      - roundcube__database_password

  roundcubemail:
    image: docker.io/roundcube/roundcubemail:latest-fpm-alpine
    ....
    secret:
      - roundcube__database_password
Further, its bit unclear if the appname__secretname requires the app name: prefix, or if there "global" to all apps, or if it's that is just your own convention in built-in apps.
- l3hw - added HW offloaded support for VLAN interfaces created directly on Ethernet for CRS8xx series switches;
This is exciting! Does this also mean that the underlying ethernet interface no longer has to be added to a bridge to get l3hw routing?
This imho fixes the "post quantum key attack" warning you see when connecting via ssh.
Maybe in a future version an added switch like  :
/export no-bloody-apps-data
could be added ...

Enabling netinstall package makes winbox3 to exit right after connecting to the router.
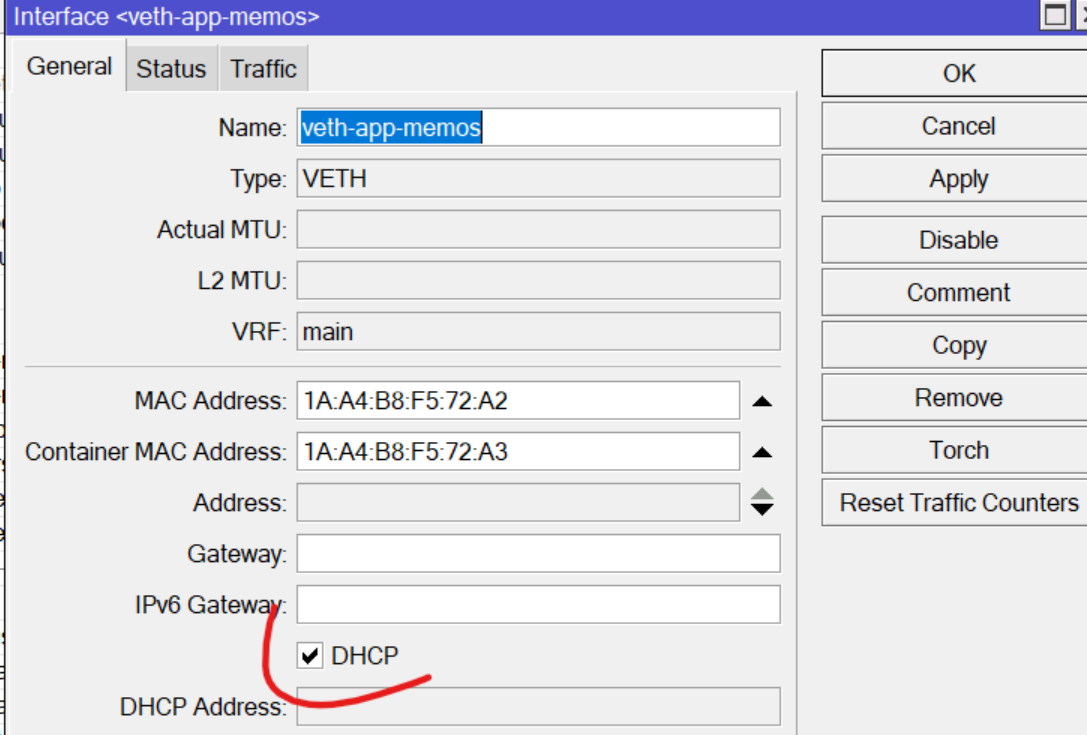
The issue with "/apps" export and extra files will be addressed in the upcoming releases.
I would also appreciate it when user-manager data would be part of the user-manager database and its backup, not in /export.
Only single tagged.
Yes, you can route VLANs by creating VLAN interfaces directly on ether interfaces, on CRS8xx.
Content deleted by author.
@EdPa Any chance we can get an option with netinstall to keep user certificate store?
Thanks!
For me, given how netinstall works and/or is supposed to work, it doesn't make sense... next steps are ask app? ask container? Ask to not "format" the device?......
There are clear and precise methods with which to export all custom certificates in bulk and reimport them later, always in bulk...
I know that a system export and import has the certificates store. An option to just backup the certificate store would be great add on for me. I tried using a script but it's not always full proof when a few have a private keys.
Thanks
:local certpass "myprivatepass"

/certificate
:foreach cert in=[find] do={
 :local certname [get $cert name]
 export-certificate $cert file-name="auto_$certname" type=pkcs12 export-passphrase=$certpass
}