v7.8rc is released!

SSTP connection to DNS name or IP address ?
If the former, it could be the DNS resolving was not active yet at that specific moment.
I can perfectly understand after a first reboot, things are bit slower when starting up.

But that’s an assumption from my part. Could be something else is playing…

Seems to be good on my CRS317 in the lab - it’s still passing L2 tagged traffic.


[zuul@crs317-02-test.lab.ipa.net] > system/routerboard/print 
       routerboard: yes
             model: CRS317-1G-16S+
     serial-number: ABCD123456
     firmware-type: dx3230L
  factory-firmware: 3.40
  current-firmware: 7.8rc1
  upgrade-firmware: 7.8rc1

*) ike2 - added support for “address”, “key-id” and “dn” for Remote ID matching (CLI only);

Hello, how should it be used? In the IPSec identity definition? The code completion gives me no hint and I have not found any changes in the confluence documentation…

Even after lots of fixes for certificates, still can’t use IKEv2 EAP VPN tunnel to NordVPN servers. IIRC this has been happening since v7.7 betas.


20:01:45 info fetch: file "root.der" downloaded
20:02:45 system,info ipsec modecfg nordvpn added by cesar
20:03:40 system,info ipsec peer nordvpn added by cesar
20:03:41 ipsec,error initiator can't find identity for peer: nordvpn
20:03:51 ipsec,error initiator can't find identity for peer: nordvpn
20:04:01 ipsec,error initiator can't find identity for peer: nordvpn
20:04:11 ipsec,error initiator can't find identity for peer: nordvpn
20:04:21 ipsec,error initiator can't find identity for peer: nordvpn
20:04:31 ipsec,error initiator can't find identity for peer: nordvpn
20:04:39 system,info ipsec identity added by cesar
20:04:41 ipsec,info new ike2 SA (I): nordvpn 191.9.xxx.yyy[4500]-185.153.xxx.yyy[4500] spi:c6438b8e214c92a5:5aca58d8b11fe66a
20:04:41 ipsec,error unable to get local issuer certificate(20) at depth:1 cert:O=NordVPN, CN=NordVPN CA8
20:04:41 ipsec,error can't verify peer's certificate from store
20:04:41 ipsec,info,account peer failed to authorize: nordvpn 191.9.xxx.yyy[4500]-185.153.xxx.yyy[4500] spi:c6438b8e214c92a5:5aca58d8b11fe66a
20:04:41 ipsec,info killing ike2 SA: nordvpn 191.9.xxx.yyy[4500]-185.153.xxx.yyy[4500] spi:c6438b8e214c92a5:5aca58d8b11fe66a
20:04:51 ipsec,info new ike2 SA (I): nordvpn 191.9.xxx.yyy[4500]-185.153.xxx.yyy[4500] spi:58d940585cecdb38:6fcb9bd3e691d40d
20:04:51 ipsec,error unable to get local issuer certificate(20) at depth:1 cert:O=NordVPN, CN=NordVPN CA8
20:04:51 ipsec,error can't verify peer's certificate from store
20:04:51 ipsec,info,account peer failed to authorize: nordvpn 191.9.xxx.yyy[4500]-185.153.xxx.yyy[4500] spi:58d940585cecdb38:6fcb9bd3e691d40d
20:04:51 ipsec,info killing ike2 SA: nordvpn 191.9.xxx.yyy[4500]-185.153.xxx.yyy[4500] spi:58d940585cecdb38:6fcb9bd3e691d40d
20:05:01 ipsec,info new ike2 SA (I): nordvpn 191.9.xxx.yyy[4500]-185.153.xxx.yyy[4500] spi:0cbbc484128c8ca9:e0817c6382f08773
20:05:01 ipsec,error unable to get local issuer certificate(20) at depth:1 cert:O=NordVPN, CN=NordVPN CA8
20:05:01 ipsec,error can't verify peer's certificate from store
20:05:01 ipsec,info,account peer failed to authorize: nordvpn 191.9.xxx.yyy[4500]-185.153.xxx.yyy[4500] spi:0cbbc484128c8ca9:e0817c6382f08773
20:05:01 ipsec,info killing ike2 SA: nordvpn 191.9.xxx.yyy[4500]-185.153.xxx.yyy[4500] spi:0cbbc484128c8ca9:e0817c6382f08773
20:05:11 ipsec,info new ike2 SA (I): nordvpn 191.9.xxx.yyy[4500]-185.153.xxx.yyy[4500] spi:b9b836cf0b2ca788:bcd7b33910718100
20:05:11 ipsec,error unable to get local issuer certificate(20) at depth:1 cert:O=NordVPN, CN=NordVPN CA8
20:05:11 ipsec,error can't verify peer's certificate from store
20:05:11 ipsec,info,account peer failed to authorize: nordvpn 191.9.xxx.yyy[4500]-185.153.xxx.yyy[4500] spi:b9b836cf0b2ca788:bcd7b33910718100
20:05:11 ipsec,info killing ike2 SA: nordvpn 191.9.xxx.yyy[4500]-185.153.xxx.yyy[4500] spi:b9b836cf0b2ca788:bcd7b33910718100

Still an issue with bridge DHCP snooping blocking IPV6 PD

Several Kernel failures on CHR. :d

100% sure

kernal is something from 1977. You sure?

Are L3 HW Offload still bug of ospf/bgp/nexthop failure or changed?
I solved those issue with disable and enable l3hw or clear arp. is that fixed?

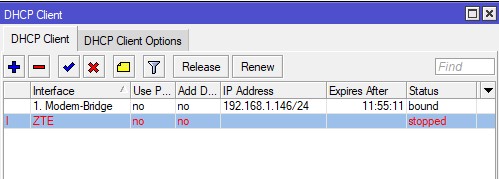
after upgrade to 7.8rc1 USB LTE can’t get DHCP client. showing status stopped
Screenshot 2023-02-11 201339.jpg

Bug with Huawei MA5671A ONT SFP Module persisting in RC1: no link is detected.

When upgrading from 7.7 to 7.8rc no link is detected on the SFP module.

http://forum.mikrotik.com/t/v7-8beta-testing-is-released/163742/307

Yes its DNS name. Maybe after an upgrade its slightly slower starting. Its no big deal at least it works, better than it broken completely in the last few releases :slight_smile:

Same here with Alcatel IK41 USB LTE modem on hAP ac2.
I have downgraded ROS to 7.7 to make it work again.

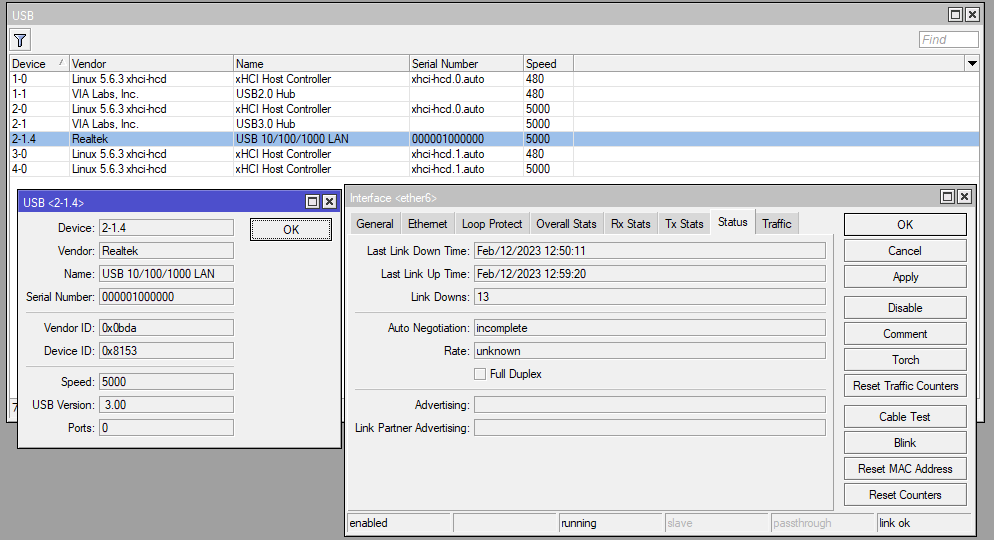
USB Gb ethernet adapter (Techole UH411) with Realtek RTL8153 not working properly. Stats tabs are empty, no autonegotiation. Tested on hap ax3 and hap ac, adapter working on linux and win. machine without problem.
rtl8153.png

No hardware encryption acceleration (Hw. Crypto) in openvpn on hAP ax3 router (cipher: AES256-GCM) In version 7.8beta3 it worked properly.

F1 for ROSE is still missing help descriptors for parameters

DenisPDA, ivicask, smotrov, kev445, own3r1138, curtdept, own3r1138, ErfanDL, username2, mszru, Brendon - Please send the supout file from your router to us to the support@mikrotik.com e-mail address or use our client portal https://help.mikrotik.com/servicedesk/
DjM - We discovered an issue that could lead up to an OVPN server failure when removing client connections.
mducharme - Actually, this functionality is already on the way to you and will be available in v7.9beta.
elbob2002, llag - Yes, it is safe to use 7.8rc and will be safe to use the 7.8 stable version on CRS devices.
rpingar, own3r1138 - This change was a potential fix for your problem. You should try it out and update us with new supout files if the problem for some reason is not fully resolved.
alacis - The issue should be resolved in v7.9beta.
achu, Amm0 - We will look into this.


alacis
FYI, LED issue introduced with 7.8beta3 still exists - viewtopic.php?t=193289 - after upgrading signal LEDs not working and you need to manually toggle it off and on under System → LEDs section.

@MikroTik STOP
This was a bug introduced in 7.8beta3 and should be fixed in 7.8rc, not 7.9 beta
Stop posting new beta for new mayor version. We are waiting of a long term release in 7 series, so next release after 7.8 should be 7.8.1 etc.
Make 7.x stable before adding new version 7.9 etc with stuff that are not important like new storage system, container ++

Are you testing on a static channel and controlling for co-channel and adjecent-channel interference?

it is for sure not a fix for not running dynamic pppoe client interface! The problem is still present on 7.8rc1
I didn’t get yet a crash so …I will update you.
regards

Jotne - My apologies for this mistake, LEDs will be fixed in v7.8, not v7.9.