Please take a look at the firewall flowchart The ultimate Mikrotik iptables flowchart - RouterOS / Useful user articles - MikroTik community forum
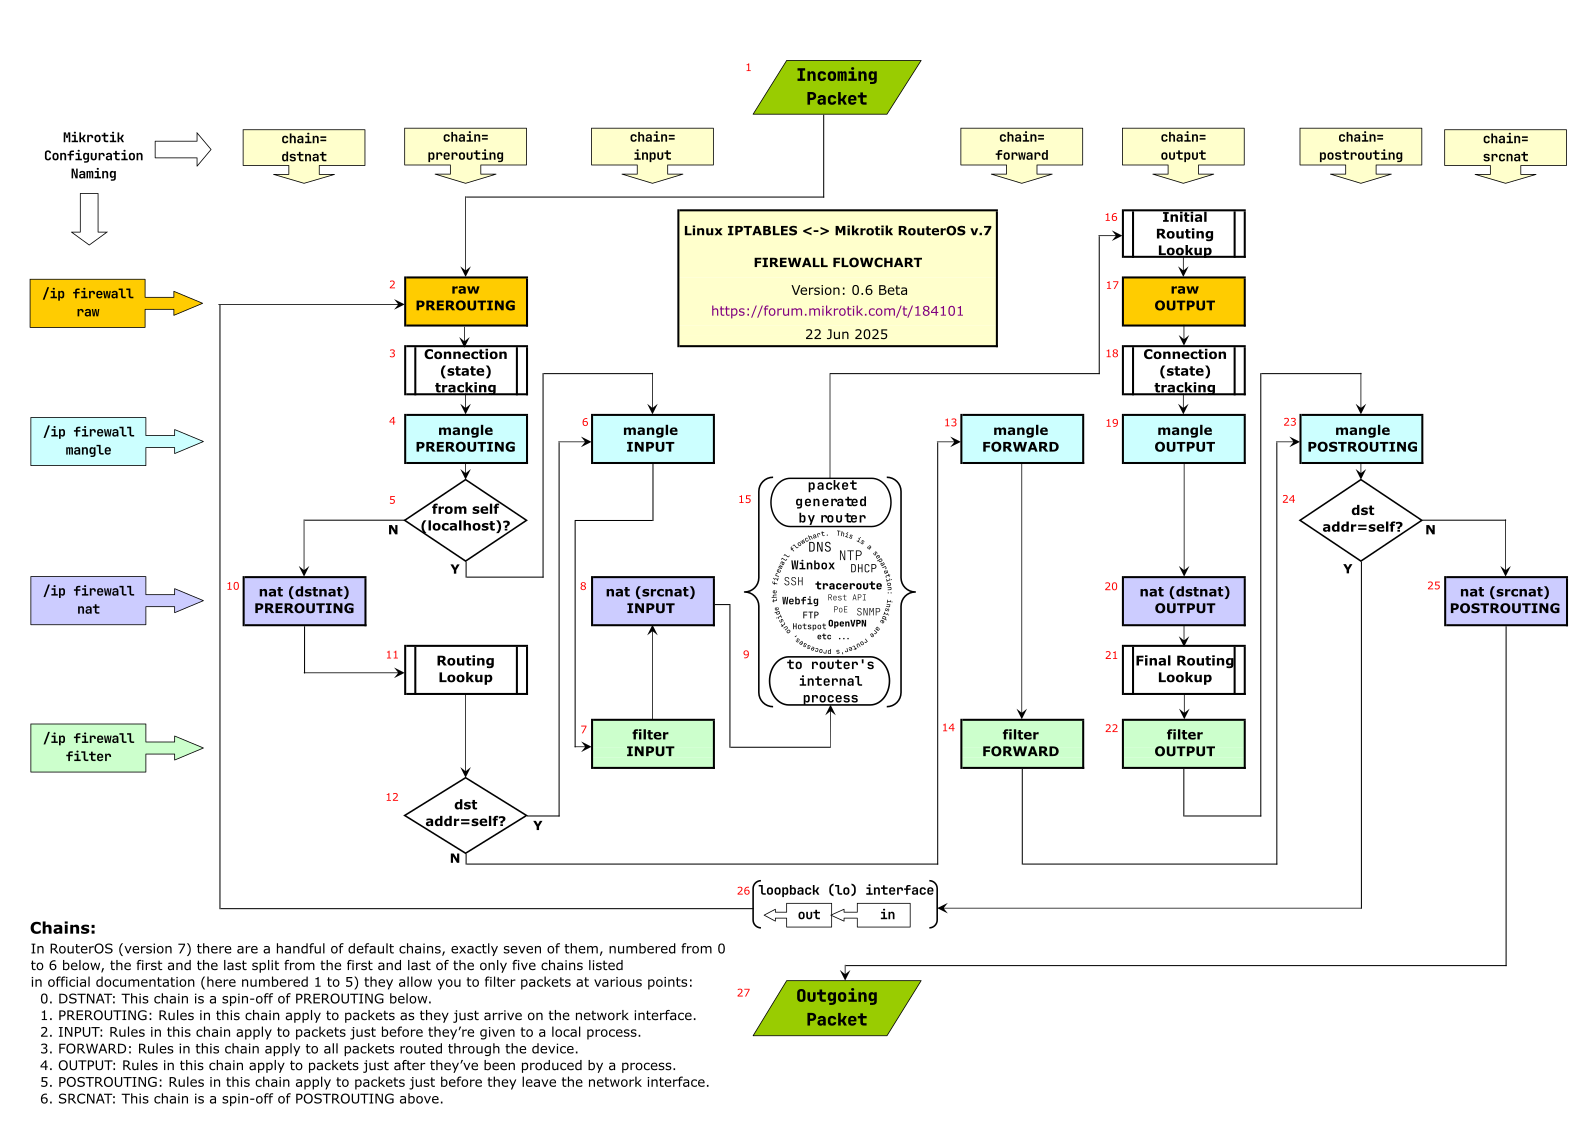
The masquerade rule, which is a SRCNAT rule, is at the end of the flowchart, at the box #25. At this point, the packet has already went through the DSTNAT manipulation, which is way earlier at #10. Which means the value of the destination address, dst-address, has already been rewritten by DSTNAT, and no longer contains the original public IP address. At #25 the value you see in dst-address (and also what is dst-address-list uses to compare) is the LAN IP address of the servers, these:
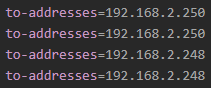
That's why the condition in the masquerade rule should be dst-address=192.168.2.0/24, like what @jvanhambelgium posted above:
or dst-address-list=local_server_list, with local_server_list containing 192.168.2.248 and 192.168.2.250.
Also those masquerade rules don't need to-ports=.