I don't think that's the case. The masquerade rule is a SRCNAT rule that happens after filter. See The ultimate Mikrotik iptables flowchart. When you properly apply the accept established,related rule first, then the other filter rules normally only affect packets in connection-state=new, which means before SRCNAT masquerade. Which means the src-address is still the original one.
It's different when the NAT rule is a DSTNAT rule, because DSTNAT is in prerouting and comes before filter
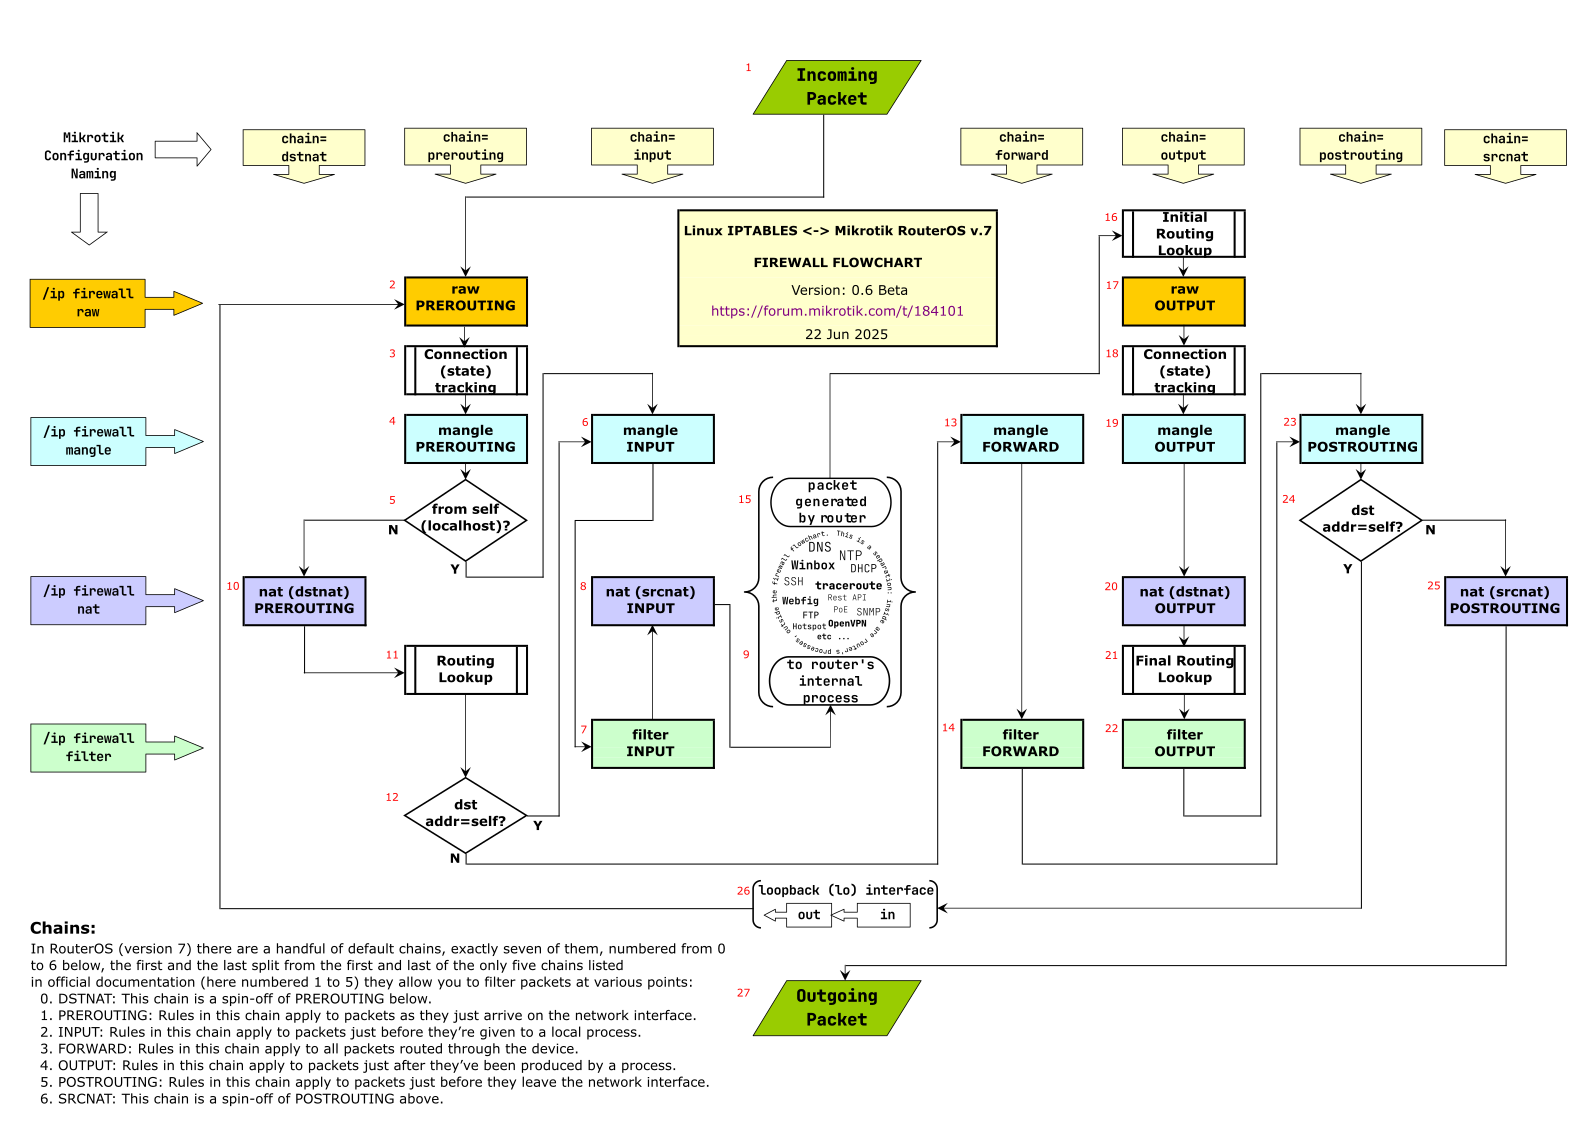
So, when the filter rules are reached, the destination address already changed.