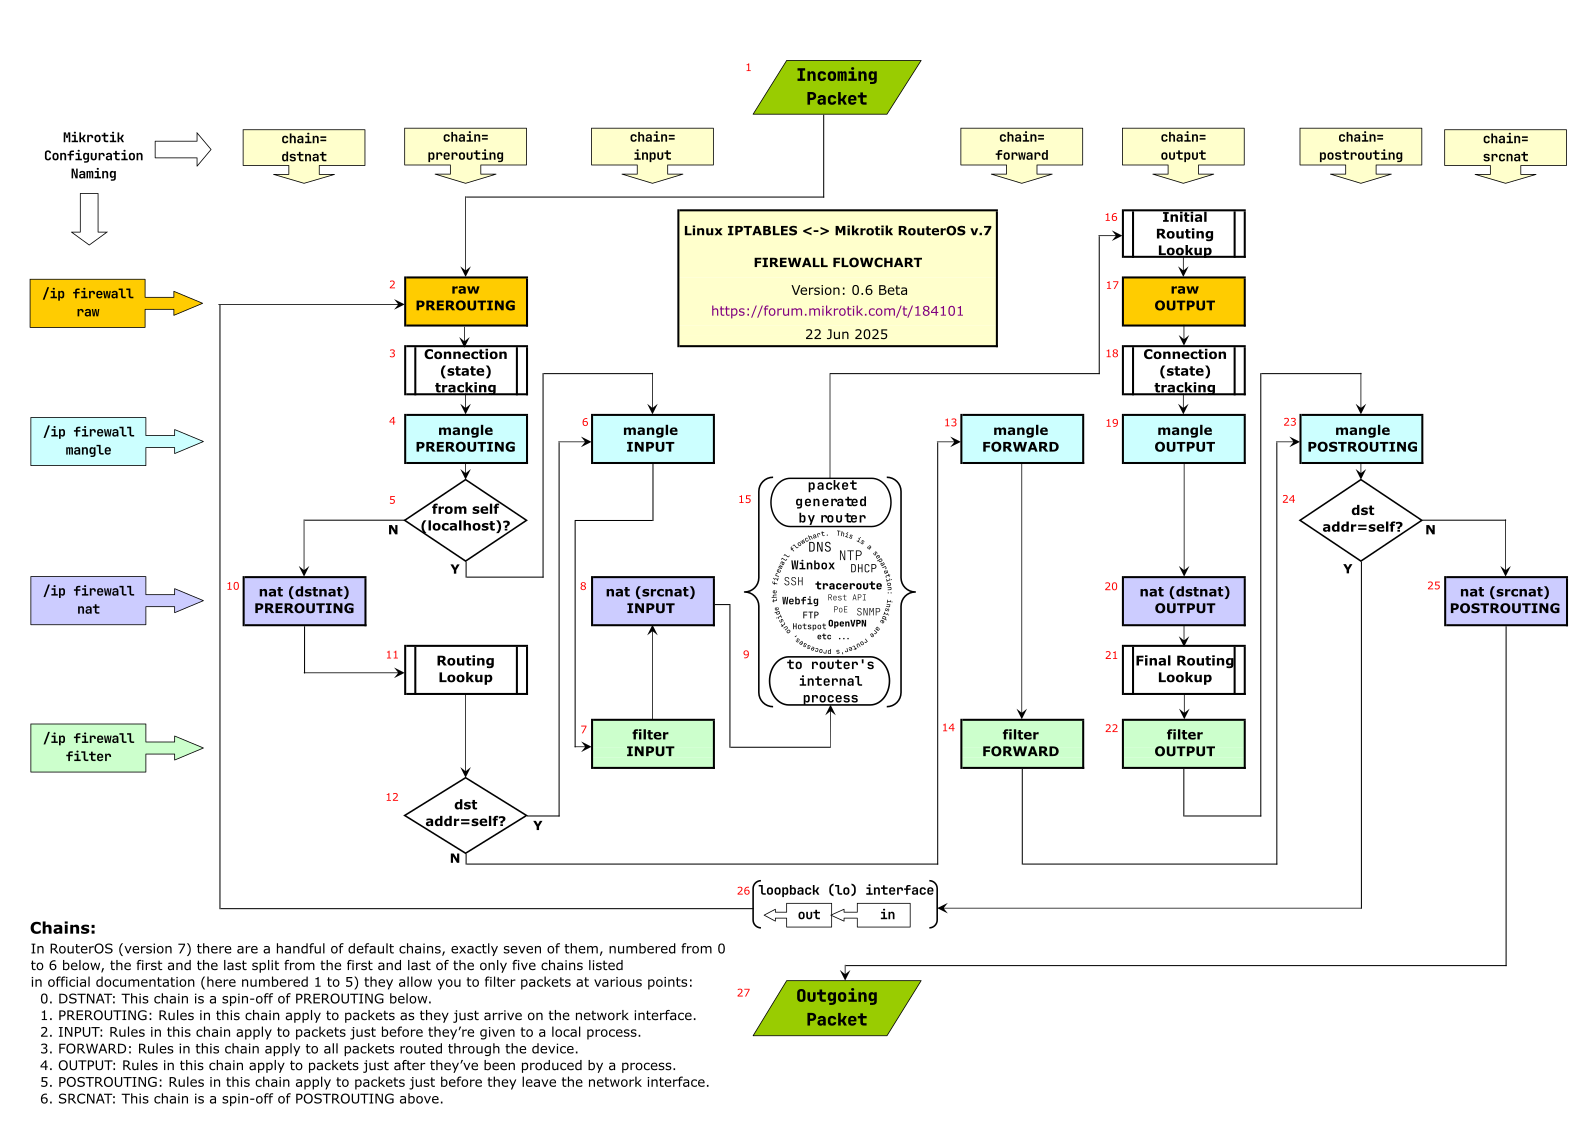
I have recently noticed that my dstnat rules show out:(unknown 0) in the log. The traffic is being forwarded correctly and everything is working fine as far as I can tell. But out of curiosity I would like to understand why the out: interface is unknown in the log?
Log:
dstnat: in:ether1 out:(unknown 0), connection-state:new src-mac xx:xx:xx:xx:xx:xx, proto TCP (SYN), externalwanip:45424->mywanip:9995, len 60
My firewall is setup with a rule that drops all new forward traffic coming from WAN interfaces, except dstnat traffic:
add action=drop chain=forward comment="Drop all except dstnat" connection-nat-state=!dstnat connection-state=new in-interface-list=WAN log=yes log-prefix="Drop all"
And my dstnat rule is setup as:
add action=dst-nat chain=dstnat dst-port=9995 in-interface-list=WAN log=yes protocol=tcp to-addresses=192.168.7.106 to-ports=9995