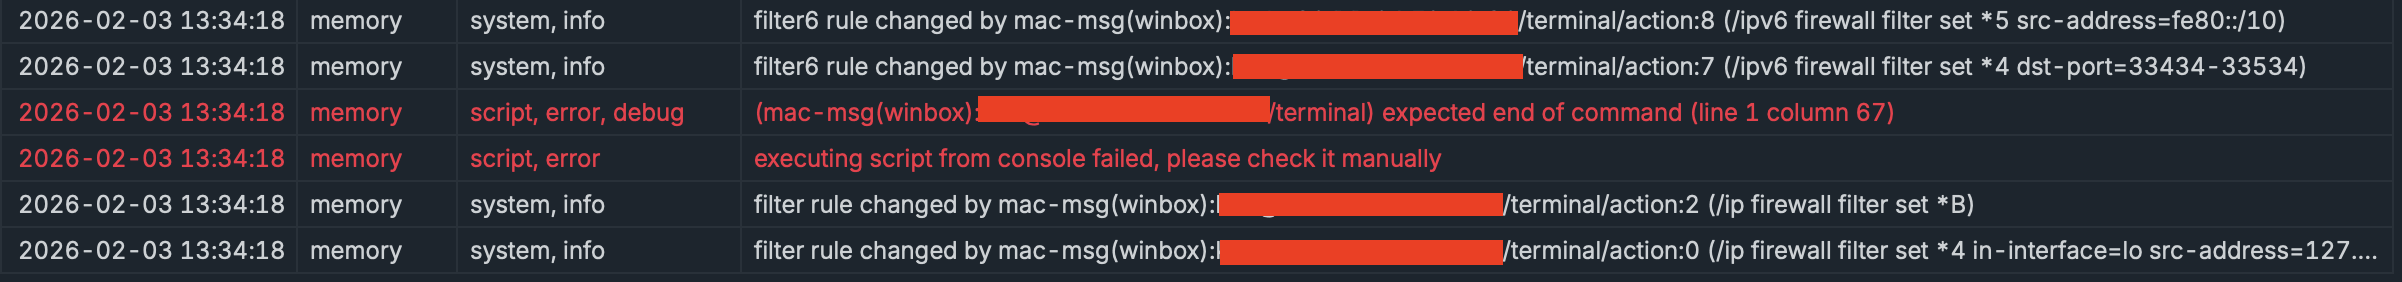
Everything described, although publicly visible and unlikely to cause harm,
is to be used only at the user's own risk.
Fix for BUGS, ERRORS on default RouterOS firewall rules and firewall changes from 6.43 to 7.23.7 (long-term) / 7.24.5 (stable) / 7.25rc1 (testing)
without reset to default for the fix.
This applies to any version of RouterOS 6.43 and later,
and also to any version of RouterOS 7.0 and later,
especially if the machine has never been reset to default after various upgrades and updates.
Just paste on terminal, fix all bugs or errors on default RouterOS firewall rules
and align only default parts to 7.23.7 (long-term) / 7.24.5 (stable) / 7.25rc1 (testing)
the remaining rules are untouched, so do not fix your errors.
For RouterOS v6.43 and up
/ip firewall filter
:if ([:len [find where comment="defconf: accept to local loopback (for CAPsMAN)"]] = 0) do={
    add chain=input action=accept src-address=127.0.0.1 dst-address=127.0.0.1 comment="defconf: accept to local loopback (for CAPsMAN)" \
        place-before=[find where comment="defconf: drop all not coming from LAN"]
} else={
    set [find where comment="defconf: accept to local loopback (for CAPsMAN)" and src-address!=127.0.0.1] src-address=127.0.0.1
}
set [find where comment="defconf:  drop all from WAN not DSTNATed"] comment="defconf: drop all from WAN not DSTNATed"
set [find where comment="defconf: drop all from WAN not DSTNATed" and connection-state="new"] !connection-state

/ipv6 firewall address-list
remove [find where list=bad_ipv6 and address="::224.0.0.0/100"]
remove [find where list=bad_ipv6 and address="::127.0.0.0/104"]
remove [find where list=bad_ipv6 and address="::/104"]
remove [find where list=bad_ipv6 and address="::255.0.0.0/104"]

/ipv6 firewall filter
set [find where comment="defconf: accept UDP traceroute" and dst-port!=33434-33534] dst-port=33434-33534
set [find where comment="defconf: accept UDP traceroute" and !(port=[:nothing])] !port
set [find where comment="defconf: accept DHCPv6-Client prefix delegation." and src-address!=fe80::/10] src-address=fe80::/10
For RouterOS v7.0 and up (differences from v6 are: in-interface=lo, hw-offload=yes and action=fasttrack-connection)
/ip firewall filter
:if ([:len [find where comment="defconf: accept to local loopback (for CAPsMAN)"]] = 0) do={
    add chain=input action=accept src-address=127.0.0.1 dst-address=127.0.0.1 in-interface=lo comment="defconf: accept to local loopback (for CAPsMAN)" \
        place-before=[find where comment="defconf: drop all not coming from LAN"]
} else={
    set [find where comment="defconf: accept to local loopback (for CAPsMAN)" and src-address!=127.0.0.1] src-address=127.0.0.1
    set [find where comment="defconf: accept to local loopback (for CAPsMAN)" and in-interface!=lo] in-interface=lo
}
set [find where comment="defconf:  drop all from WAN not DSTNATed"] comment="defconf: drop all from WAN not DSTNATed"
set [find where comment="defconf: drop all from WAN not DSTNATed" and connection-state="new"] !connection-state

# The following line may generate an error in the logs on models lacking the specific switch chip,
# but this behavior is entirely expected, and the script works regardless.
:execute "/ip firewall filter set [find where comment=\"defconf: fasttrack\" and hw-offload=no] hw-offload=yes"

/ipv6 firewall address-list
remove [find where list=bad_ipv6 and address="::224.0.0.0/100"]
remove [find where list=bad_ipv6 and address="::127.0.0.0/104"]
remove [find where list=bad_ipv6 and address="::/104"]
remove [find where list=bad_ipv6 and address="::255.0.0.0/104"]

/ipv6 firewall filter
set [find where comment="defconf: accept UDP traceroute" and dst-port!=33434-33534] dst-port=33434-33534
set [find where comment="defconf: accept UDP traceroute" and !(port=[:nothing])] !port
set [find where comment="defconf: accept DHCPv6-Client prefix delegation." and src-address!=fe80::/10] src-address=fe80::/10
:if ([:len [find where comment="defconf: fasttrack6"]] = 0) do={
    :execute "/ipv6 firewall filter add chain=forward action=fasttrack-connection connection-state=established,related comment=\"defconf: fasttrack6\" \
                                        place-before=[find where chain=forward comment=\"defconf: accept established,related,untracked\"]"
}
The default rules are here:
This needs to be clear: Anyone who updates or upgrade RouterOS will not have these updates (or default firewall) automatically applied.
So, if the machine originally had, for example, RouterOS 6.43 (or earlier) and was updated to 6.43+ or 7.xx+,
it will still NOT have the default firewall rules and the configuration fixes.
The only way to apply the fixes on such upgraded devices,
aside from using this script or comparing your rules with the default ones and applying the fixes manually,
is to run netinstall or reset-configuration.
Versions prior to 6.43 have a different firewall scheme, based on interfaces rather than groups, and I strongly recommend upgrading to the way it is default now.
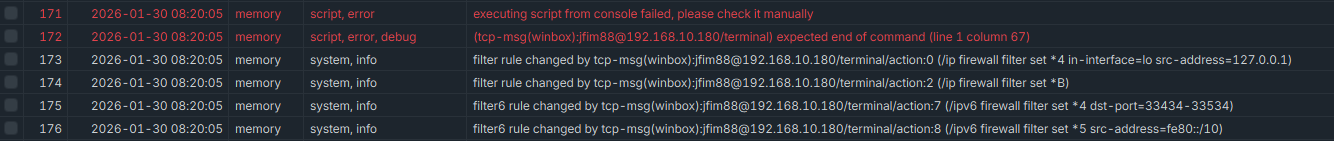

 as it deserves it