not all are willing to share router config with AI hosted somewhere...
Why not? Just omit, like on the forum, real IPs, usernames, passwords, etc., anything sensitive...
Even if it wanted to, what would the AI do? Is it keeping some secret from your own configuration to use against you?
Never send sensitive information to an LLM unless you’re running it locally or paying big bucks for a plan that explicitly excludes your interactions from their training.
and how would you expect that the above proposed "scoring" would work? It would really require some decent LLM to address most eventualities....or it would not work properly in most cases and have more "psychological effect"
Depends on config, like someone finds WG exposed port (or other service) as sensitive information, then there is a lot of effort to cleanup/obfuscate large configs (mine is 154KB), basic audit tool that fetches from MT server some validation rules can be integrated in ROS without using AI.
That, for sure...
If someone training an AI, can be converted on true programming language that check the same things...
yes...like read the manual, typical misconfiguration etc...
Let's put it from the other perspective (because taking care about others based on your own assumption might let you go in a wrong direction): Who want's to have his own configuration get scored by his router?
...then we can continue by how to ensure that the configuration would not be shared (and information will be protected), how large model would be needed to meaningfully score the configuration (while the device would have 128 MB flash and 512 MB RAM) how to prevent that such data would not be used to train AI etc. etc. etc.....then if the scoring is actually good or you have different opinion on points for this and that....
IMO this will create way more issues than benefits.... default config/wizzard, checklist and chatbot + documentation would be much more efficient
maybe also it will report some missing rules, which someone overlooked...
Regarding scoring, yes that can have some psychological effect, but still if report will have some HIGH score like exposed Telnet to WAN it will alert someone; and especially if was not intentionally configured or it is created by hacking - that it for sure trigger someone.
I mean, if you’re training your own ML model, it can be pretty tiny and run on most arm SOCs.
You don’t really need a fully blown LLM here.
simple checklist and best practice in the docs would do the same for less effort....
I could imagine... but who will train that - the average joe? Or will it be some "default ML" distributed with the RouterOS? Another thing to patch, take care of it's security, vulnerability....for what, for who?
On the other hand, anybody can come up with his own scoring system and potentially sell it to Mikrotik 
EDIT: or better - try to sell it to the community...
That will resolve ALL problems, and this topic doesn't have sense then
As discussed in this thread, not all have same skills (Joes vs non-Joes) and also overlooking can happen during making changes, so I still think some automated config validation/audit will be a good thing to have.
In terms of running the model itself, there’s not much attack surface here to be concerned about.
And yes, I’m talking about something Mikrotik would ship as part of RouterOS, and would warn users about potentially problematic configurations, and the reasoning behind it.
Alternatively, they could integrate it as part of their mobile phone app, where they can leverage a significantly better model.
But frankly, implementing it manually based on set state rather than parsing of configuration with a model would be far better, it just entails more work.
To @optio's comment:
I'd actually been thinking of building a "linter" for RouterOS, both for humans and agents. I started a new thread here:
My basic idea is borrow from https://biomejs.dev which uses a set of rules, and offers both potential fixes (if possible) and suggestion to an AI as what to look at (if one is used). And like biome, my idea is there are "rulesets" so that you can control which rules are checked, and which are ignored.
Originally I was more focused on syntax things, deprecated attributes, etc... but this whole security topic adds another use case for some "linting" of configuration so that "bad ideas" are more automatically found (and better practices are hinted at)
Additional reading/resources on the matter:
Stay safe all.
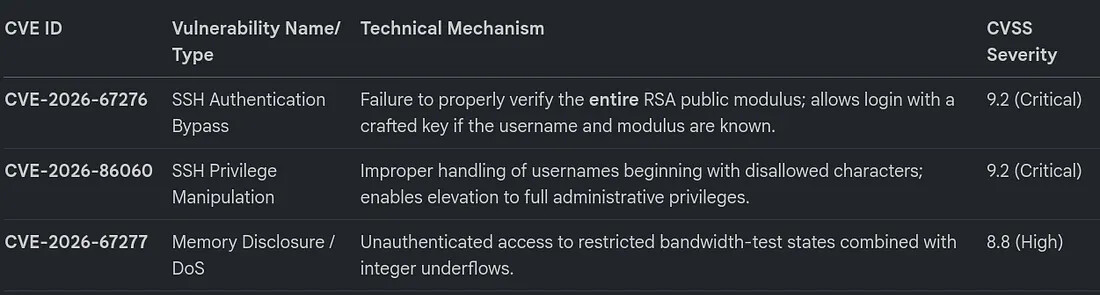
Think that so many opinions are expressed and MT is on the ground that IMO it's time to slow down putting boot in.
WTF, can we please stop with the arbitrary attempts to shut down discussions? 
Who gets to decide when a thread has had enough criticism or no longer fits someone else's view of the world? If MikroTik is following this discussion, that's all the more reason to let users express their concerns and give them a chance to respond.
I'm sure you mean well, but repeatedly telling people to slow down or stop discussing issues isn't helpful. Please let the discussion continue without trying to police it!
Who says that it was an attempt to shut down?
You? If you say so then just calm down as you are way oversensitive.
Do you want to shut me up and forbid my comments?
They are allowed at the same level as yours. Aren't they?
Do not like? Just move on ... it was suggested to me once.
Please point EXACT words of "shutting down". EXACT.
"Slow down putting boot in" means AFAIK that is time to give up a little finishing off wounded one. They are already aware of problems. Not aware, AWARE.
300+ posts ... just keep commenting. Your choice. I just expressed my POV.
You asked for the exact words, so here they are: "it's time to slow down putting boot in." That's what I was responding to.
Of course you're entitled to your opinion, just as everyone else is. But suggesting that people should ease off because MikroTik is already aware of the problems is still an attempt to influence whether the discussion should continue. You don't have to explicitly say "shut up" for that to be the effect.
And no, I'm not trying to forbid your comments. I'm asking you to stop telling others when they've said enough. If you think the criticism is wrong or unfair, challenge the actual arguments instead.
MikroTik being aware of the problems doesn't mean users should stop discussing them. Quite the opposite, this is exactly the kind of feedback they should be listening to.
And since you're also acting as a moderator, I think you need to be especially careful about how you phrase things. Comments from a moderator carry a different weight than comments from ordinary users, and repeatedly suggesting that people should ease off can easily come across as an attempt to shut down criticism.
If you can't separate your personal opinions from your role as a moderator, then perhaps you should reconsider whether that role is right for you. I don't think that's an unreasonable expectation.