I can confirm, "/ip service" filters the IP before it is passed to the respective service. It is safe against attacks.
Thank you for this clarification.
I can confirm, "/ip service" filters the IP before it is passed to the respective service. It is safe against attacks.
Thank you for this clarification.
Updated research from previous post. Restricted to two links, but included the references.
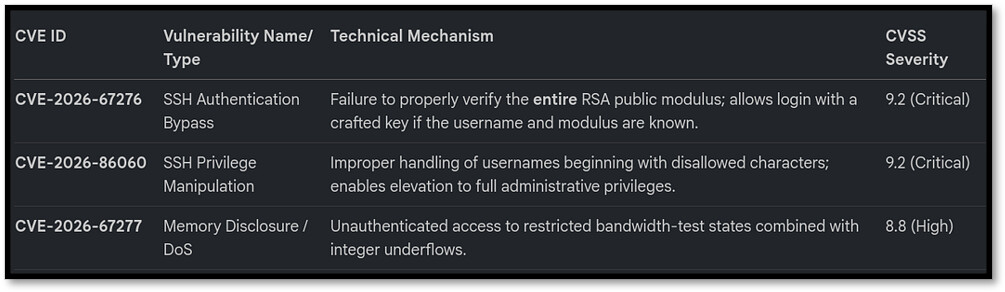
BLUF: Multiple CVEs, tracked as “MikroTrick,” are actively being exploited reported as early as the start of September. MikroTrick takes advantage of an SSH bypass, compromising an initial user, to then leverage SSH privilege manipulation resulting in administrative access. Unauthenticated Denial of Service (DoS) can also be performed from the bandwidth-test server.
Timeline:
Figure 1: CVEs chained for “MikroTrick”
Detections:
Remediations:
Resources:
<personal=on humorus=on
You misread the meaning.
Tilll the post I posted yesterday I had been thinking that the emoji placed at the end - especially at the own line - means that the comment is humorus one and should be treated as such.
I was wrong. My bad. Seems that AIs do not understand sarcasms and HIs started to loose such an ability in the "light" of free access to AI to analyze what others wrote. Not mentioning lack of will and intentional picking on.
I would repeat and expand my opionin
It's time to slow down kinking the grounded man as they do ignore it most of the time - maybe even like being kicked - and there could be none of them to kick if you knock them out too fast. There would no more fun.
emoji is a sign of sarcazm
personal=off humorus=off>
<personal=on
I would like also to add that if you use continous tense with "stop telling" then:
@Larsa, you should consider yourself: "Let he who is without sin cast the first stone".
You instructed people to stop commenting and keep opinions for themselves. You will easily find topics where you did it, so let me quote your own words: so please stop telling people what they can post or not.
If you fire up big guns with "You as moderator ...." you suggest superstitious selfcensorship and putting a muzzle on. There is no "Dr. Moderator & Mr. BartoszP" with splitted personality. Even using these exaggerated "personal=on" markups would let the picky man in bad mood to pick on as a role of "something" does not magically dissapear when they are used.
BTW, topic changed it's core meaning from "Important security update" to "What configuration is safe and how administering should be done". It should be splitted long time ago to the new one but I am afraid to even try to do that now.
According to moderation:
I think, it's my opion you can not agree with, that a part of moderation is making tough decisions and the need to "dare" sometimes. No way to satisfy all. There are dozens of posts that should be erased but they are still visible. Many of them are obviously at least "unpleasant" but they stay at their places. These posts do not draw your attention and you do not report them. Strange, really strange.
Returning to the "security sh*t, that hit the fan":
In that topic you blame MT for this and that of security level. Good. Keep going but I recall some complaining topics on introducing device-mode that raised the security level. So many "I have to netinstall new devices as they .... ". If I recall properly even in this thread there were "I have to go miles to restart the router".
Ones have to decide if they want secure to the point of absurdity devices or easier to manage ones.
In that topic we have nowadays more "absurdity level" fans, in other topics we have opposite opinions to the level of "more Quickset options".
What is better: still water or sparkling one? (rethorical jocular question)
personal=off>
<moderatormode=on
For all: Be sure, that stopic will stay open till the other admin or moderator close it. It wasn't my intention to close it as Larsa suggested.
moderatormode=off>
To Larsa:
<sarcazm=on personal=on
As you wish. You can keep chewing that chewed topic forever.
personal=off sarcazm=off>
TL;DR, patch your shit and move on.
Patched long before "TL;DR;" posts. There are some priorities to obey.
I upgraded and now my cable modem won't connect. Thanks.
You already knew it was going to end up that way.
Someone has created a working PoC for both v7 and v6 and shared a demo video, but they haven’t released the actual exploit code. The demo also shows that logging in as user -2 is not required, CVE-2026-86060 can apparently execute commands directly without first creating a user.