This post is primarily aimed at developers but if anyone has a pertinent thoughts please chime in but I have 2 restrictions. Please don't suggest not using PPPOE because that is not remotely an option as too many clients involved. The OSPF vlan standard we use is also off limits there is little room to expand the VLAN ranges.
So now my question and pondering
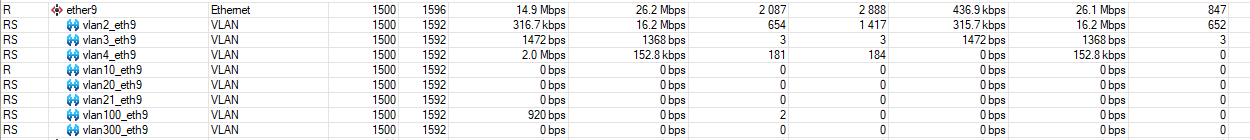
On PPPOE core routers we generally have 2 OSPF networks (i) management (ii) public IP and then we have VLAN(s) carrying the PPPOE to distribution.
Because of the well known PPPOE server performance issue generally one or two OSPF (depends if management is isolated) and the PPPOE are on a single fibre port which connects to a core distribution router.
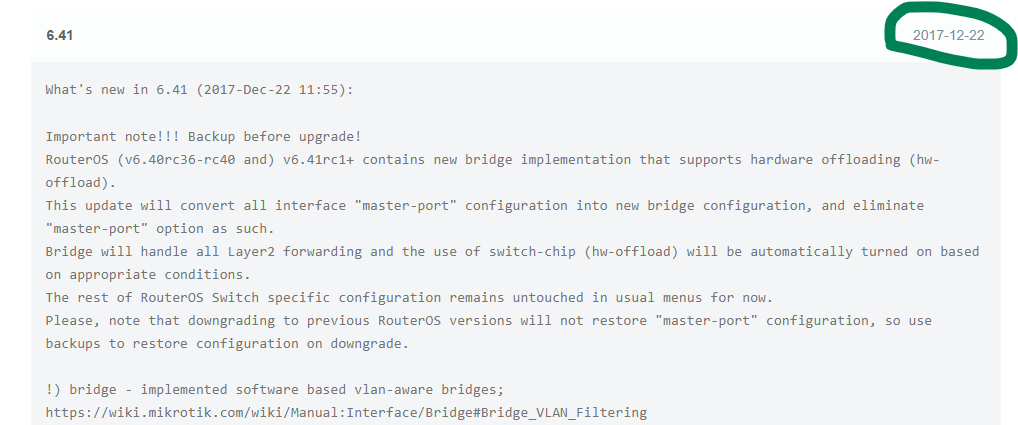
The PPPOE server VLAN are obviously being encourage to go into the new bridge style because you are even giving us the new option of "PPPoE over a VLAN" on the new bridge format.
The problem comes that the OSPF is still on old style VLAN interfaces on the the SFP. That means the SPF is sort of a mashup between old and new bridge format. Specifically you have to remember to turn the hardware offload off on the port or your OSPF doesn't work (new bridge style takes priority).
We can't bring the OSPF into the new style bridge because we set VLAN ids standards for OSPF even down to ids for management and public OSPF. Log into any router and see an interface with a ospf VLAN ID you know immediatley that is an OSPF connection to whatever is on that interface. So we are recycling the same VLAN between interfaces but no bridge.
So I can't see where this all goes with the new bridge format because we aren't going to duplicate fibre connections and we will never be able to hardware offload.
Sorry you need to stop now .. the new format didn't work for lots of situations.
It has been a work in progress and is still evolving they only just fixed the sub interface issue.
The issue I am asking about is how do you deal with a vlan sub interface that you don't want to connect to the bridge. The only way you can do it is make an old school vlan interface and try and merge it with new format.
If you want to see the sub interface change discussion it's well covered here
The problem is obvious as of 17.6 you can now put bridge sub interfaces properly and accurately on the bridge you can not however put a sub interface on a port in the bridge.
The background to this is also blind freddy obvious they (MIKROTIK) are trying to hardware offload the packets out the port so they can improve router performance and compete with the big boys. To do that everything must be described WITHIN THE BRIDGE FORMAT so all packets leave the port in the same hardware offload.
Even now as of 7.19.6 stable because you can't encapsulate just a VLAN interface on the port that also connects to the bridge you have to explicitly turn the hardware offload off and add the vlan interface to the physical interface. For this to work going forward they have to add sub interfaces to the port that don't connect to the bridge but does go thru the hardware offload.
Yes we have explained it to Mikrotik but it also needs a bit of community push. If they stop where they are the hardware offload is basically useless to most ISPs and new brdige format history repeats.
Go back to what you said the new bridge format goes back 8 years but for 7 of those it was basically useless. All you could describe was a vlan aware switch and a ROUTER doesn't need that it wants a switch you can set IP's into multiple vlans and inject or withdraw services from like every other router on the market.
I'm sure that you are aware that WE (FORUM USERS) have any possibilities to change that situation.
It's superb that you point out the problems but IMHO it's complexity and the solution needs direct contact with Mikrotik. You have to submit a ticket and push and push and push them.
If you say that 7 years have been useless and you haven't raised a ticket yet, then what you expect from us? Us, forum users.