It's already possible with some "trick":
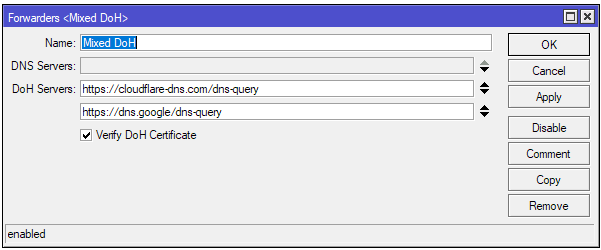

/ip dns forwarders
add doh-servers=https://cloudflare-dns.com/dns-query,https://dns.google/dns-query name="Mixed DoH"

/ip dns static
# bootstraps
add address=2606:4700::6810:f8f9 name=cloudflare-dns.com type=AAAA
add address=2606:4700::6810:f9f9 name=cloudflare-dns.com type=AAAA
add address=104.16.248.249 name=cloudflare-dns.com type=A
add address=104.16.249.249 name=cloudflare-dns.com type=A
add address=2001:4860:4860::8844 name=dns.google type=AAAA
add address=2001:4860:4860::8888 name=dns.google type=AAAA
add address=8.8.4.4 name=dns.google type=A
add address=8.8.8.8 name=dns.google type=A
# this catches all domains and uses the forwarder defined above for the queries
add forward-to="Mixed DoH" regexp="[a-z0-9-]+\\.[a-z]+" type=FWD
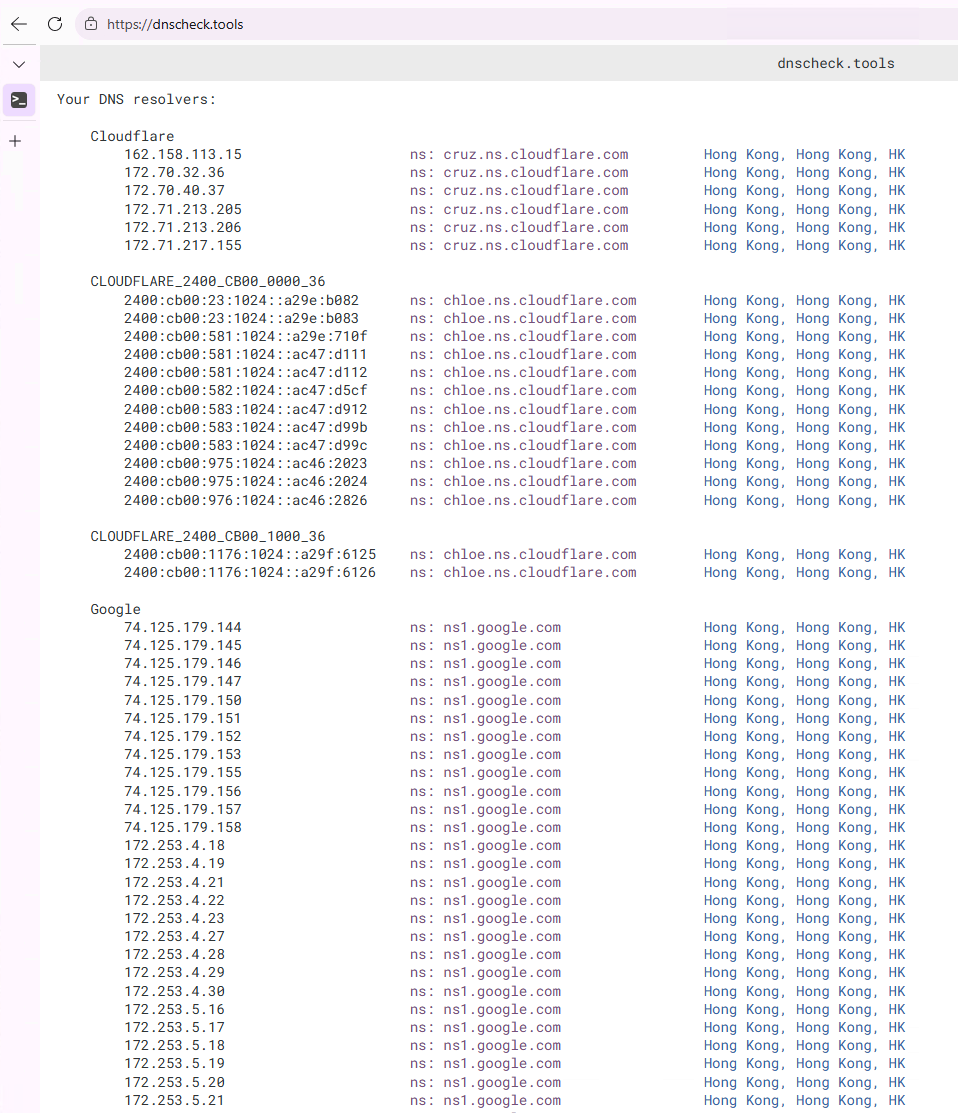
Tests with dnscheck.tools show that both Cloudflare and Google are used as resolvers (I am in Asia):
And RouterOS does make simultaneous HTTPS connections to both cloudflare-dns.com and dns.google:
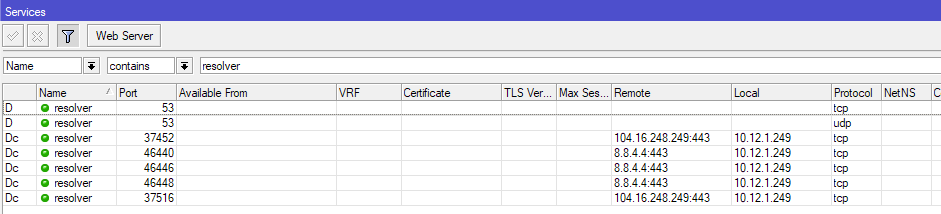
This also shows that RouterOS has no reasons to not support multiple DoH entries in the main DNS setting!